Why do businesses only care about cybersecurity once they get hacked?

Small and medium sized companies are putting a third (32%) of their revenue at risk because they are falling for some of the common misconceptions around cyber security, leaving them vulnerable to losing valuable data and suffering both financial and reputational damage.

Organisations in any industry face this risk. Due to the capability and sophistication of attackers securing personal data will always be in development. There is still reasons to make it as hard as possible and not be victim to the most basic attacks.

We've written a list of the most common reasons organisations get hacked and how you can avoid them.

Difficult to visualise the impact of risk mitigation

Businesses are always looking to increase their growth rate. At early stages, startups tend to spend a high percentage of their time in building innovative features & investing in user acquisition. This usually leaves behind little to no budget for investing on other things such as cybersecurity. Similarly, enterprises need to meet revenue goals for each quarter to maintain their stock prices.

It is often difficult to convince such startups and revenue-driven companies to invest their money in projects that do not directly contribute to an increase in revenue. Planning ahead will save you money in the long term, and cybersecurity is something you should insure your organisation with sooner, rather than later. Pro-active defense rather than reacting to a breach.

It is difficult to quantify how much damage such a breach can cause. In some cases, it can be something trivial that doesn't require public disclosure (still reported to the ICO). Whereas in other cases, it could permanently damage an organisation’s reputation.

Lack of incentives

Attempting to hack systems is inexpensive. Yet, a successful hack can lead to huge profits for hackers through extortion and theft. The payoff of a successful hack against the relatively little investment is an incentive for hackers.

On the other hand, when businesses take measures towards cybersecurity, there is little incentive to look forward to. From a day-to-day', high street business perspective, it is not perceived a valuable incentive. Even though the benefits of implementing cybersecurity measures far outweigh the losses.

When your organisation takes out an insurance, you pay your premiums upfront before benefiting from the protected losses in an unplanned event such as a fire or break-in. The same attitude should be considered when protecting your business with cybersecurity, you will be grateful for having put in protections earlier rather than once you’ve been hacked.

Indeed, the motivation for hackers is far greater than the motivation of businesses to protect against them. Think long term, and think about the headache you will prevent from having to deal with a critical situation.

Inadequate training of employees

For the most part, technology can keep its own attackers out. However, it is often the technology users that unknowingly allow hackers and malicious software in.  We have seen that on most occasions, computers are not the points of failure, but instead it is the people who are targeted in social engineering attacks. These attacks are used in a variety of ways to trick employees into providing their sensitive information. For instance, hackers might impersonate officials or large companies/orgs via email, SMS or phone calls. Commonly known as phishing, SmSishing & vishing.

Even if a business has covered cybersecurity from a technological perspective, there is more to be done. Social engineering attacks, can be easily prevented by holding regular training sessions for employees on information security. Emphasising a culture which provides an adequate reporting process without inducing fear on staff job security. Educating employees is one of the best tools to protect your business’ cybersecurity.

Absence of an information security policy

Cybersecurity is not just about intrusion detection and prevention. A key part of it is about ensuring that preventive measures are in place to reduce the risks of intrusion in the first place. This human element is one part of cybersecurity that most often gets ignored.

Any organisation that wants to strengthen its cybersecurity needs a detailed set of guidelines that address these ‘humanistic’ issues. This is where it is important to have an information security policy in place. A well-written information security policy addresses subjects such as password protection, software updates, and access to web content.

It is important to mention that an information security should be documented in a manner that is easy to understand for employees. It is one thing to create a security policy, but the key is to actually implement it within an organisation.

Conclusion

Most businesses feel that cybersecurity is an overhead cost to their operations. It is not until these organisations suffer significant losses to breaches that they realise how important cybersecurity is. With the rise in cyberattacks over the last few years, it is now time for businesses to all sizes to start taking cybersecurity seriously.

CyberSmart provides cost-effective cybersecurity compliance that help businesses protect themselves. If you would like to discuss further on the importance of cybersecurity for your business, feel free to reach out to us.
Top 10 Antivirus Products to Use for Cyber Essentials

Keeping computer systems protected against viruses and other forms of malware is one of the first steps towards cybersecurity for an organisation. This is one of the five key requirements of the Cyber Essentials scheme that organisations need to fulfil. The most effective strategy for meeting this requirement is to make use of an antivirus product that can keep unwanted malicious content and programs away.

However, with a wide variety of antivirus products available out there, it can be difficult to choose the best one for your organisation. When choosing an antivirus solution, organisations need to keep a number of factors in mind including the pricing, features, and platforms it supports.

To assist you in making the right decision, we have listed the top 10 antivirus products that you can use when preparing for a Cyber Essentials certification.

1.      Trend Micro Worry Free Advanced

Trend Micro provides comprehensive protection against malware and viruses in the form of its Worry-Free Business Security Advanced antivirus solution. It covers all the basics antivirus features such as real-time scans and scheduled scans and comes with advanced features such as anti-spam, web content filtering, ransomware shield mobile device management, and email security. Additionally, the antivirus software can detect malicious activity through USB ports and external devices to provide security against physical breaches as well.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS.

2.      Panda Endpoint Protection Plus

The Panda Endpoint Protection Plus is highly rated as one of the best enterprise antivirus products because of its advanced features and budget-friendly price. The antivirus suite comes with a well-designed management console that enables you to monitor systems in real-time. It can protect your systems against basic as well as advanced threats such as malware, spam, malicious web content, and viruses. Even though this antivirus product can sometimes slow down your computer systems, it is a choice worth considering, particularly for small businesses.

Platforms it is available on: Android, Microsoft Windows, macOS, Linux.

3.      Norton Small Business

Norton Small Business provides tailored features to small enterprises, although the protection remains the same as the ones used by large organisations. Other than providing all the basic features for protection, Norton’s Small Business antivirus product provides protection across different devices with a single license. You need a single program to protect both remote and in-office systems and manage them over the cloud. Overall, it is a good value option with a simple installation and configuration process.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS.

4.      Kaspersky Small Office Security 5.0

An effective and user-friendly antivirus software that you can use to keep your systems protected is Kaspersky Small Office Security 5.0. According to independent testers, it blocks more than 99% of malware and associated hacking attacks. The features include real-time protection, anti-spam, content filtering, and firewall. The firewall is a welcome feature that can prevent unauthorised access to your data, along with strict control of your browsers that disallow access to malicious web content.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS.

5.      Bitdefender GravityZone Business Security

Bitdefender’s GravityZone Business Security is a good option to consider if you want a high level of protection against malware threats across devices. Even though the installation and setup process of this product is quite lengthy, the antivirus software is quite simple to use once you pass those stages. The features include real-time protection, URL filtering, firewall, anti-malware, and web advisor among others. However, unlike most other antivirus products on this list, Bitdefender does not provide device location services for finding lost devices with this solution.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS.

6.      Sophos Endpoint Protection

The Sophos Endpoint Protection antivirus is suitable if you are looking for basic protection at a low-cost. Even though it is not as good as the other antivirus products in this list in terms of usability, it does a fair job in keeping away malware and viruses. The plus point is that it is much cheaper than other solutions so it can be a suitable choice for SMEs. The Sophos Endpoint Protection Advanced provides advanced protection feature such as blocking suspicious URLs and monitoring user behaviour to detect threats.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS.

7.      ESET Endpoint Security

ESET Endpoint Security is a great all-in-one antivirus solution that provides you with protection against all kinds of malware including trojans, viruses, and ransomware. Like Bitdefender, the ESET can be difficult to install and configure but once everything has been set up it works perfectly in protecting the devices within your organisation. Other than its good overall performance, its adjustable pricing policy makes it an option worth considering for SMEs.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS, Linux.

8.      McAfee Endpoint Security

McAfee Endpoint Security is a cloud-based antivirus product that helps you secure and protects all internet-enabled devices within your organisation. It provides a variety of features that help in preventing, detecting, and eliminating malware from computer systems. The excellent customer support provided via multiple channels (email, live chat, and phone) make this a good choice for an antivirus solution.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS.

9.      Symantec Endpoint Protection

Symantec is a renowned company in the cybersecurity industry, particularly because of its feature-rich product. The Symantec Endpoint Protection Business is widely appreciated because of its high-performance and functionality. It provides a range of advanced protection features including intrusion prevention, firewall, behaviour monitoring, multi-level security policies, remote data management, and device location.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS, Linux.

10. Avast Business Antivirus Pro

Avast Business Antivirus Pro is a reliable antivirus product that comes with a range of malware protection features. The antivirus software provides advanced protection features including browser protection, firewall, anti-spam, remote control options, email protection, and basic antivirus. It provides protection against third-party software installation by providing sandboxing that enables you to run applications in a ‘secured’ environment.

Platforms it is available on: Android, iOS, Microsoft Windows, macOS.

Conclusion

Regardless of how small or large an organisation is, one of the key steps that it can take to protect itself against cyberattacks is to use an effective antivirus solution. This is a major requirement that organisations must meet in order to be compliant with Cyber Essentials.

CyberSmart is an automated compliance service that helps organisations simplify the process of getting certified with leading standards such as Cyber Essentials. If you have any questions about which antivirus product you should choose for your business, get in touch with our experts right away.

GDPR Subject access request (SAR) - 6 steps to deal with it

A Subject Access Request (SAR) is the Right of Access allowing an individual to obtain records to their personal information, held by an organisation. GDPR, which became applicable in May 2018, provides individuals with the right of access to information.

It is essential that your organisation is aware of the basics of SARs and can handle them effectively to avoid large fines. In this blog post, we provide a six-step practical guide on how you can deal with subject access requests under the GDPR in 2023.

  1. Recognise the request

The first step to responding to a SAR is to identify it. The GDPR does not specify how an individual can make a valid request for information. A subject access request can be written or verbal, and it can be made to any part of your organisation including social media.

Therefore, it is best to assume that if an individual asks you for their personal data, regardless of the channel or mode of communication, it constitutes a valid subject access request under the GDPR. It is advised that basic training on the GDPR should be provided to all staff members and managers within an organisation.

Your employees should be able to recognise a SAR and pass it on to the relevant focal person who can handle the request.

  1. Understand the time limitations

The GDPR requires you to respond to a SAR within one month i.e. 30 days of its receipt. You must get back to the individual with the requested information without undue delay.

However, you can extend this time period to up to three months if the request is complex, or if the same individual has made a high number of requests. In this case, you must inform the individual that you need more time within one month of the request to avoid any legal issues.

  1. Dealing with fees and excessive requests

You cannot charge a fee for providing information to individuals in response to a subject access request. However, there is one exception to this rule. If you receive a SAR that is ‘manifestly unfounded or excessive’, you can charge a reasonable fee to deal with the request or refuse to provide information at all.

There is still some speculation over what requests can be considered manifestly unfounded or excessive and therefore, it is advised that you take caution when refusing a SAR. Similarly, there is no certain threshold for the reasonable fee that you can charge. The ICO guidance suggests that it must be charged on the basis of the administrative costs associated with the retrieval of the requested information.

To be on a safer side, it is best not to charge a fee or refuse a SAR at all. But, if you choose to refuse to deal with a repetitive SAR then you should inform the individual within one month of the receipt of the request with the reasons for refusal.

  1. Identify, search, and gather the requested data

The most time-consuming and labour-intensive part of responding to a subject access request is gathering the requested data. If an individual makes a broad request for access to all their personal data, then it can take weeks to identify and search for the information.

Personal data is defined as any information relating to an identifiable natural person under the GDPR. This broad definition makes it difficult to identify the information that you need to provide.

The ICO states that if an organisation processes a large amount of personal information, then it should ask individuals to clarify their request for information. Therefore, a good approach is to ask for additional parameters or specific pieces of information that individuals need from the SAR. However, it is important to understand that you will need to comply with the SAR even if the individual refuses to provide additional parameters.

It is advised that organisations should allocate someone to be in charge of coordinating the process of gathering requested personal data. Document management providers can help you carry out effective searches for data using the right date range and keywords. Even though these services can increase costs, it ensures that your organisation can comply with the information needs of a SAR in time and correctly.

  1. Learn about what information to withhold

A challenging aspect of responding to a SAR is to decide what information to withhold from the requester. After you have gathered all the requested information, the next step is to filter out the information that you can legally hold back.

One particular concern is to ensure that when responding to a SAR, you should not disclose the personal data of other individuals. The Data Protection Act (DPA) 2018 states that you should not comply with a SAR if it would require you to disclose information about another identifiable individual.

The exceptions are when the other individual has given their consent to the disclosure, or the organisation finds it reasonable to comply with the request without the consent of the individual. When deciding whether you disclose the information about the third party, you should balance the GDPR’s right of access against the third party’s rights.

Other than this, Section 45(4) of the DPA 2018 specifies special cases when you can withhold personal data of an individual. These include cases when non-disclosure leads to obstruction in an official or legal enquiry, or protection of public or national security.

Therefore, you should be careful about the information that you provide when complying with a subject access request. It is important to understand what information you can withhold to prevent a breach of other’s privacy or to support the public or national interest.

  1. Developing and sending a response

Once you have all everything you need for the subject access request, the last step is to develop and send a response to the individual. Organisations need to provide the following information to the requester:

  • Legal basis for and purpose of processing the personal data of the individual.
  • Third-parties to whom the personal data has been disclosed.
  • Existence of the requester’s rights to the information including the erasure of the personal data and restriction of the processing of the personal data.
  • Expected period for which the personal data will be stored.
  • Categories of personal data.
  • Information about the origin of the personal data.

Most organisations will have provided much of the information above in their privacy policy already and so can reuse it from there.

For sending out the response in 2023, the GDPR requires that you provide the information in a concise, intelligible, transparent, and easily accessible form that is understandable by the individual. Secure online portals or encrypted email are recommended ways to deliver the response securely and efficiently.

Conclusion

Understanding how to deal with a subject access request is an important part of complying with the GDPR in 2023. We have outlined a step-by-step process that you can use to comply with a GDPR subject access request from individuals.

Data protection obligations got you in a muddle? Get on top of them quickly and easily with the CyberSmart Privacy Toolbox.

CyberSmart Privacy Toolbox

Free Information Security Policy for Startups

Cyber threats

A major challenge for startups is figuring out how to invest in cybersecurity.

Despite the financial constraints, it is essential for startups to keep their online security in check, because the consequences are frightening. Statistics show that about 50% of all cyber attacks target small businesses and startups. Often, this is because of a lack of written internal policies.

Without a security policy, there is no reference for what needs to be done when a security threat arises within your startup. An information security policy can be complicated and often expensive to develop, but it is a fundamental component of cybersecurity.

In this article, we present a free information security policy guide for startups.

What should the information security policy cover?

There is no single approach to developing an information security policy that fits all organisations. Despite this, there are certain aspects that every security policy for startups should cover:

  • The security requirements that are going to be met, compulsory ones like GDPR and then either Cyber Essentials, ISO 27001, or the IASME Governance framework.
  • Who is responsible for information security tasks? It can be an internal security expert or a third-party supplier..
  • The startup’s long-term commitment to cybersecurity including what they aim to achieve through the introduction of the policy.

What should be included in the information security policy?

Even though there is no fixed format for an information security policy, given below are some key questions that you should consider when framing your security policy.

  • Who is responsible for your startup’s security?
  • What are your security objectives?
  • How are security incidents reported and managed? How can you learn from them?
  • What type of information do you handle? Does it involve customer information?
  • What ways can you use to protect different types of information?
  • How do you measure risks?
  • How should internet, email, and other communication channels be managed to minimise risks?
  • What training and awareness do the employees need?
  • What responsibilities should be given to employees for securing information?

Areas to cover in an information security policy

There are five general subject areas that should be addressed in an information security policy for startups:

  1. Security measures: Guidelines for virus protection, passwords, confidentiality of data, and levels of access to information.
  2. Disaster recovery: Instructions on how to recover from a disaster such as a data breach. Methods of data backup, including how often they should be made, should also be included.
  3. Standards for technology: Details about the types of hardware, software, and other digital systems that can be purchased by the startup. This area will also cover a list of trusted partners or vendors from where systems are to be bought.
  4. Acceptable use of technology: How should technology such as smartphones, desktop computers, email, and the Internet be used. What are the results of misuse and how can security be improved by limiting access to such technology.
  5. IT services: Information about who will be responsible for providing technical support to employees. Often, this is a member of the IT team, but can be an external partner as well. Guidelines regarding planning, installation, and maintenance of computer systems should also be covered in this area.

Conclusion

Startups are at a constant risk of cyber threats, particularly because of a lack of an effective information security policy. It is important to not only have a security policy in place, but to make sure that it addresses the specific needs of your startup and employees. If you have not developed an information security policy yet, you should consider doing so right away to minimise loss.

CyberSmart recognises the budget and time constraints that most startups have when developing their information security policy. By subscribing to one of our plans you will get access to our free policy packs, sign up today for access. We look forward to assisting you in designing a cost-effective information security policy for fortifying your startup’s security.

4 Ways to Get Your Information Security Policies Under Control

Information security policies

An information security policy is a set of rules and guidelines that an organisation issues for securing its confidential data. Employees of the organisation should understand and follow the information security policy.

In this article, we list effective ways that you can use to develop a information security policy, or beef up your organisation's existing information security policy.

1.     Address the problem of password management

Many organisations, despite knowing about the existence of their security issues, are often confused on how to address them. It might sound obvious, but this is where most of a company’s security failings can be resolved.

For instance security policies must pay much attention to password management. Employees choose their own passwords and are then responsible to manage and control them. However they should be provided with the tools to create, store and access the range of passwords they may need to use.

According to a report by Verizon published in 2017 on data breach investigations, is where things take a turn for the worst. It says that more than 4 out of 5 data breaches are happening due to compromised or weak passwords. In addition, a survey has reported that almost 80% of employees find password management a hassle. An issue that can be easily solved with a password manager.

The scale of the problem here demands that organisations address the clear problem of password management in their information security policy.

2.     Use a holistic approach

As a modern business you should understand the barrier between work life and personal life is becoming more and more indistinct. This idea extends to information security as well. Technology departments must tailor security guidelines around the modern employees work behavior.

Concepts such as BYOD (Bring Your Own Device) are gaining traction nowadays. Organisations need to take a more holistic approach to their information security policies, which involves looking beyond employee work logs and company related passwords.

A single employee, whether in-office or remote, can put the entire organisation’s information security at risk. This makes every employee a possible point of failure for the entire network. The information security policy should take this into consideration and adequately address the risks associated with BYOD. Doing so will allow them to protect the company’s information against attackers.

3.     Educate the employees

Educating employees about information security is an important process when it comes to protecting your organisation’s data.

Regular training sessions that stress the basic concepts of security such as the risks of public networks and password management should be conducted. These sessions can be delivered by internal security experts or third-party security services, depending on the resources available to your organisation.

The most common types of data breaches are caused by the lack of education of employees. Therefore, you should incorporate training and awareness in the organisation’s information security policy. For instance, a security training program can be introduced that requires employees to attend monthly security sessions held within your organisation.

4.     Automate and simplify

Simplify what you can, and automate what you cannot. This simple rule can help you improve your organisation’s information security policy significantly.

A simple information security policy will go a lot further than a binder filled with complex security procedures. This is because employees are more likely to circumvent a complex security measure than a simple one.

You should first attempt to simplify anything that you can within the security policy. For instance, make it clear what the minimum length for passwords should be, rather than just suggesting the use of strong passwords.

For things that cannot be simplified, such as the process of validating online websites, you can make use of tools such as firewalls to prevent employees from violating the policy.

Conclusion

For businesses, information security in today’s world is more of a necessity than a luxury. It is important for an organisation to make a holistic yet simple changes in their approach to information security policies, to address concerns related to cybersecurity.

CyberSmart understands that managing your information security policy can be an excruciating task. If you would like to learn more about how to improve your information security policy, get in touch with us right away. We would love to help you polish your security policy for mitigating risks of cyber attacks.

Understanding GDPR Data Controller in 5 easy steps

GDPR Data Controller

Understanding GDPR Data Controller in 5 easy steps

By now most of have heard of the General Data Protection Regulation (GDPR). But in case you've been carefully avoiding the news since 2017, it's a law put in place by the EU which strengthens the protection of citizens' data.

GDPR has brought with it some very stringent penalties for non-compliance. And if your business isn't yet compliant, you could be at risk of an astronomical fine, as well as lasting brand damage.

However, putting GDPR into practice raises some really big questions. Who is liable in the event of a breach? What is a GDPR data controller?  And who is the GDPR data processor? Let's take each in turn.

1) What is GDPR?

Before we understand the role of a GDPR Data controller, we need to tackle what GDPR is. In simple terms,  GDPR forbids the misuse of EU citizens data. And it applies whether your company is based in the EU or not.

2) Who is the GDPR Data Controller?

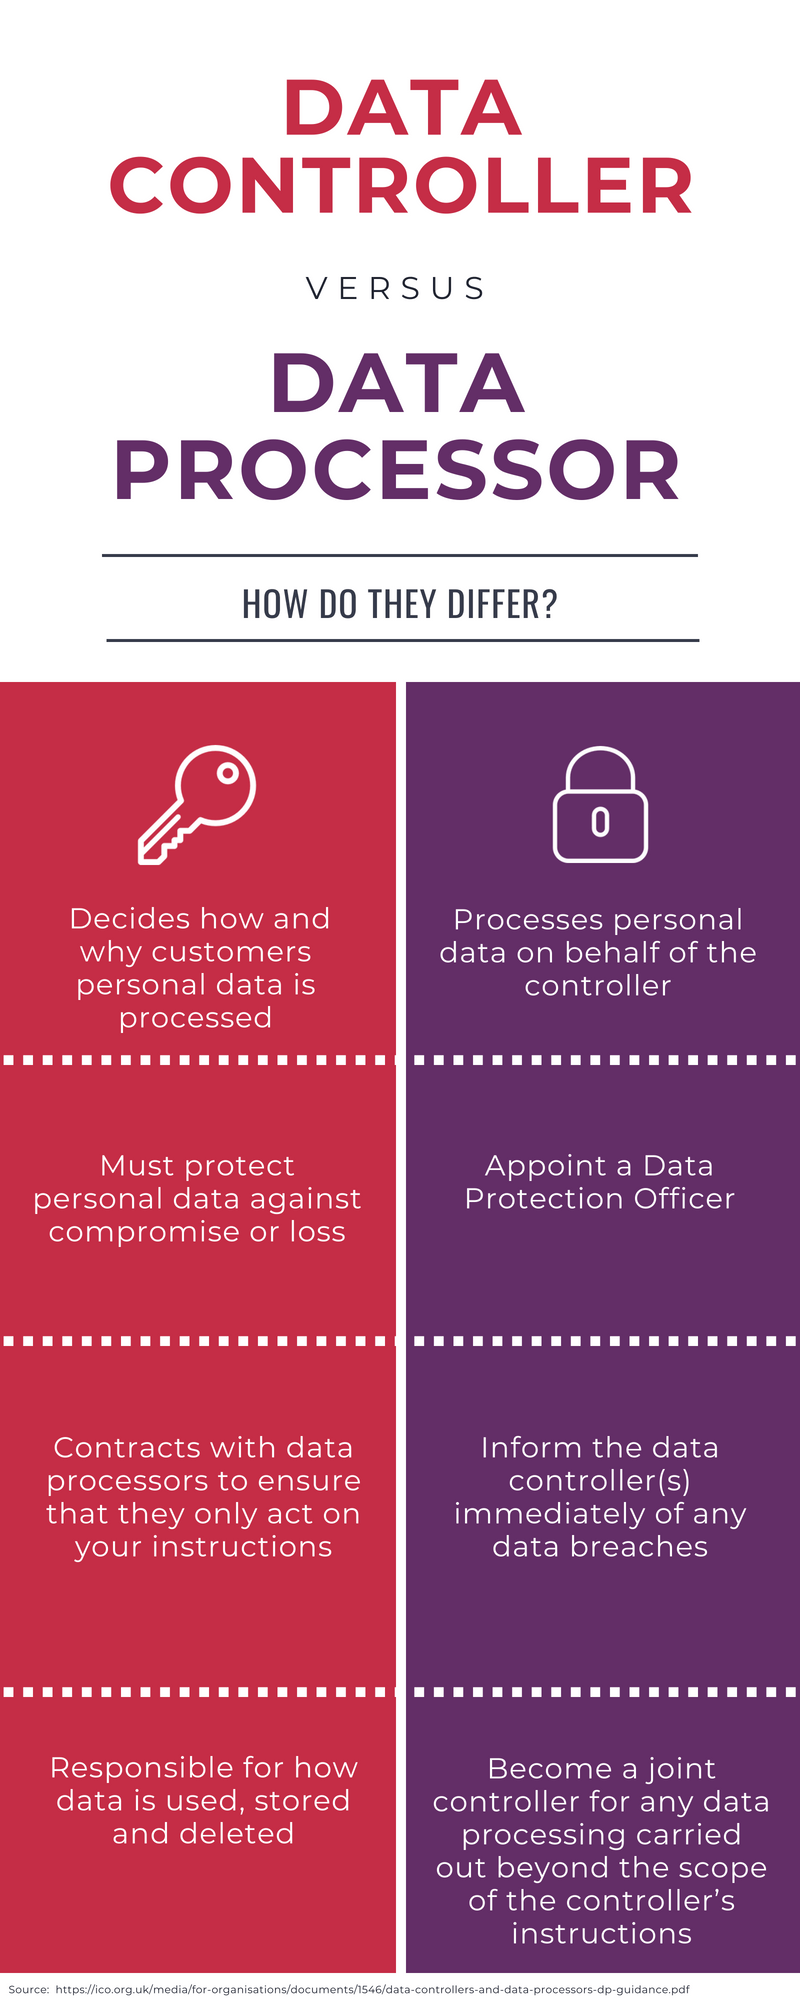
The 'GDPR data controller' is the organisation that decides how and why customers personal data is processed. In other words, it's usually your business itself. You control the data but, crucially, you don't necessarily have to hold or process it. However, even if you don't process it yourself, you're still responsible for how it's used, stored and deleted.

3) What are the GDPR Data Controller's responsibilities?

Under GDPR Data Controllers are obliged to:

  • Protect personal data against compromise or loss by implementing strict technical and organisational measures to secure data
  • Have a legal agreement with your processors to ensure they only act on your instructions and comply with GDPR

4) Who is the GDPR Data Processor?

A data processor, on the other hand, is the company or person who processes personal data on behalf of the controller. To give a few examples, it could be your data storage provider, payroll company, accountant or marketing agency.

5) What are the GDPR Data Processor's responsibilities?

Under GDPR, data processors have a lot more responsibilities, including:

  • Appointing a Data Protection Officer if their business processes sensitive or 'big' data
  • Responsibility for implementing significant security measures
  • Maintaining a record of all data processing operations under their responsibility
  • Inform the data controller(s) immediately of any leaked data
  • Become a joint controller for any data processing they carry out beyond the scope of the controller’s instructions
GDPR Data controller vs Processor
GDPR data controller vs processor

In Summary

GDPR has changed the way we process and control data.  And understanding your role as a data controller, processor or both is crucial – both to avoid legal hot water and protect your customers.

Data protection obligations got you in a muddle? Get on top of them quickly and easily with the CyberSmart Privacy Toolbox.

CyberSmart Privacy Toolbox

9 Secrets To Make Your Medtech Startup Compliant

Running a startup is hard especially in a heavily regulated sector like MedTech and because of the nature of the industry and the types of data Medtech startups typically handle it’s even more important to do compliance the right way.

While you may be compliant with CQC and HIPAA what you may not be aware of is the risk to your companies data and below are a few things you can do today to help you resolve those issues.

medtech compliance

1) Use a password manager, and make your team too

Remembering passwords has always been a hassle and traditionally the only solutions were;

  1. Using the same password everywhere
  2. Forgetting your password
  3. Writing your password down in an insecure location

All of the above solutions are incredibly insecure and present a risk to your organization especially if the passwords are the key to sensitive data that you’re liable for.

A far more secure way of storing and sharing passwords is by using a password manager. We recommend 1Password as it’s simple to use, secure and has excellent team sharing capabilities.

2) Have GDPR compliant privacy policies

You’ll need to update your terms in order to inform your customers and anyone else who you store data on about how you are collecting, processing and sharing their data.

Click here to grab a privacy policy builder for free.

3) Update, update, update

As annoying as it may seem, device manufacturers often release security patches to keep you protected, it’s critical you apply these when they become available otherwise it can lead to irreversible damage.

The CryptoLocker ransomware that hit the NHS in 2017 would have been stopped dead in its tracks if they had patched their machines within the last 2 months.  

uk medtech

Curious to know what the rest of the tips are?

To read the other 6 secrets… you can unlock them below

[emaillocker id="4581"]


4) Use 2FA for all privileged accounts


Two Factor Authentication is an excellent additional measure to ensure your company protects its data.

Even with a compromised username and password an attacker is unable to access the account because you have to authorise access to your account using a code only accessible through your phone.


5) Enable Your Firewall


The last thing you want is a hacker getting access to sensitive data which is a risk by not having a firewall enabled on your network.

In simple terms, a firewall is designed to prevent unauthorised people accessing your private networks connected to the internet. All messages leaving or entering pass through the firewall, which examines each message and blocks those that do not meet the security criteria.

Your Medtech startup needs a firewall to protect your confidential information from those who are not authorised to access it and to protect against malicious users and accidents that originate outside your network.


6) Password enabled

Believe it or not, over 90% of cyber attacks and security breaches arise from human error. With that said not having a secure password enabled on all of your employee devices is not only inadvisable but ultimately reckless.

Imagine this scenario; an employee has a personal data on their laptop and the device does not have a password enabled and the employee loses the laptop. That’s a very scary scenario but easily rectifiable by ensuring that every company or personal device that is used for work has a password enabled.


7) Disk encryption enabled

Enabling disk encryption (filevault in Mac and Bitlocker in Windows) prevents someone with physical access to a machine from extracting all the data. In order to do this on an unencrypted disk, an attacked simply removes the drive from the machine and connects it to a disk reader to access all the contents in plain text.  They can download all documents, pictures, sensitive information as well as see whatever is stored in the browser. Scary stuff. Prevent it by simply enabling disk encryption.


8) Automatic Operating System Update


Another way to prevent malicious attacks is to enable automatic software updates for your operating system. Even if you have a Mac you need to ensure that you’re using the newest operating system as it is a myth that Mac’s cannot be susceptible to threats and malware.

Hackers and malicious cybercriminals use weaknesses in the software and apps to attack your devices and steal identities and sensitive data which is why it is extremely important to ensure that your organisation is using the latest Windows, Mac or Linux software.

But what if they disrupt my work and it takes time out of my schedule? Fortunately, on most operating systems they allow you to schedule when you would like the update to occur so it shouldn’t cause much disruption and in the event that it does at least your data will be safe!


9) Certification


One of the ways to ensure that you’re handling data the correct way is to get a Cyber Essentials certification. Why would you want it? Cyber Essentials is a government-backed certificate to help organisations protect themselves against online threats and is a great way to show suppliers and customers that you take security seriously and you’ve taken steps to secure their data.

Although it’s a great start, Cyber Essentials is really the most basic level of compliance your MedTech startup should be aiming to achieve and if you desire a higher level of compliance then you should be aiming to get the Information Assurance for Small and Medium Enterprises (IASME) certification. This is based on the ISO 27001 (the industry standard for the management of information security) but tailored for small businesses.


Summary


When you do all of the steps above your MedTech startup becomes a few steps closer to becoming compliant however  If you are serious about ensuring that your business data is being protected and you want to improve your business reputation schedule a demo to learn more about Cyber Essentials.

[/emaillocker]

Case Study: Livesmart

Your Company

CyberSmart and Livesmart case study

Why is data protection important to LiveSmart?

LiveSmart aims to create a better world through health analysis and behaviour change. With great power comes great responsibility and we put our clients at the centre of everything we do - including protecting them and their data. We collect both personally identifiable data and sensitive data which means our security needs to be well thought out and very tight to protect our users.

Your Experience

What did you do about compliance before?

For the first two years, compliance was pretty relaxed. The main reason we began addressing our compliance was due to a significant client who required certain things to be in place. Additionally, with GDPR coming into play in May this year it highlighted the importance of data security and compliance. It was very much a hard and fast lesson - building the parachute while you are falling off the cliff so to speak - but it was a lesson well learnt and now that we have everything coming into place the team have a good structure to work within.

Why did you choose to use CyberSmart?

We were referred to CyberSmart by a fellow startup and after our CTO spoke with them, we felt like it would be a simple way to implement the compliance we needed to. Plus - CyberSmart... LiveSmart, seemed meant to be?!

Did it deliver on what you were hoping for?

CyberSmart has been better than we hoped. The team are incredibly friendly and helpful, they simplify some very complex issues into manageable components and make compliance much less scary than it is, while not removing the importance behind it.

Your Advice

What one tip would you give to other MedTech startups in terms of compliance?

You need to feel very certain about what is going on with your data very quickly.

Get crystal clear on what processes exist, where the data flows and who you use to process your data. Without this knowledge, you are at risk of data breaches, data loss and coming under scrutiny from your all-important customers.

In this podcast, our co-founders Jamie Akhtar and Mariella Thanner had a chat with James Gill from GoSquared about the topic of the month: GDPR!
And CyberSmart's story 🙂

(more…)

In this podcast, our co-founders Jamie Akhtar and Mariella Thanner had a chat with James Gill from GoSquared about the topic of the month: GDPR!
And CyberSmart's story 🙂

(more…)

Speaking at the lecture for the Institute of Chartered Accountants in England and Wales in London earlier this year, Elizabeth Denham of the ICO, discussed the role of accountability in GDPR and how people must adjust their mindsets in regard to how we think about data protection as well as what GDPR may actually look like in reality.

(more…)