The emergence of Qilin ransomware as a formidable cyber threat requires robust cybersecurity measures. In this blog, we'll look at how CyberSmart is helping organisations defend against this sophistacted malware.
What is Qilin ransomware?
Qilin ransomware is distinguished by its advanced encryption techniques. It uses a blend of AES (symmetric) and RSA (asymmetric) encryption to secure data. This makes decryption very difficult without the corresponding keys.
Given it's sophistication, you might expect Qilin ransomware to require an eqaully refined delivery method. But that's not the case. Most Qilin attacks are launched via common phishing scams. Once in, it exploits vulnerabilities to spread quickly across systems.
Qilin’s Operational Tactics
Qilin's operational tactics are what make it so tricky to deal with. For example, it can customise its payload to avoid detection or change its approach to exploit the target's weaknesses.
It also uses lateral movement techniques to spread accross networks, encrypting valuable data and altering file extensions. This makes file recovery extremely difficult.
Global Impact
Qilin primarily targets sectors where data access is critical. These include industries like healthcare and manufacturing which offer criminals the chance for maximum disruption.
All this demonstrates the importance of an adaptive approach to cybersecurity to counter the threat – which is where CyberSmart comes in.
CyberSmart’s defensive strategies
CyberSmart's comprehensive suite of tools can significantly mitigate the risks posed by threats like Qilin. Here's how.
1. Endpoint monitoring and compliance assurance
CyberSmart Active Protect continuously monitors endpoints. This ensures that every system in your business complies with the latest security standards. In addition, it quickly identifies vulnerabilities and provides simple instructions for mitigating them – depriving Qilin of gaps to exploit.
2. Education to combat phishing
According to a study from IBM, 95% of all cyberattacks are caused by human error. And, this is especially true of ransomware attacks. CyberSmart Academy focuses on reducing human error. It does this through targeted training to help employees recognise and avoid phishing attempts and other social engineering tactics.
3. Proactive vulnerability management
Routine vulnerability scans are critical in preempting attacks. They help to identify and address the security loopholes threats like Qilin try to wriggle through.
4. Data recovery and continuity planning
With our partners’ support, we encourage all businesses to implement data recovery and backup plans. This approach minimises the downtime and operational impact caused by a breach. So, even if the worst-case scenario happens, you’ll recover quickly.
5. Install and maintain anti-malware solutions
Although CyberSmart doesn’t directly handle malware detection, it ensures that anti-malware solutions are installed and configured correctly. Again, this provides confidence that your whole network is adequately protected.
The need for layered cybersecurity strategies
The threat Qilin poses highlights the need for a layered cybersecurity strategy. What do we mean by that?
Well, in short, protection against sophisticated ransomware is about more than anti-malware tools. Organisations must maintain rigorous update protocols, regularly monitor systems and enhance employee awareness to properly mitigate risk.
By integrating CyberSmart's advanced security solutions, businesses can strengthen their defences and ensure greater resilience against cyber threats.
Jamie Akhtar, CEO at CyberSmart, adds:
"In an era where cyber threats are increasingly sophisticated, it's vital that our defences not only match but exceed the level of threat we face. Sectors like healthcare, previously considered off-limits, are now actively targeted due to legacy systems, interconnectedness, and the necessity to restore services quickly. CyberSmart is committed to collaborating with our extensive partner network to deliver complete cyber confidence for organisations against complex threats like the Qilin ransomware. This commitment is crucial for maintaining the trust and safety of the digital systems that power our everyday lives."
Is Cyber Essentials mandatory? Who needs Cyber Essentials and why
Cyber Essentials is a UK government-backed scheme that helps organisations protect themselves against common cyber threats. Achieving Cyber Essentials certification demonstrates a commitment to cybersecurity. Unlike GDPR, Cyber Essentials isn't mandatory for UK businesses.
The Cyber Essentials scheme isn’t covered by binding regulation. Instead, it provides impartial guidance to help businesses improve their cyber posture, built around five security controls: firewalls, secure configuration, user access control, malware protection, and security update management. It's a great way for any business to improve its cyber credentials, and in some cases it's mandatory. Learn more about the conditions under which certification can be necessary in this blog post.
Government Contracts
Cyber Essentials is mandatory for businesses looking for specific government contracts.
Unless your business achieves Cyber Essentials, you will not be able to bid for such contracts at all. These contracts involve the handling of personal information or delivering certain IT products and services.
For example:
Handling the personal information of any UK citizens; e.g., bank details or home addresses
Handling the personal information of any government employees, ministers, or advisors; e.g., payroll or expenses information
Delivering IT products or services designed to store, process, or transfer data
Cyber Essentials certification is mandated for businesses entering into these contracts and demonstrates that they have achieved the standards and meet the technical requirements defined in by the scheme.
For all businesses looking to bid for government contracts that involve one of the above characteristics, it makes sense to achieve Cyber Essential certification first.
Ministry of Defence Contracts
The UK Ministry of Defence (MoD) requires all its suppliers to comply with Cyber Essentials.The MoD has previously stated that this requirement must flow down to the supply chain. It mandates that both organisations directly conducting business with the MoD, and organisations delivering to the MoD supply chain must be Cyber Essentials certified.
Importance of Cyber Essentials
Should your business get a Cyber Essentials certification even if it isn’t mandatory?
Yes. Even if you're not bidding for government or MoD contracts, you could benefit from having Cyber Essentials.
For SMEs with little or no IT support or expertise, it provides a basic first step towards cybersecurity. Most SMEs lack adequate cybersecurity measures because they mistakenly feel that they're not a target. This is a misconception:
90% of businesses and 94% of charities who experienced at least one type of cyber crime
1.5 million UK businesses hit by cybercrime in 2023
Taking the steps to Cyber Essentials
Considering Cyber Essentials for your business but not sure where to start? We've got a guide for that. Our guide to certifications in the UK has everything you need to know about Cyber Essentials and who needs it. Read it here.
7 Key takeaways from DSIT’s Cyber Security Breaches Survey 2024
Every spring the Department for Science Innovation & Technology (DSIT) releases its Cyber Security Breaches Survey. Always hotly anticipated throughout the cybersecurity sector, it acts as a ‘temperature check’ of security and resilience within UK cyberspace.
Although the report primarily intends to inform UK government policy, that doesn’t mean it isn’t useful to small businesses. In fact, the report is a bit of a lodestar for anyone interested in cybersecurity. It gives us an idea of the threats we face, how businesses are dealing with them, and what we can do to improve our collective security.
With that in mind, here are our key takeaways from the Cyber Security Breaches Survey 2024.
1. Breaches remain common
This won’t be particularly surprising to anyone but successful cybersecurity breaches remained commonplace in the last 12 months. According to DSIT’s research, half of businesses (50%) and just under a third of charities (32%) reported experiencing some form of breach.
These figures are highest for medium businesses (70%), large businesses (74%) and high-income charities with £500,000 or more in annual income (66%). However, this isn’t to say small (10-49 employees) and micro (1-9) businesses are immune. 47% of micro-businesses and 58% of small businesses were hit with a breach in the last year.
2. The cost of a breach remains low, but constant
This one is a mixed bag. One positive is that DSIT reports the average cost of a single breach across all businesses surveyed was £1,205. That’s considerably lower than figures released in reports like IBM’s Cost of a Data Breach 2023, even when we consider that the average rises to £10,830 for large and medium businesses.
Unfortunately, this isn’t the whole story. Although the headline figure for the cost of a breach is low, companies are being attacked with frightening regularity. Over half of businesses (53%) and just under half of charities (45%) reported that this happens once a month or more often. Grimmer still, a third of businesses and a fifth of charities say that they were attacked at least once a week.
This means that even if the cost of a single breach is low, many businesses are being hit multiple times a year, making the cumulative impact of attacks far higher. What’s more, while larger organisations may be able to swallow these recurring costs, their impact could be ruinous for SMEs.
3. Phishing scams are still the number one threat
By this point, most of us have first-hand experience of a phishing scam. They come in many forms, from speculative email campaigns to more targeted attacks through social media platforms like Facebook Messenger and spear phishing.
So it’s no surprise to see phishing scams at the top of DSIT’s list of most common threats. 84% of businesses and 83% of charities reported being targeted by one in the last 12 months.
However, more interesting is that the second most common threat was ‘others impersonating organisations in emails or online’ (35% of businesses and 37% of charities). This demonstrates that cybercriminals are leaning on social engineering techniques to launch attacks, rather than more technological approaches like malware and ransomware.
There are a couple of possible reasons for this. Firstly, social engineering attacks use our human nature against us, making them more difficult to defend against. Second, social engineering doesn’t require any specialist tools or tech knowledge, just a familiarity with the techniques, meaning the barrier to entry is lower for would-be scammers.
4. Does Cyber Essentials certification have an awareness problem?
Cyber Essentials certification turns ten this June. And, although the scheme has helped thousands of businesses improve their cybersecurity, it appears to have an awareness problem.
Just 12% of businesses and 11% of charities are aware of the Cyber Essentials scheme. These figures are roughly consistent with 2023 but represent a decline over the last 2-3 years. This decline is also more pronounced among smaller businesses with medium businesses (43%) and large businesses (59%) more aware.
More worrying still, only 3% of businesses and charities report adhering to Cyber Essentials. However, this does come with a caveat that a higher proportion of them (22% of businesses and 14% of charities) report having technical controls in all five areas covered by Cyber Essentials.
5. Businesses aren’t prepared for supply chain risks
Although the report reveals organisations have broadly improved when it comes to cyber risk management, there’s still one glaring omission – supply chain risks. Only one in ten businesses say they review supplier risk (11%, vs. 9% of charities). Given that supply chain attacks are predicted to cost the global economy $138 billion by 2031 this is an area that needs urgent attention in the coming years.
Despite many businesses stating that they’d take action following a cyber incident, very few have anything concrete in place to establish what those steps are. Just 22% of businesses and 19% of charities have a formal incident response plan. Once again, these figures are largely being driven by SMEs; 73% of large businesses have one.
What this suggests is that small businesses are ill-prepared for the worst-case scenario. Creating an incident response plan or security policy can be time-consuming and tricky if you don’t know where to start. SMEs need help, through tools like templates and policy management to better prepare themselves.
Alongside this, when a breach does happen, external reporting of it is uncommon. Just over a third of businesses (34%) and charities (37%) reported a breach outside their organisation. Even then, this wasn’t usually to the National Cyber Security Centre (NCSC) or Information Commissioners Office (ICO), but to their managed service provider or IT supplier. This indicates that vast swathes of cybercrime are still going unreported.
7. Basic cyber hygiene is improving
Finally, let’s end with a real positive. Cyber hygiene – by which we mean basic cyber controls – is on the up across all businesses. Most cyber threats are relatively unsophisticated so organisations can go a long way towards protecting themselves by simply adopting some simple measures.
The good news is that a majority of businesses and charities have a broad range of these measures in place. These include:
using up-to-date malware protection (up from 76% to 83%)
restricting admin rights (up from 67% to 73%)
network firewalls (up from 66% to 75%)
agreed processes for phishing emails (up from 48% to 54%)
And, even more promising, these trends are a reversal of the decline in cyber hygiene we’ve seen over the past few years. This shift is being driven by micro and small businesses, demonstrating that despite the worrying trends in awareness surrounding Cyber Essentials, basic security recommendations are having some cut through.
The move will streamline and simplify Essential Eight assessment for Australian SMEs and MSPs
Wednesday 08 May 2024 – London, UK:CyberSmart, the UK’s leading provider of complete cyber confidence to UK SMEs is excited to announce its partnership with Australian technology distributor, HAT Distribution. The partnership will provide businesses in Australia with fast, hassle-free Essential Eight assessment and year-round assurance.
CyberSmart is the world’s first complete SME solution, offering all-in-one cybersecurity monitoring, optimisation and training, proven to defend against cyber threats. With its user-friendly platform, simplified progression framework, year-round protection and unlimited support, implementing Essential Eight controls has never been easier for Australian businesses.
As cybercrime escalates in Australia, with 94,000 incidents reported in 2023* alone (equivalent to one report every 6 minutes!), completing Essential Eight – the recognised Australian government standard for cybersecurity – is not just advantageous but also crucial in certain industries. CyberSmart’s solutions are specifically designed to help businesses implement these strategies effectively so they can attain and maintain a government-approved standard of cybersecurity, reducing cyber risk.
The platform is tailored for MSPs and SMEs, who represent a critical segment in the economy but often face challenges with maintaining robust cyber defences due to limited resources and expertise. With CyberSmart, MSPs can enhance their service offerings by delivering comprehensive and cost-effective solutions to their clients, while SMBs gain access to straightforward Essential Eight assessment, without the need for extensive resources.
Australian SMEs will also gain access to CyberSmart Active Protect, a powerful on-device agent that delivers comprehensive endpoint monitoring, risk management, policy enforcement, and cybersecurity awareness training. Active Protect regularly monitors and reports the status of a device by running through a series of security controls, identifying any vulnerabilities and providing simple step-by-step walkthroughs on how to fix them.
Jamie Ahktar, CEO at CyberSmart said, “We’re excited to expand into the Australian market with HAT Distribution. Cybercrime is a worldwide business, and the interconnected nature of global commerce in 2024 means that the more geographies we are able to offer SMBs complete cyber confidence in, the better. Almost half of Australians reported experiencing cybercrime in 2023, and we believe that the comprehensive protection we’re bringing to the Australian market will be able to limit both the success and impact of these incidents moving forward.”
Josh Gammer, General Manager of HAT Distribution said, “Amidst the ever-evolving cyber threat landscape, we are thrilled to partner with CyberSmart, a leader in cybersecurity innovation, to help more Australian businesses comply with the government’s endorsed Essential Eight framework.
“With CyberSmart, even smaller players gain access to the tools required for assessment, and for MSPs, the partnership is a consultative business opportunity to guide their clients on a transformative journey toward stronger cyber defences.”
For more information about CyberSmart’s cybersecurity solution for Australia, please visit https://www.cybersmart.com/au
What is the MITRE ATT&CK framework and how can it help your business?
Hackers sit somewhere between masterminds and master criminals, depending on who you ask. There’s a fascination and frustration that surrounds them and how they do their dirty work.
Ever wanted to get inside the mind of a hacker to help protect your business from threats like malware? The MITRE ATT&CK framework is the perfect place to start.
What is the MITRE ATT&CK framework?
The MITRE ATT&CK framework is a detailed knowledge base of the tactics cybercriminals use to target victims. Using real-world examples, it shows you how hackers prepare, launch, and execute attacks.
The framework matrix is split into tactics and techniques. A tactic is a goal the cybercriminal wants to achieve, such as accessing credentials. A technique is the action or actions that achieve the tactical goal, such as brute force.
It exists to help businesses understand how cybercriminals behave in the preparation and execution of an attack. This helps raise awareness of common threats and how you can detect them in action.
Discovery – gathering system and network intelligence
Lateral movement – controlling remote systems
Collection – gathering relevant, goal-related information
Command and control – communicating with systems without detection
Exfiltration – stealing network data gathered at the collection stage
Impact – disrupting service availability and data integrity
Each tactic includes a list of techniques that explain how a hacker achieves their goal, alongside mitigation information, detection tips, and references for further reading. These are updated twice a year from public threat intelligence and incident reporting, so the information stays relevant.
It’s suitable for any organisation using:
Windows, macOS, or Linux IT systems
Network infrastructure devices
Container technologies
Cloud services such as IaaS, SaaS, Office 365
Android and iOS mobile devices
Keeping your organisation secure
The framework is a great resource to include in your cybersecurity strategy.
It encourages collaboration and information sharing, is easy-to-follow, and helps you improve your knowledge and cybersecurity posture. And, it’s free.
Use it alongside other cyber defence methods to give you broad coverage against common threats, including:
Active monitoring
Investing in an outsourced security operation centre for 24/7 protection from cyber threats on all devices that access company data.
Software
Using robust antivirus or anti-malware software to prevent, detect, and remove malicious software.
With such a powerful resource at your fingertips, you’re only going to benefit by including the MITRE ATT&CK framework in your cybersecurity strategy. Share it with your colleagues so you can all play an active role in protecting your organisation from attacks.
Social media savvy: privacy settings and security on social platforms
Social media platforms connect us with friends, family, and colleagues but can also be a goldmine for attackers. This blog post looks at the world of social media privacy and security, exploring the potential threats and steps you can take to protect yourself (and your business) from them.
Social media at home and work
Social media plays a big role in both our personal and professional lives. In our personal lives, we use platforms like Facebook, Instagram, and Twitter to stay connected with loved ones, share updates, and follow our interests.
In our work lives, LinkedIn is a go-to for professional networking, while companies use platforms like Twitter and Facebook for marketing and customer service.No matter how we use social media, it's crucial to understand the potential risks.
The threats you face when using social media
Sharing information online comes with inherent risks. Common threats include:
Social engineering: Attackers might try to manipulate you into revealing personal information or clicking on malicious links.
Malware: Links or downloads shared on social media can infect your device with malware that steals data or disrupts your system.
Phishing scams: Fake accounts or posts might try to trick you into sending money or sharing personal details. In addition, spear phishers will often use social media to gather background information on targets.
Privacy violations: Without carefully calibrated settings, your personal information and online activity could be exposed to unintended audiences.
Social media scams in practice
Operation Dreamjob
In 2023 cybercriminals from the Lazarus group, an alleged North Korean state-sponsored hacking organisation, targeted employees at a Spanish-based aerospace company.
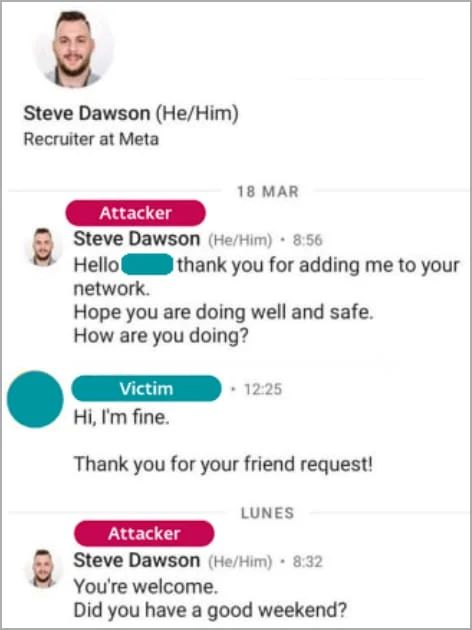
Under the campaign ‘Operation Dreamjob’, the cybercriminals identified employees on LinkedIn, introduced themself as a recruiter from Meta and commenced a fake recruitment process.
As the victim progressed through the rounds of the ‘recruitment process’, they were asked to demonstrate their competency by downloading and completing a quiz.
In this case, the victim downloaded the quiz using a work computer. Unfortunately, the download contained more than a quiz and the attackers used this to access the company’s critical systems.
This followed a similar attack by the same group in 2022 which used fake LinkedIn job offers to steal $625 million from the Ronin Network, a blockchain network that powers the popular crypto games Axie Infinity and Axie DAO.
Below is an example of what these attacks typically look like.
A bad romance
In my previous life as a cyber detective, I saw firsthand how cybercriminals frequently harness social media. This ranged from using social media platforms to execute their attacks, like above, or obtaining information from them.
In a previous blog post, I wrote about the case of a business owner who lost thousands of pounds after falling victim to social engineering. In this attack, the cybercriminal used open-source research to find out information about their target - the business owner. The business owners' use of social media to advertise their business enabled the cybercriminal to locate a business website, mobile number and key information about the business owner that enabled the attacker to go on and effectively build a relationship with the victim.
Here are some key steps to take control of your social media privacy and security.
1. Review and adjust privacy settings
Every social media platform offers privacy settings that allow you to control who sees your posts and profile information. Where possible, set everything to 'private' or 'followers only'.
2. Be mindful of what you share
Think twice before sharing personal details like your birthday, address, or phone number. Could this information be used against you?
3. Beware of suspicious links and messages
Don't click on links or download attachments from unknown senders.
These measures add an extra layer of security to your accounts and prevent you from being the low-hanging fruit cybercriminals target.
6. Be cautious about location-sharing
Consider disabling location sharing on your posts or using it selectively. Also consider what location information is in the backgrounds of your photos, as this too can be used by cybercriminals.
7. Limit third-party app access
Review and restrict third-party apps’ access to your social media accounts, including add-ons and plug-ins. And, if you need to use these tools, ensure they're reputable first.
The founding fathers of social media created it with a utopian vision of connectivity. And, although social media has fallen a long way from those halcyon days, that doesn’t mean you can’t use it safely.
By understanding the risks and taking proactive measures, you can create a safer and more secure social media experience. Remember, privacy and security are ongoing processes, so regularly review your settings and stay informed about evolving threats.
Want to know more about the threats facing small businesses? Check out our guide to SMEs and the cost of living crisis. In it, you’ll find insight from real small businesses on the threats they face and practical suggestions for mitigating them.
What is quishing and how can you protect your business?
Quishing or QRishing is a brand of phishing scam that uses QR codes to trick victims into downloading malware or sharing personal data. Despite its unthreatening name, quishing poses a real risk to businesses. However, with the right knowledge, you can stop your business from falling prey to these attacks, read on for everything you need to know.
Why QR codes?
Read most media and you’ll see plenty of stories about the security threat posed by AI or the latest nation-state attack. However, cybercrime doesn’t have to involve the latest tech or be the height of nefarious sophistication. In fact, it’s often simple scams that get you.
QR codes have been around for almost three decades. Very few people think of them as on the bleeding edge of technology, more something you use to attend an event or scan for a marketing gimmick. Yet, since they’ve seen a resurgence in their use post-pandemic, they’ve stirred up a hornet’s nest of security problems.
The most prominent of these problems is quishing. QR code technology might not be sophisticated by today’s standards, but it does lend itself well to phishing scams.
Why? Unlike a URL or email address, QR codes are hard to evaluate for legitimacy. A QR code is opaque to the human eye, making it indecipherable without a scanner. This means that by the time the victim has realised the QR code is bogus, it’s often too late.
Phishing is by far the most common form of cyberattack. According to the DCMS Cyber Security Breaches Survey 2024, 84% of businesses in the UK experienced a phishing attack in 2023.
When it comes to quishing specifically, the scant figures available are equally ominous. Research from cybersecurity company Vade detected over 20,600 quishing attacks in one seven-day period in 2023.
What’s more, it isn’t just the spectre of falling victim that threatens businesses. If your business uses QR codes, cybercriminals could hijack them to target your customers.
What does a quishing attack look like?
Quishing attacks are versatile and can take any number of forms. We’ve seen examples of them conducted in person, with a scammer approaching the victim and asking them to scan a QR code for some sort of benefit. However, the most common approach is to send an email, much like a typical phishing scam, with a QR code included.
This approach was exemplified by the Microsoft 365 quishing attack in 2023. The attack began with a phishing email asking users to reactivate their multi-factor authentication (MFA). The email used the Microsoft Authenticator logo giving it a veneer of legitimacy. Once the victim scanned the code and clicked the embedded link they were sent to a webpage that infected their device with malware.
Microsoft eventually managed to get the situation under control and issued these instructions for detecting a scam, but not before thousands of users had been attacked.
The most obvious fallout from a successful quishing scam is financial harm.Research from BDO found that among the six in ten organisations in the UK hit by phishing scams the average loss was around £245,000.
What are the consequences of a breach?
However, the potential consequences can hit more than your pocket. If the scammers manage to steal customer’s personal data, you could also be looking at serious reputational damage and regulatory fines. What’s more, your standing among partners and suppliers could take a hit too.
How can you protect your business?
Like all phishing attacks, quishing relies on social engineering to trick victims. This means it can be tricky to recognise a bogus QR code, particularly when it’s attached to a seemingly legitimate message. But that doesn’t mean it’s impossible. Here are a few things you can do to protect your business.
1. Provide cyber awareness training for staff
Staff security training is the most important tool for protecting your business from quishing attacks. The rationale behind this is simple. If your employees aren’t aware of what cyber threats look like, they’re much more likely to fall foul of them.
Cyber awareness training can go a long way towards resolving this problem. It can give them the basic cyber skills to spot and avoid a potential threat. And, it needn’t be extensive or time-consuming, just a few hours a month on the basics and regular updates on new threats can make all the difference.
2. Deploy MFA
Multi-factor authentication (MFA) adds an extra layer of security for your business, making it much harder for hackers to gain access. You likely already use MFA in some aspect of your online life, it’s now a requirement for most banking accounts. But if you haven’t already, switch it on for any system or application your business uses.
3. Use an Anti-malware tool
Anti-malware software focuses on defending against the latest threats. An effective tool should protect your business against ransomware, spyware, sophisticated phishing attacks, and zero-day attacks. Most anti-malware tools constantly update their rules, meaning you’ll be protected swiftly against any new threats, including the malware injected by quishing scams.
4. Protect your network
Your network is the gateway to your business. It’s what spear phishers are ultimately trying to gain access to when they attack you. Through it, a hacker can access just about anything your organisation does. So protect it, and protect it well. The four most simple things you can do to strengthen your network immediately are:
Install a network firewall to filter network traffic
Use a VPN to encrypt network traffic
Segment your network to eliminate single points of failure
Regularly update your router’s firmware
5. Follow software providers’ advice
As we saw in the example earlier, cybercriminals will often try to imitate software providers when launching a quishing attack. Software providers such as Microsoft are all too aware of the threat and many have released guidance on how to counter a scam.
6. Limit user access
Limit who has access to what within your business. Staff should only have admin rights within a system or application if it’s critical for their role. It might sound a bit draconian, but the reasoning behind it is sound. If a cybercriminal compromises a user account through a phishing campaign, the fewer permissions that account has the less damage a hacker can do.
7. Tie it all together
Don’t be put off by the length of the list above. If you’re unsure about where to start, complete a cybersecurity accreditation like Cyber Essentials or ISO27001 certification.
These certifications can help you adopt good cybersecurity practices (including all of the above) and build your cyber confidence.
However, you also need something that keeps your cybersecurity baseline consistently high, year-round. This is where continuous cybersecurity monitoring tools like CyberSmart Active Protect can help by giving you an ‘always-on’ view of your business’s defences.
Want to know more about the threats facing small businesses? Check out our guide to SMEs and the cost of living crisis. In it, you’ll find insight from real small businesses on the threats they face and practical suggestions for mitigating them.
Antivirus and anti-malware are the basic building blocks for any small and medium enterprise’s (SME) cybersecurity strategy. They’re the most well-known cybersecurity tools, and it’s rare to find a business that doesn’t use one.
But do you know what they protect you from, the difference between an antivirus and an anti-malware, and whether you need both? Let’s explore these key talking points.
Malware vs viruses
Before discussing the merits of the two types of software, we must tackle the difference between viruses and malware. Most people assume that the two things are synonymous. Isn’t ‘virus’ just a slightly dated way to say ‘malware’?
That’s almost correct. However, this is the world of cybersecurity, so things are always a little more complicated than they first appear.
The term ‘virus’ describes malicious code that can reproduce repeatedly – just like a biological virus. The code damages your device by corrupting your system or destroying data. Viruses are also usually considered legacy threats that have existed for a long time, and today’s cybercriminals rarely use them.
On the other hand, malware is an umbrella term that refers to many different threats. These range from ransomware to spyware and even some newer viruses (confusing, we know). The key difference is its novelty.
The threats under the term malware are new, constantly evolving, and very much in use among modern cybercriminals. So, antivirus software providers have upped their game to protect customers.
Antivirus vs anti-malware: the key differences explained
As you might expect, antivirus usually deals with older, more established cyber threats. To illustrate, think of warnings from the noughties – endless error pop-ups, trojan horses, and worm viruses. These attacks typically enter your business through tried and tested routes such as email attachments, corrupted USBs, and other standard cyber threat delivery methods.
These cyber nasties are generally very predictable and easy to counter. However, they can still do plenty of damage if left unchecked.
Anti-malware
Anti-malware software focuses on defending against the latest threats. A good anti-malware protects your business against ransomware, spyware, sophisticated phishing attacks, and zero-day attacks. Anti-malware usually updates its rules faster than an antivirus, making it the best protection against any new threats you might encounter.
Antivirus vs. anti-malware: which should you choose?
At this point, you might be wondering why you need an antivirus if anti-malware can protect your devices against the most common types of cybercrime.
Although this is a valid question, it’s a risky way to approach cybersecurity. Sure, most of the threats covered by antivirus might be dated and rarely used by the bad guys. However, that doesn’t mean they no longer exist or that they can’t still give you a significant cybersecurity headache.
Doing without antivirus is a bit like a state deciding to focus exclusively on protection from nuclear threats while neglecting the potential for invasion by land. It’s a flawed approach that leaves your business open to attack.Instead, it’s better to take a layered approach to your cybersecurity – by which we mean installing antivirus and anti-malware software to protect your business against new and old threats.
Choosing cybersecurity solutions isn’t an either/or dilemma
Antivirus and anti-malware aren't mutually exclusive. A truly effective cybersecurity strategy includes tools, training, and measures to counter any threat. Something as simple as a Cyber Essentials certification ensures your business complies with the basic requirements to deter cyber threats. This is because the steps to get qualified include:
Data encryption
Firewalls
User access management
Software and operating system updates
You get support and clear step-by-step instructions for mitigating malware in your business so you don’t overlook any vulnerabilities. Learn how easy it is to get certified today.
Malware-as-a-Service and the rise of DIY cybercrime
Cybercriminals are always looking for the next sophisticated method to target businesses. And as a small business owner, it can sometimes feel impossible to keep up with the latest developments. However, knowledge is power, which is why we bring you regular updates. Let’s explore the latest trends in DIY cybercrime and Malware-as-a-Service, and how to mitigate them.
What is Malware-as-a-Service?
Malware-as-a-Service (MaaS) is a business model used by cybercriminals known as MaaS operators. MaaS operators lease their software, hardware, and related infrastructure to others for a fee. This enables malicious criminals to distribute pre-made malware, even with minimal coding skills.
You might’ve heard of similar terms like a Software-as-a-Service model, where an end-user purchases a pre-made software solution for their business or personal use. MaaS is the same concept but with malicious software. MaaS operators distribute the software on the dark web and sometimes even provide customer support to nefarious clientele.
DIY cybercrime, or do-it-yourself cybercrime, is where a cybercriminal uses a pre-made solution to execute malicious activity. For example, they purchase ready-to-use Malware-as-a-Service, quickly get it up and running, and then use it to distribute malware to their target.
The worrying thing about DIY cybercrime is that anyone can purchase and use an off-the-shelf tool. It has never been easier for criminals to distribute malware, engage in phishing, and more.
At this point, you might be shaking your head and thinking, ‘D-I-WHY?!’ But don’t worry, all is not lost. You can dramatically reduce the threat to your business by putting the correct cybersecurity solutions in place.
Malware-as-a-Service examples
ZeuS/ZBOT
ZeuS, or ZBOT, is a MaaS package that runs on Microsoft Windows. It was designed to steal sensitive information like banking credentials. First detected in 2007, it has successfully targeted large organizations like Amazon, Bank of America, and NASA.
SpyEye
SpyEye is a computer program that infects victims' devices and steals sensitive data. In a rare case of justice, the creator of SpyEye was caught and sentenced to nine and half years in US federal prison. However, this hasn’t stopped the presence of SpyEye across the internet.
Blackhole Exploit Kit
Released on an underground Russian hacking platform, Blackhole Exploit Kit made up 29% of all web threats in 2012, making it a significant threat. Since then, the exploit kit model has continued to transform and is still widely used by cybercriminals.
How to prevent Malware-as-a-Service attacks
Like all criminal activity, MaaS isn’t a threat that’ll soon disappear. But there are several simple steps to protect your business. Here’s what we think you should prioritise.
Educate employees
Most people don’t have in-depth knowledge of malware and DIY cybercrime. Due to the ever-changing nature of cybercrime, your employees must play a part in protecting your business. Make sure people know how to spot a malware attack in your business and provide them with training and resources so they stay informed.
Complete a cybersecurity certification
A cybersecurity certification, like Cyber Essentials, is an excellent way to quickly implement robust security measures in your business. This is because the steps to qualify help you attain certification status and proactively mitigate against malware.
Additionally, many companies find that the steps help them identify overlooked vulnerabilities in their business that they might otherwise be unaware of. It covers a broad range of factors like:
Certification is a great starting point for putting in place the right defences and building your cyber confidence. However, cybercriminals won't only attack on certification day, so you need a way of monitoring your defences year-round. You could approach this manually, but beware it'll be time-consuming and require familiarity with cybersecurity best practices.
An alternative is to use a cybersecurity monitoring service, like CyberSmart Active Protect, which checks for vulnerabilities around the clock and ensures everyone in your business is working safely. Likewise, a vulnerability management tool can help you get ahead of the latest developments in cybercrime.
Want to know more about the threats facing small businesses like yours? Then have a read of our SME cost of living crisis report. It's packed full of insight into how small businesses are defending themselves during an economic downturn.
For many people, hearing the phrase ‘spear phishing’ conjures up images of intrepid divers hunting for their dinner in azure seas. However, much like ‘trojan horse’ the term has come to meet something quite different. According to research, 50% of businesses were victims of spear phishing in 2022, with the typical organisation receiving 5 attacks daily. So the threat is real. But how does a spear phishing attack work? How does it differ from a phishing attack? Most critically, what can your business do to protect itself?
How a spear phishing attack works
Spear phishing is a form of phishing attack. However, unlike the ‘spray and pray’ approach of a conventional attack, spear phishing targets specific individuals, usually within a single organisation. The ‘spear’ in its name reflects this specific targeting. A spear-phishing attack typically aims to gain privileged access. This is used to steal sensitive data or infect the target (and often their wider network) with malware.
Unlike your common-or-garden phishing attack, spear phishers assiduously research their targets. They do this so that the eventual attack appears to come from a trusted source, such as a boss or client. Spear phishing also uses social engineering techniques to dupe the victim into clicking on a link or granting access.
We’ve established what a spear phishing attack is, but how do they work? Typically, a spear phishing attack has five stages. These are:
1. Goal setting
The first stage is a simple one. After deciding to turn to crime, the bad guys start by plotting out what they want to achieve with the attack. It could be stealing ransomable data, causing disruption or myriad other goals.
2. Picking the target(s)
This stage usually involves a round of preliminary research. Which organisation should they target? Who works at the business they want to target? Are they likely to have access to the data or systems they want to access? Who are the senior leaders within the target organisation? How can they be reached?
These are the questions a cybercriminal will seek to answer as they lay the groundwork. Once they have, it’s time to go a level deeper.
3. Building a profile of the victim(s)
By now, the cybercriminals should have a solid idea of which organisation they want to attack and who within it makes the best targets. Next, it’s a case of getting to know their victims.
Spear phishers scour social media profiles and platforms like LinkedIn to discover contact details, the victim’s network of family and friends, business contacts, where they shop or bank, and even places they frequent. This information allows cybercriminals to build a rich profile of who the target is, allowing them to tailor the scam specifically to the victim.
4. Initiate contact and use social engineering techniques
Now the scheme has been devised, the cybercriminals launch their attack. Spear phishing emails usually use social engineering techniques such as creating a sense of urgency, trust or authority. The key to a good spear phishing scam is that it appears legitimate because the ‘sender’ is an individual or company the victim regularly engages with and contains at least some, authentic information.
The most expensive spear phishing attacks of all time
1. Google and Facebook
This is perhaps the most famous phishing scam of all time. Between 2013 and 2015, Google and Facebook fell prey to a £77m Spear phishing campaign. Essentially, a Lithuanian cybercriminal named Evaldas Rimasauskas posed as an Asian supplier of both companies, sending fake invoices to key leadership figures within the tech firms.
Rimasauskas was eventually caught but not before he’d managed to defraud two of the largest companies in the world out of an eye-watering sum.
2. Ubiquiti Networks
In 2015, networking giant Ubiquiti was hit with a £36.7m spear phishing campaign. According to the company’s statement on the breach, it resulted from “employee impersonation and fraudulent requests from an outside entity targeting the Company’s finance department.” In other words, the company fell victim to a classic spear phishing attack.
3. Colonial Pipeline
Of all the incidents on this list, the Colonial Pipeline attack in 2021 is the most sinister. It remains the largest publicly disclosed attack on US infrastructure to date. The breach was so serious that the US government considered it a national security threat.
The attack had several stages. First, the hacker group DarkSide discovered a vulnerability exposed in a previous breach. A Colonial Pipeline employee had likely used the same VPN password in another location, exposing the company’s network. Next, the hackers used this password to access the Colonial Pipeline, stealing over 100 gigabytes of data in just two hours. Following this, DarkSide injected the network with ransomware that infected several systems, including billing and accounting. We don’t have a definitive figure for how much the breach cost Colonial Pipeline. We know the company paid DarkSide £3.47m for the decryption key for the ransomed data. However, the real losses could have been astronomical. Colonial Pipeline supplies oil to the entire US East Coast and the attack shut down its operations for a week. This meant the non-delivery of approximately 20 billion gallons of oil, worth around £2.7 billion at the time.
Spear phishing affects small businesses too
Although all of the examples above feature globe-bestriding businesses, this doesn’t mean there’s no threat to small businesses. Unfortunately, nothing could be further from the truth. According to research, on average the employee of a small business will experience 350% more phishing and social engineering attacks than a staff member at a larger enterprise.
Why? Well, while cybercriminals are undoubtedly motivated by the prestige and financial rewards that come with the scalp of a global enterprise, small businesses represent an easy target. SMEs typically have weaker defences and less developed cybersecurity practices than their corporate counterparts, for one. However, that’s not the only reason. SMEs' employees can often be turned more easily to a cybercriminal’s malicious ends, whether through actively colluding with criminals or negligence. Indeed, CyberSmart’s research revealed that 22% of SME leaders believe employees are more likely to make mistakes – such as clicking on a phishing link – since the cost of living crisis began. Meanwhile, 20% believe employees will steal sensitive or proprietary data from the company to sell for profit or a competitive advantage.
How to protect your business
There’s no denying that small businesses are vulnerable to spear phishing attacks. Nevertheless, becoming a victim of this kind of breach isn’t inevitable. There are plenty of things you can do to ensure your business is protected. 1. Use a VPN
A virtual private network (VPN) is essential for remote working. If your business employs anyone who accesses company systems through a network that isn’t your own, even if only occasionally, you need one. Unsecured networks pose a huge threat to your business which a VPN can easily counter.
Rather than using the public network, a VPN routes your traffic through specialised servers and encrypts your data. This makes it virtually impossible for cybercriminals to break in through a public network (unless they have the password or encryption key as we saw in the Colonial Pipeline case).
2. Staff training
As mentioned earlier, Spear Phishing relies on social engineering techniques, using our human nature against us. This is tricky to counter, but not impossible. Cybersecurity awareness training can help your people recognise when they’re being targeted and give them the skills they need to avoid it.
3. Patch all software
Patching is very important to cybersecurity and the good news is that it’s simple. All you need to do is update all software with the patches providers release. This will stop cybercriminals from exploiting any vulnerabilities in providers’ software to access your business.
4. Deploy MFA
Like VPNs multi-factor authentication (MFA) adds an extra layer of security for your business, making it much harder for hackers to gain access. You likely already use MFA in some aspect of your online life, it’s now a requirement for most banking accounts. But if you haven’t already, switch it on for any system or application your business uses.
5. Protect your network
Your network is the gateway to your business. It’s what spear phishers are ultimately trying to gain access to when they attack you. Through it, a hacker can access just about anything your organisation does. So protect it, and protect it well. The four most simple things you can do to strengthen your network immediately are:
Install a network firewall to filter network traffic
Use a VPN to encrypt network traffic
Segment your network to eliminate single points of failure
Regularly update your router’s firmware
6. Always use back-ups
If the worst does happen and a spear phishing attack succeeds in stealing information, data backups can mitigate the worst effects. Not only will it enable you to minimise disruption by getting systems back up and running quickly, but it’ll also weaken cybercriminals’ bargaining power if there’s a ransom to be paid.
7. Limit user access
Be careful to limit who has access to what within your business. Users should only have admin rights within a system or application if it's critical for their role. The reason for this is simple; if a cybercriminal compromises a user account through a spear phishing campaign, the fewer permissions that account has the less damage a hacker can do.
8. Tie it all together
If the list above appears extensive, don’t fear, there are methods which allow you to tie it all together. The first is to complete a cybersecurity accreditation like Cyber Essentials or ISO27001 certification. These certifications can help you put in place good cybersecurity practices (including all of the above) and build your cyber confidence. However, you also need something that keeps your cybersecurity baseline consistently high, year-round. This is where everyday cyber protection tools like CyberSmart Active Protect can help. Finally, none of this has to cost the earth. For more on how to protect your business on a budget, check out our guide.