


NIS2
NIS2 Maturity Pathway
Assess. Fix. Stay compliant. The NIS2 Maturity Pathway takes you from gap analysis to ongoing compliance in three steps, delivered by your CyberSmart partner.
Governance, technical controls and training, covered together, with evidence always ready for regulators. NIS2 isn't a deadline you meet once. It's a standard you keep.
Know exactly where you stand on NIS2
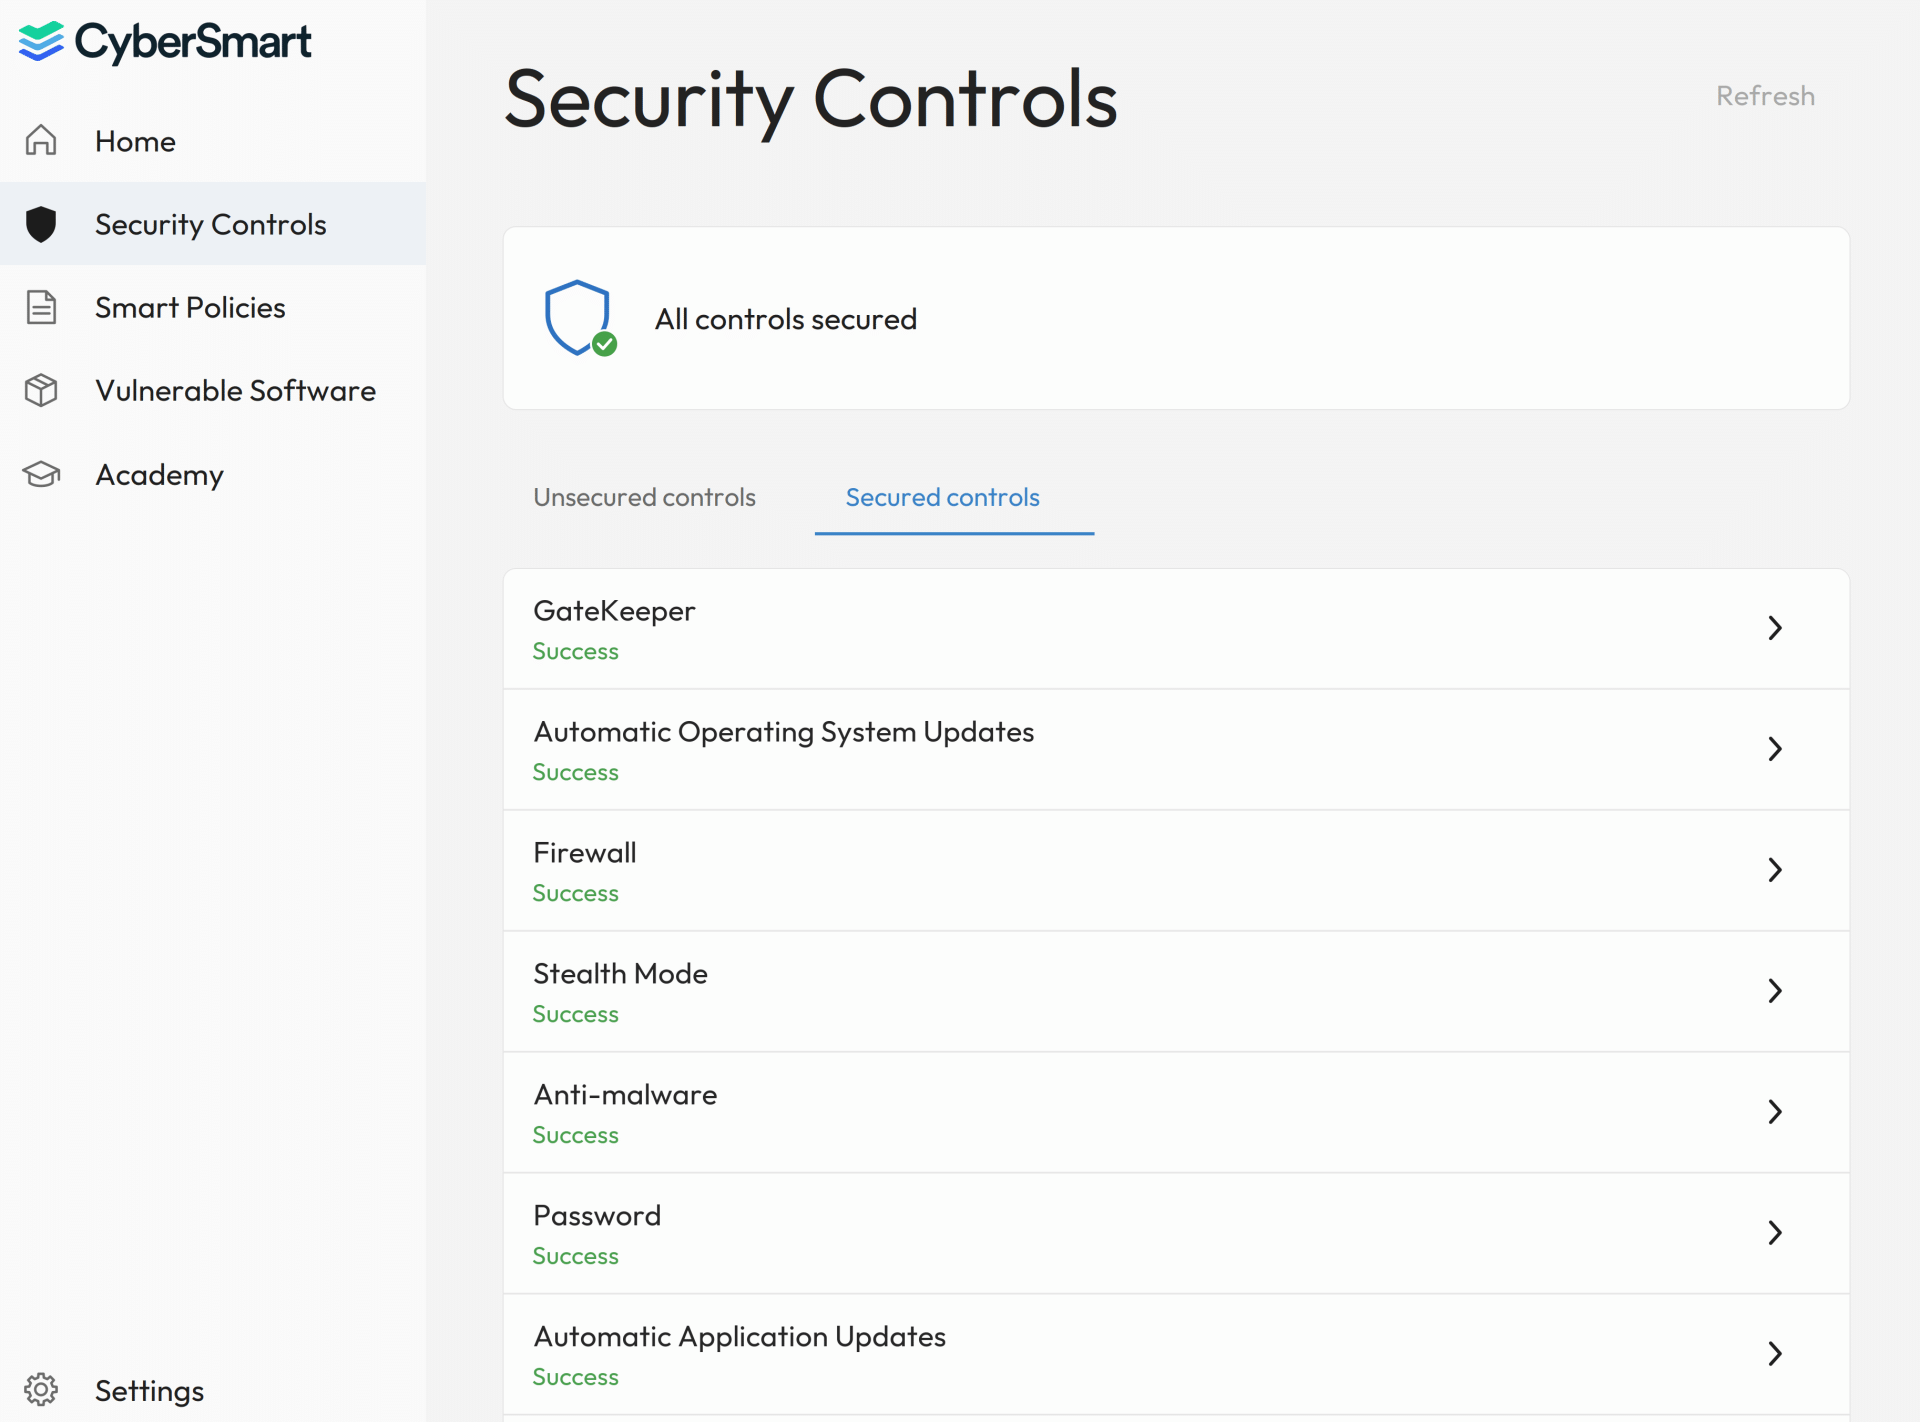
Answer clear, guided questions and get a complete picture of your compliance, with every gap flagged so you can fix what matters first.
Active Protect scans your devices at the same time, so your answers are backed by real data, not guesswork. Gaps become a prioritised plan across governance, technical controls and training. Clarity first. Then action.
Why Compliance Matters
What is NIS2?
The NIS2 Directive is the EU's updated cybersecurity law for essential and important entities, including organisations in their critical supply chains.
Time is short. Many EU countries have already written NIS2 into national law, and others are following.
The Impact
NIS2 introduces enforceable rules for risk management, incident response and supply chain security, affecting an estimated 160,000 organisations. Fines for essential entities can reach €10 million or 2% of global annual turnover, whichever is higher.
The Opportunity
NIS2 isn't just about avoiding penalties. It's a strategic opportunity to:
Introducing the NIS2 Maturity Pathway
Delivered by CyberSmart partners, this three-step model offers a complete, fast and accessible route to NIS2 readiness and compliance, with continuous monitoring and improvement built in.
Step 1: Discovery
Assess readiness
- Run Active Protect to scan devices and assess which requirements apply
- Identify cyber hygiene gaps and risks
- Review policies and controls for alignment
- Produce a health check report showing your current NIS2 posture
Step 2: Maturity Level - Baseline
Validate and remediate
- Carry out a formal NIS2 assessment on the CyberSmart platform, delivered by your partner
- Run automated scans across all endpoints with Active Protect
- Get a compliance report with prioritised, actionable recommendations
Step 3: Maturity Level - Established
Monitor and maintain
- Stay protected and prepared with regular governance reviews, board-level reports, and support for audits and regulatory checks
- Strengthen your defences with managed patching, and endpoint protection
- Build a security-aware culture with ongoing training, phishing simulations and incident response planning
Why choose a CyberSmart partner for NIS2 compliance?
Rapid NIS2 health check
See your NIS2 readiness in minutes, not months. The Cyber Confidence Score turns complex requirements into one clear snapshot your whole team can understand and act on. Clear score. Clear next steps.
Comprehensive and structured
Every key NIS2 requirement, covered: risk analysis, business continuity, secure communications and supply chain security. One three-step journey takes you from first scan to lasting maturity. Nothing missed. Nothing duplicated.
Smart remediation tools
Gaps are found automatically and ranked by risk, with step-by-step guidance to close each one. Your team knows exactly what to fix, and in what order. Less guesswork. Faster progress.
End-to-end assurance journey
Pre-assessment, assessment and post-assessment, all on one platform, with a full audit trail at every stage. When regulators or partners ask for evidence, it's ready. A trusted path towards NIS2 compliance.
Built for accessibility and scale
Intuitive enough for an SME. Powerful enough for a growing enterprise. Quick to deploy, simple to use, and flexible across every industry in scope. Built for where you are. Ready for where you're going.
Continuous protection and monitoring
Assessments show where you stood. Monitoring shows where you stand today. Continuous checks, actionable alerts and regular compliance reports keep you assured all year. Compliance isn't a moment. It's maintained.