4 Ways to Get Your Information Security Policies Under Control

Information security policies

An information security policy is a set of rules and guidelines that an organisation issues for securing its confidential data. Employees of the organisation should understand and follow the information security policy.

In this article, we list effective ways that you can use to develop a information security policy, or beef up your organisation's existing information security policy.

1.     Address the problem of password management

Many organisations, despite knowing about the existence of their security issues, are often confused on how to address them. It might sound obvious, but this is where most of a company’s security failings can be resolved.

For instance security policies must pay much attention to password management. Employees choose their own passwords and are then responsible to manage and control them. However they should be provided with the tools to create, store and access the range of passwords they may need to use.

According to a report by Verizon published in 2017 on data breach investigations, is where things take a turn for the worst. It says that more than 4 out of 5 data breaches are happening due to compromised or weak passwords. In addition, a survey has reported that almost 80% of employees find password management a hassle. An issue that can be easily solved with a password manager.

The scale of the problem here demands that organisations address the clear problem of password management in their information security policy.

2.     Use a holistic approach

As a modern business you should understand the barrier between work life and personal life is becoming more and more indistinct. This idea extends to information security as well. Technology departments must tailor security guidelines around the modern employees work behavior.

Concepts such as BYOD (Bring Your Own Device) are gaining traction nowadays. Organisations need to take a more holistic approach to their information security policies, which involves looking beyond employee work logs and company related passwords.

A single employee, whether in-office or remote, can put the entire organisation’s information security at risk. This makes every employee a possible point of failure for the entire network. The information security policy should take this into consideration and adequately address the risks associated with BYOD. Doing so will allow them to protect the company’s information against attackers.

3.     Educate the employees

Educating employees about information security is an important process when it comes to protecting your organisation’s data.

Regular training sessions that stress the basic concepts of security such as the risks of public networks and password management should be conducted. These sessions can be delivered by internal security experts or third-party security services, depending on the resources available to your organisation.

The most common types of data breaches are caused by the lack of education of employees. Therefore, you should incorporate training and awareness in the organisation’s information security policy. For instance, a security training program can be introduced that requires employees to attend monthly security sessions held within your organisation.

4.     Automate and simplify

Simplify what you can, and automate what you cannot. This simple rule can help you improve your organisation’s information security policy significantly.

A simple information security policy will go a lot further than a binder filled with complex security procedures. This is because employees are more likely to circumvent a complex security measure than a simple one.

You should first attempt to simplify anything that you can within the security policy. For instance, make it clear what the minimum length for passwords should be, rather than just suggesting the use of strong passwords.

For things that cannot be simplified, such as the process of validating online websites, you can make use of tools such as firewalls to prevent employees from violating the policy.

Conclusion

For businesses, information security in today’s world is more of a necessity than a luxury. It is important for an organisation to make a holistic yet simple changes in their approach to information security policies, to address concerns related to cybersecurity.

CyberSmart understands that managing your information security policy can be an excruciating task. If you would like to learn more about how to improve your information security policy, get in touch with us right away. We would love to help you polish your security policy for mitigating risks of cyber attacks.
Understanding GDPR Data Controller in 5 easy steps

GDPR Data Controller

Understanding GDPR Data Controller in 5 easy steps

By now most of have heard of the General Data Protection Regulation (GDPR). But in case you've been carefully avoiding the news since 2017, it's a law put in place by the EU which strengthens the protection of citizens' data.

GDPR has brought with it some very stringent penalties for non-compliance. And if your business isn't yet compliant, you could be at risk of an astronomical fine, as well as lasting brand damage.

However, putting GDPR into practice raises some really big questions. Who is liable in the event of a breach? What is a GDPR data controller?  And who is the GDPR data processor? Let's take each in turn.

1) What is GDPR?

Before we understand the role of a GDPR Data controller, we need to tackle what GDPR is. In simple terms,  GDPR forbids the misuse of EU citizens data. And it applies whether your company is based in the EU or not.

2) Who is the GDPR Data Controller?

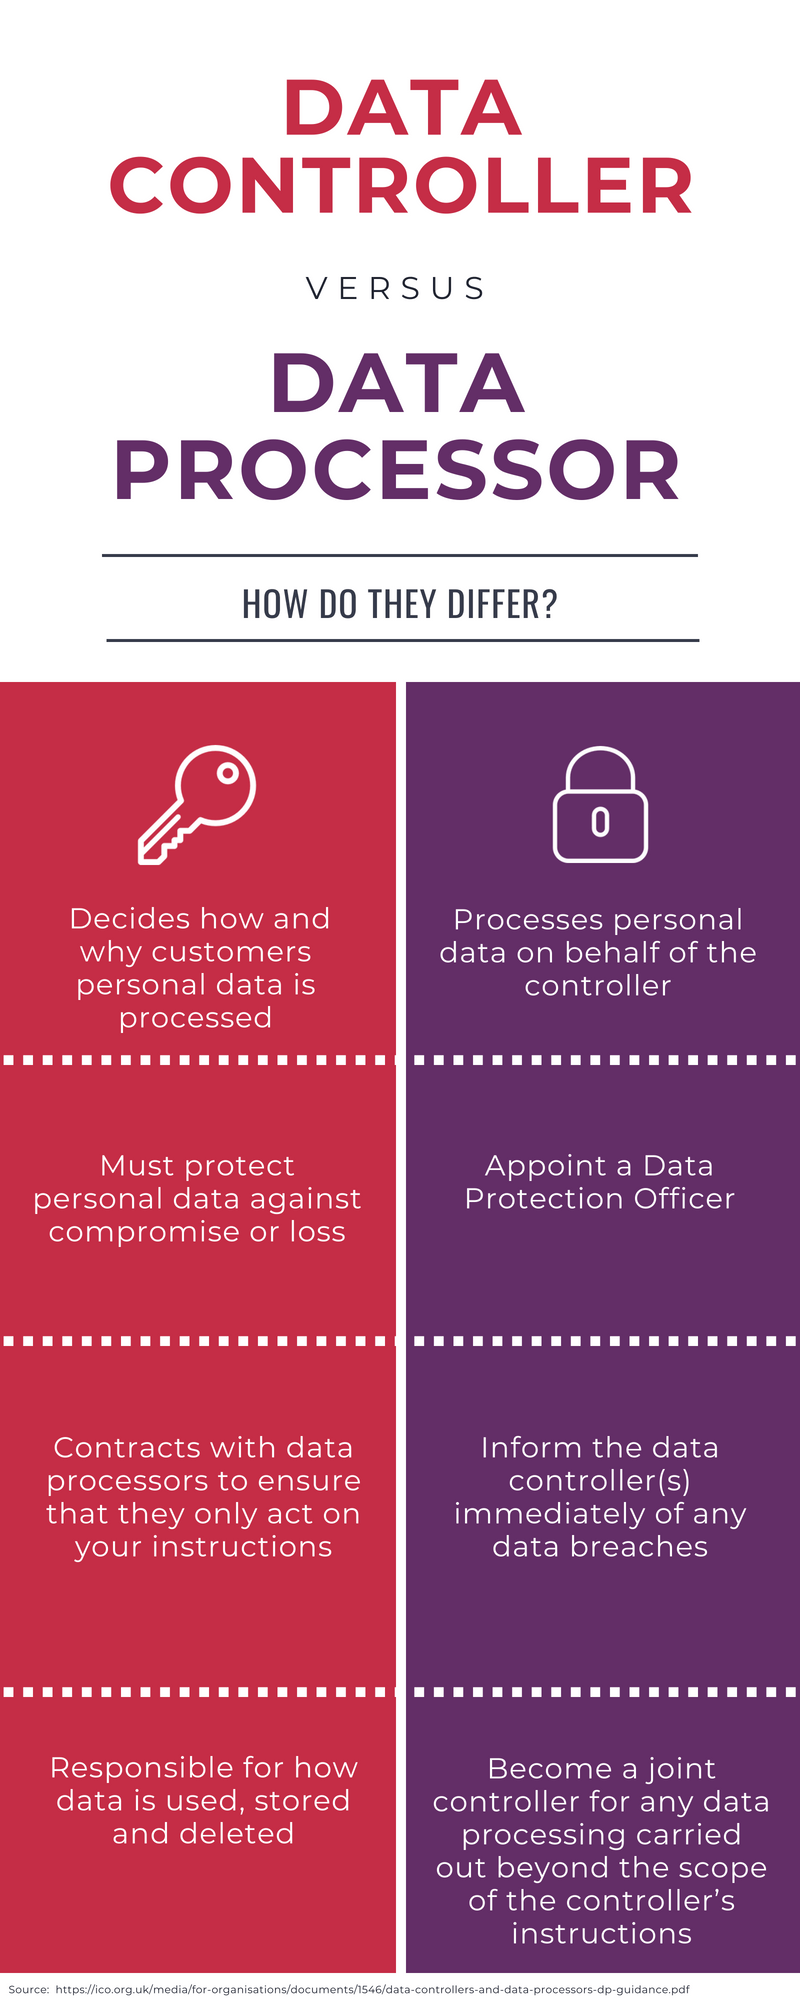
The 'GDPR data controller' is the organisation that decides how and why customers personal data is processed. In other words, it's usually your business itself. You control the data but, crucially, you don't necessarily have to hold or process it. However, even if you don't process it yourself, you're still responsible for how it's used, stored and deleted.

3) What are the GDPR Data Controller's responsibilities?

Under GDPR Data Controllers are obliged to:

  • Protect personal data against compromise or loss by implementing strict technical and organisational measures to secure data
  • Have a legal agreement with your processors to ensure they only act on your instructions and comply with GDPR

4) Who is the GDPR Data Processor?

A data processor, on the other hand, is the company or person who processes personal data on behalf of the controller. To give a few examples, it could be your data storage provider, payroll company, accountant or marketing agency.

5) What are the GDPR Data Processor's responsibilities?

Under GDPR, data processors have a lot more responsibilities, including:

  • Appointing a Data Protection Officer if their business processes sensitive or 'big' data
  • Responsibility for implementing significant security measures
  • Maintaining a record of all data processing operations under their responsibility
  • Inform the data controller(s) immediately of any leaked data
  • Become a joint controller for any data processing they carry out beyond the scope of the controller’s instructions
GDPR Data controller vs Processor
GDPR data controller vs processor

In Summary

GDPR has changed the way we process and control data.  And understanding your role as a data controller, processor or both is crucial – both to avoid legal hot water and protect your customers.

Data protection obligations got you in a muddle? Get on top of them quickly and easily with the CyberSmart Privacy Toolbox.

CyberSmart Privacy Toolbox

9 Secrets To Make Your Medtech Startup Compliant

Running a startup is hard especially in a heavily regulated sector like MedTech and because of the nature of the industry and the types of data Medtech startups typically handle it’s even more important to do compliance the right way.

While you may be compliant with CQC and HIPAA what you may not be aware of is the risk to your companies data and below are a few things you can do today to help you resolve those issues.

medtech compliance

1) Use a password manager, and make your team too

Remembering passwords has always been a hassle and traditionally the only solutions were;

  1. Using the same password everywhere
  2. Forgetting your password
  3. Writing your password down in an insecure location

All of the above solutions are incredibly insecure and present a risk to your organization especially if the passwords are the key to sensitive data that you’re liable for.

A far more secure way of storing and sharing passwords is by using a password manager. We recommend 1Password as it’s simple to use, secure and has excellent team sharing capabilities.

2) Have GDPR compliant privacy policies

You’ll need to update your terms in order to inform your customers and anyone else who you store data on about how you are collecting, processing and sharing their data.

Click here to grab a privacy policy builder for free.

3) Update, update, update

As annoying as it may seem, device manufacturers often release security patches to keep you protected, it’s critical you apply these when they become available otherwise it can lead to irreversible damage.

The CryptoLocker ransomware that hit the NHS in 2017 would have been stopped dead in its tracks if they had patched their machines within the last 2 months.  

uk medtech

Curious to know what the rest of the tips are?

To read the other 6 secrets… you can unlock them below

[emaillocker id="4581"]


4) Use 2FA for all privileged accounts


Two Factor Authentication is an excellent additional measure to ensure your company protects its data.

Even with a compromised username and password an attacker is unable to access the account because you have to authorise access to your account using a code only accessible through your phone.


5) Enable Your Firewall


The last thing you want is a hacker getting access to sensitive data which is a risk by not having a firewall enabled on your network.

In simple terms, a firewall is designed to prevent unauthorised people accessing your private networks connected to the internet. All messages leaving or entering pass through the firewall, which examines each message and blocks those that do not meet the security criteria.

Your Medtech startup needs a firewall to protect your confidential information from those who are not authorised to access it and to protect against malicious users and accidents that originate outside your network.


6) Password enabled

Believe it or not, over 90% of cyber attacks and security breaches arise from human error. With that said not having a secure password enabled on all of your employee devices is not only inadvisable but ultimately reckless.

Imagine this scenario; an employee has a personal data on their laptop and the device does not have a password enabled and the employee loses the laptop. That’s a very scary scenario but easily rectifiable by ensuring that every company or personal device that is used for work has a password enabled.


7) Disk encryption enabled

Enabling disk encryption (filevault in Mac and Bitlocker in Windows) prevents someone with physical access to a machine from extracting all the data. In order to do this on an unencrypted disk, an attacked simply removes the drive from the machine and connects it to a disk reader to access all the contents in plain text.  They can download all documents, pictures, sensitive information as well as see whatever is stored in the browser. Scary stuff. Prevent it by simply enabling disk encryption.


8) Automatic Operating System Update


Another way to prevent malicious attacks is to enable automatic software updates for your operating system. Even if you have a Mac you need to ensure that you’re using the newest operating system as it is a myth that Mac’s cannot be susceptible to threats and malware.

Hackers and malicious cybercriminals use weaknesses in the software and apps to attack your devices and steal identities and sensitive data which is why it is extremely important to ensure that your organisation is using the latest Windows, Mac or Linux software.

But what if they disrupt my work and it takes time out of my schedule? Fortunately, on most operating systems they allow you to schedule when you would like the update to occur so it shouldn’t cause much disruption and in the event that it does at least your data will be safe!


9) Certification


One of the ways to ensure that you’re handling data the correct way is to get a Cyber Essentials certification. Why would you want it? Cyber Essentials is a government-backed certificate to help organisations protect themselves against online threats and is a great way to show suppliers and customers that you take security seriously and you’ve taken steps to secure their data.

Although it’s a great start, Cyber Essentials is really the most basic level of compliance your MedTech startup should be aiming to achieve and if you desire a higher level of compliance then you should be aiming to get the Information Assurance for Small and Medium Enterprises (IASME) certification. This is based on the ISO 27001 (the industry standard for the management of information security) but tailored for small businesses.


Summary


When you do all of the steps above your MedTech startup becomes a few steps closer to becoming compliant however  If you are serious about ensuring that your business data is being protected and you want to improve your business reputation schedule a demo to learn more about Cyber Essentials.

[/emaillocker]

In this podcast, our co-founders Jamie Akhtar and Mariella Thanner had a chat with James Gill from GoSquared about the topic of the month: GDPR!
And CyberSmart's story 🙂

(more…)

In this podcast, our co-founders Jamie Akhtar and Mariella Thanner had a chat with James Gill from GoSquared about the topic of the month: GDPR!
And CyberSmart's story 🙂

(more…)

Speaking at the lecture for the Institute of Chartered Accountants in England and Wales in London earlier this year, Elizabeth Denham of the ICO, discussed the role of accountability in GDPR and how people must adjust their mindsets in regard to how we think about data protection as well as what GDPR may actually look like in reality.

(more…)

Speaking at the lecture for the Institute of Chartered Accountants in England and Wales in London earlier this year, Elizabeth Denham of the ICO, discussed the role of accountability in GDPR and how people must adjust their mindsets in regard to how we think about data protection as well as what GDPR may actually look like in reality.

(more…)

Step 1 to CE: Boundary Firewalls and internet gateways

A firewall or gateway protects internal networks and systems against unauthorised access from the internet. They are designed to provide a basic level of protection for internet users. All business networks should have a properly configured firewall in place. The firewall monitors all network traffic, whilst identifying and blocking any traffic which can be harmful.

(more…)

Step 1 to CE: Boundary Firewalls and internet gateways

A firewall or gateway protects internal networks and systems against unauthorised access from the internet. They are designed to provide a basic level of protection for internet users. All business networks should have a properly configured firewall in place. The firewall monitors all network traffic, whilst identifying and blocking any traffic which can be harmful.

(more…)

Cybersecurity standards explained

Cybersecurity standards

The cybersecurity sector is a crowded place when it comes to different standards, certifications, rules and regulations. It can also cause a lot of head-scratching and confusion for those not familiar with the best practice.

Founders and business owners often come to us and say they want to or have to get ISO 27001 certified. Hardly anyone knows when and how ISO 27001 makes sense for a small business and what other certifications can be achieved instead of ISO 27001 or used as a stepping stone towards achieving ISO 2700. Here is a brief overview of the most common cybersecurity standards in the UK: 

Cyber Essentials

In short, Cyber Essentials is a scheme designed by the UK government that aims to get all UK businesses to be able to manage their IT security to a certain level. It helps companies to implement basic levels of protection against cyberattacks, demonstrating to their customers and suppliers that they take cybersecurity seriously.

Established in 2014, the purpose of this standard is to develop necessary cybersecurity standard throughout an organisation. The standard is relatively technical and protects organisations from 80% of cyber-attacks. The most surprising factor we discovered as cybersecurity consultants was that most companies that had other standards, such as ISO 27001 or PCI-DSS implemented, would still fail under Cyber Essentials. The best use case for this standard is to implement it as a first defence and perimeter security before other standards are considered.

Cyber Essentials certification is a great first step towards GDPR. It serves as evidence that you have carried out basic steps towards protecting your business from internet-based cyber attacks.

Cyber Essentials Plus

Cyber Essentials Plus is the audited standard of Cyber Essentials. Besides including some additional controls, the implementation needs to be assessed by a Cyber Essentials Plus auditor. This obligatory audit creates additional trust in the standard and it is safe to assume that once Cyber Essentials is well-established, Cyber Essentials Plus will increasingly become mandatory.

IASME

This standard goes far beyond Cyber Essentials and can be described as a "mini version of ISO 27001:2017". Together with the government, IASME developed this standard in order to create an easily adaptable and affordable alternative to ISO 27001. The IASME standard is specially tailored towards SME’s and includes processes, people and technology. In May 2018 both IASME standards will be expanded to include GDPR readiness. Both IASME standards require Cyber Essentials as part of the readiness as well. Similarly to cyber essentials, the IASME standard can serve as proof to customers and suppliers that their information is being protected. It is provided alongside the cyber essentials certification. There are two types: the standard self-assessment and the Gold standard, which requires an audit onsite.

ISO27001

ISO 27001 is an international information security standard. Including far over 100 controls the standard is frequently implemented by corporations or businesses dealing with critical infrastructure or the public sector. ISO27001 covers areas that include security policies, access control, operations security, human resources, cryptography and compliance. It does not cover GDPR*. However, an organisation can voluntarily include GDPR in their ISMS (Information Security Management System). 

*A note on GDPR: GDPR is NOT a standard, it's a law, so we've excluded it here. 

If you have any questions about Information Security Standards or Cyber Security in general or just want to have a chat, drop us a line at hello@cybersmart.co.uk.

Looking to improve your cybersecurity but not sure where to begin? Start by getting certified in Cyber Essentials, the UK government scheme that covers all the fundamentals of cyber hygiene.

CTA button

Here's what everyone should be doing in 2018 in terms of cybersecurity and data protection:

(more…)

Here's what everyone should be doing in 2018 in terms of cybersecurity and data protection:

(more…)

Time for the UK education sector to prioritise cybersecurity

Cyber Security Education

As you probably know already, schools and universities are not immune to attacks from disgruntled employees or other insiders. However, there is another key issue for school leadership teams that is unique to the education sector: students!

Students are often more digitally aware than most teachers and other school employees. This can lead to new digital platforms being introduced into the school environment without staff being made aware.  This insider threat to schools from students is not malicious; instead, it’s an issue of negligence in some cases or lack of awareness in other.

While students and teenagers may be tech savvy, they’re not often very security conscious. The consequences of exposing the school network to a data breach or cyber attack is often not properly understood. They are also not legally culpable for any actions that might result in a breach, so there is less of an incentive to take responsibility.

Adults are also potential insider threats; a teacher may bring a corrupted USB stick into school with their learning resources, or school admin staff may open and respond to a phishing email without understanding what it is. This is why schools must keep on top of their security policies and enforce them across the whole school community.

Awareness Of The Threat Landscape

The general lack of awareness about the types of attack a school network may be subjected to, what they look like, and where they come from is a major problem for the school as a whole.

All parties - IT departments, network managers, teachers, school employees and students - must be made aware of the threat landscape with relevance to their internet and network usage. Regular training should be part of the schools’ IT policy, raising awareness of the consequences of cyber attack to the school and individuals personally – which could include disciplinary actions.

Network Protection

School networks need robust defences in place to protect from threats such as malware or DDoS attacks. Antivirus, web filtering, firewall, device encryption, mobile data management and penetration testing should all be updated regularly and reviewed to keep pace with new threats and technologies.

Managing User Privileges

An effective way of limiting the potential damage an insider threat poses is to rigorously manage who has access to the network, and what they can and can’t do.

Both staff and students should only have limited access to the school’s network based on their requirements, reducing the opportunity for malicious or accidental misuse of the network. Managing user accounts should also include regularly reviewing what access individuals require, blocking access to some systems if individuals no longer need them, and deleting users when they leave the school.

If you have any questions about Cyber Security in general or just want to have a chat, drop us a line at hello@cybersmart.co.uk

Protecting your data and organisation is hard work — let us help you make it easier.

The legal sector remains a hot target for the full spectrum of threat actors. These include cybercriminals, hacktivists, state-sponsored groups. This is largely due to the wealth of sensitive data held within the industry. For example, patent data, merger and acquisition information, protected witness information and negotiation information. The scope is vast and not limited to the above list. Legal firms are equivalent to a pot of gold for any of these groups. So, what's the state of cybersecurity in the legal sector and what can be done to improve it?

(more…)

The legal sector remains a hot target for the full spectrum of threat actors. These include cybercriminals, hacktivists, state-sponsored groups. This is largely due to the wealth of sensitive data held within the industry. For example, patent data, merger and acquisition information, protected witness information and negotiation information. The scope is vast and not limited to the above list. Legal firms are equivalent to a pot of gold for any of these groups. So, what's the state of cybersecurity in the legal sector and what can be done to improve it?

(more…)