Encryption explained: how does it work and why do SMEs need it?

Most of us have heard of encryption. It’s that recipe for secrecy that techy types talk about all the time. But for many of us, that’s where the knowledge ends.

However, for small businesses looking to improve cybersecurity, encryption can be a vital weapon in your arsenal- and one that isn’t so hard to understand. Here’s a simple explanation of what encryption is, why you need it, and when to use it.

What is encryption?

Although encryption, much like ‘the blockchain’, can seem like another one of those unfathomable technical terms, it’s actually pretty simple.

Encryption is most commonly used to protect data in transit and at rest. Ever sent a Facebook Messenger or WhatsApp message? That uses encryption. Or, a payment using online banking? Also encryption. How about buying something from a web store? You guessed it, encryption again.

You get the picture. Encryption is used everywhere in our daily lives, but how does it work?

In non-technical terms, encryption is a way of randomising data so that only an authorised recipient can understand the information. Encryption converts plaintext – for example, the text in an email between you and a colleague – and converts it into ciphertext, a string of random numbers and letters. To unlock the real message or data, you need an encryption key, which is a set of mathematical values that only the sender and the recipient of the message know, like so:

encryption

Photo PixelPrivacy

The principle is much the same as a password, but better (as we’ll see).

Why does your business need it?

So we’ve covered, in very simple terms, what encryption is. The next question is why should SMEs be using it? It’s easy to assume that if you’re not a huge multinational, processing reams of sensitive information, that your standard security tools such as firewalls and secure passwords are enough to protect your data. However, there are three key reasons why this isn’t the case.

Cyber attacks are on the rise

It’s likely not news to you that cybersecurity threats to SMEs are on the rise. Barely a week goes by without another news story or set of figures released to that effect. Indeed, the Federation of Small Businesses estimates that SMEs are collectively subject to almost 10,000 cyber-attacks a day.

A recent report from cybersecurity experts, Malwarebytes, reveals that detections of new malware continue to increase by 1% year-on-year.

A big part of the problem is the ever-increasing volume and variety of malware out there. A recent report from cybersecurity experts, Malwarebytes, reveals that detections of new malware continue to increase by 1% year-on-year. This might not sound like much, but when we’re talking about detections in the tens of millions, it soon adds up.

In this environment, it’s getting harder and harder to stay ahead of the threat. However, adopting encryption can act as a strong second line of defence. For instance, someone in your organisation accidentally clicks on a malware link in an email (something we’ve all done at least once), potentially exposing your data to an attacker. Using encryption means that they won’t be able to read whatever they find without a key, meaning your data is safe.

You’re using a cloud service

Cloud computing is now a vital part of the daily operations of most SMEs. And if you’re doing business entirely in the cloud, and don’t store any sensitive data on employees’ devices, you’re safe, right? After all, the likes of Amazon, Google, and Microsoft spend billions of dollars a year on the security of their cloud services.

Unfortunately, this is only partly true. Obviously storing your data in a cloud is far better than having everything on vulnerable systems, but that doesn’t mean it’s entirely safe.

To give an example, let’s say you use a cloud-based platform like Office 365 for your everyday operations. A would-be hacker can still intercept your data as it moves between your device and the cloud. As we’ve already mentioned, this is unlikely if you’re working with a reputable cloud provider, but it’s not impossible or even that uncommon. Using strong encryption can help protect you against this by adding another layer of defence.

Passwords aren’t the be-all and end-all

Now, you may be thinking ‘but my business has a clear password protection policy and we regularly change our passwords for laptops and devices, surely that’s enough?’
Not quite. While it’s true that a strong security policy can help protect your business against regular theft and even less sophisticated cyberattacks, it’s not enough to protect you from the really harmful stuff.

Hackers are always finding a way around even the strictest security policies and new methods for cracking passwords appear all the time. To be totally sure, you need an a solution that allows you to completely encode everything on your device. This means that even in the event someone does manage to break in, all they’ll be able to extract is random gobbledegook that’s little use to anyone without the right encryption key.

How do you use encryption?

Finally, let’s take a look at how you can use encryption to protect your business. Encryption can take many forms. How you use it will depend on what you need it for, but some common uses include:

End-to-end encryption – This guarantees data sent between two parties cannot be viewed by anyone else. Most of the internal communication tools such as Slack or Google Hangouts will come with this as standard, but it’s worth checking whichever messaging tool you use.

Cloud storage encryption – A service offered by cloud storage providers that transforms your data or text using an algorithm and stores it safely in the cloud.

Encryption as a Service (EaaS) – EaaS represents the next step up from cloud storage encryption. It’s the perfect tool for small businesses who want to use encryption but lack the resources to do manage it themselves. EaaS subscription models typically include full-disk, database, and file encryption.

Of course, these are far from the only uses of encryption. You can also use it to protect certain fields on your website, encrypt everything leaving or entering your web server and a hundred other things besides. The above are just the most common applications for SMEs.

Data is more important than ever to SMEs. In fact, in our data-driven economy, it’s often the most valuable asset a business possesses. Basic cyber-hygiene such as encryption can go a long way towards helping you protect it.

Show your customers you value their data by getting certified in Cyber Essentials, the UK government scheme that covers all the fundamentals of cyber hygiene.

Get started

A new chapter: CyberSmart raises £5.5million to fund growth

Demand from SMBs for certification drives growth to 300% per annum

We are delighted to announce that CyberSmart has raised £5.5 million which will be used to fund the growth of the company. This will enable us to continue to support small and medium-sized enterprises (SMEs) to protect themselves against cyber threats in an ever-evolving technological landscape.  The Series A funding round was led by venture capital firm IQ Capital and a group of tech-savvy individual investors.

The lockdown and shift to online working patterns means small businesses are prioritising security more than ever. CyberSmart has seen a massive increase in demand from SMEs to protect their businesses with a revenue increase of 300% over the last twelve months.

Here's what our CEO, investors, and partners have to say about this exciting news:

Jamie Akhtar, CEO CyberSmart says, “We are delighted to have closed our series “A” funding round with £5.5 million to fund our next stage of growth. Our investors have seen that we have built a great technology and also a great team. The SME market has not been easy to protect until now, and business owners have so many issues to deal with they often wait until it is too late, losing all their customer data or even cash in a cyber-attack. We take all the effort out from a business becoming secure, so it’s not as painful, time-consuming, or as expensive as one might think. People can have effective, comprehensive security and risk-reduction from a team that is there to support them through the challenges of transforming into a digital business.” 

Kerry Baldwin, Partner IQ Capital says, “What we like about CyberSmart was the automated solution to secure companies and make them compliant with certifications like Cyber Essentials, and that it reaches the underserved SME market that we felt just wasn’t being protected. When we see signs that a company has found product market fit, is way ahead in hitting its targets and is finding innovative partnerships with managed security service providers to deliver massive market penetration then we know it is a great time to invest and secure our position.  In the current situation there has never been a greater need for making sure that remote teams and small teams working from home are protected in an automated, effective affordable way.   Obviously the UK has got Cyber Essentials, but other countries have other similar certification requirements, so they solve a problem that is faced in many countries so this company will be going global as soon as possible.

Przemek Pardel, Startup Acceleration Programs Lead Europe, Google says, “CyberSmart is working hard to provide clear and simple cyber security solutions to small and medium enterprises across the globe. They have shown great determination to better their technical capabilities and further scale their product, which has been evident from their participation at our accelerator program for cyber security startups and their recent Series A funding success. We are excited to see how they will evolve and grow after they graduate from the accelerator.”

Joanna, Program Lead at CyLon says, “Great product, dedicated team and seamless execution. These three aspects of CyberSmart put together create an exceptional combination with plenty of room to grow in the future. We at CyLon as proud early adopters of CyberSmart can’t imagine our organisation without it.”

Akhtar continued, “I set up CyberSmart was after witnessing first-hand how SMEs suffer data breaches and realising that hundreds of thousands of businesses were suffering cyberattacks.  When we started, 74% of SMEs had a breach that year, if 74% of buildings caught fire, there would be fire stations on every corner.  The technology is now there that enables us to automate protecting SMEs and by implementing a cloud-based platform that is both simple and cost effective to deploy, backed by a Cyber Essentials Certification. Businesses have gone through two stages, the first phase was rapid, digital transformation which was all about connectivity, communication, basically getting your team and your company back online remotely, or online remotely.

Phase two is now. We have spent all these years building our secure, corporate infrastructure or drilling into people these secure working practices, but that has all gone out the window because everyone is now working remotely. The new focus is on how to secure teams working out of the office. So that’s the big wave which we are seeing now that has been driving demand from all types of companies. Because our technology is automated, certified, comprehensive and can be deployed, managed and monitored remotely, it's an ideal solution.

CyberSmart are working with many different types of channel partners. This represents a good opportunity to reach the SMBs. For partners there are many benefits- an income stream that also prevents churn, it makes customers more sticky. Most importantly, it makes customers more secure which helps with cyber hygiene across the whole UK business supply chain.”

The Cyber Essentials certification is recommended by the ICO and Federation for Small Businesses, and it’s required of suppliers to central and local government. Implementing its security controls can mitigate up to 99% of cyber attacks.

Akhtar continued, “Technology and automation are the way forward. By deploying a smart application that runs on all the devices no matter where people are or which device they are using, we can ensure security 24/7. This is what we mean by automated compliance. We offer a simple path to certification, but we also make sure you are compliant with that certification every day. The application essentially does all the technical bits, so people don't have to be cyber security experts themselves. 

Chris Ensor from NCSC said: “The NCSC is proud of the success achieved by CyberSmart, which was one of the first participants in our NCSC Cyber Accelerator programme. It has won a deserved reputation for producing innovative software and for encouraging businesses to seek Cyber Essentials certification.  

“The Accelerator programme is currently seeking new start-ups and we would encourage anyone with fresh ideas to apply and help us continue to drive innovation in UK cyber security.”

About CyberSmart

Born out of the GCHQ / NCSC Cyber Accelerator in 2017, CyberSmart was created by a group of forward-thinking security experts, who noticed that many companies needed to secure themselves and achieve information security standards, but ultimately found the process too complicated or were limited by financial or human resources.

We believe that every organisation should be able to easily comply with recognised standards and protect their data and infrastructure. Through making security accessible, we have achieved tremendous growth and enabled thousands of users to protect themselves against cyber attack.

The journey of a customer query at CyberSmart

Inside the CyberSmart customer support experience with Francis Kontor, our Technical Support Lead.

One of the things we are most proud of at CyberSmart is the feedback we get from our customers about the personal support we offer them. We work hard at it because we know how important it is for our clients. We are working with small businesses, some with only a few employees and no real IT staff or expertise.

Francis Kontor, Technical Support Lead

The world of cybersecurity can look daunting from the outside and our job is to make the process of protection as easy and understandable as possible. We do this in a few ways.

We get all kinds of requests from our customers and over time we've had to expand the skillsets we use to respond to them. That has meant creating both a general customer support team and a more technical one for product-specific queries. During the course of my career, I have noticed the misconception end users have in regards to what technical supports role is within an organisation and what customer support role is and if they are the same.

Of course, from a customer experience perspective, these appear as one and the same. After all, customers don’t mind who they speak to about their issue, they just want it resolved as quickly as possible so they can move on with their day.

In this article, we give a bit of a behind the scenes look at how we process customer queries at CyberSmart so we can make sure the right expert is addressing the right questions as quickly as possible.

Customer Support vs Technical Support

Our customer support is split into two main areas: Customer Success and Technical Support.

Customer Success are the friendly team answering our phones and online chats. They do the initial fielding of questions and offer support on everything non-technical within the non-technical customer experience (payment, planning, general questions).

Any questions relating to our product (how to install it, how to configure, etc.) are answered by the Technical Support team in order for our customers to get the best value out of our product.

First-line support

When a customer gets in touch, the first level of support they receive is from the Customer Success team. They manage our FAQs page and knowledge base and use it as a tool to help customers find the answers they need for common queries. First-line support handles 40%-60% of end-user queries. They have a basic understanding of the product and the business but they aren't technicians so if there's a question they can't answer about the product, they pass it on to the second-line of support.

Second-line support (Complex Queries/Problems)
When a ticket is escalated to second line support this usually means the query or problem requires more in-depth technical knowledge of the product.

Third-line support (Bespoke support)
Third-line support largely deals with tickets that require a bespoke solution for the organisation which is experiencing technical difficulties with our product. This means we might work directly with the engineering team to build a solution to a problem for a customer. After all, if they have that need, it's likely others do too.

What is Technical Support?

Technical support is what product-focused organisations like CyberSmart use to help our MSPs & direct partners get the most out of our product. Typically, we receive queries via live chat, emails, or phone calls. We resolve technical issues such as installation (PC, MAC & mobile), dashboard login errors, and other technical issues that are causing headaches for our customers.

A third-line of support question might be something around need to do a mass installation of our app to many sites but not knowing how to configure their RMM. If we got a request like this from an MSP, we would work to build them a custom solution for mass installation that they could use for our apps and others.

In summary, CyberSmart's support team is not a call centre stocked with rote answers to simple questions. We also have the capacity to help the vision of our customers come true by making the CyberSmart product fit their needs.

Cyber security is essential for business today but the process of protection doesn't have to be difficult, time-consuming, or expensive. CyberSmart was built for non-technical businesses to serve as a full cyber security team in one product with top-notch customer support. Start protecting your business today.

Securing a remote workforce: customer spotlight on LegalEdge

LegalEdge had a remote workforce back when it was still a choice. For ten years, LegalEdge has made in-house legal services accessible to small businesses and start-ups using a uniquely flexible model and a completely remote team of lawyers.

Helen Goldberg, COO Legal Edge

We sat down with Helen to learn more about her security needs and how she uses CyberSmart Active Protect with her remote team.

What were the security and/or compliance challenges you were looking to overcome?

For the most part, the challenges we faced stemmed from the fact that all our lawyers work flexibly. On the one hand, with all that is going on now, this has put us in a fortunate position to continue business as usual. However, with everyone working from home or the coffee shop as well as using their own personal devices, this has the potential of leaving many loose ends that threaten our company’s security – a fairly unique challenge that may not be unique for long, and which CyberSmart really worked with us on.

How is security important to your organisation?

As a law firm, we’re obviously incredibly risk averse – Therefore, security has always been important to our company and is something we actively wanted to get better at. Unlike a lot of businesses, most of the people we work with are freelancers, though we have some employed staff. So, we wanted to ensure that we had that extra layer of protection, particularly as they all use their own devices.

How did you discover CyberSmart and why did you select it as your solution?

I’m on a COO network with a lot of fast growth tech companies, which has been a fantastic network for me and for a lot of the COOs on it too. That is how we heard about CyberSmart . There was a lot of discussion around GDPR at the time. The guys at CyberSmart came in and did a presentation for us. As is typical in our industry, we are fairly slow to update on tech, but we just really liked the way CyberSmart did things and how they talked about their product. Because we’ve got a fairly unique setup, it was really important for us to up our game on cybersecurity: they were just really good and helpful for us in what otherwise could have been a bit of a painful process.

Which of CyberSmart’s capabilities are most valuable to you and why?

Just that extra layer of security for our remote workforce. Our model was always flexible, but the CyberSmart guys have really enabled us to embed security into this flexibility. When I used to travel on the tube and log in at the stations to check my emails, there was always that worry that I wasn’t secure. Now I know that I’ve got the level of security that I can have, or that I need to have, to protect myself . You hear about hacking, but you don’t really worry about it until something bad happens – now we don’t have to.

When I used to travel on the tube and log in at the stations to check my emails, there was always that worry that I wasn’t secure... You hear about hacking, but you don’t really worry about it until something bad happens – now we don’t have to.

It has helped us up our game. With less tech-savvy people, you’re never sure what is or is not okay. We might think we’re secure and actually not be. CyberSmart has eliminated this ambiguity for us.

I’m working from a MacBook; some people are working from old PCs... everybody’s on different devices, including iPhones. Regardless, the guys at CyberSmart have all our bases covered. We have some IT support now, but we didn’t when we first started this journey and they were there every step of the way to help us implement it. In order to get the Cyber Essentials certification, we had to pass an important questionnaire.

This required us to put in place a fairly complex policy that explained to our people what they had to do or stop doing. For example, they could not log into their devices from a coffee shop without a secure connection. But then we brought in a VPN, which helped to resolve that issue and the team at CyberSmart worked with us to make sure we were doing all the right stuff along the way.

What kind of cost savings or benefit have you found from increased security?

It was important for us to do better with our cybersecurity, so whilst it is an investment, the cost is reasonable for a business of our size and nature. We liked what CyberSmart offered and how they conducted themselves; the fact that they came recommended from another business we knew was also very reassuring.

What advice can you give someone seeking security solutions around remote working?

Give CyberSmart a call! They have been a hugely helpful partner and their customer service is outstanding. We have clients who say: “I need somebody who’s got my back on these things” and that’s when you outsource to the right people for the right price; that’s exactly what these guys have done for us.

Learn more about how to secure your remote workforce using CyberSmart Active Protect.

Our Head of Engineering talks managing a global remote-only team

Meet Rob Minford our Head of Engineering at CyberSmart. Even though we're all working from home these days, Rob's team has always been fully remote and is scattered across the globe.

In this interview with The Remoter Project, Rob talks about the benefits and challenges of working in a remote hybrid company (with some of us in an office and his distributed engineering team).

The Remoter Project is a venture that showcases the human side of remote working and explores how to successfully build and scale remote teams.

Interested in joining our growing team at CyberSmart? Check out our careers page.

Is your remote team making these security mistakes?

Summer days are here. As people begin to gather in the parks again and shops re-open, it’s beginning to feel like life is going back to normal. But for many of us, that normal won’t include going back to the office.

Consulting company Global Workplace Analytics estimates that after the pandemic, 30 percent of the entire workforce will continue to work from home regularly. Armed with Zoom and our Slack channels, we’ve succeeded in proving that a team doesn't need to be in an office together everyday to get things done.

But while a new remote world is great news for the weary commuter of 2019, it’s also great news for the cyber criminal. Over the past few months, cyber crime increased as hackers take advantage of employees who are used to relying on their offices and IT staff to protect them.

It can be hard to convince staff of the importance of digital security. After all, most people outside of IT tend to think of cyber crime as something planned and targeted- a mastermind hacker out to get critical information from the government or cause trouble for a big corporation.

What would they want with my little business? I'm too insignificant to be targeted for cyber crime. This is the wrong way to think about it. Most cyber criminals are just opportunistic. They didn't choose to rob your house because they knew you had a stash of cash under the bed (or all your passwords on your desktop). They chose it because you left the door open.

Using unsecured networks, not keeping software up to date, reusing passwords- there are a lot of ways to open the door. Luckily, many of these risks follow similar patterns and can be avoided through a few fundamental security practices. The most effective thing businesses can do right now to protect their data, their employees, and their customers is to educate their workforce on what these are and why they are important.

Here are some of the biggest (but pretty simple) mistakes your remote team might be making:

People having access to data they don’t need
According to data by the UK's Information Commissioner's Office, employee error continues to be a leading cause of data breaches. They might fall for a phishing attack or just accidentally send an email with a sensitive attachment to the wrong person.

One way to easily reduce the harm caused by data breaches, is to only give employees access to information they need to do their job. It might be easier to make a folder on Google Drive accessible to everyone in the company, but it also means you're opening a lot more doors to that data than you need to.

Unsecure networks

While people can be generally pretty savvy in terms of updating their own machines ( laptops etc) they generally forget about their routers after they set them up at home. When you first get a router, it's important to login to change your usernames and passwords (which can be easy for hackers to find online) and to turn on Wireless Network Encryption.

Employees can also use a VPN (Virtual Private Network) to change their IP address, so hackers can't see the actual location of their device. It could also allow employees to access company information from personal devices. As a business, encourage employees to follow the same protocols you had in your office in terms of accessing company data.

Out of date software and devices

It's extremely important to keep all hardware up-to-date - from laptops, routers, servers or the increasing number of IoT devices in the home to protect against things like ransomware attack. Ransomware attacks are among the fastest growing cyber threats (one report projected that in 2021, companies will fall victim to an attack every 11 seconds). Software patches are released all the time to protect against known vulnerabilities but they don't work if the system is outdated. Making sure you are using up-to-date operating systems and that software is running on the latest version is a critical part of cyber hygiene.

Not taking security seriously

Most people outside of IT have been guilty of this at some point. It's just simpler to have one password for everything! And my wife's birthday is the easy to remember! (most of the time). But these little things can have big consequences- particularly when employees are using personal devices for work. A personal phone that has access to the company Slack channel, needs to be just as a secure as a PC in the office.

The majority of breaches are made through simple human error. We weren’t paying attention and accidentally sent an email we shouldn’t have. It's critical that employees know what data in your business is sensitive and the consequences of a breach.

Lack of education

Sometimes data breaches happen because people just don't know how to see them coming. For example, as phishing scams become increasingly sophisticated, employees need to know how to spot a suspicious email and how to report it.

Recent reports show that employees aren't big fans of security. 42% of staff state that their company's security policies (like having to have an IT admin install new software) make it more difficult to do their job. This is why education is so important.

We launched a page specifically designed to offer resources for small businesses who are transitioning to a remote work environment. These include company policies and a security checklist for employees.

The reality is that in this unstable economic environment, businesses are less likely to invest in their cyber security. But cyber security doesn’t have to be expensive or confusing. This kind of basic cyber hygiene can go a long way in preventing the threats we're seeing increase on a daily basis.

The dream of working from anywhere in the world may finally be materialising for many. Let’s make sure it happens safely.

Show your customers you value their data by getting certified in Cyber Essentials, the UK government scheme that covers all the fundamentals of cyber hygiene.
Inside CyberSmart Active Protect: what's monitored and what's not

This month, we made the decision to include our CyberSmart Active Protect with all of our certification options. We did this because we know real security can’t be achieved through a certification audit once a year; it requires continuous assessment of compliance.

We also know that up to 98.5% of cyber attacks can be prevented by following the controls that our software monitors. That’s why we encourage businesses and their employees to install the app on any device that might be used for work purposes.

And that’s where things get sticky. A work app on my personal phone? That monitors me?

We get it. It all sounds a bit Big Brother. So we’re here to clear up exactly what we ‘monitor’ with our CyberSmart Active Protect and why it’s good for employees as well as businesses.

What we see

What an employer sees on devices that have the CyberSmart Active Protect installed:

  • Whether your device is complying with the five controls of Cyber Essentials
  • Which software you have installed on your computer and if it is up-to-date
  • The make, model, and year of your device
  • Your operating system (like Microsoft Windows or Apple's macOS) and which version you are running

What we don’t

An employer can’t see anything but what’s listed above but here are a few points for clarification:

  • Which websites you visit
  • Which apps you have installed on your mobile device (these are different from software. Your employer has no way to see if you downloaded CandyCrush again after you so admirably recovered from your addiction)
  • Your physical location with the device
  • When you are online or how much you are using different software on your devices

Checking your vitals

One of our engineers described CyberSmart Active Protect as an ‘ongoing health check.’ This is a good way to think about it. We’re taking your vital signs but we don’t get into any more detail than we need to. Is your firewall still up? Is a piece of software out of date that could leave a door open for attack? If it is, you’ll get a notification and clear instructions on how to fix it.

It’s good for employees too

When a device is hacked, criminals aren’t just looking for business data on customers. They will take any useful piece of information they can. With the CyberSmart Active Protect installed, employees will enjoy the benefits of protecting their personal data as well as the company’s on their personal devices.

Take the first step to protecting your business and your employees today. If you got your Cyber Essentials certification through CyberSmart, you can now access one free license to CyberSmart Active Protect via your dashboard.

Don’t take the bait: tips for avoiding a phishing attack

Phishing scams

We’ve all gotten those emails before. Congratulations! You’ve won a £100,000 voucher from Argos. Click here in the next three hours to claim your reward!  We want to believe them. They just might be real. And that is exactly the mentality cybercriminals are taking advantage of. 

These kinds of scam emails are known as phishing attacks- and they are everywhere. According to Verizon’s 2020 Data Breach Investigations Report released this week, they made up nearly a quarter (22%) of all cyber breaches this year. 

We've seen an even greater rise in these over the past three months as hackers preyed on widespread anxiety by impersonating official sources like the US Center for Disease Control, the World Health Organisation, and various government offices offering 'updates' and 'alerts' around the virus.

Phishing attacks fall into two broad categories. They are usually trying to persuade you to click on a link that will lead to a spoof site and require you to enter personal data (credit card details, personal or bank information, etc), or to download malware onto your device (either through a link or an attachment).

Many of these phishing emails can be extremely convincing. Even EasyJet fell victim this week. So how can you protect your business, your employees, and ultimately your customers against them?

Training employees how to recognise the warning signs of phishing emails is the best way to prevent these kinds of attacks and might be the best solution for smaller businesses.

While there are a few great pieces of anti-phishing software out there that use email filtering to detect and flag suspicious email addresses and malicious links or attachments, the most convincing phishing attacks often slip through the net of even sophisticated software.

Something smells fishy here: spotting the signs of a scam

Read carefully

Copywriters at big companies spend a lot of time crafting emails and there's often a noticeable lack of quality with phishing scams. A few tell-tale signs include:

  • Generic greetings - Dear user..
  • Urgent deadlines and calls to action - Click now or your home insurance will expire!!
  • Grammatical mistakes and spelling errors - Plese download the attached file to keep Your Account open. If it doesn’t seem professional, it probably isn’t.
  • News that is too good to be true - We've found a cure for the coronavirus. Click here to order your safety kit.

Check the email address

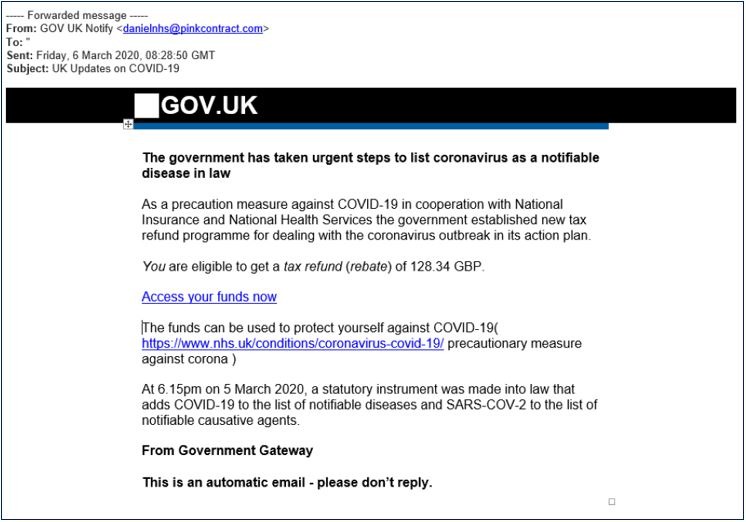
Be sure to check the email address as well as the name of the sender. Although phishing scams often use the name of someone you know or a company you work with, the email address won’t match up. If it's from @gmail.com address, for example, it's probably not a legitimate organisation.

A recent phishing attempt. Note the sender's email address - @pinkcontract.com

Question their professionalism

Remember that real brands will never ask you for personal details over email or force you to their website.

Think before you act

Above all, just take a moment to pause before you interact with any email. Before you click or download anything, reflect for a second by asking: do I know this person? Have I actually ever bought anything from this brand? How does the World Health Organisation have my work email address? Why can't Karen from Accounting spell correctly?

An ounce of prevention is worth a pound of cure

As attacks become more sophisticated, it’s almost inevitable that you or someone you know will fall victim at some point. But following basic cyber hygiene can help reduce the harm of these attacks. 

A simple way to mitigate against phishing attacks that steal credentials is to enable two-factor authentication on your accounts right now. Two-factor authentication means that when you log in you need both a password and a second form of confirmation (like a text to your mobile, for example).

Having this extra layer of security means that even with your username and password, the hacker will not be able to access employee accounts.

If an employee or business realises they have been breached, they should immediately take action by changing their personal password or disconnecting their device from the network and alerting employees in the rest of the company.

People can help prevent the spread of these large-scale attacks by immediately reporting suspicious messages to Suspicious Email Reporting Service (SERS): report@phishing.gov.uk which support's the government's Active Cyber Defence programme.

Looking to improve your cybersecurity but not sure where to begin? Start by getting certified in Cyber Essentials, the UK government scheme that covers all the fundamentals of cyber hygiene.

CTA button

When cyber security saves lives: examining the healthcare industry

Three years ago today, the UK’s National Health Service descended into chaos.

In one fell swoop, a fairly unsophisticated worldwide ransomware attack called WannaCry infected computers in hospitals across the country, hijacking thousands of pieces of connected medical equipment and holding patient and hospital data for ransom.

Becker’s Hospital Review estimates that in the United States data breaches cost the healthcare industry approximately $5.6 billion every year. The WannaCry attack cost the UK healthcare system nearly £92m. But while it was the largest breach the NHS had ever experienced, it wouldn’t be the last.

In terms of basic cyber security, the healthcare industry lags woefully behind other sectors like finance and manufacturing who often build their infrastructure with data security in mind. This is especially troubling given how attractive healthcare breaches can be to hackers (personal health information is worth an average of 10 times more than financial information on the black market). Not to mention the dire risk to patient care when day-to-day functions are interrupted. 

Here are some of the ways in which the current healthcare system is more susceptible to breach than ever and why incorporating security practices needs to be prioritised:

A complex supply chain

When we speak about the healthcare industry we aren’t just talking about hospitals and computers full of medical records.

The healthcare system is possibly the most complex supply chain in our economy. It includes everything from cleaning supplies to CRM appointment reminder software, scanning machines to climate-controlled storage of drugs shipped from all corners of the globe.

It is common practice for hackers to target the supply chains of the organisations they want to access. It is very often these small suppliers- 15 or 20 employee companies- that offer an open door through weak security practices. A November 2019 study by Orpheus of NHS suppliers showed that 95% lacked advanced security protection. 88% of them had already experienced some sort of email and employee password leaks before working with the NHS.

There is much at stake. Trust in this highly regulated industry is paramount. A data breach for a small supplier could mean the end of their business.

There is much at stake. Trust in this highly regulated industry is paramount. A data breach for a small supplier could mean the end of their business.

Data gone digital

The days of paper records are all but gone in healthcare. And with good reason. Digitised patient data makes it easy to quickly communicate between internal hospital departments and outpatient clinics, and to ensure information is always accessible and up-to-date. 

However, it also makes the institutions that hold this data an increasingly attractive target. Once acquired, patient data can be held for ransom or sold on the black market.

Last year, an Israeli research group exposed more insidious potential consequences when it demonstrated how a hacker could very quickly and realistically add or remove medical conditions (such as the appearance of a tumour) on 3D medical scans in real-time. Although this would likely only be used to target specific individuals for specific reasons- they mentioned insurance fraud and political assassination- it demonstrates how severe the consequences can be for even a simple breach.

Connected and outdated devices

From hospital lifts to MRI machines and implanted pacemakers, the healthcare system is increasingly connected to the internet. Doctors and nurses rely on these machines to monitor patient health and to serve as a partner in diagnosis.

Unfortunately, every connected device offers another potential entry point for hackers and the level of security of each device varies widely. Some of them are new and modern but others, such as expensive scanners may be ten or 15 years old. They are running on outdated operating systems and no one has the time or skillset to patch them.

A drip delivering chemotherapy drugs that had been infected with crypto-mining malware might just run a little bit more slowly. But when the precise and timely delivery of a dose is paramount, this can have disastrous results.

Hacked devices can be hard to detect and are likely running on many devices now unbeknownst to staff. A drip delivering chemotherapy drugs that had been infected with crypto-mining malware might just run a little bit more slowly. But when the precise and timely delivery of a dose is paramount, this can have disastrous results.

Over-stretched staff

A key part of any industry's cyber health is knowledge and good practice among its organisations and employees. JAMA Internal Medicine reports that the majority of breaches related to data privacy in healthcare were the result of employee error and unauthorised disclosure.

In the already overstretched world of hospitals, it is no wonder that cyber security is the last thing on the minds of most workers. It makes sense. Our healthcare providers are trained to take care of patients, not to be IT experts. 

But the NHS is the largest employer in the UK and we must come to accept that cyber security awareness is a critical part of every job- and may do its own work to save lives.

Many of these breaches could be prevented through the basic cyber hygiene covered in the government-backed Cyber Essentials scheme. This includes maintaining strong password protection, up-to-date software and firewalls, and anti-malware. If you are a healthcare provider or supplier, consider getting certified in Cyber Essentials.

Mythbusting: on security and why we're still using Zoom

Amidst its general path of destruction, coronavirus has blessed only a select few industries in lockdown (we’re looking at you baking supply companies) and fewer still have experienced a rise as meteoric as Zoom.

In the month of March, the video conferencing software jumped from 10 million to 200 million daily users. Everyone from politicians to pick-up football leagues is hosting Zoom chats making a moderately well-known company into a household name and an integrated part of our lives. 

But this rapid expansion has brought media scrutiny with it. The past few weeks the news has been littered with stories of Zoom security breaches and questions around its reliability and safety. We’re unpacking a few of the myths behind these reports and explaining why we, as a cyber security company, are still on the Zoom bandwagon.

Some technical stuff

First, almost all conferencing software, including Zoom, uses HTTPS/TLS- an encryption protocol that protects communications on the internet. It’s the same protocol your bank uses when you login online or via an app. The information is encrypted from you to the servers of the provider, and then re-encrypted from the provider to you via a similar secure link. 

Should the government be using Zoom to convey top secret information? Probably not. Is it fine for communicating openly with your team? Absolutely.

Basically, services like Zoom that use this encryption are inherently quite secure. Should the government be using Zoom to convey top secret information? Probably not. Is it fine for communicating openly with your team? Absolutely.

Security versus privacy

These two terms are very often and quite easily confused. Security protects strangers from unauthorised access to your data. Privacy has to do with the safeguarding of your identity. You can have security without privacy but not privacy without security.

The first wave of Zoom ‘security’ concerns was really about privacy and their collection of personal data of users. They have since updated their privacy policy to prevent anyone including Zoom employees from directly accessing data that users share during meetings including their names, and video/audio/chat recordings. “Importantly,” a Zoom spokesperson adds, “Zoom does not mine user data or sell user data of any kind to anyone.” While they don’t sell or share data with third parties, they do use Google Ads and Google Analytics.

If you really care about security

If you really care about security there are a few things you should always keep in mind when using videoconferencing. 

First, use a unique password. According to a recent report, 71% of accounts are protected by passwords used on multiple websites. One of Zoom’s highest profile ‘breaches’ was actually just a breach on another platform for which users had been using the same password thus opening them up to further attack.

71% of accounts are protected by passwords used on multiple websites.

Second, update your operating system and keep your video conferencing software up-to-date. This will mean any patches or protection by the company will be in place on your device. Alternatively, you can use a browser rather than a separate app which are less vulnerable to attack.

If you want to use Zoom there are some settings you can activate for enhanced protection and privacy. These include the option to watermark all content, and restricting meetings to people with a certain email domain (xxx@cybersmart.co.uk). ‘Zoom bombing’ (allowing random people to enter your calls) is prevented by requiring your attendees to use a password to join a meeting.

We don’t recommend recording meetings unless you’re happy with them eventually making the papers but if you must, you can choose to store them locally rather than on the cloud.

If you really, really care about security

If you work in an industry with incredibly sensitive data that requires end-to-end encryption, Zoom may not be the service for you. They don’t truly offer this but there are a few others that do. You might consider using Wire or Webex (this is what we use to conduct remote security audits for Cyber Essentials Plus certification).

Video conferencing is a must in the remote workplace but there are a few factors to consider when deciding which service to use. The National Cyber Security Centre offers some great guidance on this. 

As always, remember that the majority of cyber attacks can be prevented through basic cyber hygiene and the guidelines covered in the government’s Cyber Essentials scheme.