What is Cyber Essentials? Mastering the five controls of SME cybersecurity

what is cyber essentials

You might have heard that it’s something your business needs, but what is Cyber Essentials? 

Cyber Essentials is a government-backed scheme designed to help SMEs protect themselves and stay productive in a world of increasing cyber threats. And with 50% of UK businesses becoming victims of cybercrime in 2024 so far, many consider it a requirement rather than a consideration.

Why is Cyber Essentials important?

The sad truth is that every business, no matter how small, could become a target of a cyber-attack. And growing supply chains and reliance on technology services can add to your vulnerability.

Cyber Essentials is a low-effort way for any SME to go from 0% to 98.5% protection against the most common cyber threats. In as little as 24 hours, you can receive Cyber Essentials certification. 

For some businesses, Cyber Essentials is mandatory. If you want to secure government or MOD contracts, it’s essential. 

PwC revealed that 85% of consumers “wish there were more companies they could trust with their data.” And in the B2B space, revenue in the Cybersecurity market is projected to reach US$185.70bn in 2024. So, you can bet that they’ll look hard at their potential vendors and suppliers, too.

And while Cyber Essentials isn’t a panacea for all cyber threats, it provides a valuable set of controls that deliver cost-effective cybersecurity for any business. With this foundation and protection from over 98% of common cyber threats, you can grow your business with confidence.

What’s preventing businesses from getting cyber essentials?

Only 31% of UK businesses undertook a cyber risk assessment in 2024. Those who haven’t often believe that:

  • It won't happen to them. Many businesses feel as though they fall under the radar and that data breaches are out of the question
  • Their business is too small. Some SMEs feel their business is too small and don't need to assess risk because their processes don't need improving
  • They don’t have enough budget. SMEs who don't understand the value of Cyber Essentials often feel the cost of a cybersecurity certification outweighs the benefits.

Sadly, any business can fall victim to a cyber-attack, so you can't put a price on cybersecurity. Cyber-attacks cost UK businesses £10,830, on average.

Who runs Cyber Essentials?


Cyber Essentials is the brainchild of the National Security Centre (NCSC). Founded in 2016, the NCSC combines expertise from CESG (the information assurance arm of GCHQ), the Centre for Cyber Assessment, CERT-UK, and the Centre for Protection of National Infrastructure. 

Want to protect your business from 98.5% of cyber threats? Get Cyber Essentials certified today.

What areas does Cyber Essentials cover?

Cyber Essentials covers five key areas of cybersecurity across your IT infrastructure, including common outliers, like thin clients, BYOD, and home working devices. The NCSC updates the certification regularly, as modern technology becomes commonplace, to keep pace with today’s working world.

  1. Firewalls. The boundary defences of your networks
  2. Secure configuration. Security measures for building or installing devices
  3. User access control. Managing user access and admin rights
  4. Malware protection. Protection from malicious software
  5. Patch management. Making sure all systems are updated correctly

How it works

Cyber Essentials is straightforward. All you have to do is complete a self-assessment questionnaire and submit it via an online portal. The assessment questionnaire is around 30 pages and is broken up into eight sections. It includes questions like:

A4.7. Have you configured your boundary firewalls so that they block all other services from being advertised on the internet? By default, most firewalls block all services from inside the network from being accessed from the internet, but you need to check your firewall settings.

On average, we’ve found that it takes small businesses around two weeks to complete an assessment. When you submit your assessment, the certification body reviews and grades your application. They have a ‘pass/fail’ system, so once you’ve passed, you’re good to go.

The five Cyber Essentials controls

Firewalls

Firewalls are your boundary defences. They prevent and stop unrestricted access to and from private networks. Set up correctly, boundary firewalls and internet gateways allow you to take control of your system, and who can access it. And it's easy to adjust your firewall as required. 

Secure configuration

Secure configuration involves configuring computer systems, networks, or software applications to minimise potential security risks – essential when managing your servers. Configuring computers and network devices is necessary to keep vulnerabilities at bay, and will help to prevent unauthorised activity. With this in place, you can rest assured that each device will only provide the minimum data and information when building or installing.

User access control

Get complete oversight when managing user access and admin rights. It’s easy to give multiple users administrator access for convenience, but it’s crucial to restrict it to prevent hackers from obtaining your information and data.

Malware protection

Protect your business from malicious software with antivirus support. This type of data breach can wreak havoc by corrupting crucial files and stealing confidential data. Not only that, but the software could potentially block access for ransom. 

Securing your business against a wide variety of malware is essential to protect your privacy, devices, and reputation.

Patch management

Update your software as soon as new patches become available. Patch management is critical to prevent hackers from exploiting known weaknesses and updating software and operating systems can fix vulnerabilities before they become a serious issue.

Want to know more about the different types of cybersecurity certifications available to UK businesses? Then check out our comprehensive guide to Cyber Essentials and beyond.
Cybersecurity certifications


Cyber Essentials vs ISO 27001 – key differences and benefits

cyber essentials vs iso 27001

Practising good cyber hygiene is essential for SMEs. To reduce risk, the UK government has developed guidelines on how to defend against threats.  

But it’s not always easy to know which standard is best for your business. Which should you get and why? To help you decide, let’s look at Cyber Essentials vs ISO 27001.

What is Cyber Essentials?

Cyber Essentials (CE) is a government-backed scheme proven to protect against common cyberattacks. It’s the minimum certification required for any government supplier responsible for handling personal information in the UK.

For SMEs, a CE certification demonstrates you’re serious about security – both to customers and regulators. 

Your security is evaluated across five categories. You must:

1. Configure and deploy a firewall

Your firewall needs to protect all devices – especially those connected to a public or untrustworthy network.

2. Use secure configurations for devices and software

Most devices and software have default settings aimed to make the device as open and available as possible. These can leave you open to attack. 

CE requires you to reconfigure your settings to maximise security. This includes using strong (not default) passwords and introducing extra layers of security such as two-factor authentication.

3. Make use of access control to prevent unauthorised access to data and services

Your employees should have the minimum access needed to perform their role. You’ll need to set up and define access levels for standard and administrative accounts to minimise risk. 

Unlock the future of MSP cybersecurity

Explore the opportunities and challenges facing MSPs in 2024. The CyberSmart MSP Survey reveals key strategies for achieving Complete Cyber Confidence.

4. Protect yourself against malware such as viruses

Malware, short for malicious software, is any computer program that causes harm to a device or its user. 

You must implement one of the following to meet these requirements:

  • Anti-malware solutions such as Windows Defender or Mac OS XProtect
  • A sandbox environment with restricted access to the rest of your files and network
  • A software whitelist to prevent users from running anything potentially harmful

5. Keep devices and software updated

Device manufacturers and software developers release updates (also known as patches). These are key to fixing known vulnerabilities in the software and must be installed when they become available.

Want to know more about the certifications available to you? Check out our guide to UK cybersecurity certifications.

What is ISO 27001?

ISO 27001 is an international standard for information security. It defines what’s required for establishing, implementing, maintaining, and improving an information security system. It’s much more comprehensive than Cyber Essentials. 

Rather than having specific guidelines to follow, ISO27001 has 14 controls that support compliance. 

1. Develop an information security policy

This provides direction to support your people. It should clearly lay out how to manage information in accordance with laws and business requirements. You should regularly review it to check it’s effective.

2. Implement and manage information security within your organisation

You need to provide a mechanism for managing information security, including coordinating responsibilities with employees and maintaining contact with authorities, third parties, and security providers.

The ISO 27001 provides the framework for managing information security in different aspects of your organisation. For example, teleworking or project management.

3. Provide training and awareness to HR

Ensure employees are aware of their responsibilities and given suitable training to fulfil them. You also need make sure any changes in employment conditions don’t affect security standards. 

4. Ensure organisational assets are secure

You should be able to identify and classify information security assets based on the sensitivity of the information they handle. You’ll also need to assign staff responsibilities for keeping devices secure. 

5. Make use of access control to protect information

Employees and third parties should have restricted access to your information. You’ll need formal processes to grant and revoke user rights. 

6. Protect the confidentiality and integrity of information 

Use encryption to protect the confidentiality and integrity of your data. This can help keep you safe by making the data unusable for hackers – even if they do manage to access your network.

7. Prevent unauthorised physical access to your workplace

Protect physical assets from unauthorised access and natural disasters. If these areas are breached, for example by forced entry or extreme weather, it could cause operational issues and expose sensitive data. 

8. Deploy secure configurations for operational infrastructure

You must securely configure devices, software, and operating systems. This might include:

  • Using antivirus software
  • Changing default settings to security-first ones
  • Gathering and recording evidence of security vulnerabilities 

9. Secure configurations for network infrastructure

All routers, switches, services, and software that make up your network must be configured to standards you set in a network services agreement. The agreement should identify security features and management requirements for the network, including: 

  • How to monitor and control network traffic
  • How to securely use applications and systems, e.g. by using a firewall

10. Prioritise security when acquiring, developing, and maintaining information systems

Consider security at every level of your information system. From the moment you set up a new system, you must have security controls to prevent the loss or misuse of information.

11. Ensure information security for activities by suppliers

Monitor all outsourced activities to confirm that your suppliers comply with the same security requirements you’ve laid out for your own organisation. 

12. Develop an effective approach for managing information security incidents

If an accident occurs or your systems are breached, you need to:

  • Communicate the details of the security incident and event quickly
  • Gather and preserve evidence for further analysis
  • Develop your information security process to prevent a repeat incident

13. Prevent information security failures from interrupting business continuity 

ISO 27001 provides a step-by-step process to continue operations after a breach. A key aspect of this is making sure staff can access information systems. 

14. Ensure compliance with information security policies and standards

Get guidance on how to adhere to standards and abide by the law so you stay compliant.

Cyber Essentials vs ISO 27001 – what are the main differences?

There are five basic differences when comparing the two security standards. 

  1. Flexibility – Cyber Essentials is prescriptive. You’ll get detailed guidance on what to do and how to do it. ISO 27001 requirements, on the other hand, are broader and leave more to your discretion
  2. Time –  It can take as little as a day to get CE accredited whereas ISO 27001 takes 6-9 months
  3. Audits – There’s no audit in the Cyber Essentials assessment, but for ISO 27001 you’ll have yearly maintenance audits and a recertification audit every 3 years
  4. Location – Cyber Essentials is only recognised in the UK, whereas ISO 27001 is international
  5. Level of difficulty – Cyber Essentials is very much an entry-level qualification that gives you a good foundation of knowledge. ISO 27001 is advanced in subject matter and assessment criteria

Cyber Essentials vs ISO 27001 – the benefits

Cyber Essentials is a great entry-level qualification with simple instructions and a fast certification process. It’s perfect for business that want to show a commitment to cyber hygiene and bid for government contracts.

ISO 27011 is an internationally recognised accreditation that showcases robust security practices – which may give you a competitive edge. 

Choosing your accreditation

The best certification for your business depends on your requirements, size, and infrastructure. Now that you know the key talking points in the Cyber Essentials vs ISO 27001 debate, hopefully you’ll be able to make a more informed decision.

Discover the latest cybersecurity insights for MSPs

Uncover the critical findings from the CyberSmart MSP Survey 2024. Learn how managed service providers are navigating the evolving cybersecurity landscape and what it means for your business.

Press release: MSP market is pivoting towards providing cybersecurity solutions, new CyberSmart Research indicates 

MSP report

Increased focus on offering security as a service from the customers of Managed Service Providers, CyberSmart survey finds 

New research conducted by CyberSmart, a leading provider of SME security solutions indicates that Managed Service Providers, historically expected to manage IT infrastructure for their customers, are increasingly expected to protect this infrastructure too. 

The research, conducted by OnePoll in Spring 2024, polled 250 senior leaders at UK-based Managed Service Providers, found that 65% of MSP customers now expect their provider to manage either their cybersecurity infrastructure or both their cybersecurity and IT infrastructure. 

This interest in Managed Service Providers’ security capabilities has been noted by the MSPs surveyed in new business/RFP meetings, where 73% suggested either somewhat more (51%) or much more (22%). 

The expectation that MSPs should manage security as well as IT can be viewed as a response to the security capabilities which their customers have in-house: 37% of respondents indicated that only 20% or less of their customers have a specific cybersecurity role in-house, reflecting the need for MSPs to take ownership of cyber on behalf of their customer base 

What’s more, it has been reflected in strategic and structural changes taking place at MSPs. Respondents indicated they had made the following changes in the past 12 months: 

  • 33% had increased the associated budget for their security capabilities 
  • 28% have increased the associated budget for their regulatory capabilities 
  • 28% have made specialist cybersecurity hires
  • 14% have made specialist regulatory hires 

“This change in customer expectation and need reflects a sea-change in how Managed Service Providers need to operate,” said Jamie Akhtar, Co-Founder and CEO at CyberSmart. Managed Service Providers are a lifeline for many SMEs and the underappreciated backbone of much of our economy’s IT infrastructure as such. As IT and cybersecurity threats become increasingly intertwined, it makes sense that managed service providers would begin to offer more security services. However, as previous research has indicated, MSPs themselves are vulnerable to cyberattacks. It’s important that they - and the wider security industry - do all that they can to empower MSPs to provide the security services they are now expected to with absolute confidence.” 

Is your MSP ready for cyber threats?

With 87% of MSPs experiencing breaches, understanding the current cybersecurity challenges is crucial. Access the CyberSmart MSP Survey 2024 to equip your organisation with the knowledge to stay ahead.

BYOD and Cyber Essentials security: how certification protects your business

cyber essentials byod

You’ve probably heard the phrase BYOD before. ‘Bring Your Own Device” has been the darling of business and technology journalists for much of the last decade. And BYOD really is more than just hot air and hyperbole. For SMEs, it has the potential to change the way we approach procurement and resourcing forever.

Back in 2018, research estimated that BYOD adoption in the UK had reached 45% of UK businesses. However, that was before the pandemic and the dramatic increase in remote working. While current estimates vary, most indicate that between 70% and 80% of businesses now have some kind of BYOD scheme.

BYOD gives employees the option to use their own devices for work. And, as with any device that connects to your network and has access to business information, these devices fall within the scope of Cyber Essentials certification.

Unlock the future of MSP cybersecurity

Explore the opportunities and challenges facing MSPs in 2024. The CyberSmart MSP Survey reveals key strategies for achieving Complete Cyber Confidence.

BYOD cybersecurity risks

Employees using their own devices to access company networks and data presents various problems. Personal devices typically have less effective security measures than those configured and owned by businesses, and employees are less likely to follow strict security protocols on their own devices. There’s plenty of evidence to suggest we engage in riskier behaviour when using our personal laptops and phones.

Even if an employee only uses their personal smartphone, tablet, or laptop to check their emails at the weekend, or do some after-hours work at home, they’re still subject to Cyber Essentials’ BYOD requirements. 

It’s vital that employees follow the core principles of Cyber Essentials every time they use a device for work, whether personal or provided by the company. At a minimum, they must ensure that:

  • The device’s security settings are switched on and up to date
  • Anti-malware tools are installed
  • Apps are up to date 

What if you don’t have a formal BYOD policy? 

Even if your business doesn’t have a formal BYOD policy, it’s still important to guard against the threat posed by personal devices. For example, to ensure we’re not giving cybercriminals a backdoor into our business, we ask employees to install the CyberSmart Active Protect app on any device they might use to access work.

Active Protect constantly checks devices to ensure they comply with Cyber Essentials BYOD requirements, and flags any problems to the company, and the user. This means that however your staff choose to work, you know they’re doing it safely. 

Cyber Essentials and BYOD: why it matters

Cyber Essentials is the UK government scheme that covers the fundamentals of cyber hygiene for all types of business. It’s also a requirement for some government contracts. Cyber Essentials helps you to protect your organisation against the most common cyber attacks, whatever devices your employees are using. 

Cyber Essentials BYOD requirements may vary, but overall, they cover five technical controls:

  • Using a firewall to secure internet connections
  • Choosing the most secure settings for all devices and software
  • Controlling who has access to company data and services
  • Protecting your business from viruses and other malware
  • Keeping devices and software up to date

Following the Cyber Essentials advice for each of these controls will help you to avoid:

  • Phishing attacks
  • Malware
  • Ransomware
  • Password-guessing
  • Network attacks

Becoming Cyber Essentials-certified

Cyber Essentials certification shows that your business is using the five technical controls, and assures your current and future customers that you have a proactive and professional approach to cybersecurity. CyberSmart is the UK’s leading Cyber Essentials certification body – contact us to find out more about Cyber Essentials accreditation.

Is your MSP ready for cyber threats?

With 87% of MSPs experiencing breaches, understanding the current cybersecurity challenges is crucial. Access the CyberSmart MSP Survey 2024 to equip your organisation with the knowledge to stay ahead.

Understanding Cyber Essentials firewall requirements

cyber essentials firewall requirements

One of the five major controls of Cyber Essentials is to configure and deploy a network firewall. Let's delve into what that means in practice.

What’s a firewall?

A firewall is a network security system that creates a buffer zone between your company’s network and external networks. In simple terms, it creates a secure zone between your devices and the internet.

To qualify for Cyber Essentials, all your internet-connected devices should be protected with a firewall. 

Is your MSP ready for cyber threats?

With 87% of MSPs experiencing breaches, understanding the current cybersecurity challenges is crucial. Access the CyberSmart MSP Survey 2024 to equip your organisation with the knowledge to stay ahead.

Types of firewall 

There are two kinds of firewall that meet the cyber essentials firewall requirements:

  1. Personal firewall
  2. Boundary firewall

Personal firewall

You'll usually find these installed on internet-connected desktops or laptops. Most operating systems come with a built-in personal firewall so you're likely already using one.

Boundary firewall

Also known as a network firewall, boundary firewalls provide a protective buffer around your entire network of devices. In most cases, you’ll need a hardware firewall to deploy a boundary firewall.

How do firewalls work?

Firewalls restrict inbound and outbound traffic to ensure you connect safely to
to external networks like the internet. They prevent desktops, laptops, and mobile devices within your network from accessing malicious or harmful content. 

Firewalls do this by using rules to restrict the kind of traffic that gets in. These rules allow or block incoming traffic into a network depending on its source, destination, and communication protocol.

Cyber Essentials firewall requirements 

The Cyber Essentials firewall requirements are to use and configure a firewall to protect every device in your business. And, especially the ones connected to public or untrusted Wi-Fi networks. 

To comply with Cyber Essentials, you must:

  • Disable permissive firewall rules once they become obsolete
  • Make use of personal firewalls on devices connected to untrusted networks like public Wi-Fi or hotspots
  • Block unauthenticated and untrusted inbound connections by default
  • Review and update default passwords and settings according to the organisation’s security requirements
  • Use strong administrative passwords with a mix of upper and lower-case characters, numbers, and symbols, or disable remote administrative access
  • Set and document administrator-approved firewall rules 
  • Restrict administrative access to the firewall interface. Access should be protected with:
    • Two-factor authentication
    • An IP whitelist with a small number of devices only

Does your firewall meet Cyber Essentials requirements?

Setting up a properly configured firewall is one of the first steps towards a Cyber Essentials certification.

If you’d like to learn more about network firewalls and how to configure them for Cyber Essentials, contact us.

Or, if you want to know more about Cyber Essentials and the benefits of certification to small businesses like yours, check out our guide.

Discover the latest cybersecurity insights for MSPs

Uncover the critical findings from the CyberSmart MSP Survey 2024. Learn how managed service providers are navigating the evolving cybersecurity landscape and what it means for your business.

How to respond to social engineering attacks

respond to social engineering attacks

Cybersecurity threats are a growing concern for businesses of all sizes. Small businesses, in particular, often underestimate their risk, thinking that cybercriminals only target larger corporations. However, this misconception can lead to vulnerabilities that are easily exploited. In this blog post, you will learn about social engineering, how to prevent attacks, respond if an attack occurs, and why practice makes perfect in maintaining your security posture.

What is Social Engineering?

Social engineering is a tactic cybercriminals use to manipulate individuals into divulging confidential information or performing actions that compromise security. Unlike technical hacking, social engineering exploits human psychology rather than software vulnerabilities.

One common form of social engineering is phishing. Phishing involves sending deceptive emails that appear to be from legitimate sources. This tricks recipients into clicking on malicious links or providing sensitive information like passwords and credit card numbers. 

Phishing attacks are by far the most common type of cyber attack experienced by UK businesses. 84% of businesses that identified any breaches or attacks in the last 12 months reported experiencing phishing attacks.

Among organisations that identified breaches or attacks, 35% reported experiencing impersonation attempts, where attackers pretended to be the business or its staff in emails or online. More alarming still, although 21% of businesses yet to experience an attack didn’t think they’d need to close in the event of one, 100% of those who have been victims said they would.

So the risk is very real for businesses of all sizes, regardless of industry. But what can you do about it? 

Prevention is better than cure

When it comes to cybersecurity, prevention is always better than cure. Implementing technical controls can help safeguard your business from cyber threats. Here are a few to get you started.

Email filtering

Whichever you use, most email platforms include filtering solutions to block phishing emails, it’s how things end up in your spam folder. But what you might not know is that you can calibrate the rules yourself. Setting strict rules for what can and can’t enter your business’s inboxes can almost completely remove the chance most phishing emails will ever reach a human. 

Multi-factor authentication 

Use multi-factor authentication (MFA) for all accounts within your organisation. MFA adds an extra layer of security by requiring multiple forms of verification before granting access to sensitive information. This means, that even if a hacker does get hold of an employee’s login credentials, it’ll be far more difficult for them to gain access to company platforms, documents, or sensitive data. 

Regular software updates

A huge number of successful breaches start with a known vulnerability. In 2023 alone, more than 50% of the high-risk vulnerabilities tracked by Qualys were used by cybercriminals to attack victims. 

Fortunately, there’s a quick and easy way to ensure your business doesn’t fall prey. Software developers regularly release patches to address vulnerabilities, usually in the form of updates. Run these updates whenever they’re released, you can even set your operating system to auto-update. 

Technology isn’t enough 

Although technology is a vital component of cyber defence, we can’t rely solely on it. As I explained at a recent talk, for technology to be successful people must want to use it and our culture must motivate us to do so.

We can start to achieve this culture through security training and awareness. Educating employees about the dangers of social engineering and how to recognise phishing attempts is crucial. Regular training sessions can help employees stay vigilant and understand the latest tactics used by cybercriminals. This understanding and realisation of the threats and possible impacts upon individuals and the businesses they work for will sow the seeds of a strong culture.

Incident Response Procedures

Despite the best preventive measures, breaches can and will still occur. Having a robust incident response procedure in place can mitigate the damage and help your business recover quickly.

Incident response procedures are predetermined protocols that outline the steps to take when a cybersecurity incident occurs. These procedures ensure an efficient and effective response, minimising any impact on your business.

An effective incident response plan should include:

Preparation -  Ensure your team is ready to handle incidents by establishing and training on policies, tools, and communication plans.

Detection and analysis - Monitor systems to quickly identify and assess incidents, determining their scope and impact.

Containment, eradication, and recovery - Implement strategies to control the incident, remove the threat, and restore affected systems and data to normal operations.

Post-incident activity - Review and document the incident and response actions, using insights to improve future response efforts and strengthen security measures.

Practise, Practise, Practise

Developing an incident response plan is not enough. You must also regularly practice it to ensure it remains effective.

Depending on your organisation's size and resources, you must determine which incidents should be subject to a lessons learnt process. For example, all incidents with a critical or high ticket associated with them. After each relevant incident, conduct a thorough review to identify what worked well and what didn’t. Use these lessons to improve your response procedures and prevent future incidents.

Want to know more about the cybersecurity threats facing your customers? Check out the The CyberSmart MSP Survey 2024, our deep dive into the cybersecurity sector in 2024.

Press release: Cyber Confidence at MSPs high, despite falling victim to data breaches

MSP report

CyberSmart research reveals high levels of cyber confidence in MSPs, despite 87% experiencing a breach in the past 12 months.

London, UK - July 10th 2024 - New research conducted by CyberSmart, a leading provider of SME security solutions indicates that nearly all MSPS report high rates of cyber confidence across their organisations, despite the vast majority having experienced at least one data breach in the past 12 months.

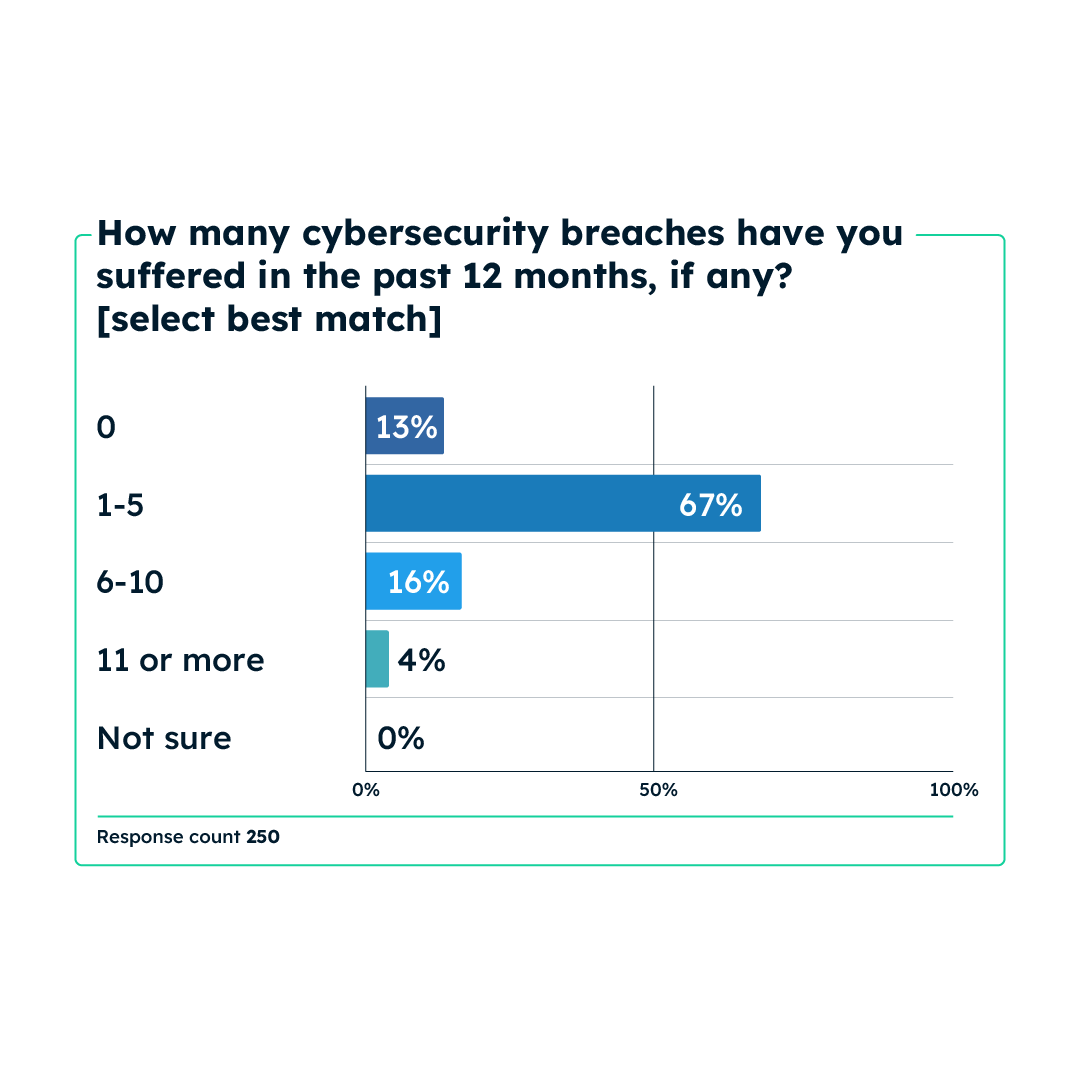
The research, conducted by OnePoll in Spring 2024, polled 250 senior leaders at UK-based Managed Service Providers, found that an overwhelming majority of MSPs - 87% - had experienced at least one data breach in the past 12 months, with 16% indicating they had experienced more than 5 incidents in the same timeframe.


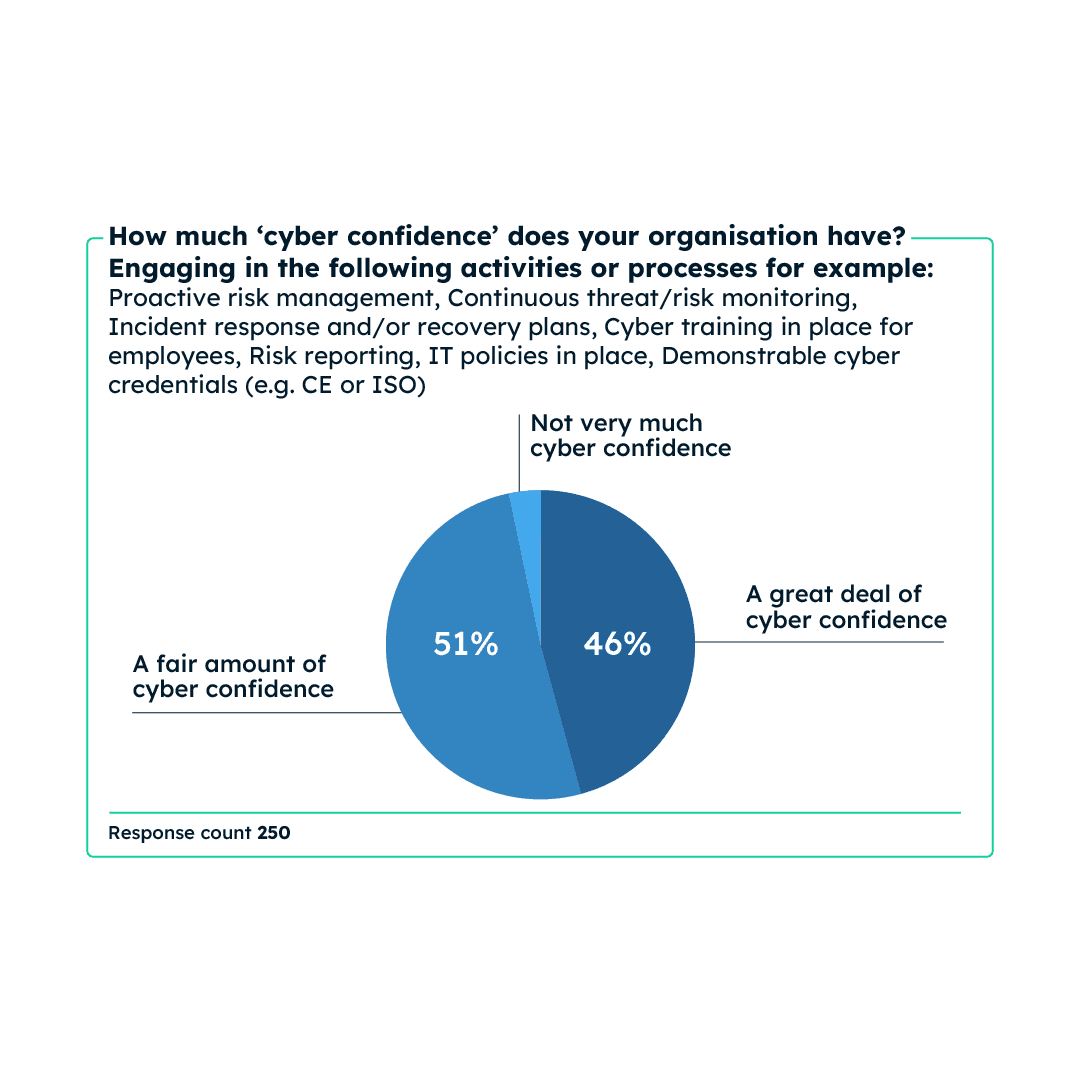
This track record on cybersecurity stands in contrast to the associated cyber confidence that the surveyed MSPs reported. Almost all - 97% - of the MSPs surveyed suggested that their organisation had either a ‘fair’ amount of cyber confidence or a ‘great deal’ of cyber confidence.

Another interesting aspect of the results is that this confidence appears to be projected onto MSP customers too, with respondents reporting that they believed 85% of their customers had either a fair or a great deal of cyber confidence.

What are the top threats to MSPs?

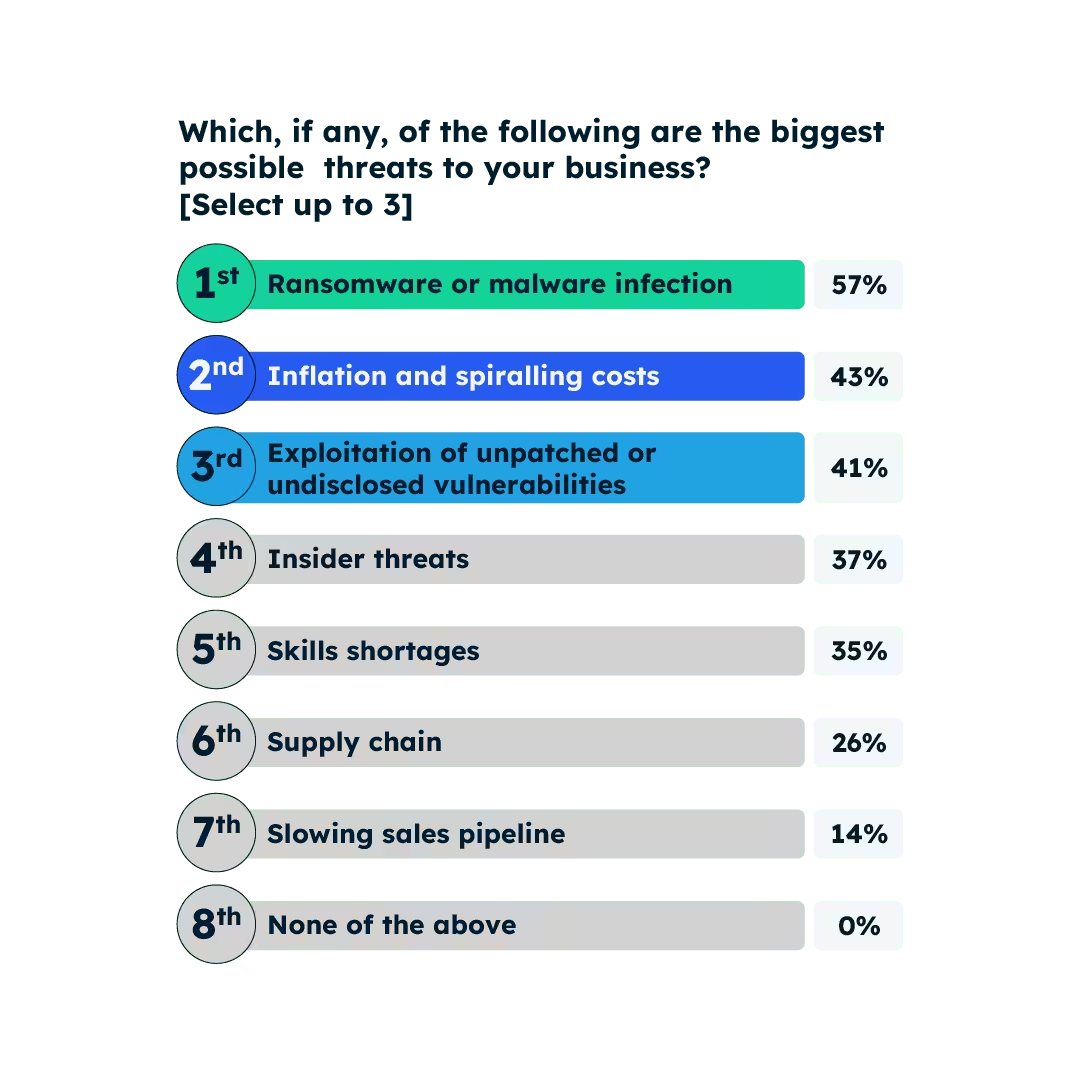
Both the customers and providers identified ransomware and malware infection as the top concern, at 55% and 57% respectively. For MSPs, inflation and spiralling costs came in second (43%) and for customers, exploitation of unpatched or undisclosed vulnerabilities was the second most concerning threat (44%).

“The associated confidence noted by MSPs is heartening but needs to reflect the reality on the ground for MSPs, and their own perception of their security posture is concerning and highlights the need for the cybersecurity to step up and work closer with Managed Service Providers,” said Jamie Akhtar, Co-Founder and CEO at CyberSmart.

“MSPs, due to the levels of privileged access they will have into multiple companies, make for an appealing target for cybercriminals. This, coupled with the fact they are responsible for the IT infrastructure of companies without IT or security resources, means it is paramount that security providers work closer with them to protect the £ 5.5 million SMEs who in many cases turn to MSPs to keep them safe. Failure to do this could be existential for many of their customers.”

MSPs suggested that a focus on cybersecurity training, IT policies and fostering a more security-conscious culture would help them to achieve complete cyber confidence.

Discover the latest cybersecurity insights for MSPs

Uncover the critical findings from the CyberSmart MSP Survey 2024. Learn how managed service providers are navigating the evolving cybersecurity landscape and what it means for your business.

8 benefits of Cyber Essentials certification

benefits of cyber essentials

Safeguarding your business from cyber threats is crucial. By gaining the Cyber Essentials certification, you can protect your business against a wide range of cyberattacks. 

Understanding the benefits of cyber essentials can help you increase trust and safeguard your business.

What is Cyber Essentials?

Cyber Essentials is a cybersecurity certification designed by the government to give organisations a standard level of protection.

There are five security controls with criteria to address cybersecurity effectively and mitigate the risk from cyber threats: 

  • Firewalls
  • Secure configuration
  • User access control
  • Malware protection
  • Security update management

1. Improve your security processes

Once accredited, you’ll be at less risk of GDPR non-compliance. It’ll protect you against the estimated  7.78 million cybercrimes that UK businesses experienced in the last 12 months.

The 8 benefits of Cyber Essentials

2. Build trust with customers

With so many high-profile cyberattacks worldwide, consumers are rightly concerned about who to share data with. They want to know that their personal data will be safe.

Having this accreditation lets customers know that you operate your business to a good standard of cybersecurity — providing the reassurance they need to buy from you with confidence. It also helps to build a good reputation for your business as time goes on.

3. Bid for government contracts

If you want to work with organisations within the MoD and bid for government contracts, you’ll need a Cyber Essentials certificate. This is a huge opportunity to work on large-scale projects and form long-lasting relationships with public sector organisations. 

4. Become a trusted supplier

For the 12 months your certificate is valid, your company’s name appears on the NCSC website. This makes it easy for potential customers to check your cybersecurity credentials and validate your business.

5. Strengthen your supply chain

Your customers, partners, suppliers, and investors need confidence in your ability to operate safely. Having a registered certification validates your processes and means they know you operate with their best interests at heart.

6. Reduced cyber insurance premiums

Obtaining Cyber Essentials certification can potentially facilitate your cyber insurance application.  Insurers recognise the certification as a sign of good cyber hygiene.  Many insurers select to insure these controlled risks and some may offer preferential treatment in underwriting.

7. Operational resilience

Cyber Essentials builds your business’s operational resilience, making you better prepared to handle cyber incidents. This means less downtime, quicker recovery, and a stronger response to potential threats

8. Competitive advantage

Demonstrating your commitment to cybersecurity can set you apart from competitors who may not have the same level of protection. This can be a huge differentiator when attracting new customers and partners, who prioritise security and reliability. 

Start meeting your business needs

Addressing the basic needs of your business will build you a foundation for success. Getting your cybersecurity in order is a must, and working towards a Cyber Essentials certification will put you on the path to better data management. 

Want to know more about cybersecurity certifications and which one is best suited to your business? Our guide has everything you need to make a decision.

Discover the latest cybersecurity insights for MSPs

Uncover the critical findings from the CyberSmart MSP Survey 2024. Learn how managed service providers are navigating the evolving cybersecurity landscape and what it means for your business.

Introducing: The new and improved desktop app for CyberSmart Active Protect

CyberSmart Active Protect

CyberSmart is excited to announce the relaunch of our desktop app for Active Protect. Designed to safeguard users and devices from cybersecurity threats, it comes complete with cybersecurity awareness training, endpoint monitoring, device misconfiguration assessments and the ability to enforce compliance with company policies. 

How does Active Protect work?

Active Protect runs an unobtrusive agent in the background on your devices, checking configurations, training modules passed, and policies read and acknowledged. 

Once Active Protect has run its scans, passes and fails are reported back to the user and administrator(s) with tips for addressing any misconfigurations. Plus, the employee(s) responsible for cybersecurity in your organisation can view this information through several different dashboard views. 

For desktop users, the app can be downloaded via email once an administrator has sent out the enrollment link. And, for mobile, through the app store relevant to your device.

What’s changed? 

Radical redesign

The first thing you’ll notice upon opening the new and improved Active Protect is how it looks and feels. We’ve updated the design with the latest user experience (UX) principles in mind, making it easier to use than ever before. 

Renamed security controls 

We felt ‘device checks’ wasn’t clear enough so we’ve renamed them ‘security controls’ to reflect their purpose better. We’ve also renamed each check to give users a more accurate picture of their status. 

Updated security controls

All Active Protect’s security controls have been updated with new logic to help them stay up-to-the-minute with changes to manufacturers’ operating systems. This dramatically reduces the risk of false positives and makes them our most accurate security controls yet. 

Improved memory usage

Memory is an important resource for any small business. So, to free up as much as possible for our customers, we’ve rebuilt our security controls to minimise CPU usage when running a check.

Consolidated reporting

You can now see every desktop version of Active Protect in your business in one place. This makes it simpler than ever to ensure everyone in your organisation has the highest protection levels. 

Legacy devices page

Manage devices on older versions of Active Protect and give them access to the latest features and security enhancements.

Vulnerable software security control

Most excitingly of all, we’ve added a brand new security control that analyses a user's desktop for software vulnerabilities, complete with a severity rating system, so you know which fixes to prioritise first. 

Changes to security controls

As we mentioned earlier, we’ve made some changes to the names of Active Protect’s security controls. To help you avoid confusion, here’s a handy list of the changes.

CyberSmart Active Protect

How to get access

From the 24th of June 2024, all new devices will be automatically enrolled on the latest version of Active Protect. For existing devices, there are in-platform buttons and simple instructions in our Knowledge Base on how to get access to the latest version.

Cost of living CTA 3

Cyber Essentials checklist - prepare and pass

cyber essentials checklist

The Cyber Essentials scheme provides an effective framework against cyberattacks. Getting Cyber Essentials certified is a great first step to protecting your digital assets and personal data.

For those considering bidding on work such as UK Government supply chain contracts, it’s a mandatory certification. 

Like all official certifications, achieving Cyber Essentials requires preparation and investment of time, budget, and some technical awareness. Learn more on how to prepare and pass certification with our Cyber Essentials checklist.

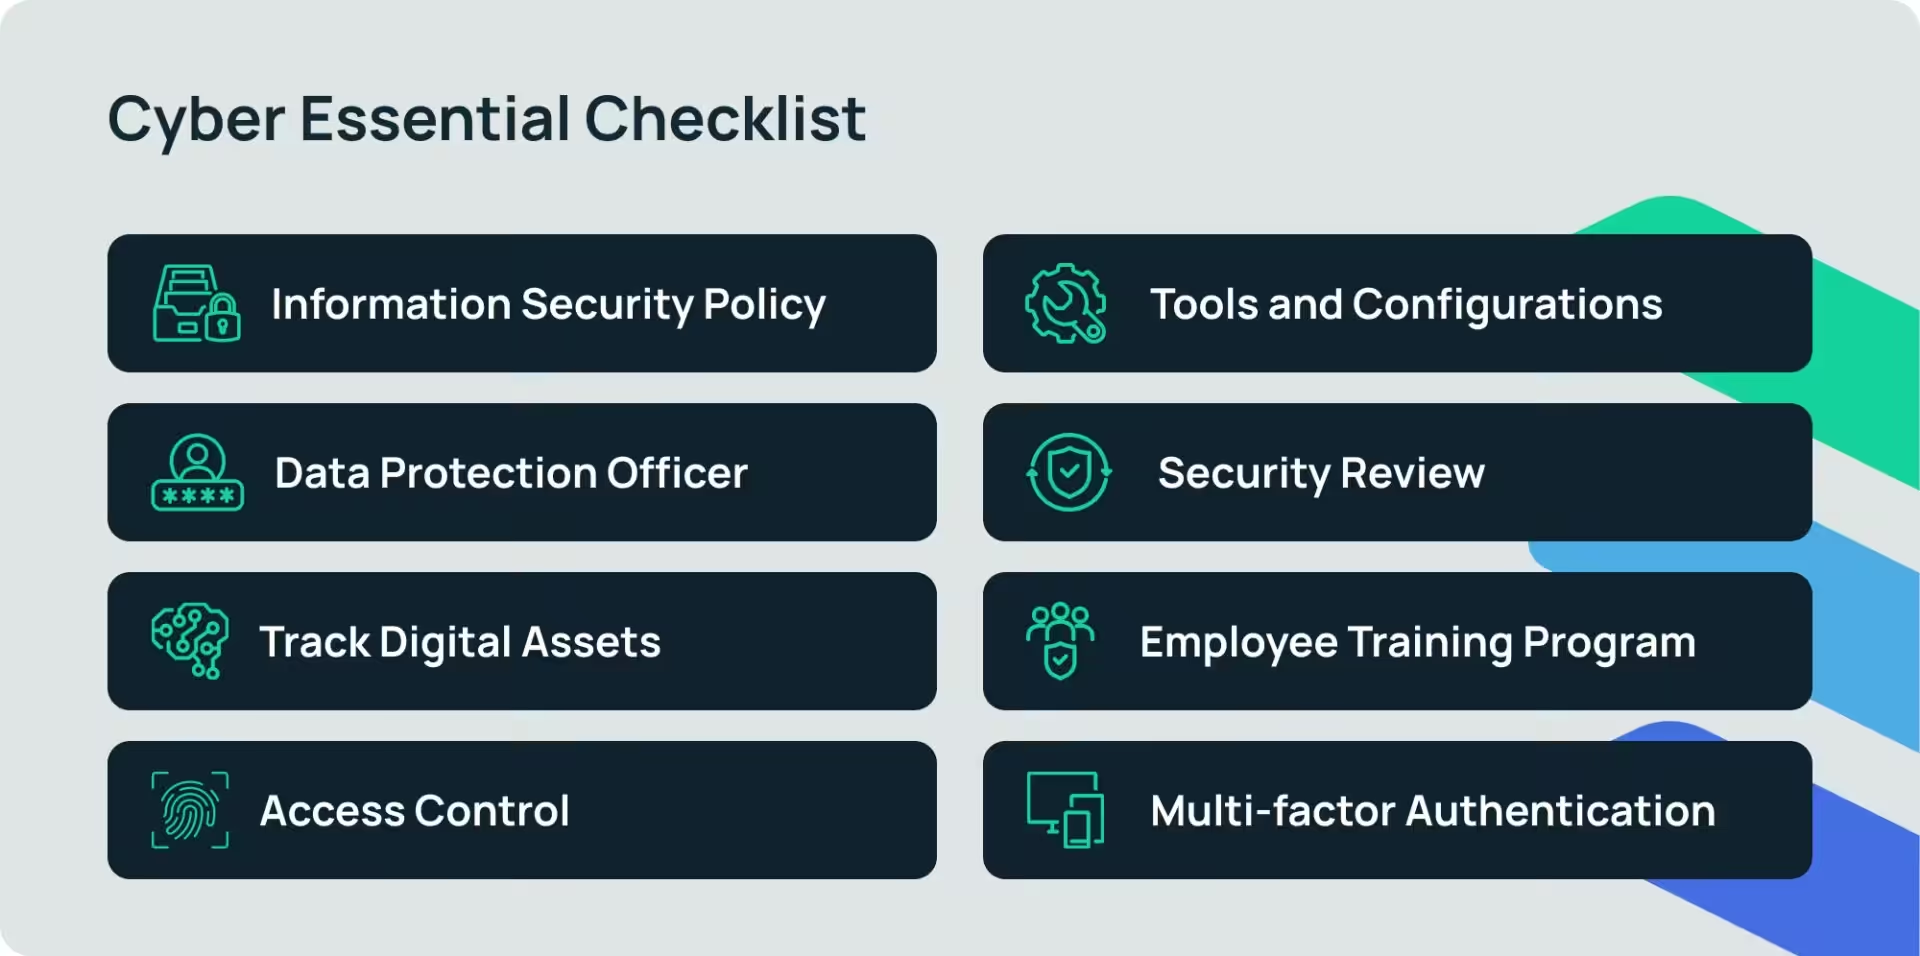
1. Create an information security policy

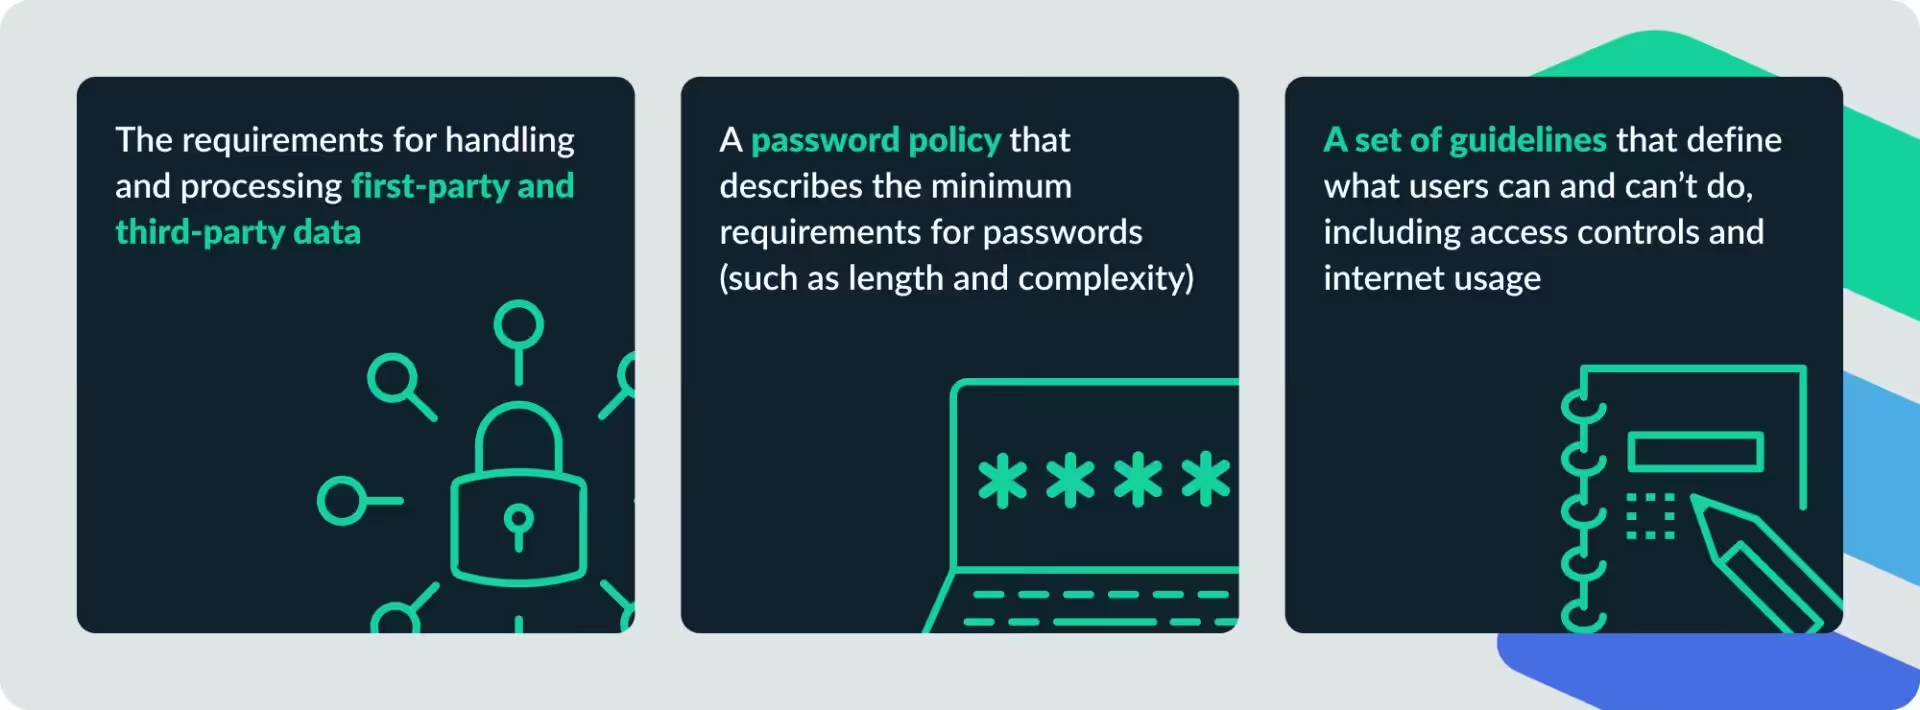
The first step is to develop an information security policy. Your policy should establish the requirements and rules for cybersecurity that will help you to achieve Cyber Essentials, including:

  • The requirements for handling and processing first-party and third-party data
  • A password policy that describes the minimum requirements for passwords (such as length and complexity)
  • A set of guidelines that define what users can and can’t do, including access controls and internet usage

Your security policy doesn’t have to be a long and complex document. Instead, it should document rules for cybersecurity in a simple, obvious way that all your employees and suppliers can understand and comply with.Consider incorporating guidelines for remote work into your Cyber Essentials checklist, including secure use of personal devices and VPN. It’s crucial to define procedures for responding to security breaches and reporting incidents in and away from the organisation.

2.     Assign a data protection officer

Although not mandatory for all organisations, appointing a single senior employee as a Data Protection Officer (DPO) can help you enforce the information security policy within your organisation.

For SMEs, assigning a DPO can be a crucial step in coordinating all security initiatives. For external parties and IT users, they're a single point of contact for queries and concerns related to security.

Cyber Essentials requires businesses to complete and submit a self-assessment questionnaire and provide relevant evidence to support answers, to achieve certification.

Having a DPO ensures that everybody understands who is responsible for completing the questionnaire and who to go to for advice and guidance. It also encourages the DPO to conduct regular audits and risk assessments – leading to security awareness and promoting training for other employees.

3. Keep track of your digital assets

To make sure that all software and devices are protected, you should keep an inventory of digital assets. Include the details of versions and updates for both software and devices.

Knowing what and where your assets are is good practice, especially with information security assets. It helps you keep software updated, which is essential, and is the best first step to protecting your systems and data.

Knowing what devices your business has is the best way to identify unauthorised devices and to take action to remove or isolate them. Establish a clear process for securely disposing of outdated or unused assets to keep everything organised and safe. 

Tracking your digital assets helps to identify vulnerabilities and to keep a close watch on devices within your network.

4. Enforce access control

Access control ensures that only authorised personnel can see sensitive information and enforcing strong access control is an essential step for achieving Cyber Essentials certification.

Make use of a Role-based Access Control (RBAC) system ensures IT users have only the privileges that they need for their job role and access to only those systems they need to be effective and operate safely.

Regularly review and update user permissions when changes occur in roles or employment status, using access control software that provides detailed logs and alerts for unauthorized access attempts. 

5. Make use of the right tools and configurations

A firewall and antivirus are essential security tools required for Cyber Essentials.

Your security system helps protect devices on a network from external threats such as those from the internet.

Your antivirus software protects your systems from viruses and other malware that leads to corruption and theft of personal or proprietary data.

You should ensure your firewalls are properly configured to disallow access to malicious content. Making use of a firewall and antivirus will help your business prevent the most common types of cyberattacks.

6.     Conduct regular security reviews

To ensure that your digital assets remain safe and protected, it is vital to document, track, and review the effectiveness of the cybersecurity measures you have taken. Put a security team in place to oversee and act on any findings, so you can use them to improve future security policies and procedures.

Knowing the strengths and weaknesses of your network can help you fine-tune cybersecurity, especially as you grow. You should conduct regular security reviews to:

7. Introduce employee training programs

Interactive training modules on how to recognise phishing scams will provide employees with up-to-date resources and guidelines on best practice. Encourage a culture of cybersecurity awareness through regular, updated training materials that detail the latest threats and optimal procedures. 

Use the assessment results to identify gaps in knowledge, tailor training to everyone, and provide more efficient feedback. 

8. Use multi-factor authentication (MFA)

Implement multi-factor authentication (MFA) that goes beyond traditional passwords. MFA provides two or more verification factors to gain access, such as a temporary code sent to a mobile device or email account. 

Look to integrate multi-factor authentication for all security-critical systems, including cloud services, email, administrative accounts and more. This is especially important when employees are working remotely, where there is a risk of external threats. 

Start your Cyber Essentials checklist

If you’re a small or medium scale business, getting started with cybersecurity can seem daunting — especially if you have no technical IT skills. However, achieving a Cyber Essentials certification is a great way to begin, and for a small investment of time and effort, it can significantly reduce risk. Follow the Cyber Essentials checklist outlined above, and you will be well-prepared to pass the certification.

CyberSmart is an automated platform to help businesses stay secure with recognised certification standards including Cyber Essentials. Businesses can gain certification as individual companies or can join the many organisations that have achieved Cyber Essentials by partnering with us today. If you have any questions, whether it is preparing for Cyber Essentials, or how to protect your company systems and data, please reach out to learn more.

Cybersecurity certifications