Our Head of Engineering talks managing a global remote-only team

Meet Rob Minford our Head of Engineering at CyberSmart. Even though we're all working from home these days, Rob's team has always been fully remote and is scattered across the globe.

In this interview with The Remoter Project, Rob talks about the benefits and challenges of working in a remote hybrid company (with some of us in an office and his distributed engineering team).

The Remoter Project is a venture that showcases the human side of remote working and explores how to successfully build and scale remote teams.

Interested in joining our growing team at CyberSmart? Check out our careers page.

Is your remote team making these security mistakes?

Summer days are here. As people begin to gather in the parks again and shops re-open, it’s beginning to feel like life is going back to normal. But for many of us, that normal won’t include going back to the office.

Consulting company Global Workplace Analytics estimates that after the pandemic, 30 percent of the entire workforce will continue to work from home regularly. Armed with Zoom and our Slack channels, we’ve succeeded in proving that a team doesn't need to be in an office together everyday to get things done.

But while a new remote world is great news for the weary commuter of 2019, it’s also great news for the cyber criminal. Over the past few months, cyber crime increased as hackers take advantage of employees who are used to relying on their offices and IT staff to protect them.

It can be hard to convince staff of the importance of digital security. After all, most people outside of IT tend to think of cyber crime as something planned and targeted- a mastermind hacker out to get critical information from the government or cause trouble for a big corporation.

What would they want with my little business? I'm too insignificant to be targeted for cyber crime. This is the wrong way to think about it. Most cyber criminals are just opportunistic. They didn't choose to rob your house because they knew you had a stash of cash under the bed (or all your passwords on your desktop). They chose it because you left the door open.

Using unsecured networks, not keeping software up to date, reusing passwords- there are a lot of ways to open the door. Luckily, many of these risks follow similar patterns and can be avoided through a few fundamental security practices. The most effective thing businesses can do right now to protect their data, their employees, and their customers is to educate their workforce on what these are and why they are important.

Here are some of the biggest (but pretty simple) mistakes your remote team might be making:

People having access to data they don’t need
According to data by the UK's Information Commissioner's Office, employee error continues to be a leading cause of data breaches. They might fall for a phishing attack or just accidentally send an email with a sensitive attachment to the wrong person.

One way to easily reduce the harm caused by data breaches, is to only give employees access to information they need to do their job. It might be easier to make a folder on Google Drive accessible to everyone in the company, but it also means you're opening a lot more doors to that data than you need to.

Unsecure networks

While people can be generally pretty savvy in terms of updating their own machines ( laptops etc) they generally forget about their routers after they set them up at home. When you first get a router, it's important to login to change your usernames and passwords (which can be easy for hackers to find online) and to turn on Wireless Network Encryption.

Employees can also use a VPN (Virtual Private Network) to change their IP address, so hackers can't see the actual location of their device. It could also allow employees to access company information from personal devices. As a business, encourage employees to follow the same protocols you had in your office in terms of accessing company data.

Out of date software and devices

It's extremely important to keep all hardware up-to-date - from laptops, routers, servers or the increasing number of IoT devices in the home to protect against things like ransomware attack. Ransomware attacks are among the fastest growing cyber threats (one report projected that in 2021, companies will fall victim to an attack every 11 seconds). Software patches are released all the time to protect against known vulnerabilities but they don't work if the system is outdated. Making sure you are using up-to-date operating systems and that software is running on the latest version is a critical part of cyber hygiene.

Not taking security seriously

Most people outside of IT have been guilty of this at some point. It's just simpler to have one password for everything! And my wife's birthday is the easy to remember! (most of the time). But these little things can have big consequences- particularly when employees are using personal devices for work. A personal phone that has access to the company Slack channel, needs to be just as a secure as a PC in the office.

The majority of breaches are made through simple human error. We weren’t paying attention and accidentally sent an email we shouldn’t have. It's critical that employees know what data in your business is sensitive and the consequences of a breach.

Lack of education

Sometimes data breaches happen because people just don't know how to see them coming. For example, as phishing scams become increasingly sophisticated, employees need to know how to spot a suspicious email and how to report it.

Recent reports show that employees aren't big fans of security. 42% of staff state that their company's security policies (like having to have an IT admin install new software) make it more difficult to do their job. This is why education is so important.

We launched a page specifically designed to offer resources for small businesses who are transitioning to a remote work environment. These include company policies and a security checklist for employees.

The reality is that in this unstable economic environment, businesses are less likely to invest in their cyber security. But cyber security doesn’t have to be expensive or confusing. This kind of basic cyber hygiene can go a long way in preventing the threats we're seeing increase on a daily basis.

The dream of working from anywhere in the world may finally be materialising for many. Let’s make sure it happens safely.

Show your customers you value their data by getting certified in Cyber Essentials, the UK government scheme that covers all the fundamentals of cyber hygiene.

Inside CyberSmart Active Protect: what's monitored and what's not

This month, we made the decision to include our CyberSmart Active Protect with all of our certification options. We did this because we know real security can’t be achieved through a certification audit once a year; it requires continuous assessment of compliance.

We also know that up to 98.5% of cyber attacks can be prevented by following the controls that our software monitors. That’s why we encourage businesses and their employees to install the app on any device that might be used for work purposes.

And that’s where things get sticky. A work app on my personal phone? That monitors me?

We get it. It all sounds a bit Big Brother. So we’re here to clear up exactly what we ‘monitor’ with our CyberSmart Active Protect and why it’s good for employees as well as businesses.

What we see

What an employer sees on devices that have the CyberSmart Active Protect installed:

  • Whether your device is complying with the five controls of Cyber Essentials
  • Which software you have installed on your computer and if it is up-to-date
  • The make, model, and year of your device
  • Your operating system (like Microsoft Windows or Apple's macOS) and which version you are running

What we don’t

An employer can’t see anything but what’s listed above but here are a few points for clarification:

  • Which websites you visit
  • Which apps you have installed on your mobile device (these are different from software. Your employer has no way to see if you downloaded CandyCrush again after you so admirably recovered from your addiction)
  • Your physical location with the device
  • When you are online or how much you are using different software on your devices

Checking your vitals

One of our engineers described CyberSmart Active Protect as an ‘ongoing health check.’ This is a good way to think about it. We’re taking your vital signs but we don’t get into any more detail than we need to. Is your firewall still up? Is a piece of software out of date that could leave a door open for attack? If it is, you’ll get a notification and clear instructions on how to fix it.

It’s good for employees too

When a device is hacked, criminals aren’t just looking for business data on customers. They will take any useful piece of information they can. With the CyberSmart Active Protect installed, employees will enjoy the benefits of protecting their personal data as well as the company’s on their personal devices.

Take the first step to protecting your business and your employees today. If you got your Cyber Essentials certification through CyberSmart, you can now access one free license to CyberSmart Active Protect via your dashboard.

Don’t take the bait: tips for avoiding a phishing attack

Phishing scams

We’ve all gotten those emails before. Congratulations! You’ve won a £100,000 voucher from Argos. Click here in the next three hours to claim your reward!  We want to believe them. They just might be real. And that is exactly the mentality cybercriminals are taking advantage of. 

These kinds of scam emails are known as phishing attacks- and they are everywhere. According to Verizon’s 2020 Data Breach Investigations Report released this week, they made up nearly a quarter (22%) of all cyber breaches this year. 

We've seen an even greater rise in these over the past three months as hackers preyed on widespread anxiety by impersonating official sources like the US Center for Disease Control, the World Health Organisation, and various government offices offering 'updates' and 'alerts' around the virus.

Phishing attacks fall into two broad categories. They are usually trying to persuade you to click on a link that will lead to a spoof site and require you to enter personal data (credit card details, personal or bank information, etc), or to download malware onto your device (either through a link or an attachment).

Many of these phishing emails can be extremely convincing. Even EasyJet fell victim this week. So how can you protect your business, your employees, and ultimately your customers against them?

Training employees how to recognise the warning signs of phishing emails is the best way to prevent these kinds of attacks and might be the best solution for smaller businesses.

While there are a few great pieces of anti-phishing software out there that use email filtering to detect and flag suspicious email addresses and malicious links or attachments, the most convincing phishing attacks often slip through the net of even sophisticated software.

Something smells fishy here: spotting the signs of a scam

Read carefully

Copywriters at big companies spend a lot of time crafting emails and there's often a noticeable lack of quality with phishing scams. A few tell-tale signs include:

  • Generic greetings - Dear user..
  • Urgent deadlines and calls to action - Click now or your home insurance will expire!!
  • Grammatical mistakes and spelling errors - Plese download the attached file to keep Your Account open. If it doesn’t seem professional, it probably isn’t.
  • News that is too good to be true - We've found a cure for the coronavirus. Click here to order your safety kit.

Check the email address

Be sure to check the email address as well as the name of the sender. Although phishing scams often use the name of someone you know or a company you work with, the email address won’t match up. If it's from @gmail.com address, for example, it's probably not a legitimate organisation.

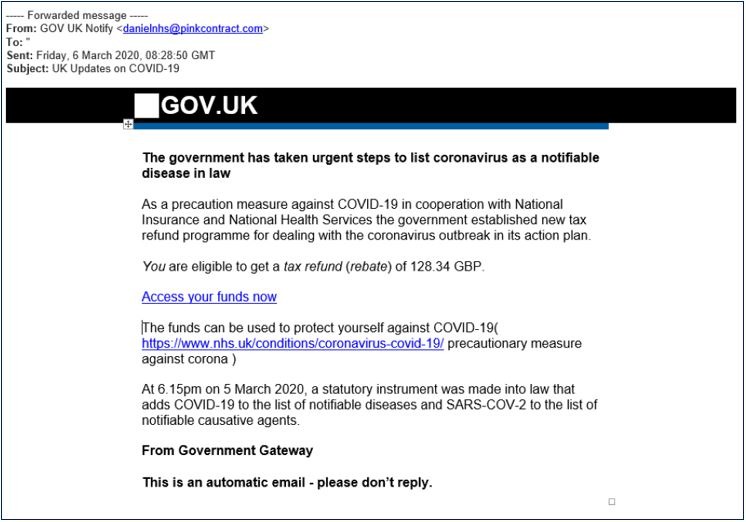
A recent phishing attempt. Note the sender's email address - @pinkcontract.com

Question their professionalism

Remember that real brands will never ask you for personal details over email or force you to their website.

Think before you act

Above all, just take a moment to pause before you interact with any email. Before you click or download anything, reflect for a second by asking: do I know this person? Have I actually ever bought anything from this brand? How does the World Health Organisation have my work email address? Why can't Karen from Accounting spell correctly?

An ounce of prevention is worth a pound of cure

As attacks become more sophisticated, it’s almost inevitable that you or someone you know will fall victim at some point. But following basic cyber hygiene can help reduce the harm of these attacks. 

A simple way to mitigate against phishing attacks that steal credentials is to enable two-factor authentication on your accounts right now. Two-factor authentication means that when you log in you need both a password and a second form of confirmation (like a text to your mobile, for example).

Having this extra layer of security means that even with your username and password, the hacker will not be able to access employee accounts.

If an employee or business realises they have been breached, they should immediately take action by changing their personal password or disconnecting their device from the network and alerting employees in the rest of the company.

People can help prevent the spread of these large-scale attacks by immediately reporting suspicious messages to Suspicious Email Reporting Service (SERS): report@phishing.gov.uk which support's the government's Active Cyber Defence programme.

Looking to improve your cybersecurity but not sure where to begin? Start by getting certified in Cyber Essentials, the UK government scheme that covers all the fundamentals of cyber hygiene.

CTA button

When cyber security saves lives: examining the healthcare industry

Three years ago today, the UK’s National Health Service descended into chaos.

In one fell swoop, a fairly unsophisticated worldwide ransomware attack called WannaCry infected computers in hospitals across the country, hijacking thousands of pieces of connected medical equipment and holding patient and hospital data for ransom.

Becker’s Hospital Review estimates that in the United States data breaches cost the healthcare industry approximately $5.6 billion every year. The WannaCry attack cost the UK healthcare system nearly £92m. But while it was the largest breach the NHS had ever experienced, it wouldn’t be the last.

In terms of basic cyber security, the healthcare industry lags woefully behind other sectors like finance and manufacturing who often build their infrastructure with data security in mind. This is especially troubling given how attractive healthcare breaches can be to hackers (personal health information is worth an average of 10 times more than financial information on the black market). Not to mention the dire risk to patient care when day-to-day functions are interrupted. 

Here are some of the ways in which the current healthcare system is more susceptible to breach than ever and why incorporating security practices needs to be prioritised:

A complex supply chain

When we speak about the healthcare industry we aren’t just talking about hospitals and computers full of medical records.

The healthcare system is possibly the most complex supply chain in our economy. It includes everything from cleaning supplies to CRM appointment reminder software, scanning machines to climate-controlled storage of drugs shipped from all corners of the globe.

It is common practice for hackers to target the supply chains of the organisations they want to access. It is very often these small suppliers- 15 or 20 employee companies- that offer an open door through weak security practices. A November 2019 study by Orpheus of NHS suppliers showed that 95% lacked advanced security protection. 88% of them had already experienced some sort of email and employee password leaks before working with the NHS.

There is much at stake. Trust in this highly regulated industry is paramount. A data breach for a small supplier could mean the end of their business.

There is much at stake. Trust in this highly regulated industry is paramount. A data breach for a small supplier could mean the end of their business.

Data gone digital

The days of paper records are all but gone in healthcare. And with good reason. Digitised patient data makes it easy to quickly communicate between internal hospital departments and outpatient clinics, and to ensure information is always accessible and up-to-date. 

However, it also makes the institutions that hold this data an increasingly attractive target. Once acquired, patient data can be held for ransom or sold on the black market.

Last year, an Israeli research group exposed more insidious potential consequences when it demonstrated how a hacker could very quickly and realistically add or remove medical conditions (such as the appearance of a tumour) on 3D medical scans in real-time. Although this would likely only be used to target specific individuals for specific reasons- they mentioned insurance fraud and political assassination- it demonstrates how severe the consequences can be for even a simple breach.

Connected and outdated devices

From hospital lifts to MRI machines and implanted pacemakers, the healthcare system is increasingly connected to the internet. Doctors and nurses rely on these machines to monitor patient health and to serve as a partner in diagnosis.

Unfortunately, every connected device offers another potential entry point for hackers and the level of security of each device varies widely. Some of them are new and modern but others, such as expensive scanners may be ten or 15 years old. They are running on outdated operating systems and no one has the time or skillset to patch them.

A drip delivering chemotherapy drugs that had been infected with crypto-mining malware might just run a little bit more slowly. But when the precise and timely delivery of a dose is paramount, this can have disastrous results.

Hacked devices can be hard to detect and are likely running on many devices now unbeknownst to staff. A drip delivering chemotherapy drugs that had been infected with crypto-mining malware might just run a little bit more slowly. But when the precise and timely delivery of a dose is paramount, this can have disastrous results.

Over-stretched staff

A key part of any industry's cyber health is knowledge and good practice among its organisations and employees. JAMA Internal Medicine reports that the majority of breaches related to data privacy in healthcare were the result of employee error and unauthorised disclosure.

In the already overstretched world of hospitals, it is no wonder that cyber security is the last thing on the minds of most workers. It makes sense. Our healthcare providers are trained to take care of patients, not to be IT experts. 

But the NHS is the largest employer in the UK and we must come to accept that cyber security awareness is a critical part of every job- and may do its own work to save lives.

Many of these breaches could be prevented through the basic cyber hygiene covered in the government-backed Cyber Essentials scheme. This includes maintaining strong password protection, up-to-date software and firewalls, and anti-malware. If you are a healthcare provider or supplier, consider getting certified in Cyber Essentials.

Mythbusting: on security and why we're still using Zoom

Amidst its general path of destruction, coronavirus has blessed only a select few industries in lockdown (we’re looking at you baking supply companies) and fewer still have experienced a rise as meteoric as Zoom.

In the month of March, the video conferencing software jumped from 10 million to 200 million daily users. Everyone from politicians to pick-up football leagues is hosting Zoom chats making a moderately well-known company into a household name and an integrated part of our lives. 

But this rapid expansion has brought media scrutiny with it. The past few weeks the news has been littered with stories of Zoom security breaches and questions around its reliability and safety. We’re unpacking a few of the myths behind these reports and explaining why we, as a cyber security company, are still on the Zoom bandwagon.

Some technical stuff

First, almost all conferencing software, including Zoom, uses HTTPS/TLS- an encryption protocol that protects communications on the internet. It’s the same protocol your bank uses when you login online or via an app. The information is encrypted from you to the servers of the provider, and then re-encrypted from the provider to you via a similar secure link. 

Should the government be using Zoom to convey top secret information? Probably not. Is it fine for communicating openly with your team? Absolutely.

Basically, services like Zoom that use this encryption are inherently quite secure. Should the government be using Zoom to convey top secret information? Probably not. Is it fine for communicating openly with your team? Absolutely.

Security versus privacy

These two terms are very often and quite easily confused. Security protects strangers from unauthorised access to your data. Privacy has to do with the safeguarding of your identity. You can have security without privacy but not privacy without security.

The first wave of Zoom ‘security’ concerns was really about privacy and their collection of personal data of users. They have since updated their privacy policy to prevent anyone including Zoom employees from directly accessing data that users share during meetings including their names, and video/audio/chat recordings. “Importantly,” a Zoom spokesperson adds, “Zoom does not mine user data or sell user data of any kind to anyone.” While they don’t sell or share data with third parties, they do use Google Ads and Google Analytics.

If you really care about security

If you really care about security there are a few things you should always keep in mind when using videoconferencing. 

First, use a unique password. According to a recent report, 71% of accounts are protected by passwords used on multiple websites. One of Zoom’s highest profile ‘breaches’ was actually just a breach on another platform for which users had been using the same password thus opening them up to further attack.

71% of accounts are protected by passwords used on multiple websites.

Second, update your operating system and keep your video conferencing software up-to-date. This will mean any patches or protection by the company will be in place on your device. Alternatively, you can use a browser rather than a separate app which are less vulnerable to attack.

If you want to use Zoom there are some settings you can activate for enhanced protection and privacy. These include the option to watermark all content, and restricting meetings to people with a certain email domain (xxx@cybersmart.co.uk). ‘Zoom bombing’ (allowing random people to enter your calls) is prevented by requiring your attendees to use a password to join a meeting.

We don’t recommend recording meetings unless you’re happy with them eventually making the papers but if you must, you can choose to store them locally rather than on the cloud.

If you really, really care about security

If you work in an industry with incredibly sensitive data that requires end-to-end encryption, Zoom may not be the service for you. They don’t truly offer this but there are a few others that do. You might consider using Wire or Webex (this is what we use to conduct remote security audits for Cyber Essentials Plus certification).

Video conferencing is a must in the remote workplace but there are a few factors to consider when deciding which service to use. The National Cyber Security Centre offers some great guidance on this. 

As always, remember that the majority of cyber attacks can be prevented through basic cyber hygiene and the guidelines covered in the government’s Cyber Essentials scheme.

The Cyber Essentials questionnaire: are you prepared?

In 2015, a research team at Lancaster University concluded that 99% of cyber risks could be avoided through following a set of surprisingly simple security measures. These measures, or controls, make up the basis of the government's standard for security certification, Cyber Essentials, which is what we help businesses achieve here at CyberSmart.

However, there's a lot you can do on your own to prepare yourself for the Cyber Essentials assessment or just to improve your general cyber hygiene around its guidelines. We're going to walk you through some of the processes you will need to have in place when you complete the self-assessment for Cyber Essentials before it is reviewed by an assessor.

Keep in mind that the Cyber Essentials questionnaire is asking you to evaluate every device in your company (laptops, personal computers used for work, phones, the works) and whether it complies with the rules. If it is being used for work, it should be included.

Choose the most secure settings for your devices and software

☐ Know what 'configuration' means

☐ Find the settings of your device and try to turn off a function that you don’t need

☐ Find the settings of a piece of software you regularly use and try to turn off a function that you don’t need

☐ Read the NCSC guidance on passwords

☐ Make sure you're still happy with your passwords

☐ Read up about two-factor authentication

Control who has access to your data and services

☐ Read up on accounts and permissions

☐ Understand the concept of 'least privilege'

☐ Know who has administrative privileges to your data and on which machines

☐ Know what counts as an administrative task

☐ Set up a minimal user account on one of your devices

Protect yourself from viruses and other malware

☐ Know what malware is and how it can get onto your devices

☐ Identify three ways to protect against malware

☐ Read up about anti-virus applications

☐ Install an antivirus application on one of your devices and test for viruses

☐ Research secure places to buy apps, such as Google Play and Apple App Store

☐ Understand what a 'sandbox' is

Keep your devices and software up to date

☐ Know what 'patching' is

☐ Verify that the operating systems on all of your devices are set to ‘Automatic Update’

☐ Try to set a piece of software that you regularly use to 'Automatic update'

☐ List all the software you have which is no longer supported

If you can follow this guidance now, you can pass certification quickly and with flying colours. If you struggle with any of them, CyberSmart has helped guide hundreds of SMEs of all sizes and experience through the same process, so feel free to get in touch. We offer a quick and simple step by step process so you can get Cyber Essentials certified today.

Essential cyber security terms: decoded

If you’re like most people, no one ever taught you how to use a computer. Not properly. They aren’t like cars. Rightly so, we force excitable teenagers through a host of training before we let them behind the wheel. They spend months in lessons learning the basics of how to use it, maintain it, and control it before they can be trusted to take it out on the road.

No, at some point most of us just sat down at a screen, ignored the instruction manual, and relied on some well-designed user interfaces to figure it out ourselves.

This is a dangerous game. Your computer is not an isolated piece of hardware. It is linked to that greatest of connectors and stores of information- the internet.
These computers have access to your banking details, your shopping preferences, your personal data and correspondence and most of the time we’re operating them with very little training or testing.

As the world of cyber security develops, it’s important that businesses and customers have at least a rudimentary knowledge of basic terms which they may come across as they live and work via their computers. You don’t have to be an IT technician to protect your device, just as you don’t have to be a mechanic to check your oil.

We’ve compiled a short list of some of the most common terms in the cyber security world and what they mean for you. So hopefully, next time you see a prompt for two-factor authentication, you’ll take them up on it:

Antivirus
Antivirus software is used to prevent or remove unwanted malware from infecting a computer. Using this software provides a computer user with a safer working environment and a more efficiently operating computer. There are lots of companies offering anti-virus software including Avira, Symantec and McAfee.

Breach
An incident in which data, computer systems or networks are accessed or affected in a non-authorised way. Also known as a ‘hack.’

Bring your own device (BYOD)
An organisation's policy that allows employees to use their own personal devices for work purposes.

Cloud
Where shared compute and storage resources are accessed as a service (usually online), instead of hosted locally on physical services. Resources can include infrastructure, platform or software services.

Digital footprint
A 'footprint' of digital information that a user's online activity leaves behind.

End user device (EUD) or end point
Collective term to describe modern smartphones, laptops and tablets that connect to an organisation's network.

Firewall
A network security system that monitors and controls incoming and outgoing network traffic. Establishes a barrier between a trusted internal network and untrusted external network, such as the Internet.

Malware
Malicious software - a term that includes viruses, trojans, worms or any code or content that could have an adverse impact on organisations or individuals.

Patching
Applying updates to firmware or software to improve security and/or enhance functionality.

Pentest
Short for penetration test. An authorised test of a computer network or system designed to look for security weaknesses so that they can be fixed.

Two-factor authentication (2FA)
The use of two different components to verify a user's claimed identity such as a password and text to your mobile device. Also known as multi-factor authentication.

CyberSmart's remote team: tips for staying sane

We’ve always had a strong work-from-home culture here at CyberSmart. We’ve got team members based all over the globe and encourage staff in London to work from wherever they work best. We are, in many respects, ‘remote by design.’

But this week, for the first time, we took the step along with businesses across the world to send our staff home and go fully remote in light of the spread of the coronavirus. 

As we make our way through this first week, hunkered down in our kitchens and living rooms, we’ve implemented a few new office rituals to help keep up team morale. Here are a few of the practices we’ve been using to stay sane:

One of the perks of home working - new coworkers

Stand-up and stand-down meetings

Working from home can be disorienting. You’ve got dogs begging for walks and dishes demanding to be washed while a never ending stream of work alerts is pinging from your computer screen. The line between life and work can be very difficult to see. 

To combat this ambiguity, we have implemented two standing meetings at the start and end of every day. These offer a clear marker for the beginning and end of the workday and provide an opportunity to share priorities and struggles, and to make sure we all know where we’re heading together.

Using a variety of communication channels

We haven’t changed our communication channels since transitioning to a remote setup, but we’ve quickly realised how valuable they are. Obviously, instant messaging is important in the absence of face-to-face contact, but having different messaging channels for distinct purposes is also key. 

We use Slack for real-time work messages and WhatsApp for generally aligning the team. Project management software like Monday.com or Asana provide a space for organising and scheduling tasks.

Obviously, instant messaging is important in the absence of face-to-face contact, but having different messaging channels for distinct purposes is also key.

Shared lunches

Did you know the word ‘companion’ comes from the Latin roots of ‘com-’ meaning ‘together’, and ‘panis’ meaning ‘bread’? Sharing a meal- breaking bread together- is an age-old bonding experience for us humans and our regular office team lunches were something we knew we would miss when we went our separate ways. We use Google Meet or Slack so we can dial in once a week to see each other’s faces as we devour our respective fridge leftovers.

Tavern

Every Thursday afternoon we do something called Smart Culture and Smart Work in the office. We grab a beer from the fridge or make a cuppa and talk about our company culture, our values, and the way we work. It’s a place where we as employees can help shape the development of the business.

Since we have gone remote this time has become precious. It may be the only opportunity we have in a week to reflect together on the way that we work (something that’s changing shape everyday). We have strong core values but are we living them? Who did a fantastic job this week? What’s blocking our communication between teams? What can we change to support one another better? 

Social (distance) bonding

As with team lunches, our monthly team socials have also been forced into the virtual world. Maintaining a sense of camaraderie while apart is critical right now, so we are experimenting with ways to continue to bond across the void. Online games and virtual farming are on the cards, but we’ll have to see what the next few weeks bring. 

Has your team gone remote to combat the spread of coronavirus? What are you doing to keep up spirits and ensure business continuity? As an information security company, we urge you to be aware of the vulnerability to security breaches that can come with remote working. To help address this issue, we have set up a special page for small businesses focused on resiliency during COVID-19. There you can find more information on best practices and free, downloadable checklists and policy packs for your own use.

A note from our CEO, Jamie Akhtar, on Covid-19 and business continuity

COVID-19

As the Covid-19 virus outbreak continues to escalate across the planet, I would like to update you on how the situation is being addressed at CyberSmart. 

First and foremost, our thoughts are with all who have been affected by coronavirus, especially the ones who have contracted the virus and to their families that support them. Our team wishes you a speedy recovery.

Our team, customers and partners

The safety of our employees, their families, and our partners and our clients, is our greatest priority. That is why we have transitioned the business to fully remote operations, effective as of Monday 16th March. 

Remote working is a practice that has been tried, tested and encouraged since the beginning of our business - we are “remote by design”. With team members across the globe, the ability to work remotely has always been an integral part of our business continuity strategy, and we are grateful for that now. This experience allows us to continue delivering our services to the highest standard, and uninterrupted, even in unprecedented times like these. 

We will be releasing these very practices we follow, alongside tips from our team, on our new dedicated small business resilience page .

We hope this information helps our customers, partners and any other members of the business community to take on remote working safely and productively.

Business as usual

CyberSmart’s daily operations are carrying on unaffected and we foresee no impact on our operations. With information security at the core of what we do, our team is particularly well-prepared to maintain business as usual, and continue to serve our customers with the highest quality of service.

Because of our remote capabilities, we are now delivering all certification fully remotely. This includes Cyber Essentials Plus which is normally conducted by an in-person auditor. However, our team of assessors is able to use the CyberSmart app to remotely test all devices who have it installed and help you achieve certification. Remote audits can be conducted regardless of if your team is in the office or working at home. We support both company provided and users own devices (BYOD) so all situations are catered for. As always, we commit to rapid turnarounds - we will get you certified in as little as 24 hours for Cyber Essentials and 7 days for Cyber Essentials Plus. 

Be aware of your security

I’d like to urge our customers and the public about the importance of cybersecurity to businesses right now as we are seeing an increase in opportunistic people using these ambiguous times to make gains for themselves through phishing and cyber breaches. 

We urge you to take a look at our content for all the tips to make your business safe and, should you have questions, please contact our team. We are here to use our in-house expertise to aid and advise, free of charge.

We urge you to take a look at our content for all the tips to make your business safe and, should you have questions, please contact our team. We are here to use our in-house expertise to aid and advise, free of charge.

CyberSmart is here to help

These are unprecedented, challenging times and I believe we will only make it through by bringing the business community together and supporting each other. As we become more socially distant, it is more important than ever that we stay connected. 

Please feel free to reach out to me and our team on hello@cybersmart.co.uk if there’s anything you think we can support with.

Stay positive, stay healthy and remember - together we are stronger.

Jamie Akhtar

CTA button