UK Government Cyber Action Plan: What MSPs Need to Know Now

43% of UK businesses experienced a cyber breach last year. Only 14% assess cyber risk in their immediate suppliers.

That gap is about to close, fast.

The UK government recently published its Cyber Action Plan, backed by £210 million and a new central authority. The plan officially focuses on central departments and arm's-length bodies (ALBs) meeting baseline standards by 2029. But if you're an MSP or IT service provider serving public sector clients, the official timelines matter less than understanding the direction of travel.

Because government plans don't stay contained. What starts as a departmental delivery target becomes a procurement requirement. Then a supply chain expectation. Then a client question you're expected to answer.

Are you going to be ready when this plan affects your clients?

Why MSPs Should Act Now

The government's Cyber Action Plan creates three immediate pressures that will cascade to MSPs faster than the official 2029 timeline suggests:

  1. Personal accountability creates budget urgency

Accounting Officers (permanent secretaries, CEOs of government bodies) are now personally responsible for cyber risk across their departments, ALBs, and supply chains. Not departmentally responsible. Personally. When senior officials have personal liability, budgets move faster than policy timelines.

  1. The enforcement gap is closing

The Cyber Security and Resilience Bill, introduced in November 2025 and passed its second reading in January 2026, will bring medium and large MSPs into direct regulatory oversight for the first time. The Bill is now in committee stage and expected to become law later this year, introducing several critical requirements:

  • The 24/72 Rule: Notify the regulator within 24 hours of discovering a significant incident, provide full report within 72 hours
  • Turnover-Based Fines: Up to £17 million or 4% of global turnover for serious breaches (GDPR levels)
  • Proactive Supervision: The Information Commission (IC) (formerly the Information Commissioner’s Office, or ICO), which will take on new network and information systems security responsibilities under the Bill, can inspect your security posture before incidents occur
  • Registration Requirements: RMSPs will have three months to register with the ICO once relevant provisions commence
  1. The urgency mismatch creates competitive advantage

Here's the tension: The NCSC's own messaging in its Annual Review 2025 is "it's time to act," reinforced by thousands of incidents handled last year and a rising threat picture. But the Action Plan's milestones feel cautious: 50% supplier assurance coverage by 2029, two-thirds of assessed systems meeting 75% of CAF outcomes.

The NAO called out similar issues in its January 2025 report on government cyber resilience. This plan responds to many of those critiques, but the pace still lags behind the threat environment the government itself describes.

For MSPs, that gap creates both opportunity and planning challenge. Clients who wait for mandates will be scrambling. Clients who move now can be defensible, not just compliant on paper. But move too early and you're investing ahead of demand; wait too long and you're scrambling to catch up when clients start asking questions.

The skills dynamic makes this urgent:
Government faces a massive skills gap: one in three cyber roles are unfilled, and 70% of specialist roles rely on contractors because government can't match private sector salaries. The plan creates a Government Cyber Profession to address this, but in the meantime, departments will need partners who can deliver.

What the Government Is Actually Doing

The government is establishing the Government Cyber Unit, a centralised function within DSIT that will set standards, provide services, and hold departments accountable. This represents a fundamental shift from fragmented, department-by-department approaches to active central coordination.

The core commitments:

  • The Cyber Assessment Framework (CAF) becomes the organising model for assurance, operationalised through GovAssure
  • Cyber Essentials positioned explicitly as a baseline control
  • Supply chain assurance becomes mandatory, with 50% of ALBs required to implement "some type" of supplier assurance by April 2029
  • Accounting Officers now personally accountable for cyber risk in their departments, ALBs, and supply chains
  • Evidence and reporting move from policy theatre to practical delivery

The plan also acknowledges something important: legacy systems are hard to defend (28% of government systems are legacy tech), funding is constrained, and cyber incidents are routine, not exceptional.

The Three-Phase Government Rollout

Understanding the government's implementation timeline helps with planning:

Phase 1: Building (by April 2027)

  • Government Cyber Unit established with core functions
  • Clear standards and targets set for departments
  • Government Cyber Profession launched
  • Incident Response Plan published

Phase 2: Scaling (by April 2029)

  • Departments deliver costed cyber improvement plans
  • Central services pipeline established
  • Departments fully operating within new governance structures
  • 50% of ALBs implement supply chain assurance

Phase 3: Improving (post-2029)

  • Continuous improvement based on data insights
  • Strategic supplier management at scale
  • Profession drives transformation

The demand you'll see won't wait for Phase 2. Procurement teams move faster than policy milestones, and Accounting Officers with personal accountability will act sooner rather than later.

What to Expect: The Cascade Effect

Based on the plan's structure and typical government procurement patterns, here's what to expect:

Cyber Essentials becomes non-negotiable
Not because clients suddenly care about technical controls, but because buyers will use it as a fast, visible way to raise the floor. If you're bidding on work involving public sector clients, regulated industries, or supply chains touching either, CE will move from nice-to-have to table stakes.

CAF becomes the reference model
Even for organisations that never formally adopt CAF, its language and structure will shape how assurance is described, measured, and bought. GovAssure is how this gets operationalised: departments assess critical systems against CAF outcomes and report centrally. If your outputs don't map cleanly to CAF outcomes, you'll spend time explaining why instead of demonstrating value.

Assurance pressure cascades early
Based on how government procurement typically works, requirements cascade like this: government sets requirements for departments, departments push requirements onto their ALBs, ALBs push requirements onto suppliers, and suppliers turn to their MSPs for support. Given the April 2027 and 2029 milestones in the Action Plan, most organisations are likely in the early stages of this process - understanding requirements and planning responses rather than actively implementing yet. But lead departments are now explicitly accountable for the cyber resilience of their ALBs and sectors, which means the timelines say 2029 but procurement processes will move faster.

Evidence replaces effort
The Action Plan emphasises the need to demonstrate compliance through evidence rather than assertions. Clients must show progress to auditors, insurers, and procurement teams. If your service model doesn't produce portable, reusable evidence, you'll be asked to redo work you've already done.

Centralised support creates new dynamics
The Government Cyber Unit will offer services and support to departments at scale. This includes technical advisory, detection services, incident response retainers, and a "partnering function" to help organisations access what they need. For MSPs, this could mean competition from centralised offerings, or opportunities to deliver services through government frameworks.

The Cyber Security and Resilience Bill: Timeline and Preparation

The Bill must pass through both Houses of Parliament before receiving Royal Assent. Once it becomes law, different provisions will be brought into force in phases through secondary legislation (commencement regulations).

This phased approach allows time for:

  • Consultation on specific technical requirements and thresholds
  • Development of guidance and support materials
  • MSPs and regulators to prepare for implementation

For MSPs, this represents a fundamental shift: cybersecurity will move from being primarily a service you sell to also being a regulatory requirement you must live by. The time to prepare is now, before the requirements take effect.

What to do now:

  • Review your current incident response and reporting capabilities
  • Ensure you have appropriate security measures and documentation in place
  • Budget for registration fees and compliance costs

What This Means in Practice

If you're serving public sector clients, regulated industries, or supply chains connected to either, three things shift:

Cyber Essentials becomes the entry point
Fast, standardised, and increasingly expected. Treat it as the gateway to deeper work, not the finish line.

Ongoing assurance becomes the business model
One-off certifications don't match the demand environment. Clients need continuous visibility, not annual audits. Build services that assume compliance is a state, not an event.

Portability and automation win
Manual processes and bespoke outputs don't scale. The MSPs who thrive will be the ones who can turn security work into usable evidence quickly and consistently.

How Leading MSPs Are Responding

Your clients won't wait until 2029 to ask questions about supply chain assurance, Cyber Essentials status, and ongoing compliance evidence. They're asking now.

Over 1,000 MSPs use CyberSmart to answer at scale:

Cyber Essentials certification in as little as 24 hours with unlimited expert support

Continuous compliance monitoring that tracks security posture in real-time

CAF-aligned evidence clients can reuse across tenders, audits, and insurance reviews

Multi-tenant operations with flexible commercial models built for MSP delivery

Security work becomes evidence. Evidence answers questions. Questions answered quickly become revenue.

The Bottom Line

The 2029 milestones are political. The demand is arriving now.

Clients are already facing supply chain assurance requirements in procurement, audits, and renewals. The MSPs who can respond immediately with portable evidence will win that work.

Book a demo to see how leading MSPs are turning compliance demands into scalable revenue streams with CyberSmart.

CSMv4 Is Live: What Defence Suppliers Need to Know About DCC Requirements

As of December 3rd, 2025, the Cyber Security Model version 4 is live. If you're in the defence supply chain, the Defence Cyber Certification (DCC) is the assurance framework the MOD expects you to use.

The MOD's letter to industry makes clear that Defence Cyber Certification is the assurance framework the MOD expects defence suppliers to use. Begin your certification journey, or risk being locked out of MOD opportunities.

What Actually Changed on December 3rd

The new cyber security standards launched via Industry Security Notice 2025/07. These standards were developed in partnership between the MOD and defence suppliers through the Defence Cyber Protection Partnership.

The Defence Cyber Certification scheme was announced in May 2025, with Level 0 going live in July and Levels 1-3 following in August. December 3rd marks the official launch of CSMv4, providing defence suppliers with a structured assurance framework for demonstrating cyber security compliance.

Why This Matters Now

The Strategic Defence Review stated bluntly that UK Defence continues to carry intolerable levels of cyber risk. The Defence Industrial Strategy sets out the ambition to develop a resilient UK industrial base. Recent attacks on Marks & Spencer, the Co-op, and Jaguar Land Rover demonstrate the threat is real and immediate.

The UK Defence supply chain is a priority target for adversaries. Your subcontractors, suppliers, and partners are all potential entry points. The MOD is closing those gaps.

Understanding the Four Certification Levels

The DCC operates across four levels, each corresponding to the cyber risk profile of your contracted work:

Level 0 (Very Low Risk) – The entry point. Beyond Cyber Essentials, you'll need two additional basic controls. This is the very minimum defence contractors will need. Suitable for suppliers providing low-risk goods like stationery or facilities management with minimal MOD system interaction.

Level 1 (Low to Moderate Risk) – Many defence suppliers will land here. Requires 101 controls covering governance, risk management, protective controls, incident response, and staff training. Cyber Essentials remains the technical baseline. Typical for IT support services, standard software solutions, training, consultancy, or logistics where you have some access to MOD systems or official data.

Level 2 (High Risk) – Demands 139 controls with sophisticated governance, continuous monitoring, and robust technical assurance. Cyber Essentials Plus becomes mandatory. Aimed at suppliers regularly handling sensitive MOD data, providing managed IT services for defence operations, or developing bespoke software integrating with MOD infrastructure.

Level 3 (Substantial Risk) – The highest level, requiring 144 controls and expert cyber security capabilities. Reserved for mission-critical work: command and control systems, cloud infrastructure for classified operations, weapons systems components, or advanced defence technology where compromise could have severe operational impact.

Start with Level 0, Plan for Higher

The MOD encourages defence suppliers to seek certification, beginning with Level 0. Individual contracts may specify higher levels as appropriate to the work being undertaken.

A single DCC certificate can be used across multiple MOD contracts that specify DCC, provided the contracts require a level at or below your certification level. If you achieve Level 1, you can use that certificate for Level 0 or Level 1 contracts, eliminating repeated contract-by-contract security assessments.

Certification lasts three years, subject to annual attestations and maintaining valid Cyber Essentials certification.

Common Pitfalls to Avoid

Letting Cyber Essentials lapse – If your Cyber Essentials certification expires during the DCC assessment process, you'll automatically fail. Even if everything else is perfect.

Scoping too narrowly – You can't exclude parts of your organisation that don't directly handle MOD data. The scheme demands organisation-wide compliance.

Assuming certification means you're set for three years – You must complete annual attestations confirming ongoing compliance and renew Cyber Essentials annually. At the three-year mark, full recertification is required.

Treating it as a checkbox exercise – Assessors will interview staff, request demonstrations, and verify operational evidence. Policy documents without proof of implementation won't suffice.

What You Actually Need to Do

This is where suppliers typically hit friction. Many organisations already follow good security practices but lack documentation. DCC assessments are evidence-driven. You need policies, logs, training records, and proof of implementation for each control.

Here's the systematic approach:

  1. Confirm your required level – Check your MOD contract to determine whether you need Level 0, 1, 2, or 3. If you're preparing to bid without a current contract, consider which level aligns with your anticipated work.
  2. Get Cyber Essentials certified – This is the baseline for all DCC levels. It covers firewalls, secure configuration, user access control, malware protection, and security update management. Levels 2 and 3 require Cyber Essentials Plus.
  3. Define your scope – DCC takes a whole-organisation approach. You can't certify only the team handling MOD work directly. Every business critical system and department must be in scope. Document this clearly in your Statement of Scope.
  4. Conduct a gap analysis – Compare your current security measures against the required controls for your level. Level 1 alone requires 101 additional controls beyond Cyber Essentials. Create a tracker listing each control, its status, supporting evidence, and outstanding actions. CyberSmart provides a gap analysis framework as part of our Defence Readiness Package to streamline this process.
  5. Address the gaps – Develop or update security policies, implement technical measures like logging and vulnerability scanning, establish new processes for risk assessments and supplier vetting, and assign clear roles for administering security measures.
  6. Collect evidence – Organise written policies, training records, system configuration screenshots, patch management reports, access control lists, incident logs, backup logs, risk registers, and supplier security questionnaires. Cross-reference everything against specific controls.
  7. Build your risk register – Document your information assets, threats, vulnerabilities, existing controls, and risk treatment decisions. DCC requires systematic risk management with periodic reviews.
  8. Run an internal review – Before formal assessment, have someone outside the direct process review your scope definition, compliance documentation, staff awareness, and evidence quality. Identify weak spots while you can still address them.
  9. Book your assessment –Engage an IASME-accredited DCC certification body like CyberSmart. We'll review your submission, conduct interviews or demonstrations to verify controls, and issue your certificate upon successful assessment.

What the MOD Expects Beyond Certification

The December letter also highlights two foundational approaches the MOD wants to see embedded across supplier organisations:

Active Cyber Defence – The NCSC's framework for protective DNS, mail check, web check, and early warning systems that actively defend against cyber threats rather than simply reacting to them.

Secure by Design – Building security into products and services from the ground up rather than bolting it on later. This approach reduces vulnerabilities and creates more resilient systems.

These approaches represent the MOD's expectation that cyber security becomes fundamental to how defence suppliers operate, embedded in everything from product development to daily operations.

Why Early Adoption Matters

Many prime contractors are already requesting certification from their subcontractors ahead of any formal mandate. This creates adoption pressure across the entire supply chain.

Some prime contractors are requesting certification from their subcontractors. Individual contracts may specify DCC as a requirement, making it valuable to understand the scheme and your readiness to pursue certification if needed.
Certification takes time. Understanding the requirements now means you can respond quickly if a contract opportunity specifies DCC. Prime contractors are asking subcontractors about their certification status during procurement discussions.es.

Practically, early adoption also positions you to respond quickly when contract opportunities begin factoring DCC into their evaluation criteria. Prime contractors are already asking subcontractors about their certification status during procurement discussions, signalling that the commercial landscape is shifting ahead of any formal mandate.

According to Thales' 2024 Data Threat Report, 93% of organisations in the critical national infrastructure sector observed an increase in cyber-attacks in 2024. The threat environment continues to worsen. Getting ahead of certification requirements means building genuine resilience, not just meeting compliance obligations.

Cascade This to Your Subcontractors

The MOD letter explicitly asks that you cascade this information to all defence subcontractors within your supply chain. If you work with other suppliers on MOD contracts, they need to know these requirements apply to them too.

Your certification doesn't insulate you if your subcontractors present security weaknesses. The defence supply chain is only as strong as its weakest link.

Getting Support

If you don't have a dedicated in-house cybersecurity team, preparing for DCC can feel overwhelming. Working with an experienced certification partner simplifies the process significantly.

Look for partners offering guidance at every stage, scoping support, policy and documentation advice, technical implementation assistance, and training programmes to embed security awareness across your teams.

The right partner translates technical jargon into actionable steps, provides templates and examples for policies, recommends appropriate tools and configurations, and helps you understand what good evidence looks like for each control. Certification bodies assess your compliance but cannot implement solutions. The scheme requires this separation to maintain assessment independence.

CyberSmart's Defence Readiness Package

CyberSmart is the UK's most trusted certification body, delivering more certifications than any other provider. Our Defence Readiness Package combines DCC and Cyber Essentials certification with year-round protection in a single purchase, eliminating the complexity of coordinating multiple certification bodies.

What sets us apart:

Rapid turnaround – Our experienced assessors move you through the certification process efficiently, understanding exactly what's required at each stage.

Pre-assessment preparation – We review your current cybersecurity posture and identify vulnerabilities or gaps before formal assessment, saving you time and avoiding failed attempts.

Expert Support – Utilise our team of cybersecurity experts for technical queries, guidance on preparing evidence for the Applicant Guide, and renewal advice throughout your certification journey.

Continuous protection and monitoring – We go beyond assessment day with continuous monitoring, actionable alerts, and regular compliance reporting to help maintain your cybersecurity posture year-round. This includes CyberSmart Active Protect for 24/7 protection and comprehensive asset management.

Integrated tools and training – Smart Policies provides trackable DCC-aligned governance policy creation and distribution, while CyberSmart Learn Lite delivers simple, easy-to-implement security awareness training that embeds best practices across your teams.

The Bottom Line

DCC provides defence suppliers with a clear framework for demonstrating cyber security competence. Some contracts already specify DCC as a requirement. The MOD encourages suppliers to understand the scheme and consider certification where appropriate to their defence work. Their message to industry is to: "start seeking certification now…your proactive engagement and leadership are critical in continuing to safeguard the UK's defence and national security."

Don't wait for the mandate. Start now.

CyberSmart's Defence Readiness Package combines DCC and Cyber Essentials certification with year-round protection, continuous monitoring, and unlimited expert support. We help defence suppliers navigate the certification process from initial gap analysis through to successful assessment and ongoing compliance.

Download our DCC Playbook for a deeper look, and book a call with our team to get started on your DCC journey!

6 key takeaways from the NCSC Annual Report 2025

The leaves are turning, there’s a chill in the air, and autumn is here in the UK. For the cybersecurity world, this means one thing: the National Cybersecurity Centre’s annual review is about to drop. As in previous years, we’ve gone away, reviewed the report and stripped out the key points to save you the time. So, without further ado, here are our key takeaways from the NCSC Annual Report 2025.

1. The number of attacks on the UK has increased (again)

It’s rare to read a cybersecurity sector report with good news to share, but still, the NCSC’s findings make for alarming reading. The past 12 months have seen a significant rise in cyberattacks, with a 50% increase in highly and nationally significant attacks compared to the previous year.

Digging a little further into those numbers, the NCSC reported 204 “nationally significant” cyber incidents between September 2024 and August 2025. That’s significant because it’s the highest ever number, and it’s a huge increase (130%) from the previous year’s 89 incidents. In all, the NCSC received 1727 incident tips in the period, with 429 of those classified as cyber incidents which required the agency’s support.

2. The biggest cyber threats to the UK

The report also tackles what the NCSC regards as the greatest threats to the UK’s cybersecurity, ranging from state-backed actors to artificial intelligence and large language models.

State actors

Given the geopolitical turmoil currently raging across the globe, it’s not a surprise to see crimes linked to a number of state-backed cybercriminals mentioned in the report. However, of more interest is the specific threats the NCSC has linked to each state.

  • China: The Flax Typhoon group, linked to several attacks on the UK
  • Russia: The Authentic Antics malware, which steals victims’ login details and tokens to enable long-term access to email accounts
  • Iran: Attempted attacks on US and UK critical national infrastructure (CNI) as part of the Iranian-Israeli conflict
  • North Korea: Fake IT worker scams, designed to funnel money from UK companies to the DPRK state

Ransomware

Ransomware remains one of the most acute threats to UK organisations. The NCSC highlights the retail attacks on Marks & Spencer and the Co-op as high-profile examples. However, the report stresses that while it might seem that retail has become a key target, in reality, most cybercriminals are sector agnostic, picking victims based on:

  • Who is most likely to pay a ransom
  • Who is most vulnerable to operational downtime
  • Who holds sensitive data that would cause significant harm to UK citizens if leaked

AI

You can read more about the specific threats and opportunities presented by AI in our blog on the subject. But, needless to say, the NCSC is very concerned about the use of AI, both by cybercriminals (particularly state-backed groups) to supercharge their attacks and by companies for everyday tasks. The latter presents a huge risk due to problems like slopsquatting and businesses unwittingly creating vulnerabilities through their use of LLMs and other tools.

Cyber proliferation

This is perhaps the most interesting of the threats discussed by the NCSC. Cybercrime has been going through a transition in recent years, from something largely practised in the margins by the highly tech-literate and cyber spies to a full-blown black market industry.

The rise of malware-as-a-service and DIY cybercrime has democratised hacking. No longer do cybercriminals need advanced coding skills or any real knowledge of how malware works to launch attacks. Instead, anyone can simply head to a dark-web marketplace and buy off-the-shelf malware and ransomware. This is a trend the NCSC expects to accelerate further over the next five years, particularly as regimes like the DPRK continue to back innovation among criminal groups.

Threats to critical national infrastructure

The cyber threat to the UK's critical national infrastructure (CNI) remains high. The NCSC notes the attacks by the DragonForce ransomware group (Coop, Harrods, M&S) as the current most likely kind of attack. However, the report also notes that hacktivist activity has shifted to low-skilled attacks against operational technology.

3. It’s time to act

The report represents a real hardening in the rhetoric used by both the NCSC and the government more widely. The NCSC stresses the urgency for every organisation – big or small – to act now by making themselves harder to successfully attack.

Notably, this places the responsibility firmly with businesses themselves. As Richard Horne, the NCSC’s chief executive, put it, “cybersecurity is now a matter of business survival and national resilience”.

How should firms do this? Well, one of the key recommendations from the report is for businesses to ensure suppliers meet Cyber Essentials standards to reduce supply chain vulnerabilities. Alongside this, it also draws attention to the importance of cyber insurance (and the fact that it’s often included with Cyber Essentials). The report also urges businesses to use the NCSC’s free early warning service to keep on top of emerging cyber threats.

4. Cybersecurity must become a boardroom priority

Much like DSIT’s Cyber Breaches Survey earlier this year, the NCSC makes it clear that cyber risk management is now a boardroom priority and responsibility. In the past, many businesses treated cybersecurity as a task for technical teams with little in the way of board oversight or direction.

The report makes it clear that this has to change. Boards now need to take a proactive approach to cybersecurity, both in terms of setting strategy and oversight of technical teams. It’s also worth noting that it’s highly likely this will be formalised in the upcoming Cybersecurity and Resilience Bill currently going through its last legislative stages.

5. High-profile attacks are a wake-up call for all businesses

When we look back on 2025 in years to come, it’ll almost certainly be remembered as the year societal attitudes to cybersecurity shifted. The attacks on Co-op, Harrods, M&S, Jaguar-Land Rover and now rail operator LNER have awoken the public to the potentially crippling impact of large-scale cyberattacks.

The same is true for businesses. While the business community has made huge strides in cyber preparedness and how it treats security in recent years, the last few months have really brought home the importance of cybersecurity. As a result, the NCSC expects all organisations, no matter the sector or size, to treat cybersecurity as a priority going forward.

6. The UK government is taking action

Finally, the NCSC and the UK government as a whole have been spurred into action by the events of this year. Most notably, following the publication of the NCSC’s report a ministerial letter has been sent to the CEO’s (or leaders) of FTSE 350 companies. The letter outlines several things the UK government expects business leaders to do, including:

  • Make cyber risk a Board-level priority using the Cyber Governance Code of Practice
  • Require Cyber Essentials across your supply chain
  • Sign up for the NCSC’s Early Warning service

Where does that leave ordinary businesses?

Of course, not everyone has the resources of an FTSE 350 company. In fact, 90% of businesses in the UK don’t. However, that doesn’t mean that the NCSC’s findings don’t apply. Cybersecurity is everyone’s responsibility, so here are a few things any business can do.

  • Focus on the importance of ‘Cyber basics’ like phishing awareness, security training, and technical controls such as multi-factor authentication
  • Complete Cyber Essentials certification at a minimum, especially if you’re part of a larger supply chain
  • Sign up for free-to-use tools like the NCSC’s Early Warning and Takedown Services
  • Consider purchasing specialist cyber insurance (often included with Cyber Essentials), which can help you recover far quicker following a breach
  • Use the Cyber Governance Code of Practice to implement board-level responsibility for cybersecurity

For managed service providers, the onus is on you (and partners like CyberSmart) to help businesses understand and adopt a good cybersecurity baseline. It’s often overlooked how many of the high-profile cyber incidents we’ve seen in 2025 stem from breaches at smaller suppliers, and we all have a part to play in making the UK a safer place to live and do business.

CyberSmart Patch helps you reduce vulnerabilities by keeping third-party software up to date — without the hassle. Try it today.

Frequently asked questions

    • Cyber risk to the UK continues to increase (a 50% increase on 2024)
    • In the wake of high-profile attacks, cybersecurity must become a boardroom priority
    • The UK faces a wide range of threats, such as ransomware, state-backed actors, attacks on critical national infrastructure, cyber proliferation, and AI.
    • Businesses must require Cyber Essentials across their supply chain
    • The UK government is taking action, including sending a ministerial letter to FTSE 350 companies
  • The NCSC and UK government have shifted their rhetoric to demand action from businesses to build national cyber resilience. The government now expects UK businesses to make cybersecurity a board-level priority and take action to improve cybersecurity across their supply chain.

    • Focus on the importance of ‘Cyber basics’ like phishing awareness, security training, and technical controls such as multi-factor authentication
    • Complete Cyber Essentials certification at a minimum, especially if you’re part of a larger supply chain
    • Sign up for free-to-use tools like the NCSC’s Early Warning and Takedown Services
    • Consider purchasing specialist cyber insurance (often included with Cyber Essentials), which can help you recover far quicker following a breach
    • Use the Cyber Governance Code of Practice to implement board-level responsibility for cybersecurity

Press release: CyberSmart takes up post as NCRCG National Ambassador

With Cyber Security Awareness Month firmly underway, the National Cyber Resilience Centre Group (NCRCG) has proudly welcomed CyberSmart on board as a National Ambassador.

Funded and supported by the Home Office, policing and Ambassador business partners, NCRCG is bringing together all those who have a vital responsibility for combating cybercrime to help strengthen the cyber defences of small and medium-sized enterprises (SMEs). The organisation forms part of the Cyber Resilience Centre (CRC) network alongside nine, regional and police-led Centres, which engage directly with the SMEs in their localities. 

A leading cybersecurity specialist, CyberSmart is perfectly placed to join the ranks of NCRCG’s National Ambassador Programme. With over 1,000 Managed Service Providers (MSPs) and over 6,000 SME customers in the UK, it is primed to act as an enabler to this crucial sector within the digital economy. 

In partnering with NCRCG, CyberSmart will empower MSPs and SMEs around cyber resilience and signpost the support offered by the CRC network and the national technical authority, NCSC.  

SMEs are the backbone of the UK economy, making up around half of the turnover in the UK private sector. As a result, SMEs must be made aware of the need to protect themselves and the steps they can take, as well as the value of cybersecurity. CRCs provide vital resources and advice for SMEs, making cyber resilience accessible to everyone, even those with limited in-house IT resources or knowledge. 

As seasoned industry experts, CyberSmart will also be using its platform as a National Ambassador to share its wealth of cybersecurity knowledge and research with SMEs across the country, including through NCRCG’s CyberVersed podcast series.

Jamie Akhtar, CEO of CyberSmart, said:

At CyberSmart, we’re proud to join NCRCG as National Ambassadors. Our mission to support, educate and empower UK SMEs, and the MSPs that serve them, on the importance of cybersecurity aligns with that of NCRCG. Whereas many advanced cybersecurity solutions primarily cater to enterprises, SMEs are often underserved, lacking affordable access and dedicated support, despite being major targets. Through initiatives like the UK government Cyber Essentials scheme, we’re able to help establish a baseline security standard for SMEs, which is crucial for supply chain integrity. As SMEs find themselves targeted more heavily by cybercriminals, it is essential that we educate and support these critical organisations.”

Joanna Goddard, Chief Experience Officer at NCRCG, said:

“CyberSmart is a fantastic asset to our National Ambassador cohort and, with the organisation’s links to Managed Service Providers in particular, will enable us to tap into a sector which plays a critical role in contributing to the UK’s cyber resilience. 

“Millions of small and medium-sized businesses across the country rely on the IT support and advice provided to them by their MSPs, however many are still not benefiting from any cyber security support which is a significant missing piece of the puzzle. It is therefore essential that we raise awareness amongst MSPs of the CRC network and where their customers can go for additional, police-backed help.  

“We are so pleased to be working with CyberSmart on this and to be welcoming them on board at such an opportune moment in the cyber security calendar.”

8 key takeaways from The CyberSmart MSP Survey 2025

MSPs are often overlooked. You’ll rarely hear about them in the media, and beyond the odd government report, there’s little research conducted about these organisations that form the backbone of many economies. And this is especially true when it comes to their cybersecurity.

In 2024, we set out to change this with our first CyberSmart MSP Survey. For 2025, we went a little further. This year we’ve expanded the survey to include markets with a strong MSP presence across the globe. The CyberSmart MSP Survey 2025 features 900 MSP leaders from the UK, France, Belgium, Australia, New Zealand, Sweden, Germany, and the Netherlands.

However, not everyone has time to read the full report. So, if that’s you, strap in and we’ll run through the key takeaways for The CyberSmart MSP Survey 2025.

1. MSPs are being breached at an alarming rate

The last year has seen a number of high-profile breaches of MSPs. One such example is the £3m fine levied by the Information Commissioner’s Office (ICO) on an MSP providing software and services to the NHS in March 2025, over security failings that led to a ransomware attack. 

Or, even more recently, in May 2025, the Dragonforce ransomware gang breached an MSP’s remote monitoring and management (RMM) tool to conduct a supply chain attack. But beyond the headlines, our survey uncovered evidence that successful attacks on MSPs are widespread.

Of the 900 MSP leaders we surveyed, 69% reported being breached two or more times in the last 12 months. This represents a slight increase from the 67% who reported breaches in our 2024 edition. Shockingly, 47% of those surveyed had experienced three or more breaches in the last 12 months.

Want to know more about the threats facing MSPs? Read the report in full here.

2. Perception of customer risk remains high

2025 has become the year of the major cyber breach. We’ve seen everyone from big-name retailers to government agencies being hit with attacks. So it’s not a surprise to see that MSP leaders are about as concerned for their customers’ cyber safety as they were in 2024.

58% of those that we surveyed felt their customers were more at risk, a slight decrease from 61% last year. However, what is interesting is that the percentage of MSPs who sense no change in risk level in the previous 12 months has halved (from 24% to 12%).

This suggests that MSPs broadly fall into two camps on risk. Either they’re relatively confident in their customers’ cybersecurity measures, and so feel risk has declined, or emerging threats have made them more concerned than ever.

3. Emerging AI threats are what keep MSP leaders up at night

Earlier this year, Forbes labelled 2024 “a landmark year in the evolution of AI”, and in many ways it was. 2024 was the year many of us began using generative AI in our day-to-day lives and work.

However, as with any new technology, the rise of generative AI has a darker side. Cybercriminals, never ones to miss a chance at innovation, have also begun using the technology, whether for uber-convincing deepfakes, spinning up malware in minutes, or weaponising AI’s tendency to hallucinate to launch attacks.

It’s perhaps this which explains why AI has rocketed to the top of MSP leaders’ concerns. Some 44% of our respondents listed it as a concern, which is remarkable when you consider that it barely featured in last year’s report. Worryingly, it’s also probably the threat most MSPs are least well-equipped to deal with, due to the lack of easy-to-use tools to counter AI-powered attacks.

4. MSPs transitioning to full cybersecurity providers

In last year’s report, we highlighted how customers increasingly expect MSPs to manage and implement their cybersecurity alongside IT services. In 2024, 65% of MSP leaders we spoke to told us that customers now expect them to manage their cybersecurity.

This trend has continued in 2025. A staggering 84% of MSPs now manage either their clients’ cybersecurity infrastructure or their clients’ cybersecurity and IT estate combined. 

This growing expectation for MSPs to manage cybersecurity is reflected in the scrutiny placed on them by customers in new business meetings. 77% of respondents said scrutiny of their businesses’ security capabilities has increased either slightly or a lot, suggesting that MSP customers are more aware than ever of the importance of good cyber credentials in a potential partner.

5. MSPs are rising to meet demand

81% of the MSPs we spoke to said they’d increased spend on specialist cybersecurity hires.

Likewise, 78% had upped spending on their security capabilities such as training, defences or products and services for customers.

But it’s not just security that MSPs have invested heavily in over the past 12 months.

MSPs are increasingly concerned about compliance with cybersecurity regulations and frameworks. Whether it’s the European Union’s Network and Information Systems Directive 2 (NIS2), Essential 8 in Australia, or the UK’s upcoming Cyber Security and Resilience Bill, compliance with regulations has become an important part of the landscape for MSPS across the globe.

As a result, MSPs are spending big on regulation. 60% of our respondents had invested in specialist regulatory hires in the last 12 months. Meanwhile, 64% had increased spending onregulatory capabilities over the same period.

6. MSPs’ cyber confidence is high, but there’s room for improvement

Despite the number of breaches suffered by MSPs, it doesn’t seem to affected overall confidence. 76% of respondents said that their business displayed either complete or above average cyber confidence, despite 69% of them suffering multiple breaches in the past year.
 
However, before we conclude that MSPs are overconfident in their cybersecurity, it’s worth adding a caveat. Given their role as cybersecurity providers and advisors to their clients, most MSPs do display above-average levels of cyber confidence, especially when compared to other businesses.

It’s also worth noting that the number of MSPs who described their cyber confidence levels as average or above (96%) has remained consistent with 2024. 97% of those we surveyed last year rated their cyber confidence levels as ‘fair’ or ‘great’. What’s more, outside the 20% who categorised their cyber confidence as complete, most MSPs (80%) recognised there was some room for improvement.

7. Confusion reigns over ransomware payments

By far the most surprising result of our survey concerns ransomware payments. Attitudes towards ransomware payments have shifted in the last few years. Many governments, most notably the UK, have mooted bans on ransomware payments for public bodies and government contractors. Meanwhile, cyber insurance providers are increasingly advising clients not to pay ransoms.

With that in mind, it was unexpected to see so many MSPs (45%) answer that they kept a dedicated allocation of money in case of ransomware attacks. More worrying still is the 11% of MSPs that have no dedicated budget for ransomware payments or cyber insurance.

What’s at the root of this? Well, what businesses should or shouldn’t do when it comes to ransomware payments has always been poorly defined. What your business is advised to do will largely depend on where you’re based and who’s advising you. And this is reflected in our survey results, suggesting that MSPs are just as confused as everyone else.

8. MSPs are concerned but prepared for regulations

For our last questions, we asked MSPs which upcoming regulations and legislation they were most concerned about.

As you’d expect, the results were largely predicated on geography, with UK MSPs most concerned about the upcoming Cyber Security and Resilience Bill (28%) and the Cyber Assessment Framework (49%). Whereas, MSPs based in the European Union were more concerned with the Digital Operational and Resilience Act (40%) and NIS2 (14%). And, naturally, Australian MSPs were focused on Essential 8 (15%). 

However, what’s far more interesting is how prepared MSPs are to meet legislative and regulatory changes. Regardless of jurisdiction, a large portion of our respondents were ready to meet regulations. 46% said they had a compliance plan for their business, and a further 15% indicated that they were ready to adapt to regulatory changes as and when they happen.
Another 39% of MSPS felt they were ready to offer a solution or guidance to customers in meeting cybersecurity regulations. This is a healthy figure; however, it’s a little unexpected that it isn’t higher.

Helping clients meet regulatory obligations is set to be the key opportunity for MSPs across 2025 and beyond, so those MSPs not meeting demand could be leaving revenue on the table.

Want to know more about the global cybersecurity landscape for MSPs? Access the CyberSmart MSP Survey 2025 in full, here.

DSIT’s Cyber Governance Code of Practice explained

If we’ve learned anything from the recent news cycle, it’s that large UK businesses need help. Attacks on M&S, The Co-op, and Harrods have left the country reeling and cybersecurity back at the top of the agenda. So, the release of the Department for Science, Innovation & Technology’s Cyber Governance Code of Practice for medium and large businesses feels timely.

But what is it? And should smaller businesses adopt its recommendations too? We answer these questions and more in this blog.

What is the Cyber Governance Code of Practice?

The Cyber Governance Code of Practice is a framework designed to guide boards and directors on effectively governing cyber risks. Primarily aimed at medium and large organisations, it aims to help business leaders build resilience within their organisations and defend against a wide range of cyber threats.

What does the code include?

Broadly speaking, the code sets out critical governance principles that every board (or director) should apply to their organisation. Think of it as a set of cybersecurity ‘dos’ for people in positions of authority.

More specifically, the code focuses on five fundamental principles. Much like Cyber Essentials and its five controls, these principles cover the key bases of effective cybersecurity. These principles are:

  • Risk management
  • Cyber strategy
  • People (cyber-aware culture and training)
  • Incident planning and response
  • Assurance and oversight

Each principle is supported by a set of three to five actions directors are advised to take. For example, one of the actions for People is to “Undertake training to improve your own cyber literacy.” These actions help directors and business leaders gradually build cyber confidence throughout their organisation and, ultimately, better secure it against cyber threats.

How does it integrate with other frameworks?

The Code complements other resources like the National Cyber Security Centre’s (NCSC) Cyber Security Toolkit for Boards and the Cyber Assessment Framework (CAF).

Alongside this, the code is bolstered by free cyber governance training and a cybersecurity toolkit to help boards implement its recommendations.

Is the code voluntary?

While voluntary, the Code is positioned as the minimum level of board accountability expected within UK businesses. Plus, it likely won’t be voluntary for long. The upcoming Cyber Security and Resilience Bill is widely expected to reinforce these standards and possibly even create some form of legal responsibility for boards. 

In other words, it’s well worth getting ahead of the legislation by adopting these measures now.

Why has the code been created?

Time for a brief history lesson. The code was co-designed by the NCSC and industry experts to address two things. Firstly, as we’ve seen illustrated by the attacks on some of the UK’s flagship retailers in the last few weeks, there’s a high prevalence of cyber incidents among large businesses. According to DSIT’s latest research, some 74% of large and 67% of medium-sized organisations reported cyber incidents in the past year.

Secondly, board-level responsibility for cybersecurity has seen a gradual decline since its high of 38% of UK organisations in 2021 (the figure is 25% in 2025). The code aims to put managing cyber risk back at the front and centre of boards’ thinking and give senior leaders a clear framework for how to do it.

More broadly, the frameworks fit with upcoming legislation to form a key part of the UK government's approach to improving national cyber resilience.

Who is the code for?

We mentioned earlier that the Cyber Governance Code of Practice was primarily aimed at medium to large businesses. This is because larger businesses typically have a formalised board and governance structures.

However, you shouldn’t take away the message that the framework isn’t useful if you’re a small business. Most obviously, because small businesses often do have boards or, at the very least, directors. More importantly, the framework has value for any organisation.

Regardless of your organisation’s size, adopting its recommendations will help you bolster your defences, mitigate risks, and gain cyber confidence.

Want a simple solution for meeting the Cyber Governance Code of Practice's staff training recommendation? Check out CyberSmart Learn.

The latest updates on the UK government’s Cyber Security and Resilience Bill

Back in July 2024, the UK government announced its plans to bring a Cyber Security and Resilience Bill before parliament. The bill is designed to tackle the growing threat to the UK’s critical national infrastructure (CNI), such as water, power and healthcare.

Things have been pretty quiet ever since, beyond some theorising about what the bill might include by industry blogs and panel discussions. But, as of early April, we have movement! The Department of Science, Innovation and Technology (DSIT) has released its Cyber Security and Resilience Policy Statement, setting out legislative proposals.

Here’s everything we know about the upcoming Cyber Security and Resilience Bill and what it could mean for your business.

What are the legislative proposals?

Of course, there’s no guarantee that all of the measures in the following list will be enacted or that, if they are, they’ll have the same scope. We’ve got months of amendments in both the Commons and the Lords before we see the final bill early next year. However, this what has been sketched out.

1. Broader regulatory scope

The bill aims to broaden the scope of the 2018 NIS Regulations to include more organisations and suppliers. This would place stronger obligations on those deemed “critical” suppliers, like Managed Service Providers (MSPs) and those part of public sector or national infrastructure supply chains.

2. More power for regulators

Regulators would have greater powers to improve cybersecurity and resilience in the sectors they oversee. These powers could include:

  • Technical standards: Establish clearer cybersecurity standards and requirements based on the National Cyber Security Centre’s (NCSC) Cyber Assessment Framework.
  • Incident reporting improvements: Expanded criteria, faster (24-hour initial notification, 72-hour detailed report), streamlined reporting to regulators and the NCSC, and new transparency requirements, such as informing customers directly of significant incidents.
  • ICO powers: Improved proactive information gathering powers for the ICO to better manage risks within digital services.
  • Cost recovery: Regulators could recover the costs of oversight through fees, reducing the taxpayer’s burden.

3. A more flexible cyber framework

The proposals would give the government greater flexibility to update cybersecurity frameworks, as and when needed, without primary legislation.

This is a sensible approach, allowing regulators to become a little more agile in responding to new threats and trends. For example, this would allow the government to extend the framework to cover new sectors. In fact, we think it’s highly likely this will happen as the UK’s cyber infrastructure further matures.

4. Greater executive powers

The bill also seeks to grant the government much stronger executive powers to respond to cyber threats when necessary for national security. Essentially,  this means that if an organisation subject to regulation isn’t addressing a cyber threat that could impact national security adequately, say, a supply chain attack involving critical infrastructure, the government could step in and force them to act.

What’s still under consideration?

As with any bill at this stage of the legislative process, some areas are still under consideration. The exact scope of the powers the Secretary of State could be granted is a live debate, due to obvious concerns about executive overreach. And, there are two other proposals still being ironed out.

Data centres regulation

The government is considering regulating data centres. This is due to their newly designated (and overdue) status as critical national infrastructure. 

Any data centre with 1 megawatt capacity or more would likely be within scope of the regulations, unless they’re an enterprise data centre, in which case the threshold would be significantly higher (10 megawatt).

According to Raconteur, there are 224 such data centres, run by 68 operators, across the UK. The government expects 182 of them to fall in scope. So, if data centres are included, it’d be a major legislative change.

Statement of strategic priorities

The bill could also enshrine in law a commitment to publish a regular “statement of strategic priorities for regulators”. The thinking behind this is to create a unified and consistent approach to cybersecurity among UK regulators and ensure everyone is pulling in the same direction.

How will the Cyber Security and Resilience Bill affect MSPs?

If you run an MSP, the bill’s effect on your business will largely depend on its size and who it works with. 

According to the government’s 2024 figures, there are 11,492 MSPs active in the UK. Of these, we estimate that between 1,500 and 1,700 MSPs are potentially within scope of the NIS regulations. However, up to 600 may already be captured under existing cloud provision to their customers.

That leaves around 900 to 1,100 large and medium-sized MSPs that may need to consider the impact of regulatory compliance with NIS.

Due to their size the 3,200 small MSPs and 6,600 micro MSPs operating in the UK are likely to be exempt from regulation. But if you lead a smaller MSP, that doesn’t necessarily mean the rules won’t impact you at all. You could still feel the effects due to standards embedded by larger competitors, or if you’re with a critically important sub-sector, such as defence.

What does the industry think of the proposals?

The industry has generally welcomed the announcement. Few within the cybersecurity sector disagree that our critical national infrastructure needs stronger defences. Or that any attempt to tackle the threat has to include the thousands of businesses that make up CNI supply chains.

Last year alone saw a ransomware attack on NHS pathology provider Synnovis that led to permanent damage to patients’ health, a data breach of payroll information at the Ministry of Defence, not to mention the revelations about Thames Water’s poor security.

Meanwhile, the NCSC  reported  2024 was a record-breaking year for attacks on CNI. And, according to the 2024 Thales Data Threat Report, 93% of CNI organisations saw a rise in cyber-attacks over the last year, with  42% of those suffering a data breach. 

Against this backdrop, despite the extra obligations it places on businesses, it only be seen as welcome and long overdue.

Did you know 59% of SMEs provide no mobile cybersecurity training to staff? Find out why this is a problem and what to do about it in our SME Mobile Threat Report.

What PPN 014 means for your business

Procurement Policy Note (PPN) 014 changes the requirements for government and public sector body tenders in the UK. Here’s everything you need to know.

What is PPN 014?

PPN 014 is a government directive aimed at reducing cyber risk in public sector supply chains. Essentially, if your business supplies services or products to government departments or bodies, you’ll be required to prove you have basic cybersecurity controls in place. The simplest way to do this is to complete Cyber Essentials certification.

Why has PPN 014 been enacted?

Simply put, supply chain attacks pose a huge problem. More than 75% of software supply chains experienced cyberattacks in 2024, at a rate of one every two days. What’s more, supply chain attacks are projected to cost the global economy $138 billion (£108 billion) by 2031. 

At the same time, according to government research, UK businesses are ill-prepared for supply chain risks. Only one in ten businesses say they review supplier risk (11%, vs. 9% of charities). PPN 014 is an attempt to plug this gap.

Want to know more about the risks posed by supply chains? Check out our guide to supply chain attacks

History and timeframes

Since 2014, suppliers bidding for certain government contracts have been expected to demonstrate a minimum level of cybersecurity. Earlier PPNs ( PPN 09/14 and PPN 09/23) built this foundation and PPN 014 updates it in line with recent legislation such as the Procurement Act 2023 and Procurement Regulations 2024.

If you’re a business PPN 014 applies to (more on which in the next section) there are a couple of dates to bear in mind:

  1. 24th February 2025 – all procurements that begin on or after this date are subject to the new rules

2. Contracts awarded up to (and including) the 23rd February 2025 will continue to follow the earlier PPN 09/23  requirements

Who is in scope for PPN 014?

If you work with any of the following, you’ll be considered ‘in scope’ for PPN 014 the next time you bid for a contract: 

  • Central government departments and executive agencies
  • Non-departmental public bodies (NDPBs)
  • NHS bodies

To bid for any of these contracts you must be prepared to demonstrate that your cybersecurity meets the standards laid out by PPN 014.

What you need to do to meet PPN 014

Procurement requirements can appear daunting, especially if you’re new to thinking about your cybersecurity. However, the provisions of PPN 014 are actually quite simple and shouldn’t require wading through hours of paperwork or reinventing the wheel. Here’s what you should do.

1. Get Cyber Essentials certified

First things first, you need to complete Cyber Essentials or Cyber Essentials Plus certification. Cyber Essentials certification will help you put in place the five basic security controls required by PPN 014. 

Plus, it’ll protect your company. Cyber Essentials is proven to defend against 98.5% of the most common cyber threats. And, organisations with Cyber Essentials are 92% less likely to claim on cyber insurance policies.

All in all, it’s the easiest route to meeting PPN 014 requirements.

2. Check your certification scope

Once you’ve completed Cyber Essentials, you need to check the scope of your certificate. Does it cover the parts of your business that are relevant to the contract you’re bidding for?

If your operations are split across multiple locations, offices or areas you’ll need to clarify which parts are included. In most cases, this will have been something you tackled when undertaking the assessment. However, it’s always worth checking nothing has changed as it could invalidate your evidence if part of your operations fall outside the scope of your certificate.

3. Prepare documentation

Next, you’ll need to provide evidence of your certification when tendering. You should receive either a digital or physical certificate once you complete the assessment.

4. Keep an eye on your renewal date

Cyber Essentials is an annual certification so you’ll need to renew it once a year to account for any changes in your business. With this in mind, it’s worth keeping an eye on when your renewal date is coming up so you don’t become ineligible for government contracts.

How to prepare for PPN 014

1. Review the guidance

Visit the National Cyber Security Centre’s (NCSC) Cyber Essentials website and use the readiness toolkit to understand the requirements.

2. Understand your contractual requirements

Check tender documents carefully to confirm whether Cyber Essentials certification (or equivalent) is needed. If in doubt, you can always ask the contracting authority or your managed service provider for clarification.

3. Talk to CyberSmart

CyberSmart is dedicated to helping small businesses build Complete Cyber Confidence within their organisations. If you’re struggling with the requirements of PPN 014 or need to start the Cyber Essentials certification process, talk to us, we can help. We offer unlimited guidance and support, free 25k cyber insurance on completion, and we often get you certified in as little as 24 hours. 

If you already work with an MSP (Managed Service Provider) or IT company, let us know so we can speak with them to support you through the process.

How can Managed Service Providers help?

Of course, if you’re an MSP who works with government bodies you’ll need to comply with the requirements of PPN 014 yourself. If this is the case, you likely need a Cyber Essentials certification (something we recommend for all MSPs, regardless of who you work with).

However, you may also need to help your clients meet these requirements. Whether by managing their IT services, helping them complete Cyber Essentials, or advising on security best practices, you have a vital role to play.

Supporting your clients

There are a few key things you can do to support your clients with PPN 014, these are:

Subcontractor management

If you work with other vendors or subcontractors, make sure they meet the necessary cybersecurity standards. By far the simplest way to do this is to insist that anyone you work with has a valid Cyber Essentials certification as a minimum requirement.

Provide advice

Many businesses, particularly SMEs, won’t be aware that they need to complete Cyber Essentials to bid for government contracts. This is your chance to walk them through the process, offer advice on best practices and, ultimately, help them become more secure.

Offer pre-tender support

Offer assistance to clients in preparing tenders that require PPN 014 compliance by outlining the certification roadmap and available resources such as the NCSC’s Active Cyber Defence guidance.

Finally, if you need support, reach out to CyberSmart. We work with over 800 MSPs across the UK and beyond. Find out how partnering with CyberSmart could benefit your business here.

Supply chain CTA 2


Everything you need to know about the upcoming Willow Question Set for Cyber Essentials

Spring is on the horizon and, in the cybersecurity world, that often means only one thing: changes to the Cyber Essentials question set. Titled Willow, a new question set is due to go live on 28th April 2025, replacing 2023’s Montpellier question set.

The Willow Question Set introduces several key updates to enhance organisations’ protection and reflect modern work practices. Here’s everything you need to know. 

Why is the change happening? 

As cyber threats continue to evolve, so too must our defences. In recognition of this, IASME and the National Cyber Security Centre (NCSC) have made some subtle tweaks to the question set. 

It’s best to think of these changes as a natural evolution of Cyber Essentials to account for new forms of authentication and changing working practices. Plus, they should help make the assessment process smoother by providing better guidance for anyone completing the certification.

What are the key updates in the Willow Question Set?

Scope clarification

The new question set provides clearer guidelines on what must be included in the scope of the assessment. For example, this includes any device accessing organisational data or services, even if they connect to cloud services rather than internal systems. 

Firewall management

Under the Willow Question Set, all firewalls and routers must be listed in the network equipment section. There’s also a requirement for home and remote routers to use software firewalls.

The language around firewall management has also been updated in an attempt to drive businesses to review their firewall rules regularly.

Password management

Willow updates existing password policy best practices by emphasising the need for secure configurations. It also introduces passwordless authentication as an acceptable method for securing firewalls and routers. However, passwordless systems may still require brute-force protection methods – such as randomly generated passwords, using letters and symbols etc – if they use backup passwords.

Vulnerability fixes

The terminology for patching throughout the assessment has been changed to “vulnerability fixes.” This is to better reflect the importance of patching and includes configuration or registry changes for vulnerabilities with a CVSS score of 7 or higher, or those classified as high or critical risk.

Definitions and language

There are a few minor changes to the language within the question set. For example, updating the term "plugin" to "extension" and changing references from "home working" to "home and remote working.”

What about Cyber Essentials Plus?

As well as being subject to a new question set, there are some key changes to the Cyber Essentials Plus certification process to be aware of. Assessment tests 1 (Remote Vulnerability), 3 (Malware protection), 5 (Account Separation) remain the same. However, there have been some tweaks to tests 2 and 4.

Test 2 – Internal Vulnerability Assessment

The sampling process for the Internal Vulnerability assessment has changed substantially:

  1. Auditors must conduct sampling immediately before the audit. In previous years, the sample was drawn from the self-assessment report.
  2. Assessors validate the way sampling is conducted This means an assessor will need to see the methods used to determine the number of devices in scope for the assessment.
  3. The assessor or certification body will hold and store sampling evidence for the one-year duration of the certificate. IASME can also request this information at any time.
  4. The specific devices included in the assessment, including the vulnerability scanning and end user tests, will be now be determined by the assessor. 
  5. The random sample of devices picked by the assessor will be sent to the applicant no more than 3 working days in advance.
  6. Internal vulnerability scans will now include ‘configurational changes’ as failure conditions. In the past, high severity vulnerabilities like Unquoted Windows File Path, or Registry Key issues weren't considered conditions for failure – they are now.

Test 4 – Multi-factor Authentication for Cloud Services

Rather than testing all cloud services, as in previous years, a sample is taken instead.

Only cloud services that are accessible by users or devices included on the random scope are tested. If none of the users can access a specific cloud service, then that service is not tested.

Impact on your business

The impact of these changes on your business should be positive. The Willow Question Set provides better guidance and clarity for anyone undergoing Cyber Essentials Certification. Not only will it make the assessment processes easier, but it’ll also better equip your business to meet modern cyber threats. 

However, it’s well worth familiarising yourself with the new requirements before your next renewal.

Managed service providers

The same is true if you’re an organisation providing Cyber Essentials for businesses. Your customers should be able to get through the assessment with less support and finish it better protected to boot.

Again, it’s definitely worth getting to grips with the new requirements so you can offer support to customers where they need it.

If you have any questions about the changes or want to know more about what they mean for your business, please get in touch. We’ll be happy to walk you through it.

Did you know 59% of SMEs provide no mobile cybersecurity training to staff? Find out why this is a problem and what to do about it in our SME Mobile Threat Report.


5 key findings from the CyberSmart Mobile Threat Report

To celebrate the launch of CyberSmart Active Protect for mobile, we commissioned a survey asking 250 UK CEOs from companies with under 250 employees about their mobile security habits. We hoped to find out how the UK’s small businesses are tackling mobile security threats, what their security looks like, and whether there were obvious areas for improvement.

Our resulting SME Mobile Threat Report makes for illuminating and, at times, sobering reading. Here are our key takeaways.

1. Most small businesses expect staff to use mobile phones for work

Bring your own device (BYOD) policies can offer dramatic CapEx savings. And, unsurprisingly, this is a very attractive proposition for small businesses with tightened belts. Therefore, it’s no surprise that 60% of organisations expect their employees to use mobile devices to carry out work tasks, despite not providing all of them with work phones.  Indeed, 65% of those businesses that don’t provide all staff members with mobile phones expect staff to use personal devices.

There’s nothing wrong with this in principle. Why wouldn’t you take advantage of devices your people already own, rather than investing heavily? However, as we’ll see shortly, it can pose some problems. 

2.  Many SMEs don’t have a mobile code of conduct for staff

Behaviour is essential to any successful BYOD policy. Staff need to understand what’s expected of them from a security perspective to work safely.

For example, you might enforce a policy that staff must never connect to an unsecured Wi-Fi network without using a VPN.  A clear code of conduct or security policy can help prevent your business from being exposed to unnecessary risks. 

So it’s concerning to see that while 59% of small businesses do have a code of conduct for completing work-related tasks on personal devices, over a third (39%) don’t.

3. Most SMEs don’t offer mobile security training to staff

Although it’s concerning that many small businesses are implementing BYOD programmes without clear security and conduct policies in place, we came across an even bigger problem. 

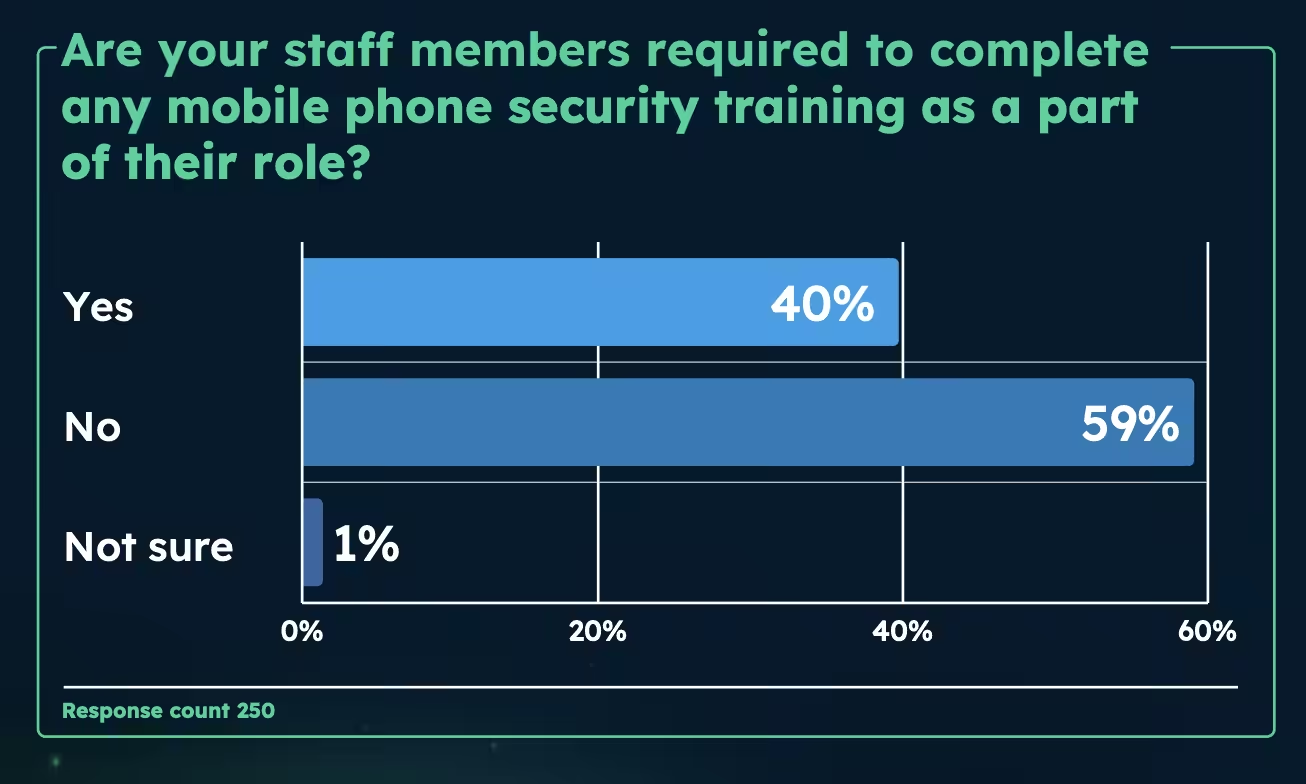
The majority (59%) of our respondents said that they don’t provide any mobile phone security training for staff. Without training on how to identify and avoid cyber threats or what safe online behaviour looks like, these businesses are courting potential disaster.

According to research from Cybint, 95% of cyber breaches stem from some sort of human error, or, in simple terms, could have been prevented. This is also backed by older research from Stanford University and Tessian which puts the figure at 88%.

Whichever figure you prefer, that’s a lot of preventable cyberattacks. And,

by not providing security awareness training to staff, it’s exactly these kinds of breaches that small businesses are risking.

Interestingly, many of our concerns around SMEs neglecting staff training and policies are born out later in the Mobile Threat Report.

According to the Department for Science Innovation & Technology (DSIT), 84% of all UK businesses have received some kind of phishing attack in the last 12 months. So, we asked SME leaders whether they or anyone at their business had clicked on a malicious link via mobile.

Although almost half (47%) of small business leaders responded no, some 38% reported that someone within their business had clicked on a phishing link – still a high number. What’s more, the real figure is likely to be somewhat higher given that a further 15% were either unsure or preferred not to answer.

This poses a real risk for small businesses. The UK has lost £1.7 billion to phishing scams in the last year, while the average cost of a breach to an SME ranged between £2,240 and £17,190. Worse still, phishing scams are often used to launch much nastier cyber threats such as ransomware and banking trojans. 

5. SME staff are engaging in risky behaviour

Perhaps unsurprisingly given the problems we outlined earlier, the day-to-day cyber hygiene of SME staff raises concerns.

For example, a quarter of respondents admitted using a mobile device for work at a public charging station (e.g., at an airport or café), and 36% of respondents have worked from a public WiFi network on a mobile device. A further 9% admitted to forwarding corporate data to a personal account, and 11% admitted to storing corporate passwords or log in credentials on a mobile device without encryption.

This risky behaviour suggests low mobile security awareness among employees and a clear lack of concrete policies.

The good news? These risks are easy to mitigate

We’ve painted a pretty bleak picture of UK SMEs’ mobile security. And, it’s true, our research indicated some areas of real concern. However, the good news is that all of the issues our survey revealed are easy to mitigate.

To find out how, read our full report here.