AI and cybersecurity: what you need to know

If there is a defining buzzword of the last few years, it’s probably artificial intelligence (AI). Barely a day passes without a company, tech entrepreneur, or even government proselytising about the technology and its transformative potential. However, when it comes to AI and cybersecurity, the picture is blurrier.

We often hear about the negative side of AI. Justifiably so, as the NCSC puts it

“AI will almost certainly continue to make elements of cyber intrusion operations more effective and efficient, leading to an increase in frequency and intensity of cyber threats.”

Nevertheless, things are more complicated than they first appear. Of course, AI can be used by criminals to supercharge cyber threats. But it can also be used to create stronger defences than ever before. In this blog, we’ll look at both the good and the bad, before asking how businesses looking to leverage AI can do so safely.

What do we mean by AI?

For the purposes of this explanation, we’ll be focusing on the two most widely used types of AI: generative and agentic (there are others).

Generative AI

This is the type of AI you probably use in your daily life – think ChatGPT, Claude, Microsoft Copilot or Perplexity. Also known as large language models (LLMs), generative AI uses existing data to ‘generate’ new content like text, video, images, audio or code. Crucially, this type of AI relies heavily on human inputs or ‘prompts’ to create things.

Agentic AI

Agentic AI is a type of artificial intelligence that is designed to operate more or less autonomously with minimal human supervision. Unlike generative AI, agentic AI is proactive and has agency to adapt to context and pursue complex goals without prompting or guidance at least in theory.

Both types of AI can be put to a wide variety of tasks, from software development to customer support. Plus, they can even be used for cybersecurity, potentially offering levels of protection that businesses would’ve needed very deep pockets to acquire just a few years ago.

So far, so good, we hear you say. What’s the catch?

Well, like any powerful technology, AI isn’t inherently good or bad. The key is how it’s used and who is using it.

AI and cybersecurity: the bad

For all its transformative potential, AI has a darker side. Let’s deal with that first. We’re going to split this into two sections: one dealing with the non-malicious cybersecurity risks AI raises, and the other, how the bad guys are using it to their advantage.

Hallucinations and human error

Hallucinations

Have you ever asked an LLM a question and felt that the answer it gave you wasn’t quite right? You weren’t imagining things. A common problem, particularly with LLMs, is AI hallucination. This is exactly what it says on the tin. Sometimes, generative AI models present incorrect or misleading information as fact.

There are a few reasons for this, ranging from being trained on poor-quality data to unclear prompts from the human guiding it. The technical how and why isn’t particularly important, but what is, is how this becomes a cyber risk.

Unfortunately, it’s not just content that LLMs hallucinate. If you’re using one to code, it may write scripts containing open-source software packages that don’t exist. Why does this matter? Well, cybercriminals have devised a way to use AI hallucinations to their own malicious ends – a process called “slopsquatting”.

Basically, a cybercriminal could publish a fake package, containing malware, to an official repository with the same details as the hallucinated one. When another user prompts the same LLM to generate code and it returns the same hallucinated response, the victim would be directed to download the malicious package, exposing their systems to malware.

This might sound unlikely. After all, what are the chances of a different user generating the same code? Sadly, it’s more common than you might think. According to research from the University of Texas at San Antonio, Virginia Tech, and the University of Oklahoma, package hallucination is a common problem with (LM-generated code. Across all LLMs, researchers found hallucinations present in around 20% of all packages.

The persistent, repeatable nature of these hallucinations makes them very bad news for anyone other than cybercriminals.

Human error

A far bigger problem than slopsquatting is good, old-fashioned human error. We can all be guilty of not really thinking about what we’re doing when using tools like LLMs, particularly when it comes to the data we share with them. 
For example, say you want to automate certain tasks in your business using generative or agent-based AI. The first thing you’d need to do is feed the AI algorithm data to train it. However, it really matters what data you use; it’s possible for an AI to “see too much”.

Hackers have realised that some companies will feed sensitive information such as business strategy, customer data, or intellectual property into AI algorithms. Unfortunately, they’ve also devised a way of accessing this data. All an attacker who gains access to the AI needs to do is continually prompt it with leading questions until the AI unwittingly reveals corporate IP.

It’s a similar story with employees using AI for day-to-day tasks. Without clear guidance, there’s always a risk that staff could share too much information with AIs, particularly those using free or open-source models.

The bad guys tool up

We’ve already mentioned a couple of ways cybercriminals can exploit AI to launch cyberattacks. Unfortunately, those are far from its only uses for hackers. Here are a few additional examples of how cybercriminals are taking advantage of AI.

AI-powered social engineering

Social engineering is by far the most common form of cyberattack. And that isn’t likely to change with the advent of generative and agentic AI. Both allow cybercriminals to perfect the art, whether that’s by spinning up convincing phishing campaigns faster than ever, creating malicious AI chatbots, or generating near-perfect deepfakes.

Malware and ransomware development

Perhaps the most worrying use of AI is the automation of malware creation and attacks. There’s already evidence of cybercriminals using AI to create new malware variants with unique characteristics to help evade detection. 
The picture becomes even more sinister when you consider how agentic AI could be used. It’s entirely plausible that agentic AI could be used to create and run malware that analyses an organisation’s defences and adapts in real time to evade detection by malware protection tools.

Worse still, we know that malware as a service has grown in popularity over the past few years. This means there’s likely to be a secondary market for AI-developed malware and ransomware, selling to cybercriminals who aren’t sophisticated enough to create these tools, potentially upping the level of attack they’re able to launch.

Data poisoning

Data poisoning refers to when cybercriminals go after the very datasets AIs are trained on. By injecting false information into the dataset, attacks can foul the model’s learning process, corrupting its decision-making.

AI-driven breaches

While relatively unsophisticated tactics like brute force and DDoS attacks are already largely carried out by bots, AI has the potential to supercharge them. AI can be used to improve the efficiency and speed of password cracking or to create tools that can bypass security measures like CAPTCHAs and other forms of biometric authentication.

AI and cybersecurity: the good

Although we might be entering a golden age of cybercrime for hackers, don’t despair; there is hope. Here are just a few potential uses of AI for cybersecurity.

Agentic AI as a defensive tool

We’ve painted a pretty bleak picture about the nefarious capabilities of AI. However, it’s important to remember that AI is a tool which can be used for good or ill, depending on who’s using it.

There are a number of companies that’ve already developed defensive agentic AI products. For example, Darktrace’s Antigena which can can identify and mitigate threats as they emerge, without needing prior knowledge of the specific malware or attack method. Likewise, Crowdstrike has developed its Falcon platform, an advanced endpoint protection solution.

These are just two examples of the technology being developed. And, while the cost of these tools is currently prohibitively expensive for most small businesses, options for all price points are likely to become available over time.

Threat intelligence and predictive analysis

AI models can be invaluable in determining where the next attack is coming from. Some models can be used to aggregate and analyse data from across the globe, identifying emerging threats and predicting attack patterns.

Automating security measures

Another exciting potential use of AI is for automating routine security measures. For instance, AI models can be instructed to configure firewalls or scan for threats, or patch vulnerabilities, freeing up staff for complex technical issues.

Incident response

We all know how quickly you respond to a breach or threat can often determine its outcome. Agentic AI could dramatically speed up our ability to respond by analysing incidents, providing recommendations or even initiating automated responses to threats, minimising the damage and downtime.

Training

Finally, Generative AI is fantastic at creating engaging content. So why not use it to create scenario-based training, such as phishing simulations? These scenarios could be tailored to adapt in real time, helping employees stay ahead of emerging threats.

What should you do to mitigate AI risks?

We’ve tackled the potential uses of AI models for cybersecurity, both good and bad. But what should you be doing to safeguard your business in the here and now?

Improve your AI security posture

If you’re using AI systems for day-to-day tasks around your business, there are a few basic cybersecurity measures you’ll need to adopt. These include:

  • Encrypting corporate data to prevent AI models from training on it and cybercriminals from accessing it
  • Adopting strict access controls on who uses AI and for what within your business
  • Continuous monitoring of your AI systems for unusual behaviour

Educate your people

Ensure everyone in your business is aware of the dangers of AI tools, both in terms of attacks and human error. You can do this through cybersecurity awareness training and by implementing an AI security and governance policy that outlines what legitimate and risky uses are.

Avoid vibe coding

If you’re a business that employs developers or programmers, you should discourage the use of vibe coding for any system that could pose a security risk. “Vibe coding” is a process where users express their intention using plain speech, and the AI transforms that into code.

The problem with vibe coding is that the developer often doesn’t know how the AI created the code. It’s a leap of faith, one which can lead to problems like slopsquatting or inadvertently creating vulnerabilities.

A note of caution

All of the above comes with a fairly large caveat. Current agentic AI, despite the hype, still has technical limits. Many AI agents today perform well in narrow, well-defined tasks but struggle with complex, general contexts.

In a live cybersecurity scenario, an AI might handle known patterns but get confused by a novel situation that doesn’t fit its training. This applies equally to attack and defence, making a lot of what we’ve talked about in this blog theoretical.

That being said, AI models continue to improve at a rapid rate, and these capabilities aren’t far away. So, if you aren’t already thinking about how AI affects your cybersecurity, there’s no time like the present.

Want to give your people the skills to recognise cyber threats before they turn into breaches? Check out CyberSmart Learn, our cybersecurity focused learning management system.


Bridging the IT/OT gap: cybersecurity training for manufacturing

When your production line grinds to a halt due to a cyber incident, the impact is far-reaching. Despite this, many manufacturers still treat their IT and operational technology (OT) as separate entities with separate security needs. Effective cybersecurity training for manufacturing addresses this divide and the sector-specific vulnerabilities.

Why manufacturing is a prime target for cybercriminals

Manufacturing is the most targeted sector, accounting for 25.7% of all cyber-attacks

Why? Because: 

  1. Downtime has a significant impact on manufacturing 
  2. Manufacturers have high-value intellectual property such as product designs/blueprints, proprietary manufacturing processes, chemical formulas, etc. 

With such valuable assets at stake, manufacturers need robust protection at every level – yet one vulnerability consistently undermines even the best technical defences. As with other industries, the human element is the weakest link in their cybersecurity. In fact, four out of ten cyber threats involve employees.

The importance of cybersecurity training for manufacturing

Manufacturing facilities face a unique cybersecurity challenge – they operate two different technology networks simultaneously. Business systems (IT) handle company information, while specialised machinery (OT) controls factory equipment. Good cybersecurity training helps unite IT and OT teams, which often have different security priorities. It also addresses the talent shortage in manufacturing cybersecurity, which exceeds 67% globally.

Want to know more about the threats facing manufacturers like you? Check out our guide to cybersecurity for manufacturers.

Training priorities for manufacturing environments

Your cybersecurity training programme should target five key areas that address manufacturing vulnerabilities:

1. Recognising OT-specific threats

Train employees to spot attacks designed to target industrial control systems. These threats look different from traditional ones and include manipulated sensor readings, unexpected system changes, and commands that could damage equipment.

2. Supply chain security awareness

With 15% of cyber incidents originating from vendors or partners, supply chain security breaches are a significant risk. 

Teach employees how to: 

  • Conduct vendor risk assessments
  • Identify what security requirements should feature in contracts
  • Monitor third-party access to systems

3. Securing the IT/OT boundary

Show teams how to maintain separation between business networks and production systems while still allowing necessary data flow. This might include learning about data diodes, industrial firewalls, and network segmentation.

4. Ransomware protection

With 71% of manufacturing cyber-attacks involving ransomware, employees need to understand how ransomware attacks can paralyse production.

Your training should cover: 

  • The importance of keeping industrial control systems patched
  • Protocols for isolating infected systems 
  • Backup strategies for OT environments

5. Phishing readiness

Manufacturing staff are prime targets for phishing attacks disguised as supplier communications, order queries, or delivery notifications. Train your team to spot these deceptive emails by examining sender addresses, checking for pressure tactics ("urgent action required"), and verifying requests through separate channels before clicking links or opening attachments.

6. Regulatory compliance

Manufacturing faces complex compliance requirements that vary by industry, product, and location. Training staff on compliance reduces violation risks.

Focus on:

  • Regulations specific to your industry
  • Security controls required by different frameworks
  • Documentation processes
  • Audit preparation

7. Incident response plans

Develop manufacturing-specific incident response procedures that prioritise operational safety and continuity. This ensures teams know how to respond without making hasty decisions that could cause further damage.

Comparing top cybersecurity training providers for manufacturing

When selecting a cybersecurity training provider for your manufacturing operations, it's important to choose one that understands the unique challenges of industrial environments and the IT/OT convergence. Here's how several leading providers compare:

CyberSmart Learn

Strengths:

  • Manufacturing-specific training modules
  • Strong focus on regulatory compliance
  • Supports Cyber Essentials certification
  • User-friendly platform accessible to non-technical staff

Limitations:

  • Limited simulation capabilities for industrial threats

Ideal for: small to mid-sized enterprises that want to establish a strong security awareness program with clear compliance benefits.

Dragos

Strengths:

  • Specialized in industrial control systems (ICS) security
  • Offers hands-on OT security training
  • Includes ICS-specific threat intelligence

Limitations:

  • Higher price point
  • May be too technical for general employee training

Ideal for: larger manufacturers with sophisticated OT environments that require specialised technical training for engineering and security teams.

KnowBe4

Strengths:

  • Large library of security awareness content
  • Customizable training paths for different roles
  • Robust analytics and reporting

Limitations:

  • Less manufacturing-specific content
  • Limited coverage of OT security topics

Ideal for: Organisations looking for security awareness training with strong phishing defence capabilities.

Accreditations to support your cybersecurity training

As your employee training progresses, you'll be in a good position to improve your security posture even further with an accreditation like Cyber Essentials. This certification offers a clear framework that can reduce cyber risks by up to 98.5%. It covers five key control areas:

  • Firewalls and internet gateways
  • Secure configuration
  • Access control
  • Malware protection
  • Patch management

Working towards an accreditation and having regular training keeps cybersecurity top of mind.

Keep your cyber defences running like a well-oiled machine

Don't wait for a costly incident to prioritise cybersecurity training for manufacturing. With proper education that addresses both IT and OT environments, your team becomes your strongest defence against threats targeting your production line.

Considering introducing cybersecurity awareness training into your business? Check out CyberSmart Learn, our cybersecurity focused learning management system.
“Note to self” phishing scams explained

Phishing scams have been around almost as long as email has existed. The first recorded use of the technique was in the mid-1990s, when a group of enterprising hackers posed as AOL employees and used email and instant messaging to steal users’ passwords and account credentials.

For the most part, phishing scams have remained remarkably unsophisticated across the intervening decades. Most phishing attempts are fairly low-effort and pretty easy to discern as scams. However, every now and again, cybercriminals come up with something a little different. This blog covers one such tactic: “note to self” phishing scams.

What do we mean by “note to self”?

Simple, most email providers offer users the ability to send a message to themselves from within their account. This then appears in your inbox as a “note to self”. You’ve probably done this at some point; it’s an incredibly handy way of setting yourself reminders.

However, as we’ll see, cybercriminals have found a way to weaponise this feature.

How do note-to-self phishing scams work?

So, how does a pretty humdrum email feature become a key part of a successful phishing scam?

Well, crucially, you can only send a “note to self” from within the same email account. This is the crux of the scam. 
A cybercriminal spoofs your email address and sends a “note to self” claiming to have breached your account.

They’ll then usually demand some form of ransom, such as cryptocurrency, in exchange for deleting some compromising files, photos or data they claim to have on the victim. There’s usually a strict time limit given for payment, say 48 hours, after which the hacker will threaten to leak this data or email your contact list with it.

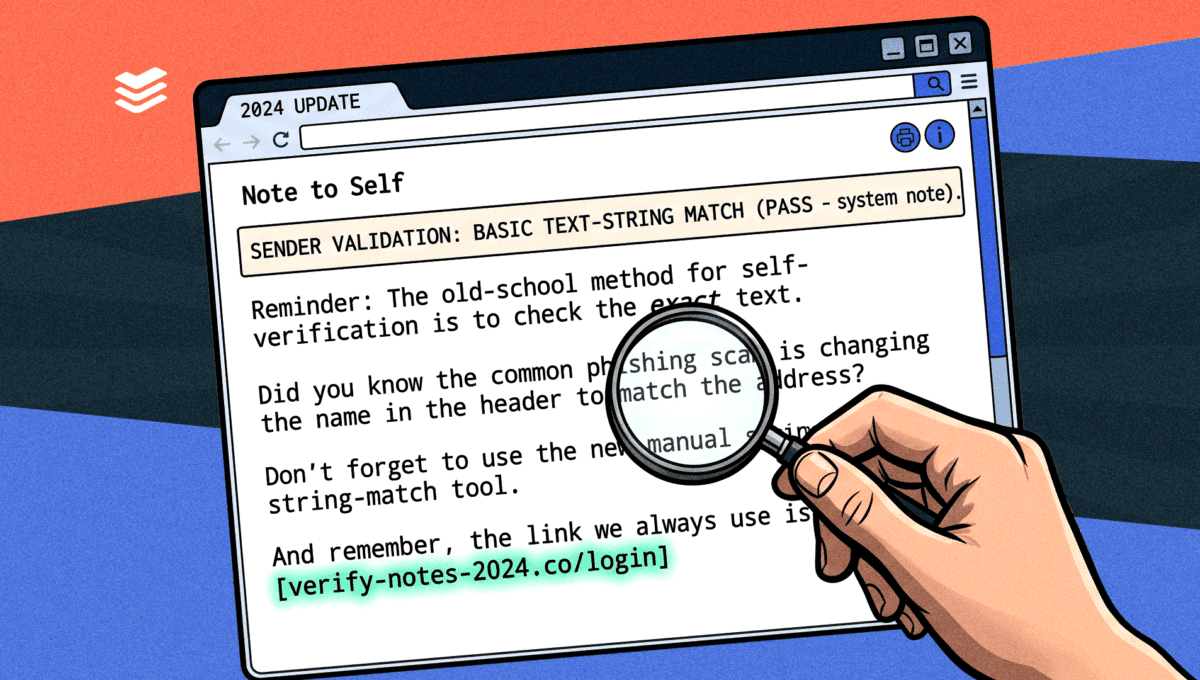
To illustrate, here’s one I made earlier:

But here’s the clever bit: the cybercriminal doesn’t actually have access to your account or any compromising or sensitive data. They just want you to think they do. 

Instead, the hacker has used something called email spoofing to make it appear as though the message has come from inside your account. It hasn’t, but you won’t immediately know that. In fact, you’ll probably panic (don’t worry, I did). And it’s this panic that the cybercriminal is trying to induce, hoping you’ll act before you have time to think about it too much.

What is email spoofing?

Every email contains a header, which is a code snippet that contains important information about the message, including the sender, recipient and tracking data. Unfortunately, hackers have learned how to weaponise this to deceive victims.

Email spoofing is when a cybercriminal uses the header to mask their identity and impersonate a legitimate sender. There are usually two approaches to this, one we’re going to call the ‘sophisticated way’ and another, which is less impressive.

The sophisticated approach

This technique is rarer than the one we’ll discuss next and much more convincing, making it a lot more dangerous. Cybercriminals use a script to forge the fields the recipient can see in the header. In simple terms, this means the email will appear to come from a legitimate sender.

This is possible because the email transmission protocol, Simple Mail Transfer Protocol (SMTP), doesn’t have a built-in method for authenticating email addresses. It also means that these spoofs will evade most email security.

This technique is the one typically used for note-to-self phishing scams, and it’s what makes them so effective.

The more common approach

The less sophisticated email spoofing technique is to register an email domain which is very similar to the legitimate one being impersonated. For example, CEO@m3gacorporation.com rather than CEO@megacorporation.com

You’ll see this approach more often in the wild because it’s easier to achieve and doesn’t require any specialist tools or knowledge. However, it’s generally less effective as it relies on victims not paying attention, meaning it can be pretty easily foiled with just a little thought.

How to spot a note-to-self scam

At this point, you might be wondering how it’s possible to avoid falling for a note-to-self scam. If the spoofed email looks totally legitimate, how are you supposed to tell the difference?

Fortunately, it’s actually very simple. If you receive an email like the one we’ve outlined above, here’s what you should do.

1. Don’t panic

As we mentioned earlier, if you receive a note-to-self phishing email, your first instinct is probably going to be panic. It’s often easier said than done, but try not to. Take a deep breath and don’t do anything drastic or click on any link until you’ve worked through the next few items on the list. 

If it’s helpful, you can use the “Stop, Look, Think” anti-phishing technique. Remember, cybercriminals rely on creating a sense of urgency to get you to act before thinking critically. After all, it’s one of the most common and effective social engineering techniques in existence.

Don’t fall for it. Tell yourself that nine times out of ten, this is a phishing scam, not a real compromise of your email account.

2. Check the sender's email address

Next, check the sender’s email address. Does the email really match your own, or are there subtle differences? If the attacker has used a less sophisticated spoofing technique, this is where they’ll give themselves away as phoney.

3. Check your sent folder

If the email address appears identical to yours, it’s probably a more sophisticated spoof. However, there's still an easy way to tell if your email account has really been breached.

As the name suggests, “note to self” emails can only be sent from inside the account, so check your sent emails. If the email doesn’t appear there, then it hasn’t been sent from your account, meaning it’s a phishing scam.

4. Check the IP address of the sender

You shouldn’t need to do this, but if you want some extra peace of mind, check the sender's IP address. If the message had really been sent from inside your account, the IP address would match the one associated with your email.

To find the IP address associated with an email, you need to analyse the email header, specifically the "Received:" lines.

To do this in Gmail, open the email, click the three vertical dots, and select "Show Original" or "View original message". 

In Outlook, open the email, go to File > Properties, and look at the Internet headers. 

You can also use tools like WhatIsMyIP.com to check email headers. Although it’s worth noting that if you use a virtual private network (VPN), this step won’t work. This is because VPNs create a fake or proxy IP address to mask your internet identity.

5. Delete the email and move on with your day

Once you’re confident that the message is a phishing scam, flag it as spam to your email provider.  After this, there’s nothing left to do but delete it and move on with your day.

Want to know more about how to protect your business from phishing scams? Check out CyberSmart Learn, our cybersecurity-focused learning management system.

Protecting patient data – cybersecurity training for healthcare providers

Patient health records are a gold mine for cybercriminals. Just one record sells for up to £1,000 on the dark web compared to £5 for credit card details. Worse still, breaches of healthcare providers are becoming ever more common. In the past five years, 8903 incidents have been reported to the Information Commissioners Office. And, according to research from Kroll, healthcare was the most targeted sector in 2024 (accounting for nearly a quarter of all breaches).

However, there is a simple, often overlooked, thing you can do to better protect your hospital, surgery or business. 95% of breaches stem from some kind of human error, whether that's clicking on a phishing link or replying to the wrong email. So, one of the best things you can do for your organisation's cyber health is to invest in cybersecurity training.

The benefits of cybersecurity training for healthcare providers

Cybersecurity training equips your team to make better security decisions every day. From checking emails to managing passwords, every action carries potential risk. Without proper training, these become vulnerabilities.

Training strengthens your cyber health in several ways.

Compliance

Healthcare companies must comply with strict regulatory requirements under GDPR, the Data Protection Act 2018, and sector-specific frameworks like the NHS Data Security and Protection Toolkit. Proper training ensures your team understands their role in maintaining compliance.

Protecting sensitive data

Train your team how to handle data properly, so they’re always security conscious, whether they’re sharing test results or updating records. This naturally creates a barrier against unauthorised access and maintains efficiency.

Continuity of care

When systems go offline during a cyberattack, patient care suffers. Appointments get cancelled, test results are inaccessible, and treatment plans are delayed. Training helps prevent these disruptions and prepares your team to maintain essential services during security incidents.

Reputation management

Patient trust takes years to build but can disappear overnight after a data breach. Effective training minimises this risk and ensures your team can respond appropriately if an incident occurs.

Improving your cyber health – six areas for cybersecurity training for healthcare

1. Phishing awareness training

Phishing initiates 91% of all cyberattacks, with healthcare staff facing sophisticated scams designed for medical contexts. Recent examples include fake COVID-19 vaccine scheduling emails and fabricated patient record requests.

Training priorities:

  • Run simulated phishing exercises using healthcare-specific scenarios
  • Teach staff to spot indicators of fraudulent communications
  • Establish clear reporting channels for suspicious messages
  • Reinforce that legitimate organisations never request passwords via email

2. Password and authentication security

Strong authentication is crucial. Credential theft enables 61% of healthcare breaches, but proper authentication practices can block most of these attempts.

Training priorities:

  • Teach password management suitable for clinical environments
  • Implement and train staff to use password managers
  • Implement multi-factor authentication (MFA)
  • Ensure staff understand why MFA matters
  • Introduce protocols for password resets in emergencies

3. Device and endpoint security

Healthcare workers use multiple devices across various locations, and every device is a potential entry point for attackers.

Training priorities:

  • Develop clear guidelines for practice-owned and personal devices
  • Establish practical BYOD protocols for healthcare workflows
  • Schedule device updates that don't interrupt patient care

4. Incident response

Clear protocols for security incidents alongside fast response times can significantly limit damage and disruption.

Training priorities:

  • Develop streamlined incident response procedures to maintain patient care
  • Clarify what constitutes a reportable security incident
  • Establish clear communication channels during security events
  • Practice incident scenarios regularly with realistic, relevant examples

5. Network security basics

Your network is crucial for seamless communication, data sharing, and patient care, but it also expands your attack surface. A single network vulnerability can expose your entire organisation to breaches.

Training priorities:

  • Secure network access, particularly for remote access
  • Teach staff to recognise warning signs of network intrusions
  • Establish protocols for connecting medical devices to networks
  • Provide guidance on secure application use

6. Social engineering awareness

Healthcare faces unique social engineering risks, including imposters posing as patients, pharmaceutical representatives, or officials.

Training priorities:

  • Develop verification procedures that maintain patient privacy
  • Ensure identity protocols are followed before granting access
  • Train reception staff on handling unusual information requests

Delivering cybersecurity training in healthcare

The way you deliver training directly impacts its effectiveness. Here's how to ensure your investment pays off:

Delivering cybersecurity training in healthcare

The way you deliver training directly impacts its effectiveness. Here's how to ensure your investment pays off:

Keep sessions short

Micro-learning sessions are easier to digest and schedule than lengthy sessions. Keep modules short and focused to help information retention.

Make it relevant

Avoid generic training. Use scenarios relevant to your people, like updating patient records, using appointment systems, and sharing treatment plans. This demonstrates how security applies to them and their daily activities.

Focus on practical actions

Busy healthcare professionals need actionable guidance, not theory. Focus on specific behaviours that improve security without disrupting patient care.

Test and reinforce

Regular simulations, knowledge checks, and refreshers maintain vigilance. Consider healthcare-specific phishing simulations and exercises based on real incidents.

Build a supportive culture

Move beyond compliance to foster a culture where security enhances patient care. Recognise staff who report suspicious activity, and ensure leadership demonstrates security best practices.

Launching your healthcare cybersecurity training

Here’s how you can prepare for training:

  1. Assess your current situation by examining your unique workflows, systems, and previous security concerns
  2. Survey your staff to identify knowledge gaps and existing strengths
  3. Review security incidents that have affected similar healthcare organisations

Consult specialist frameworks like NHS Digital's Data Security and Protection Toolkit

Based on this assessment, develop a focused training plan – either on your own or with a training provider – that addresses your highest-priority risks first with comprehensive coverage over time.

Building a security-first culture

Effective cybersecurity training for healthcare providers doesn't require massive budgets. Focus on healthcare-specific skills and integrate security habits into daily workflows that staff already understand.

Considering introducing cybersecurity awareness training into your business? Check out CyberSmart Learn, our cybersecurity focused learning management system.

DSIT’s Cyber Governance Code of Practice explained

If we’ve learned anything from the recent news cycle, it’s that large UK businesses need help. Attacks on M&S, The Co-op, and Harrods have left the country reeling and cybersecurity back at the top of the agenda. So, the release of the Department for Science, Innovation & Technology’s Cyber Governance Code of Practice for medium and large businesses feels timely.

But what is it? And should smaller businesses adopt its recommendations too? We answer these questions and more in this blog.

What is the Cyber Governance Code of Practice?

The Cyber Governance Code of Practice is a framework designed to guide boards and directors on effectively governing cyber risks. Primarily aimed at medium and large organisations, it aims to help business leaders build resilience within their organisations and defend against a wide range of cyber threats.

What does the code include?

Broadly speaking, the code sets out critical governance principles that every board (or director) should apply to their organisation. Think of it as a set of cybersecurity ‘dos’ for people in positions of authority.

More specifically, the code focuses on five fundamental principles. Much like Cyber Essentials and its five controls, these principles cover the key bases of effective cybersecurity. These principles are:

  • Risk management
  • Cyber strategy
  • People (cyber-aware culture and training)
  • Incident planning and response
  • Assurance and oversight

Each principle is supported by a set of three to five actions directors are advised to take. For example, one of the actions for People is to “Undertake training to improve your own cyber literacy.” These actions help directors and business leaders gradually build cyber confidence throughout their organisation and, ultimately, better secure it against cyber threats.

How does it integrate with other frameworks?

The Code complements other resources like the National Cyber Security Centre’s (NCSC) Cyber Security Toolkit for Boards and the Cyber Assessment Framework (CAF).

Alongside this, the code is bolstered by free cyber governance training and a cybersecurity toolkit to help boards implement its recommendations.

Is the code voluntary?

While voluntary, the Code is positioned as the minimum level of board accountability expected within UK businesses. Plus, it likely won’t be voluntary for long. The upcoming Cyber Security and Resilience Bill is widely expected to reinforce these standards and possibly even create some form of legal responsibility for boards. 

In other words, it’s well worth getting ahead of the legislation by adopting these measures now.

Why has the code been created?

Time for a brief history lesson. The code was co-designed by the NCSC and industry experts to address two things. Firstly, as we’ve seen illustrated by the attacks on some of the UK’s flagship retailers in the last few weeks, there’s a high prevalence of cyber incidents among large businesses. According to DSIT’s latest research, some 74% of large and 67% of medium-sized organisations reported cyber incidents in the past year.

Secondly, board-level responsibility for cybersecurity has seen a gradual decline since its high of 38% of UK organisations in 2021 (the figure is 25% in 2025). The code aims to put managing cyber risk back at the front and centre of boards’ thinking and give senior leaders a clear framework for how to do it.

More broadly, the frameworks fit with upcoming legislation to form a key part of the UK government's approach to improving national cyber resilience.

Who is the code for?

We mentioned earlier that the Cyber Governance Code of Practice was primarily aimed at medium to large businesses. This is because larger businesses typically have a formalised board and governance structures.

However, you shouldn’t take away the message that the framework isn’t useful if you’re a small business. Most obviously, because small businesses often do have boards or, at the very least, directors. More importantly, the framework has value for any organisation.

Regardless of your organisation’s size, adopting its recommendations will help you bolster your defences, mitigate risks, and gain cyber confidence.

Want a simple solution for meeting the Cyber Governance Code of Practice's staff training recommendation? Check out CyberSmart Learn.

From vulnerability to vigilance: developing your cybersecurity awareness and training policy

No matter how robust your technical defences are, your company’s cybersecurity is only as strong as your least cyber-savvy employee. One careless click, one reused password or one small mistake can have significant consequences.

That’s why a cybersecurity awareness and training policy is so important.

What is a cybersecurity awareness and training policy?

A cybersecurity awareness and training policy is a formal document that outlines how your business approaches cybersecurity education. 

It defines: 

  • The type of training employees receive
  • How often they receive it
  • What's expected of them

Unlike a general security policy focusing on technical controls, a security awareness and training policy specifically addresses the human element of cybersecurity. It ensures your team has the knowledge and skills to appropriately identify and respond to threats.

Why you need a cybersecurity awareness and training policy

It’s easy to overlook the importance of formalising your approach to cybersecurity awareness training. Here’s why implementing a comprehensive policy is so important: 

  • Human error is your biggest vulnerability
  • Regulatory compliance requires it
  • It reduces your cyber insurance premium

Human error is your biggest vulnerability

50% of UK businesses have a basic cybersecurity skills gap, meaning staff lack confidence in performing fundamental security tasks like storing personal data securely or detecting malware. Given that human error accounts for most breaches, you don't want to be in the 50% of businesses with a skills gap.

It can help with regulatory compliance

While it's not explicitly required, many industry regulations and standards – including GDPR Cyber Essentials, and ISO 27001 – strongly recommend security awareness training.

It could reduce your cyber insurance premiums

Insurance providers often look more favourably on businesses with formal security awareness programmes, which can result in lower premiums.

What to include in your cybersecurity awareness and training policy

Creating an effective cybersecurity awareness and training policy isn’t complicated. Here are the essential elements to include:

1. Training modules and content

Your policy should clearly outline the topics your training programme covers. 

Here are some common weaknesses to address:

  • Password protection: best practices for creating and managing strong passwords
  • Phishing awareness: how to identify and report suspicious emails
  • Multi-factor authentication (MFA): why it's important and how to use it properly
  • Safe internet usage: guidelines for browsing safely and avoiding malicious websites
  • Data handling: procedures for handling sensitive information
  • Mobile device security: how to secure work phones and manage bring your own device (BYOD) risks 
  • Incident response and recovery: what to do when something goes wrong

2. Training frequency

Your cybersecurity awareness and training policy must specify how often employees receive training. 

Consider:

  • Initial training for new employees during onboarding
  • Annual refresher courses for all staff
  • Quarterly micro-learning sessions (10-15 minutes) on specific topics
  • Ad-hoc training when new threats emerge or after security incidents

3. Delivery methods

Not all training is created equal. Your policy should outline how training will maximise engagement and retention. 

  • Interactive e-learning: self-paced modules that employees can complete at their convenience
  • Simulated phishing exercises: practical tests that reinforce email security awareness
  • Workshop sessions: team-based exercises that encourage discussion and problem-solving
  • Video content: short, engaging videos that explain key concepts
  • Infographics and visual aids: quick-reference guides for common security scenarios

4. Assessment criteria

Your security awareness and training policy needs clear metrics to measure success, such as: 

  • Knowledge checks: share quizzes and tests to measure understanding
  • Phishing simulation results: track click rates on simulated phishing emails
  • Incident reporting: monitor the number and severity of security incidents reported
  • Compliance rates: track training completion rates 

Behavioural changes: observe improvements in security practices

Making your security awareness and training policy work for you

The most effective policy is one you actually implement. Follow these practical tips.

Make it relevant

Use examples directly related to your business instead of abstract concepts your team won’t be able to follow.

Bridge the knowledge gap

Address the disconnect between technical teams and leadership. 35% of cybersecurity leads say senior managers don't understand the cyber risks facing their organisation.

Lead by example

Ensure management follows security practices – when leaders demonstrate good security habits, teams are more likely to follow suit.

Keep it current

Review and update your policy at least once a year.

Achieve your personnel best

A well-structured cybersecurity awareness and training policy strengthens your business from within. Clear guidance, ongoing education, and practical training puts the power in the hands of your people.

Considering introducing cybersecurity awareness training into your business? Check out CyberSmart Learn, our cybersecurity focused learning management system.
Dodging the phishing net – why phishing awareness training matters

We've all received those suspicious emails asking us to "verify" our account details or claiming we've won an improbable prize. While some attempts appear comically obvious, others are sophisticated enough to trick even the most vigilant employees.

So much so, that 91% of all cyberattacks begin with a phishing email. 

The good news? With the right training, your team can become your strongest line of defence.

What is phishing awareness training?

Phishing awareness training teaches employees how to identify and respond to phishing attempts. It covers everything from recognising suspicious emails and text messages to understanding the psychological tactics cybercriminals use to manipulate recipients.

Unlike technical security measures, like firewalls, that work silently in the background, phishing awareness training actively engages your team. Over several sessions, it transforms them from potential vulnerabilities into valuable protectors of your company's digital assets.

How does phishing awareness training work?

Effective phishing awareness training is an ongoing commitment. It typically includes:

  • Educational content – Interactive modules, videos, and reading materials that explain phishing tactics and prevention strategies
  • Simulated attacks – Controlled phishing simulations test employee vigilance in real-world scenarios
  • Regular updates – Training content that evolves as new phishing techniques emerge
  • Performance tracking – Individual and team metrics that measure improvement, helping you identify employees who might need additional support

The best training combines these elements into a cohesive learning experience that builds confidence and vigilance.

What are phishing attack simulators, and why do you need them?

Phishing simulators test your employees with realistic but harmless phishing attempts. They help your team develop an instinct for spotting hooks in seemingly innocent messages.

These simulators:

  • Create realistic phishing scenarios tailored to your industry
  • Track who ‘takes the bait’ by clicking links or submitting information
  • Provide immediate feedback and educational resources
  • Generate reports to measure improvement over time

Businesses of all sizes benefit from simulators. For smaller organisations especially, where a single security incident could have devastating consequences, these tools provide cost-effective training that turns theoretical knowledge into practical skills.

Why is phishing awareness training important?

1. It strengthens your defences

When your team knows what to look for, they’re more likely to spot suspicious communications. This proactive approach prevents successful attacks before they happen.

With proper training, employees learn to scrutinise:

  • Sender details and email domains
  • Unusual requests or urgent language
  • Suspicious links and attachments
  • Grammatical errors and inconsistent formatting

2. It minimises human error

We're all human, and humans make mistakes. A momentary lapse in judgement, a hurried click, or simple curiosity can have devastating consequences.

Research shows that human error causes 85% of cyber breaches. Phishing awareness training addresses both skills-based errors (not knowing how to identify threats) and decision-based errors (when security protocols are unintentionally bypassed).

By building knowledge and good habits, you turn potential weak points into security strengths. And with the right tools, you can track employee progress, set training deadlines, and ensure your team stays up to date with the latest threats. CyberSmart Learn, for instance, offers customisable training reports that help you identify knowledge gaps and measure improvement over time.

3. It aids compliance

Beyond the practical security benefits, phishing awareness training helps meet regulatory requirements. Many compliance frameworks – including GDPR, HIPAA, and SOC 2 – specifically require security awareness training.

Even in industries without explicit requirements, documented training programmes demonstrate due diligence and can:

  • Reduce liability in case of a breach
  • Lower cyber insurance premiums
  • Reassure customers and partners about your security posture

Outsmarting phishers

Phishing attacks succeed because they exploit human psychology. While firewalls and antivirus software are essential, they can't protect against an employee accidentally compromising sensitive information.

By investing in phishing awareness training, your team can become the most effective countermeasure in your arsenal against cybercrime.

Considering phishing awareness training for your business? CyberSmart Phish allows your business to run tailored phishing simulations, educate employees in real time, and track behavioural insights. And, it's included as part of CyberSmart Learn our cybersecurity awareness training platform, designed for small businesses and managed service providers.

Beyond digital defences: what is a human firewall in cybersecurity?

Firewalls, antivirus software, and intrusion detection systems are all essential components of a strong cybersecurity strategy. But what if the most effective defence against cyber threats isn’t digital at all?

What if you had a human firewall? A security layer built from awareness, vigilance, and smart decision-making, not code.

Understanding the human firewall

If you’re wondering, “What is a human firewall in cybersecurity?”, it’s simply employees who actively follow cybersecurity best practices. 

Just like a traditional firewall that blocks malicious traffic, a human firewall prevents cyber threats by identifying suspicious activity, avoiding social engineering attacks, and adhering to security policies.

Why you need a human firewall

Cyber threats that target people, not systems, are increasing. In fact, 42% of organisations experienced a successful social engineering attack in the past year. 

Hackers exploit basic human nature like wanting to be helpful, responding to authority, and acting quickly under pressure. 

Common social engineering threats include: 

These tactics are markedly more convincing with the rise of AI. Where suspicious emails once contained obvious spelling errors or unusual phrasing, AI-generated content now appears more polished and professional. Voice cloning can mimic your CEO on the phone, and deepfakes create convincing video impersonations of colleagues, meaning it's now easier than ever to fool people.

The benefits of a strong human firewall

When you have a strong human firewall, the advantages extend far beyond just withstanding breaches, they include: 

  • Faster threat detection 
  • Improved customer confidence 
  • Streamlined regulatory compliance 
  • Enhanced business resilience

Faster threat detection

Employees who know what to look for spot unusual or suspicious activities faster. This significantly cuts the average lifecycle of cyberattacks, reducing their impact.

Improved customer confidence

When clients know your team follows best practice, trust grows. 83% of consumers remain loyal to businesses they believe handle their data responsibly.

Streamlined regulatory compliance

Meeting GDPR and other regulatory requirements is easier when your whole team understands their data protection responsibilities, helping you avoid hefty fines.

Enhanced business resilience

Operations bounce back faster after security incidents when teams know exactly what to do. Businesses with well-trained employees recover faster, minimising downtime and financial losses.

How to build a human firewall in cybersecurity

Building a human firewall in cybersecurity happens step by step – or should we say brick by brick?

1. Conduct regular cybersecurity training

Regular cybersecurity training programmes educate your team on the latest threats, attack techniques, and prevention methods.

2. Establish a clear cybersecurity policy

Share a cybersecurity policy that outlines best practices, acceptable use of company resources, and protocols for reporting security incidents. Ensure your team reviews these policies regularly to stay in the loop.

3. Encourage a security-first culture

Create a culture where you recognise and reward employees for proactive security behaviours.

4. Implement access controls

Limit access to sensitive data based on job roles. This ensures your team can only access information that’s necessary for their work.

5. Run simulations

Simulate social engineering attacks to spot-check your team’s understanding and see how they perform under pressure.

6. Enforce strong authentication practices

Use multi-factor authentication (MFA) and enforce strong password hygiene.

Put your people at the centre of your cybersecurity

Effective cybersecurity has less to do with your tech and more to do with your team. Building a strong human firewall means fostering a culture of shared responsibility, where every individual plays an important role in protecting your business from potential threats.

Considering introducing cybersecurity awareness training into your business? Check out CyberSmart Learn, our cybersecurity focused learning management system.
8 key takeaways from DSIT’s Cyber Security Breaches Survey 2025

Spring has sprung, and Easter has just passed. That can only mean one thing: the Department for Science, Innovation & Technology’s (DSIT) Cyber Security Breaches Survey 2025 has arrived.

If you’re unfamiliar with it, the annual report acts as a barometer of the UK’s cyber resilience. It outlines what UK organisations are doing to protect themselves, levels of cyber knowledge, common threats, the costs of breaches, and much more besides. However, it is also a very long report. So, as in previous years, we’ve pulled together the key takeaways for you.

1. Cyber breaches fall 

Let’s begin with some good news. Just over four in ten businesses (43%) and around a third of charities (30%) reported having experienced any kind of cybersecurity breach or attack in the last 12 months. This works out at around 612,000 businesses and 61,000 charities.

This represents a fall from the 2024 edition, where 50% (or 718,000) of businesses experienced a breach or attack. The figures are still higher than 2022 (39%), but it’s the first time in a few years that we’ve seen a decline rather than an increase.

The decrease is primarily driven by fewer micro and small businesses identifying phishing attacks (35% of micro businesses down from 40% in 2024 and 42% of small businesses down from 49% in 2024). However, breaches in medium and large businesses remain very high (67% medium and 74% large) with little change from 2024.

It’s hard to know what to make of this. On the one hand, it’s entirely possible that SMEs are simply bothering to report phishing attacks less often (as they’re so common), rather than a real decline in attacks. But, on the other hand, it could be an early indication that cybercriminals have redoubled their attacks on larger businesses.

2. Phishing remains the most common (and disruptive) cyber threat

Phishing scams have been by far the most common cyber threat faced by UK organisations for several years now. Unsurprisingly, 2025 is no different. 85% of businesses and 86% of charities experienced at least one phishing attack in the last year.

Phishing scams are seen by organisations as the most disruptive because of the time needed to investigate and address them, due to the sheer volume of attacks. And, more interestingly, because most businesses recognised the importance of employee training to combat the threat.

The interviews cited in the report also reveal that businesses of all sizes are increasingly worried about the growing sophistication of phishing attacks. In particular, many organisations mentioned AI impersonation as a threat they felt fearful of.

3. Ransomware attacks on the rise?

DSIT reports a significant growth in ransomware incidents in the last year. Just over 1% of businesses experienced an attack, compared to less than 0.5% in the 2024 edition of the survey. What’s interesting is that, despite the increase in ransomware attacks, several sources are reporting a global decline in the prevalence of ransomware payments.

For example, CyberEdge Group’s 2025 Cyberthreat Defense Report reveals that only 41% of targeted organisations chose to pay out last year, a drastic fall from 63% three years ago. Likewise, the Data Security Incident Response Report from US law firm Baker-Hostetle suggests fewer attacks and lower ransom payments than in previous years.

Could we be seeing the last days of ransomware’s prevalence as a cybercrime tactic, as more and more organisations refuse to pay and governments (including the UK) actively discourage it?

4. Small businesses get serious about supply chains

Although the proportion of businesses conducting supplier risk assessments (29%) has remained relatively flat (31% in 2024), we’ve seen a significant increase among SMEs.48% of small businesses carried out a risk assessment covering cybersecurity, up 7% from 2024. While, in an ideal world, the figure could be higher, this represents real progress in small businesses’ awareness of supply chain threats.

5. Small businesses’ cyber hygiene is improving

Most encouragingly, there’s evidence of real improvements in the cyber readiness and hygiene of the UK’s small businesses. All of the following areas saw significant increases in this year’s survey: 

  • Cyber security risk assessments (48%, up from 41%)
  • Cyber insurance coverage (62%, up from 49%)
  • Formal cyber security policies (59%, up from 51%)
  • Business continuity plans addressing cyber risks (53%, up from 44%)

This appears to indicate a real sea change in small businesses’ perceptions of cyber risk and what they need to do to manage it. In previous years, small businesses have typically been weak on measures like cyber insurance and formal policies and continuity plans. However, these figures demonstrate that SMEs are beginning to take cybersecurity much more seriously.

6. The financial impact of cyber breaches increases

Although it’s not a marked change, the average total cost of a business’s most disruptive breach increased this year. Among those businesses that were breached but with no outcome, the figure for this year is £1,600 (up from £1,205 in 2024). 

It’s a similar, if slightly more expensive, story for those businesses that experienced a breach with an outcome. For these businesses, the average cost was £8,260, up from £6,940 last year. 

It’s hard to gauge exactly what’s behind this rise. The costs are self-reported, so it’s possible that they’re within the normal range of difference we’d expect to see year-to-year. However, it’s also possible that it demonstrates a larger trend of breaches growing more disruptive.

7. Most businesses have the basics in place

Another real point of encouragement in this year’s survey is the widespread adoption of basic technical controls. Most businesses and charities have implemented basic cyber controls, including:

  • Network firewalls (72% of businesses and 49% of charities)
  • Backing up data securely via a cloud service (71% of businesses and 58% of charities) 
  • Restricted admin rights (68% of businesses and 68% of charities)
  • Updated malware protection (77% of businesses and 64% of charities)
  • Password policies (73% of businesses and 57% of charities)

However, there’s definitely room for improvement. The adoption of more advanced controls like multi-factor authentication (40% of businesses and 35% of charities), a virtual private network for staff connecting remotely (31% of businesses and 20% of charities), and user monitoring (30% of businesses and 31% of charities) remains low.

Likewise, although cybersecurity training and awareness activities are pretty widespread in large businesses (76%), few medium, small and micro businesses are offering it to staff. Just 19% of all businesses have some sort of training or awareness programme in place.

8. Governance and certifications are a mixed bag

The good news is that cybersecurity is a high priority for the majority of organisations (72% of businesses, 68% of charities), much the same as in previous years. However, a trend is emerging in who is responsible for cybersecurity. Board-level responsibility for cybersecurity seems to be on a gradual decline since its high of 38% of organisations in 2021 (it’s 27% in 2025).

This could mean that organisations are increasingly hiring specialists to manage security. Alternatively,  it could be that boards are increasingly delegating the responsibility to subordinates who’ve gained greater cyber knowledge. At this point, we don’t know for sure, but it’s certainly a trend worth watching.

Finally, while businesses appear to be prioritising cybersecurity like never before, awareness of NCSC campaigns and accreditations like Cyber Essentials is declining.

For example, the NCSC’s Cyber Aware Campaign has declined from 2021(when 34% of businesses and 38% of charities were aware of it). Likewise, just 12% of businesses and 15% of charities are aware of Cyber Essentials.

What can we do in 2025?

It’s clear that, while there are plenty of positives to take from this year’s Cyber Security and Breaches Survey, we in the cybersecurity community have some work to do. So, what should we prioritise in 2025? Here are our suggestions for Managed Service Providers, resellers, cybersecurity specialists or anyone involved in the sector

  • Enhance our outreach and education for micro and small businesses, in particular, focusing on the importance of phishing awareness, security training, and advanced technical controls like MFA
  • Develop our own solutions and threat awareness resources to counter the rise of malicious AI use
  • Encourage organisations to formalise cybersecurity responsibilities at the board level
  • Promote the integration of cyber risk considerations in software procurement
  • Highlight the importance and accessibility of Cyber Essentials and government guidelines to improve baseline cybersecurity practices

Did you know 59% of SMEs provide no mobile cybersecurity training to staff? Find out why this is a problem and what to do about it in our SME Mobile Threat Report.


The importance of cybersecurity awareness training for employees

The cybersecurity skills gap doesn’t just affect large corporations. With 58% of organisations citing insufficient skills as the primary cause of breaches, cybersecurity awareness training is essential for businesses of all sizes.

What is cybersecurity awareness training?

Cybersecurity awareness training equips your employees with the knowledge and skills to identify, avoid, and respond to cyber threats. It covers everything from identifying phishing attempts to understanding password hygiene and safe device usage.

Unlike technical security measures that work in the background, awareness training directly empowers your team to make security-conscious decisions.

Your business runs on data – customer information, intellectual property, financial records, and operational details. The consequences of neglecting this data are far from virtual. 

Why is cybersecurity awareness training important?

Protects sensitive data

A data breach compromises more than just information, it severely impacts customer trust. Among businesses that have experienced a cyber-attack, 47% report greater difficulty attracting new customers, while 43% say they've lost existing customers entirely.

Cybersecurity awareness training teaches employees to recognise which information is sensitive, how to handle it safely, and identify unsafe practices that could put your business at risk.

Minimises human error

Human error accounts for a staggering 85% of cyber breaches. From clicking malicious links to using weak passwords or falling for social engineering tactics, simple mistakes can have catastrophic consequences.

Training significantly reduces these errors by building security awareness into everyday activities. When employees recognise threat patterns, understand the importance of security protocols, and develop good security habits, they go from your biggest vulnerability to your greatest defence.

Improves incident response

Even with the best preventative measures, security incidents still occur. When they do, the speed and effectiveness of your response is key to reducing the damage.

Formal incident response plans aren't as common as they should be. 36% of medium and large organisations don’t have a one. This is alarming, considering that quick action minimises "dwell time" – the period when cybercriminals have free access to your systems.

Cybersecurity awareness training provides employees with clear steps to follow when they spot something suspicious, reducing the window of opportunity for hackers to cause harm.

Helps you comply with regulations

Regulatory compliance isn't optional, and non-compliance can result in severe penalties. GDPR infringements, for example, could cost your business up to €20 million (around £18 million) or 4% of global annual revenue, whichever is higher. 

Effective training ensures your team understands their responsibilities under these regulations and how to meet them.

Secures the remote workforce

Remote work has created new security challenges that traditional office-based defences can't address. When employees work from home, public venues, or on the move, your security perimeter extends to every location and device they use.

Threats include: 

  • Unsecured home networks that lack enterprise-grade protection
  • Unauthorised usage of personal devices for work purposes
  • Public Wi-Fi vulnerabilities that expose sensitive data 

Cybersecurity awareness training tailored to remote work scenarios helps employees recognise these risks and mitigate them. It ensures your security travels with your team, whether they're working from the kitchen table or a beachside café.

Should I get a cybersecurity certification?

Alongside training, certifications are a great way to take your security posture to the next level. Cyber Essentials provides a framework to improve your overall security and demonstrate your commitment to protecting data.

A certification helps you:

  • Show customers and partners that you take security seriously
  • Meet compliance requirements
  • Follow proven security frameworks rather than ad-hoc approaches
  • Win new business, such as government contracts and private sector opportunities, which require certification

Build a culture of cybersecurity awareness

The importance of cybersecurity awareness training for employees can’t be overstated. When security becomes part of your company's culture, employees naturally bring it into their daily routines and decision-making. And ultimately, this is what reduces cyber risk, and improves cyber resilience.

Considering introducing cybersecurity awareness training into your business? Check out CyberSmart Learn, our cybersecurity focused learning management system.