You asked, and we listened. After being one of our most requested features from partners, we’re delighted to announce the general availability of our Ticketing API to help you automate security workflows effortlessly.
Here’s everything you need to know.
What is it?
Our Ticketing API now offers full access to certifications and desktop security controls, providing deeper integration and flexibility for your customers’ security needs. Whether you want to automate workflows, integrate with other systems, or customise your offerings, our API gives you the tools to do so.
Who is it available to?
All CyberSmart Partners, no matter your tier. Our Ticketing API isn’t currently available to direct customers.
How do you set it up?
Although our Ticketing API offers powerful features, it’s worth noting that it’s not a plug-and-play solution. You’ll require developer expertise to set it up and take advantage of its full functionality.
We’ve prepared some resources to help your team get started, including:
A step-by-step guide to setting up our ticketing API, which you can find here
We recommend sharing these resources with your developers as soon as they begin the implementation process.
What’s next?
We understand that this current rollout is quite technical, and we’re aware that not all partners may be ready to dive in immediately. While this is the first phase, we’re committed to improving and expanding the functionality in the future.
However, for the moment, this is full scope of our Ticketing API release. Rest assured we’ll keep you updated as we work on future enhancements.
We’re excited to see how you use the Ticketing API to unlock new possibilities for your customers. Please reach out with any questions or feedback, and thank you for being a valued partner.
10 mobile device security best practices every business should follow
Whether it’s replying to emails during your morning commute or logging into Slack while you enjoy a well-earned break, mobile devices have become indispensable to how we work. Laptops, smartphones, and tablets let us communicate and collaborate from anywhere with a reliable internet connection. This flexibility allows us to be just as productive on the move as we are in the office.
As with any innovation, there are drawbacks. Mobile devices are a gateway to sensitive corporate information and confidential client files, making them an extremely tempting target for hackers. So, it’s essential you have robust security measures in place to protect your data.
With that in mind, here are ten mobile device security best practices every business should implement.
Strengthen your defences with these mobile device security best practices
1. Create a mobile usage policy
A mobile usage policy establishes clear guidelines on how to use company-owned and personal devices safely. It outlines the security requirements staff must follow as well as the consequences for non-compliance.
Implementing a policy in your business ensures everyone follows the same standards and procedures, increasing your resilience to cyber threats.
Biometric authentication makes it harder for unauthorised users to access mobile devices. It replaces traditional verification methods, like passwords or personal identification numbers (PINs), with unique biomarkers – typically a fingerprint or face scan. These are difficult to crack without advanced technology, which means they’re more secure than simple six-digit PINs.
3. Encourage multi-factor authentication
Even the strongest passwords are crackable with enough time and the right tools. That’s why mobile device security best practice recommends activating multi-factor authentication (MFA) on all employee devices.
MFA is a security measure that requires two or more verification methods to access accounts, applications, or systems. This can be any combination of passwords, PINs, one-time codes, biometrics, or other reliable forms of authentication. It’s much harder for cybercriminals to break through multiple layers of security, which increases your protection against unauthorised access.
4. Encrypt devices
Encryption converts device data into unreadable code you need a key to access, keeping it safe from prying eyes. Most devices come with some form of built-in encryption. For example, Google encrypts all Pixel phones by default.
For added protection, consider investing in a mobile encryption app. These tools offer advanced security features such as hybrid encryption, secure messaging, and periodic code audits.
5. Stay on top of updates
Apple, Google, and Microsoft release security patches regularly to safeguard mobile devices against vulnerabilities. Install these updates as soon as they become available, or turn on automatic updates to ensure device security is always up to date.
6. Restrict app downloads
Unregulated, third-party app stores are breeding grounds for mobile malware and other cyber threats. To reduce your exposure, restrict app downloads to reputable sources. For example, the Apple App Store or Google Play.
It’s also sensible to review an app’s access permissions before installation and adapt them accordingly (if possible) to protect sensitive information.
7. Use a VPN
A virtual private network (VPN) masks your IP address and encrypts your internet connection, making it harder for cybercriminals to monitor your activity and intercept sensitive data.
VPNs are essential when using public Wi-Fi networks, which offer little to no protection against hackers. Just remember that even the most advanced VPNs can’t make public networks entirely secure. As such, mobile device security best practices recommend avoiding unsecured networks unless absolutely necessary.
8. Back up critical data
Data backups are a crucial failsafe that enable you to recover important files quickly if a device is lost or stolen. For added peace of mind, follow the 3-2-1 rule. This recommends creating three copies of sensitive data on two different media, with one of them stored off-site.
Popular storage media include external hard drives, network-attached storage devices, and cloud storage platforms.
9. Run regular cybersecurity training
According to Verizon, 68% of data breaches involve a non-malicious human element. This covers everything from leaving a mobile device unattended in public places to falling victim to a phishing attack. Although it’s impossible to eliminate these risks entirely, educating staff in mobile device security best practices goes a long way to protecting your business.
10. Establish an incident response plan
No device is 100% immune to cyber threats. The important thing is how you react should the worst happen.
A clear and comprehensive incident response plan helps you contain device breaches and get back to business as usual faster. Additionally, employees feel more confident responding to cyber threats and feel more comfortable reporting them, helping you spot threats earlier.
(Best) practice makes perfect
In the face of increasingly sophisticated cyber threats, mobile security is no longer optional. Following these mobile device security best practices help you lay a solid foundation for your cybersecurity. Deployed alongside specialist mobile security tools, they protect your business from the financial, operational, and reputational consequences of a data breach.
Did you know 59% of SMEs provide no mobile cybersecurity training to staff? Find out why this is a problem and what to do about it in our SME Mobile Threat Report.
Managed service provider cybersecurity: how to protect yourself and your clients
Managed service providers (MSPs) are at greater risk of cyberattacks than other businesses. The question is, why?
What makes MSPs, like yours, such an enticing target? And what can you do to protect your business and your clients?
Why do cybercriminals target MSPs?
MSPs might seem like an odd target. We tend to think of them as technology experts, with the best cybersecurity solutions, processes, policies, and tools. So surely there are more tempting targets? Unfortunately, this is only partially true.
No matter how well-protected an MSP might be, plenty of cybercriminals believe the risk is worth the reward. MSPs have remote access to their clients’ systems and networks. Not to mention huge amounts of data – everything from employee login credentials to financial records.
In short, cybercriminals target MSPs for the same reason they attack supply chains. Successfully breaching their defences can create a domino effect that extends way beyond the initial target, leading to ‘follow-on’ activity across the MSP’s client base.
What are the consequences of a successful MSP cyber-attack?
Cyber-attacks have direct and indirect consequences for MSPs.
Direct consequences
Disruption is perhaps the most obvious consequence. Unless you catch it early, a successful cyber-attack can bring your systems down, requiring a lengthy clean-up operation to put right. Not only does this impact productivity, it also has a detrimental effect on employee confidence and morale. There may be financial consequences to consider, too.
A serious malware attack can lead to prolonged service outages that directly impact your bottom line. Meanwhile, a successful ransomware attack may result in locked systems or stolen data, leaving you no choice but to pay the ransom. Additionally, you may have to pay a fine if an independent investigator decides your cybersecurity failed to meet the minimum requirements of your industry.
Then there's the possible reputational damage of a cyber-attack, which can make harder to attract new clients and retain existing ones.
Indirect consequences
Often, your clients suffer most from a managed service provider cybersecurity breach – particularly if you work with SMEs.
Only 33% of UK SMEs use threat monitoring tools, according to one government survey. At the same time, even fewer (31%) conducted a cybersecurity risk assessment last year. This makes SMEs more susceptible to threats than large organisations, enabling attacks to spread faster.
The Kaseya ransomware attack illustrates how easily an attack can get out of control. After exploiting vulnerabilities in the provider’s software, the breach spread to dozens of MSPs and over 1,500 of their customers in a matter of hours.
7 tips to defend against managed service provider cybersecurity threats
There’s no doubt cyberattacks can have serious consequences for MSPs. However, adopting a few simple measures can go a long way to protecting you and your customers.
1. Install software patches
Even the best-protected software can develop vulnerabilities over time, presenting a golden opportunity to wily hackers. You can mitigate this risk by updating your software with the latest patches as soon as they become available.
It’s like mending a puncture. The sooner you apply the patch, the less air escapes. Updating your software works on the same principle, allowing you to catch issues before they escalate. The best part? It’s quick and easy, taking only a couple of minutes a month.
Multi-factor authentication (MFA) is an application security process that requires users to set up two or more verification methods. Alongside the traditional username and password, these include:
Security questions
PIN codes
Biometrics (e.g. thumbprints)
On their own, passwords are vulnerable to data leaks and brute-force attacks. By contrast, MFA is difficult to crack – even for the most sophisticated hackers.
3. Back up your systems and data
Backing up your systems and data provides a vital failsafe should you suffer a breach. In some cases, it can even help you avoid having to pay a ransom.
The simplest and most cost-effective approach is to use data backup software. Once installed, it automatically copies data to one or more external sources. For example, an external drive, data centre, or cloud server.
Not sure what to back up? Use this simple rule of thumb: anything you don’t want to lose, back up.
4. Segregate your networks
Dividing your network into distinct parts (or sub-networks) helps to prevent unauthorised access to sensitive data.
The key to this is setting strict access controls for each sub-network, based on the zero-trust principle. This ensures users only have the privileges they need to do their job. It might sound extreme, but it’s critical in allowing you to isolate affected systems, customers, or accounts in the event of an attack.
Start with the basics. Teach staff how to spot the tell-tale signs of a cyberattack and how to respond. Looking further ahead, consider running regular top-up courses to keep staff up to date with best practices. This gives them the knowledge, skills, and confidence to combat threats.
6. Create an incident response plan
Cyberattacks aren’t inevitable. But, statistically speaking, they are likely. That’s why you need a coherent and actionable response plan, in case the worst does happen.
An incident response plan is a set of instructions that tells employees what to do in the aftermath of a cyber-attack. It helps you organise an effective and coordinated response, minimising damage and helping you recover faster.You’ll also need to encourage your clients to develop their own incident response plans. Just 4% of MSPs say all their clients have active incident response plans.
Is your software/hardware process documented, repeatable, and measurable?
How do you stay updated on emerging vulnerabilities?
What level of malware protection do you have in place?
What physical and digital access controls do you use?
How do you ensure upstream suppliers adhere to cybersecurity best practices?
Remember: when it comes to cybersecurity, a unified approach is the best defence.
Stay on top of cybersecurity
The cybersecurity landscape is like a daunting place. New threats emerge all the time, creating obstacles for you and your customers. But by following these simple steps, you can reduce your exposure to common security risks and work safely.
What is SVG phishing and how do you defend against it?
Phishing is one of the oldest cybercrime techniques in the book. Indeed, the first phishing email is thought to have originated back in the mists of time, around the year 1995. However, that doesn’t mean cybercriminals haven’t got creative in the years since. Added to recent innovations like smishing and Facebook Messenger scams, there’s a new threat to contend with: SVG phishing.
Here’s everything you need to know about this new threat, including what it is, how it works and, most importantly, how to counter it.
What is SVG phishing?
SVG phishing refers to the use of Scalable Vector Graphics (SVG) files in phishing attacks. An SVG is an image file format for creating and editing two-dimensional graphics. SVG files are a popular format for web and graphic design because they can be scaled up and down easily.
Cybercriminals use these files to deliver malware or direct victims to spoof forms that steal victims’ credentials.
Why do cybercriminals use SVG phishing attacks?
SVG phishing has gained traction in the cyber underworld because of its ability to evade traditional security measures. SVG files are less frequently flagged as potentially suspicious by security tools designed to detect more common file types like PDFs. This allows phishing emails containing SVG attachments to bypass many email filters, giving cybercriminals a route into target organisations.
How do SVG phishing attacks work in practice?
In practice, SVG attacks work much like any other phishing scam. Typically, a cybercriminal disguises the SVG files as legitimate documents or requests, using social engineering techniques to convince victims to open them.
It could be a request to edit a file from your ‘boss’ or a report that ‘requires your attention right now’, regardless, the techniques aren’t any more sophisticated than a typical phishing scam.
Once opened, these files can execute JavaScript, redirecting users to malicious websites, displaying fake login forms designed to capture sensitive information like passwords, or releasing malware into company systems.
However, while many SVG attacks aren’t particularly sophisticated, cybercriminals are getting smarter in how they launch them. There’s evidence of some campaigns using images that mimic documents like Excel spreadsheets, these include embedded forms for credential harvesting.
Are there any famous examples?
SVG phishing techniques have been in use since at least 2015, but media reports tend not to differentiate them from other types of phishing. Nevertheless, there are a couple of recent examples that researchers have identified.
1. Agent Tesla Keylogger: January – February 2024
Agent Tesla is a keylogger. It monitors keystrokes, takes screenshots, and steals passwords from various applications before sending the data back to the bad guys. It’s not a new form of malware; cybercriminals have been using it since around 2014, but in 2024, cybercriminals started delivering it via SVG files.
This campaign used a spoof Microsoft Excel spreadsheet, delivered via phishing emails. Once the victim opened the spreadsheet a script was run unleashing Agent Tesla.
2. XWorm RAT: December 2023 – present
The catchily named XWorm RAT is another form of malware, used for keylogging and stealing cryptocurrency wallets.
These campaigns used various techniques. Some used links embedded in phishing emails, and others included SVG files as attachments. Once opened, these SVG files initiated the download of zip archives containing XWorm RAT, unleashing the malware on the victim.
There’s no doubt SVG phishing poses a serious threat, able to avoid detection by many email filtering tools. But that doesn’t mean there’s nothing you can do to protect your business.
Staff training
We’re always championing the benefits of staff security training, but it’s particularly important when it comes to phishing. By their nature, phishing campaigns rely on social engineering techniques so, if you can train staff to recognise the tell-tale signs, you can effectively neuter the threat.
What training looks like will depend on the expertise within your organisation. You could
Implement realistic phishing simulations to test employee awareness or something more simple like webinars and videos. However you approach it, the key is that employees can quickly recognise suspicious emails and attachments.
Limit SVG Handling
One surefire way to mitigate the threat posed by SVG phishing is to limit what your email or browser can do. You can configure email platforms and browsers to block or restrict script execution within SVG files. This stops hidden nasties like Agent Telsa or XWorm RAT from running their malicious code.
Configure email filtering
In a similar vein to the previous point, more advanced email security solutions will be able to analyse attachments for malicious content. Check whether yours can analyse scripts embedded in SVG files. However, it’s worth noting that many email providers can’t do this yet, which is part of the reason for the success of SVG phishing campaigns.
Use CDR Technology
Admittedly, this solution is likely to be beyond the financial reach of most small businesses. Content Disarm and Reconstruction (CDR) solutions are expensive and tend to be the preserve of large corporations and those organisations that need to spend a lot on security.
But, if you’re feeling particularly flush, CDR is a great option for disarming SVG phishing. CDR systems treat all incoming files as potentially harmful. They deconstruct any incoming files, removing anything malicious, before rebuilding them and sending them on to the recipient.
Put policies in place
If your staff don’t understand the dangers of SVG files or the safe behaviours expected of them, they’re much more likely to fall prey to a scam.
Develop policies for handling email attachments, especially those from unknown or dubious sources. You could also consider restricting certain file types in email communications unless they’re absolutely necessary for operations. Once you’ve set these policies, you need to ensure employees adhere to them. The best way to do this is to make them readily available (they’re no use buried in a long-forgotten corner of a shared drive) and log who’s read them.
Dangerous, but avoidable...
SVG phishing is dangerous, but it doesn’t have to be an insurmountable problem. By implementing these strategies, your business can significantly reduce the risks and protect company data.
To celebrate the launch of CyberSmart Active Protect for mobile, we commissioned a survey asking 250 UK CEOs from companies with under 250 employees about their mobile security habits. We hoped to find out how the UK’s small businesses are tackling mobile security threats, what their security looks like, and whether there were obvious areas for improvement.
Our resulting SME Mobile Threat Report makes for illuminating and, at times, sobering reading. Here are our key takeaways.
1. Most small businesses expect staff to use mobile phones for work
Bring your own device (BYOD) policies can offer dramatic CapEx savings. And, unsurprisingly, this is a very attractive proposition for small businesses with tightened belts. Therefore, it’s no surprise that 60% of organisations expect their employees to use mobile devices to carry out work tasks, despite not providing all of them with work phones. Indeed, 65% of those businesses that don’t provide all staff members with mobile phones expect staff to use personal devices.
There’s nothing wrong with this in principle. Why wouldn’t you take advantage of devices your people already own, rather than investing heavily? However, as we’ll see shortly, it can pose some problems.
2. Many SMEs don’t have a mobile code of conduct for staff
Behaviour is essential to any successful BYOD policy. Staff need to understand what’s expected of them from a security perspective to work safely.
For example, you might enforce a policy that staff must never connect to an unsecured Wi-Fi network without using a VPN. A clear code of conduct or security policy can help prevent your business from being exposed to unnecessary risks.
So it’s concerning to see that while 59% of small businesses do have a code of conduct for completing work-related tasks on personal devices, over a third (39%) don’t.
3. Most SMEs don’t offer mobile security training to staff
Although it’s concerning that many small businesses are implementing BYOD programmes without clear security and conduct policies in place, we came across an even bigger problem.
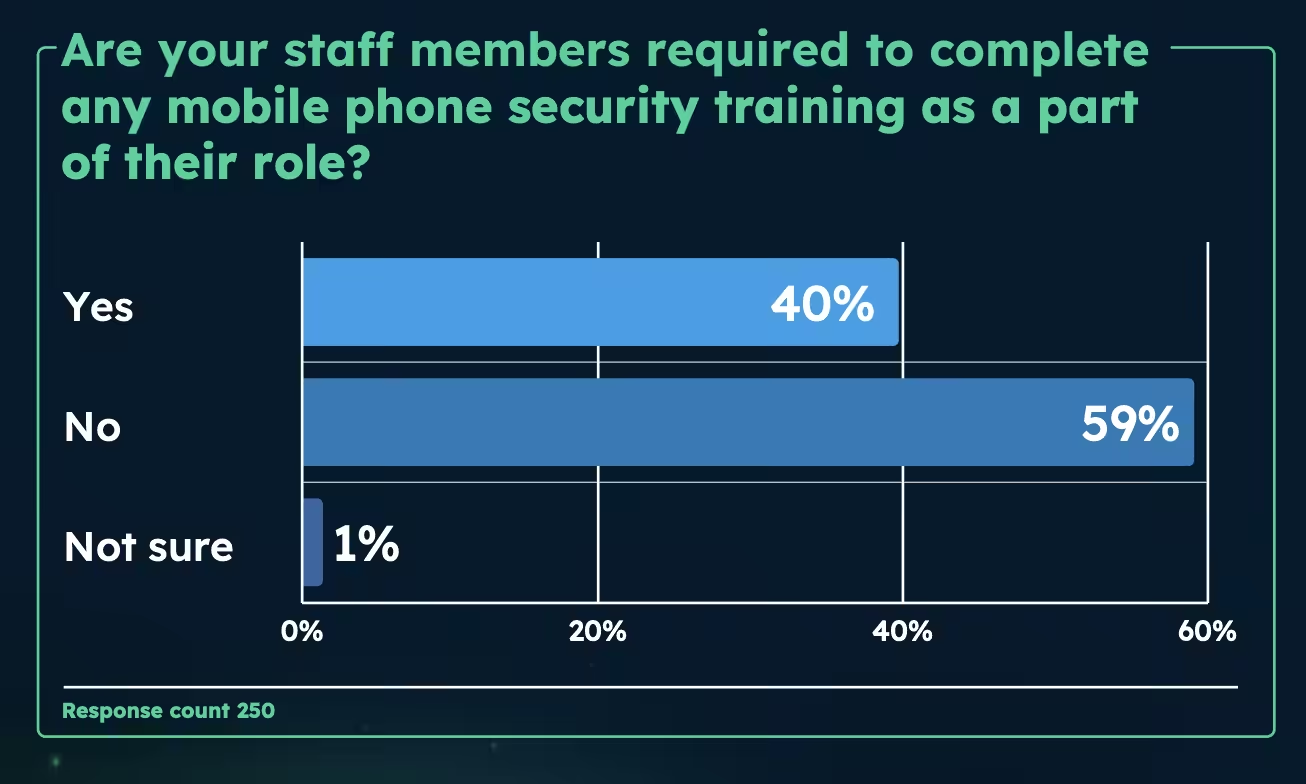
The majority (59%) of our respondents said that they don’t provide any mobile phone security training for staff. Without training on how to identify and avoid cyber threats or what safe online behaviour looks like, these businesses are courting potential disaster.
According to research from Cybint, 95% of cyber breaches stem from some sort of human error, or, in simple terms, could have been prevented. This is also backed by older research from Stanford University and Tessian which puts the figure at 88%.
Whichever figure you prefer, that’s a lot of preventable cyberattacks. And,
by not providing security awareness training to staff, it’s exactly these kinds of breaches that small businesses are risking.
4. Over a third of SME staff have clicked on a malicious link
Interestingly, many of our concerns around SMEs neglecting staff training and policies are born out later in the Mobile Threat Report.
According to the Department for Science Innovation & Technology (DSIT), 84% of all UK businesses have received some kind of phishing attack in the last 12 months. So, we asked SME leaders whether they or anyone at their business had clicked on a malicious link via mobile.
Although almost half (47%) of small business leaders responded no, some 38% reported that someone within their business had clicked on a phishing link – still a high number. What’s more, the real figure is likely to be somewhat higher given that a further 15% were either unsure or preferred not to answer.
This poses a real risk for small businesses. The UK has lost £1.7 billion to phishing scams in the last year, while the average cost of a breach to an SME ranged between £2,240 and £17,190. Worse still, phishing scams are often used to launch much nastier cyber threats such as ransomware and banking trojans.
5. SME staff are engaging in risky behaviour
Perhaps unsurprisingly given the problems we outlined earlier, the day-to-day cyber hygiene of SME staff raises concerns.
For example, a quarter of respondents admitted using a mobile device for work at a public charging station (e.g., at an airport or café), and 36% of respondents have worked from a public WiFi network on a mobile device. A further 9% admitted to forwarding corporate data to a personal account, and 11% admitted to storing corporate passwords or log in credentials on a mobile device without encryption.
This risky behaviour suggests low mobile security awareness among employees and a clear lack of concrete policies.
The good news? These risks are easy to mitigate
We’ve painted a pretty bleak picture of UK SMEs’ mobile security. And, it’s true, our research indicated some areas of real concern. However, the good news is that all of the issues our survey revealed are easy to mitigate.
Mobile devices are essential to the hybrid workforce. Having remote access to critical business systems and data enables teams to communicate, collaborate, and work more efficiently – wherever they are. But this convenience also makes mobile devices an ideal target for cybercriminals.
Among the growing list of threats, mobile malware is perhaps the most prevalent.
What is mobile malware?
Mobile malware is the umbrella term for malicious software specifically designed to target smartphones, tablets, and similar devices. It comes in various forms:
Viruses
Ransomware
Spyware
Trojan Horses
Worms
Cybercriminals employ a range of methods to deliver their nefarious payloads. These include disguising malicious software as legitimate apps – which infiltrate your device when you attempt to download them – and concealing compromised links or attachments in phishing emails and SMSs. Typically, the hacker’s goal is to:
Lock or delete important files
Steal sensitive data or hold it to ransom
Steal bank account details or financial information
Damage or hijack business devices
Spy on rival businesses
iOS vs Android: what’s more secure?
Like all Apple products, iOS has built-in safeguards to protect against cyber threats. This makes it more secure than Android, which uses an open-source model. However, neither operating system is infallible.
Common signs of infection
Mobile malware can cause serious harm if left unchecked – from costly operational downtime to reputational damage, fines, and even legal action. So, it’s crucial you know how to spot the signs of infection.
Give your device a thorough health check if you see any of these symptoms.
Poor performance
Drained battery
Overheating
Frequent crashing
Persistent pop-ups
Suspicious app downloads
Unexplained charges
8 tips to protect your business devices
Protecting your business devices against mobile malware doesn’t have to be time-consuming or expensive. From using secure Wi-Fi to investing in dedicated mobile device security, here are some quick, cost-effective steps to strengthen your defences.
1. Install security patches immediately
Apple and Android devices receive regular security patches – roughly every month or two. These critical updates fix flaws and vulnerabilities in your device’s operating systems. Install them as soon as possible or switch on automatic updates to close any obvious gaps in your security.
2. Only use trusted apps
Unregulated, third-party app stores are a haven for mobile malware and other cybersecurity threats. Mitigate this risk by enforcing stringent security policies that require employees to use trusted storefronts, like the Apple App Store and Google Play.
3. Avoid suspicious links
As obvious as it might sound, you can significantly reduce your cybersecurity risks by avoiding suspicious links and attachments. If you don’t recognise the sender’s email address, notice something strange about the message, or receive an unusual request, don’t click. It’s better to be safe than sorry.
4. Enforce a strong password policy
Have you ever used a well-known phrase as a password? Maybe a pet’s name? Perhaps you use the same one for every account? Don’t worry; there’s no judgement here. No one really likes passwords, but they’re a crucial component of mobile security.
Keep your devices and data secure by implementing a strong password policy that requires employees to use unique, complex passwords for every device. Follow these best practices to make them easier to manage:
Use a combination of four random nouns. E.g. fenceplanetoctopussauce
Use a mixture of upper- and lower-case letters, numbers, and special characters
Use a dedicated password manager to generate passwords for you and store them in a secure vault
5. Enable multi-factor authentication
Strong passwords alone may not be enough to deter tenacious cybercriminals. For added protection, enable multi-factor authentication (MFA) on your business devices and accounts. This requires employees to use two or more forms of verification, such as:
Passwords
PINs
Biometrics (e.g., a fingerprint or face scan)
Software tokens
6. Use password-protected Wi-Fi
Public networks are a convenient gateway to the internet, but they’re also exposed. To prevent cybercriminals from intercepting sensitive messages or launching harmful man-in-the-middle attacks, ensure employees only use password-protected Wi-Fi when working away from the office. If that isn’t possible, use a virtual private network (VPN) to encrypt network data and prevent unauthorised access.
7. Train your employees
68% of all breaches are the result of human error. So, running regular training sessions that teach staff how to identify and respond to cyber risks goes a long way to mitigating them. This includes when and how to share sensitive data, how to spot phishing attempts, and how to remove mobile malware.
8. Install mobile cybersecurity software
For the highest level of security, you can’t beat dedicated mobile device security software. Designed specifically for smartphones and tablets, it constantly scans devices for common security risks, such as:
Misconfigurations
System vulnerabilities
Suspicious apps
Malicious content
It can also block untrustworthy websites and repel attacks in real-time. This gives you more time to respond if something does get past your defences.
Mitigate the mobile malware threat
Mobile malware attacks continue to rise as more employees use their smartphones for work. But by understanding the threat and adopting these simple measures, you can enjoy the benefits of hybrid working safely and securely.
Want to know more about mobile specific threats your business faces? Check out our SME Mobile Threat Report.
Seven key takeaways from the NCSC Annual Review 2024
The National Cybersecurity Centre’s (NCSC) Annual Review 2024 offers a comprehensive overview of the UK’s cybersecurity landscape. This year’s report is a mixed bag for the industry. On one hand, significant progress has been made in areas such as threat prevention. However, persistent challenges remain and the report underscores the urgent need for collective action to tackle the most pervasive threats.
Here’s what you need to know, supported by key statistics and expert insights from the review.
1. Ransomware remains the most immediate threat
Unsurprisingly, ransomware remains high on the NCSC’s agenda. Attacks like the one on Synnovis, which disrupted NHS services and delayed thousands of medical procedures, demonstrate the deep impact of ransomware.
The review highlights the increasing sophistication of these attacks, with industrial control systems now a key target.
"Ransomware remains the most significant, serious, and organised cybercrime threat faced by the UK," the NCSC emphasised.
Key stat: The NCSC managed 20 ransomware incidents in 2024, 13 of which were classified as nationally significant—up from 10 in 2023.
Takeaway
Proactive resilience is essential. Adopting frameworks like Cyber Essentials can significantly reduce vulnerabilities to ransomware, as shown by the 92% reduction in insurance claims for certified organisations.
2. Nation-state threats escalate
The geopolitical landscape is amplifying cyber threats, with Russia, China, and North Korea leading state-sponsored campaigns. China, in particular, has been identified as a persistent actor targeting critical infrastructure for espionage and potential disruption.
"China state-affiliated actors routinely seek access to networks globally, targeting critical national infrastructure for espionage and disruptive purposes," warns the review.
Key stat: In 2024, the NCSC issued 1,957 cyber attack alerts, including 89 nationally significant incidents—a sharp rise from 62 the previous year.
Takeaway
The alignment of public and private sector defences is critical to counter sophisticated, state-sponsored attacks.
3. Artificial intelligence: A dual challenge
AI is reshaping cybersecurity, offering both threats and opportunities. While cybercriminals are using AI for precision reconnaissance and social engineering, defenders are harnessing AI to automate detection and improve response times.
"Generative AI will make it harder for defenders to identify social engineering attacks without the development of new mitigations," the NCSC noted.
Key stat: AI-driven tools have significantly narrowed the time between vulnerability discovery and exploitation, heightening the need for real-time defences.
Takeaway
Although cybercriminals appear to have the edge in AI at the moment, it doesn’t have to be this way. As the technology develops, organisations should explore AI-enhanced cybersecurity solutions to match adversaries’ growing capabilities.
4. Cyber Essentials: A proven solution
The Cyber Essentials scheme continues to demonstrate its value as a foundational framework for organisational security. Now in its tenth year, the programme has helped thousands of businesses mitigate common cyber threats.
"Cyber Essentials is a proven baseline that guards against the most common cyber attacks while signalling to customers that businesses take security seriously," the review stated.
Key stats: Organisations with Cyber Essentials are 92% less likely to claim on cyber insurance policies.
Over 33,000 Cyber Essentials certifications were issued in 2024, a 20% increase on the previous year.
Takeaway
Businesses of all sizes should prioritise achieving Cyber Essentials certification to protect themselves and build customer trust.
5. Securing democracy: Election protection
The NCSC played a pivotal role in safeguarding the 2024 UK General Election, implementing pre-emptive measures to secure infrastructure and provide tailored cyber support to high-risk individuals.
"The general election was delivered smoothly and securely, with no major incidents impacting the outcome," the review confirmed.
Key stat: Over 50% of the bespoke alerts issued by the NCSC in 2024 related to pre-ransomware activity, enabling organisations to act before attacks could escalate.
Takeaway
Critical events require tailored cybersecurity strategies to pre-empt threats and ensure operational continuity.
6. The role of legislation in resilience
The Cyber Security and Resilience Bill, expected to become law this year, will expand regulatory protections, enhance reporting requirements, and enforce stronger accountability across digital supply chains.
"The bill is a crucial step toward hardening the UK’s defences against sophisticated cyber threats," the NCSC stated.
Key stat: Over 70% of organisations in the NCSC’s trust groups have adopted Early Warning services to enhance preparedness.
Takeaway
Organisations must prepare to comply with stricter regulatory requirements, especially in critical infrastructure sectors.
7. Systemic market challenges
The NCSC highlights a critical gap in how technology markets prioritise security. Basic safeguards like multi-factor authentication are often treated as premium features rather than standard offerings.
"We must build a future where products are secure, private, resilient, and accessible to all," the review advocates.
Key stat: Memory safety vulnerabilities remain one of the most prevalent causes of breaches, exacerbated by insufficient adoption of secure-by-design principles.
Takeaway
Industry and regulators must champion secure-by-design principles to address systemic vulnerabilities and improve resilience.
What is the key takeaway?
Above all, the NCSC’s Annual Review is a stark reminder that, from small businesses to national infrastructure, the UK’s cyber resilience requires urgent attention. That might sound like a gargantuan task. However, in reality, all it requires is that everyone pitches in.
"Improving resilience is not a technical challenge—it’s a matter of urgency and leadership," the review concludes.
Whether you’re an SME or part of a critical national sector, the time to act is now. Adopt frameworks, collaborate with trusted partners, and embed security into your operations. Together, we can close the resilience gap and create a safer digital future.
Want to know more about the threats facing small businesses like yours? Check out our latest research, The SME Mobile Threat Report.
Press release: Poor mobile security practices rife at SMEs, CyberSmart survey finds
Cybersecurity incidents and poor mobile cybersecurity hygiene is endemic across the UK's SMEs
London, UK – 04/12/2024 - New research conducted by CyberSmart, a leading provider of SME security solutions, indicates that mobile cybersecurity incidents at small businesses are widespread.
The research, conducted by OnePoll in Autumn 2024, polled 250 small-medium enterprise (SME) business owners or leaders in the UK, found that over a third (38%) of small business employees or owners report clicking on a phishing link via mobile.
Elsewhere, 30% of respondents reported losing or having stolen a mobile phone containing sensitive corporate information, leaving their business more vulnerable to potential cybercriminal activity.
While these dramatic incidents are a concern from a security perspective, the minutiae of business activity taking place on a mobile, without policies in place, also suggest a concerning lack of security awareness from SMEs. For example, a quarter of respondents admitted using a mobile device used for work to a public charging station (e.g., at an airport or café), and 36% of respondents have worked from a public WiFi network on a mobile device. A further 9% admitted to forwarding corporate data to a personal account, and 11% admitted storing corporate passwords or login credentials on a mobile device without encryption.
“These results are obviously a concern for SMEs and their employees. Large organisations are more likely to implement security awareness training for mobile devices and implement a code of conduct for corporate devices. This is not a luxury afforded to most SMEs, who do not have the resources or time to do so.” Said Jamie Akhtar, Co-Founder and CEO at CyberSmart. “It is the responsibility of the cybersecurity industry to change this, and to make security more accessible for the small businesses which make up 99% of the UK economy.”
CyberSmart research reveals 60% of businesses expect their employees to carry out work tasks on their personal mobile phone.
London, UK – 26/11/2024 - New research conducted by CyberSmart, a leading provider of SME security solutions indicates that organisations not only allow employees to use their personal mobile phones to compete work tasks but actively expect them to.
The research, conducted by OnePoll in Autumn 2024, polled 250 small-medium enterprise (SME) business owners or leaders in the UK, found that 60% of organisations expect their employees to use mobile devices to carry out work tasks despite not providing all of them with work mobile phones.
Equally concerning is that almost two thirds (60%) of staff members are not expected to carry out mobile security training. An organisation that allows employees to use personal mobile phones to carry out work without security training is massively increasing the chance of a breach.
Elsewhere, the survey unearthed a worrying lack of concern from business leaders regarding cyber security and employee security. 40% of organisations do not have a mobile code of conduct in place for employees.
“While these results are concerning, SMEs in the UK remain chronically underserviced by the cybersecurity industry” said Jamie Akhtar, Co-Founder and CEO at CyberSmart. “It is important to make the distinction that many of these organisations have limited resources and are already stretched thin making it difficult for them to invest in cybersecurity.
We would advise SMEs to engage with solution providers who understand their specific needs, and more broadly would advise them to consistently focus on cybersecurity training, IT policies and fostering a more security-conscious culture would help them to achieve a more secure workplace.”
Desktop computers, laptops, and mobile devices are often the first port of call for hackers looking to launch a cyber-attack. Collectively known as endpoints, hackers treat them as a convenient gateway into your systems.
However, there are ways to defend your business. And the most effective is with dedicated endpoint detection and response (EDR).
What is endpoint detection and response?
Coined by Gartner’s Anton Chuvakin in 2013, endpoint detection and response is a branch of cybersecurity technology that encompasses automated threat monitoring tools.
Where traditional antivirus software is reactive, EDR is proactive. Once installed, it continuously monitors your devices, collecting and analysing data in real time to detect cybersecurity threats. If it does, it responds automatically – repelling or containing the threat before it can spread.
Most endpoint detection and response solutions follow the same basic approach, even if their capabilities differ.
Step 1. Data collection
Working quietly in the background, the software collects data from each device on your network. This includes:
Authentication requests
Network connections
Configuration changes
Device performance
Then, it consolidates everything into a central database for easy access.
Step 2. Analysis and detection
Next, the software analyses the data and compares the results against global threat intelligence to identify threat indicators. These typically fall into one of two categories:
Indicators of compromise (IOC): signs that a threat has breached a system or endpoint.
Indicators of attack (IOA): pattern or behaviours that signal a cyber-attack is about to happen or in progress.
Security team members can access this information directly from the software, allowing them to monitor threats across your business in real time.
Step 3. Response
Should the EDR software flag a potential threat, it automatically contains it.
The nature of the response depends on the nature of the threat and your software’s capabilities. Typical responses include:
Notifying security personnel
Suspending the affected device(s) processes
Disconnecting the affected device(s) from your network
Triggering an antivirus scan
Step 4. Investigation and remediation
With the threat contained, security teams are free to investigate it. Some EDR software generates comprehensive reports that allow you to track incidents back to their source. This helps you pinpoint the root cause, track it's trajectory through your systems, and organise your response.
For example:
Patching the vulnerability
Updating detection rules
Deleting malicious files
Repairing or restoring damaged components
Step 5. Prevention and threat hunting
EDR software keeps detailed records of every incident. Security analysts can access this data at any time, learning from past incidents to prevent future ones. It also helps them:
Identify vulnerabilities
Track how specific threats develop over time
Support threat hunting exercises
Benefits of endpoint detection and response
Identify blind spots
At the highest level, endpoint detection and response is all about visibility. It lets you monitor every device in real time, highlighting misconfigurations and unsecured connections cybercriminals can exploit. With this information, you can plug gaps in your defences and put in place measures to prevent similar cases in future.
Spot emerging threats
Antivirus software is great at detecting known threats. It does this by comparing the threat’s unique signature against global threat intelligence databases.
However, this approach makes it less effective at combating emerging or evolving threats such as social engineering attacks, like phishing.
By contrast, EDR identifies threats by looking for signs of suspicious activity and behaviour. This means it can detect new and established threats.
Block sophisticated attacks
Dynamic endpoint security and detection software combats advanced threats, outing it ahead of basic antivirus tools. This includes sophisticated malware variants that can go unnoticed for months, waiting for the perfect opportunity to strike, or adapt their behaviour to avoid detection.
Minimise or prevent damage
As an automated solution, EDR reduces the delay between threat detection and mitigation. Once it identifies a potential threat, the software immediately takes steps to contain and neutralise it. This prevents attacks from escalating, minimising the damage to your business and saving you from a costly clean-up operation.
Your first line of defence
Even the most advanced antivirus software can’t catch every threat. New tactics and attack vectors emerge every day, some of which will make it past your security perimeter.
Endpoint detection and response software works in tandem with your existing security tools. It forms a vital layer in your defence network, spotting the sophisticated threats traditional antivirus can’t see to keep your network, systems, and data safe.