The top 6 challenges MSPs face with Cyber Essentials Plus

Regardless of your specialism, sector, or size, if you’re a managed service provider (MSP), chances are a customer will have asked you at some point to help them with their Cyber Essentials Plus certification. For many MSPs, it’s a regular job. But supporting customers to prepare for and pass Cyber Essentials Plus isn’t without its challenges.

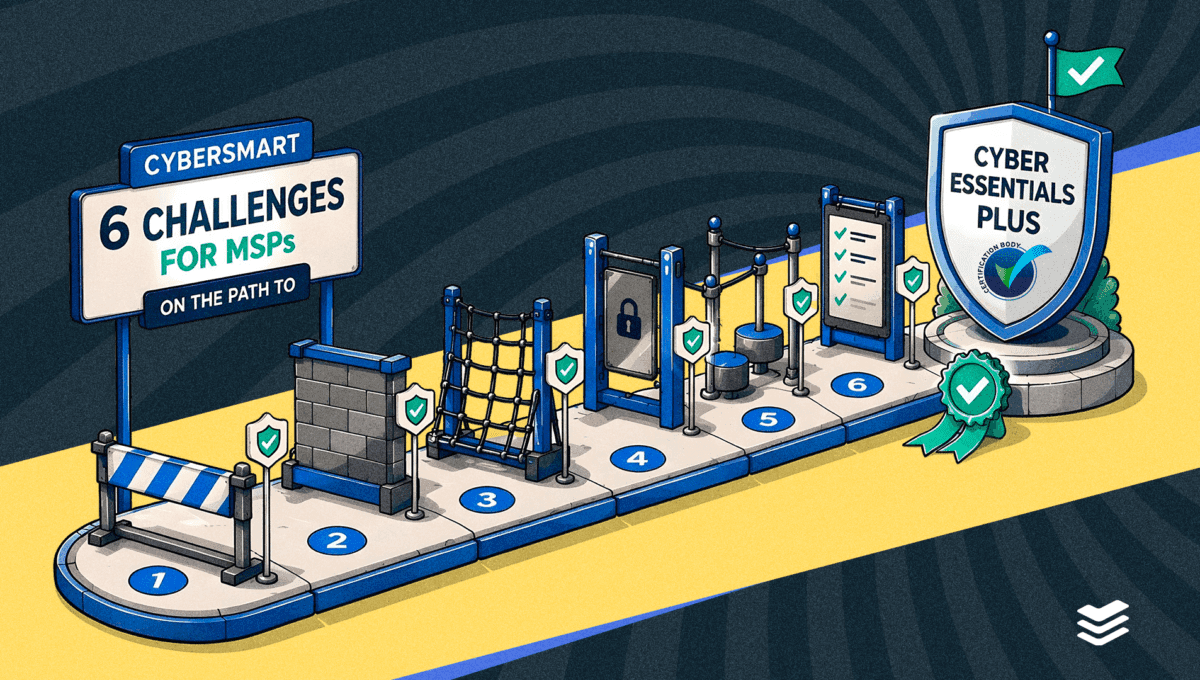
As any MSP can attest, Cyber Essentials Plus audits can turn into a complicated round of remediations, resubmissions, and delays. However, it doesn’t have to be this way. Most of the time, Cyber Essentials complications are caused by easily avoidable mistakes. To help you and your clients experience smoother, faster audits, we’ve pulled together the six most common challenges MSPs face with Cyber Essentials Plus and how to avoid them.

1.  Missing high-quality vulnerability management

In a time of tightened budgets, many MSPs use what they have or what they can find cheaply for vulnerability management. And that usually means an RMM tool or the least costly solution available. This might not sound like much of a problem. After all, isn’t it just good business sense to use what you have if it’ll do the job?

However, when it comes to a Cyber Essentials Plus audit, it does cause problems. The problem is that RMMs or unapproved tools often don’t check for all the same vulnerabilities the CE+ audit looks for. So, when the Assessor runs their approved scan, new or higher-risk issues suddenly appear, even though the MSP thought everything was fine.

Or, to put it another way, it’s a bit like using your car’s dashboard gauges to check you’re roadworthy; the MOT test will still find things your dashboard never told you about. 

Unexpected vulnerabilities discovered during audits trigger rapid, unplanned remediation tasks, resulting in delays, additional costs, and increased stress for both you and your customers.

What to do about it

Use approved, comprehensive vulnerability scanning tools like Qualys Guard, Nessus, or CyberSmart Vulnerability Manager. This not only makes for a smoother audit process; it also means your clients will benefit from a better level of year-round protection.

2. Device configuration errors

Many people go through life with devices configured to the default settings they came with. However, as well as posing a security risk, this is a sure-fire way for your clients to experience problems during a Cyber Essentials Plus audit.

Misconfigured devices or default settings, such as passwords, outdated .NET versions, or unused open ports, are some of the most common causes of audit failure. Plus, default settings and misconfigurations provide entry points for cybercriminals to exploit. Research from SOCRadar released in 2023 estimated that security misconfigurations are responsible for as much as 35% of all cyber incidents ever.

What to do about it

Look to standardise configurations across your client’s business using clearly documented baselines. The easiest way to do this is to use a tool that can automatically detect configuration issues, so you can address them as and when they arise, rather than working through all of them come audit time.

Alongside this, you should regularly audit client systems, removing default passwords and applying secure configuration standards, such as those from the Centre for Internet Security.  

3. BYOD and shadow IT

Bring Your Own Device (BYOD) has been a boon for businesses, especially since the COVID-19 pandemic. However, it’s not without security risks and can cause problems for Cyber Essentials audits. Personal devices often have less robust security measures than those configured and managed by businesses. What’s more, some research suggests that employees are less likely to engage in cyber secure behaviours when using personal devices (although other studies propose that the opposite is true)

Shadow IT poses many of the same problems for MSPs. Unmanaged or unlisted devices can lead to uncontrolled data leakage, malware infections, and exposure of sensitive data. Plus, when it comes to audit time, you’ll need every device used within the business to comply with Cyber Essentials controls, potentially adding remediation time, delays and costs.

What to do about it

Use solutions like CyberSmart Active Protect for Mobile, which offers privacy-first monitoring of personal devices, verifying compliance without infringing user privacy. Establish clear BYOD policies and regularly review asset registers. If technical solutions aren't available, MSPs may manually validate configurations through documented screenshots provided by users.

4. MFA on cloud accounts

MSPs and their customers often face issues fully rolling out multi-factor authentication (MFA) across all cloud-based accounts. Tracking this across your client base can prove a challenge, and, somewhat inevitably, some administrative accounts end up getting missed.

This is a problem for a couple of reasons. Firstly, a lack of MFA increases the likelihood of unauthorised account access and data breaches – particularly for administrative accounts, which have wide access privileges. Secondly, as MFA on administrative accounts is a Cyber Essentials requirement, they could fail their audit.

What to do about it

Enable MFA across all cloud-based administrative accounts, prioritising accounts with higher privileges. Clearly document your MFA implementation policies, regularly audit accounts, and provide users with practical support to simplify adoption.

5. Lack of account separation (users running as admin) or incorrectly configured JIT solutions

The importance of access control and account separation won’t be news to most MSPs. Nevertheless, it’s often something customers get wrong. Businesses commonly grant users permanent administrative privileges when they don’t need them. Or, even when they use just-in-time (JIT) privilege management, they configure it poorly.

Once again, this poses a couple of issues. Most importantly, permanent administrative rights significantly increase the chance of malware installation, unauthorised changes, and major incidents due to human error. Alongside this, it can lead to failed Cyber Essentials Plus audits.

What to do about it

Adopt the principle of 'just enough' privilege (providing the minimal required permissions for daily operations) rather than 'just in time' (temporary elevation for tasks). Cyber Essentials explicitly accepts ‘just enough’ approaches. Review Privileged Identity Management (PIM) and Privileged Access Management (PAM) configurations carefully to ensure compliance.

6. Industry-specific challenges

While Cyber Essentials Plus might be beneficial to just about every sector you can think of, the simplicity of the audit process can vary wildly based on industry. For example, clients in industries such as education, construction, or legal frequently use external contractors, temporary staff, or need to grant access to students.

This can dramatically complicate asset control and compliance. Worse still, it often introduces non-compliant devices into organisations, creating security risks and making your client less likely to pass their audit.

What to do about it

Maintain clear, documented asset registers, policies, and user agreements specifically designed for temporary or external users. IASME guidance provides specific information tailored for managing contractors, students, and single-person entities effectively within Cyber Essentials guidelines. MSPs should carefully define the compliance boundaries and regularly audit or confirm device security status with temporary or external personnel.

The challenges MSPs face with Cyber Essentials Plus aren’t insurmountable

Hopefully, your top takeaway from this blog is that the challenges you’re likely to face in leading clients through the Cyber Essentials Plus process aren’t insurmountable. With each challenge, proactive steps ahead of the audit can significantly simplify the Cyber Essentials Plus certification journey, giving you happier clients and stress-free staff.

CyberSmart Patch helps you reduce vulnerabilities by keeping third-party software up to date — without the hassle. Try it today.

Frequently asked questions

    1. Missing high-quality vulnerability management
    2. Device configuration errors
    3. BYOD and Shadow IT
    4. MFA on cloud accounts
    5. Lack of account seperation
    6. Industry-specific challenges
  • Bring Your Own Device (BYOD) refers to the practice of employees using personal devices for work. This is usually a policy the business has implemented.

    Shadow IT on the other hand, refers to software, hardware, or cloud services used by employees for business purposes without the knowledge or approval of the company's IT department.

    However, both come with similar security risks and often make the Cyber Essentials Plus audit process more complicated.

  • CyberSmart offers a number of tools to help simplify the Cyber Essentials Plus audit process for MSPs and their client.

    • CyberSmart Vulnerability Manager (CSVM) is an approved vulnerability scanner and checks for everything that the Cyber Essentials Plus audit covers, making for smoother audits and year-round protection.
    • CyberSmart Active Protect offers privacy-first monitoring of personal devices and year-round compliance with Cyber Essentials Controls.
    • CyberSmart Patch automates patch management for third party software, helping you to stay on top of vulnerabilities.
    • We're also the UK's leading provider of Cyber Essentials and Cyber Essentials plus certifications.

9 patch management best practices every business should follow

It's 3 am on a Tuesday. Your phone buzzes with urgent alerts – systems are down and customers can't access their accounts. After a bit of investigating, it turns out the culprit is yesterday's "minor" security update that nobody thought needed testing. Sound familiar?

Patches are a bit like dental check-ups. You know they're essential for your health, but it’s always tempting to put them off until a more convenient time. Suddenly, months pass and you’re on the wrong end of a painful (and expensive) procedure.

Ignoring patches or failing to test them before installation can prove similarly costly. The good news is that, by following these nine patch management best practices, you can protect your systems and avoid the 3 am wake-up calls.

What is patch management?

Before we dive into patch management best practices, let's quickly clarify what we're talking about. 

Patch management is the process of distributing and applying updates to software, firmware, and drivers. Developers release these updates or “patches” to correct vulnerabilities or bugs in their systems and add new features to their products.

Patch management best practices

1. Stay up to date on device and software vulnerabilities

When it comes to patch management, knowledge is your first line of defence. After all, you can't patch what you don't know about.

Keep an eye on the latest cybersecurity threats and patch releases by:

  • Subscribing to vendor security bulletins
  • Monitoring vulnerability databases like the European Union Vulnerability Database
  • Following cybersecurity news and threat intelligence feeds
  • Maintaining an accurate inventory of all your assets

Create a detailed inventory of all hardware, software, endpoints, and connected devices. Full visibility is necessary to maintain consistent patch compliance across your tech stack.

2. Prioritise patches based on risk

Effective patch management starts with understanding which vulnerabilities pose the greatest threat to your business.

Start by categorising patches into three tiers based on their severity and the importance of the affected systems:

  • Critical – security patches that address actively exploited vulnerabilities
  • Important updates that fix significant bugs or security issues
  • Optional feature updates or minor improvements

For example, a critical patch for an internet-facing server handling customer data needs immediate attention. A similar patch for an isolated test machine can wait. Keep a record of your prioritisation decisions to justify your choices, if questioned, and provide valuable context for future patching cycles.

Between patches, monitor vendor announcements closely. Subscribe to security bulletins so you know when urgent patches are released.

3. Automate where possible

Automation transforms patch management from a burden to a background process. Modern patch management tools can:

  • Scan for missing patches
  • Schedule deployments
  • Alert you to critical vulnerabilities
  • Generate compliance reports

Resist the temptation to automate everything. Start with low-risk or routine patches, like antivirus definitions, then expand gradually as you build confidence in your automation tools.

4. Test patches before installation

Whether you deploy patches manually or automate the process, always test first. Start with a small pilot group of tech-savvy users who can spot and report issues before you roll out to everyone. 

For important updates to critical systems, patch management best practices recommend testing them first in a controlled environment. This doesn't have to be expensive. Simple virtualisations can help you create realistic test scenarios without breaking the bank. The key is to ensure it matches your production environment as closely as possible.

5. Make patch management routine

Without an established routine, patch management becomes a reactive rather than a controlled process.

Microsoft provides a great anchor point with Patch Tuesday (or Update Tuesday). It releases security updates and software patches on the second Tuesday of every month, providing a predictable schedule for deploying updates across your organisation.

But don’t stop there. Create dedicated maintenance windows to keep on top of updates. Maybe that's Sunday mornings for your servers, or Tuesday evenings for workstations. The key is consistency – when people know when updates are coming, they can plan around them.

6. Define responsibilities

A patch management process without clear ownership is like a ship without a captain. When there’s no clear chain of command, critical tasks get missed. 

Document who's responsible for each task, activity, and process. Define who:

  • Identifies and assesses new patches
  • Approves patches for testing
  • Conducts testing and validation
  • Manages deployment schedules
  • Handles emergency patching decisions
  • Documents the entire process
  • Keeps users informed about upcoming patches

Regular cybersecurity training ensures everyone understands not just their role in patching, but why it matters for overall security.

7. Look beyond software

Many businesses focus solely on operating systems and application patches while ignoring the foundation everything runs on – firmware and drivers. But these updates are just as critical as software patches.

Firmware

Firmware vulnerabilities can provide attackers with deep system access that persists through OS reinstalls. These vulnerabilities often go undetected by traditional security tools, making them a prime target for supply chain attacks.

Drivers

Driver updates are equally important. Outdated drivers don't just cause performance issues – they can contain security vulnerabilities that give attackers kernel-level access to your systems. Whether it's graphics drivers, network adapters, or printer drivers, keeping them current is essential for both security and stability.

Don't forget about third-party applications. Simply turning on Windows and Apple updates won’t protect you from the open-source and third-party vulnerabilities that account for up to 80% of the global total. Password managers, for example.

Incorporating firmware vulnerabilities and third-party applications into your patch management strategy ensures you don’t overlook these vital updates and leave your systems exposed.

8. Establish standard and emergency patching policies

Not every patch can wait for your next maintenance window. Having separate procedures for routine and emergency patching ensures you can respond quickly to emerging threats, without sacrificing control.

Your standard patching policy should cover:

  • Regular maintenance windows
  • Testing requirements
  • Approval processes
  • Communication protocols

Define clear triggers for emergency patching, such as active exploitation or zero-day vulnerabilities in internet-facing systems, and a deployment window. For example, within 48 hours of seeing the notification.

Document your procedures thoroughly. This should include who can authorise emergency patches and how to communicate urgent changes to affected users. 

Establishing clear emergency procedures is particularly important for critical vulnerabilities that include a risk of collateral damage to other assets.

9. Implement a rollback plan

Even with the most thorough testing, patches can (occasionally) create unanticipated issues in your systems. A solid rollback plan helps you bypass potential complications and maintain system stability when things don't go as planned.

Your rollback plan should cover:

  • Clear rollback triggers define what constitutes a failed patch
  • Communication plans who needs to know about the rollback and when 
  • Step-by-step procedures document exactly how to reverse the patch
  • System backups essential for data recovery and system restoration

Keep records of any rollbacks you perform. Understanding why patches failed helps prevent similar issues in future deployments.

From 3 am panic to proactive patch management

Implementing all of these patch management best practices in one go probably seems like a daunting prospect. The good news is you don’t have to.

Start small. Pick one or two best practices that address your biggest pain points and build from there. Remember, patch management isn't about achieving perfection once. It's about establishing consistent, controlled processes that keep your systems safe and stable day in, day out.

CyberSmart Patch helps you reduce vulnerabilities by keeping third-party software up to date — without the hassle. Try it today.

Frequently asked questions

  • Check your system's update settings. 

    On Windows, go to Settings > Update & Security > Windows Update. 

    On Mac, click the Apple menu > System Preferences > Software Update. 

    Most applications have an "About" or "Check for Updates" option in their menu. If you're managing multiple devices, consider using dedicated patch management software.

  • For critical security patches, aim to install them as soon as possible to minimise exposure. Install emergency patches within 48 hours of notification. Regular updates can follow your standard maintenance schedule.

  • Yes, patch management is one of the five key controls of Cyber Essentials. To achieve certification, you must ensure none of your software or devices run on unsupported versions and that you install updates within 14 days of release for critical or high-risk vulnerabilities.

  • While the core principles remain the same, the execution differs. Windows offers more granular control through Group Policy and tools like Windows Server Update Services (WSUS). Mac updates are typically managed through macOS Software Update or Mobile Device Management (MDM) solutions. Both require testing and staged rollouts, but Mac environments often have fewer compatibility issues due to Apple's tighter ecosystem.

  • Yes, significantly. iOS devices receive regular updates directly from Apple. Android is a little less predictable, with update availability depending on both Google and device manufacturers.

The impact of phishing on SMEs

When you think about business phishing attacks, what comes to mind?

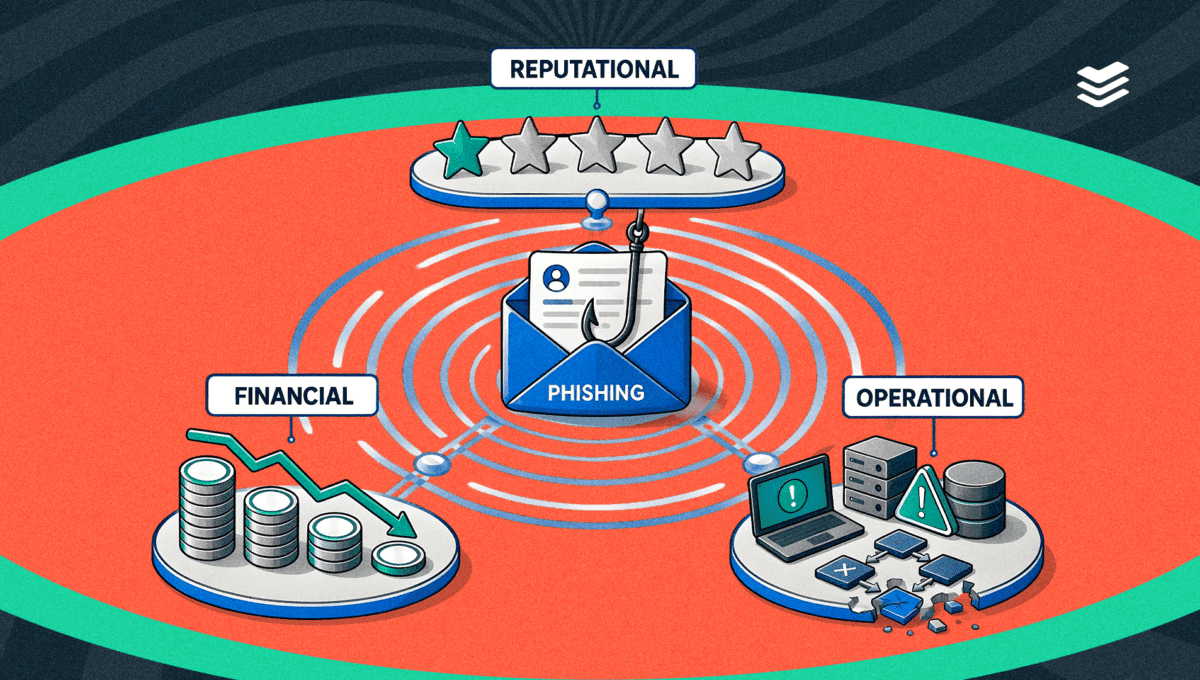
Most people imagine a hooded hacker in a dark room draining the company bank account. But the true impact of phishing extends far beyond stolen funds. A single attack can have consequences that cascade through your entire organisation for weeks, months, or even years.

Charting the real impact of phishing

From costly productivity losses and regulatory fines to damaged customer relationships, phishing attacks strike at the very foundation of your business.

Financial consequences that compound quickly

The most obvious impact of phishing is theft. Once cybercriminals have tricked victims into handing over sensitive information, like bank account details, they can use it to steal company funds. But as scary as that thought is, the hidden expenses often dwarf these initial losses.

When phishing attacks take your systems down, productivity plummets. Employees can't access essential files, emails, or applications. You can’t process orders or service requests, and business grinds to a halt.

According to research on UK SME downtime, the median cost ranges from £1,800 for micro business to £15,000 for medium-large ones. So, a phishing attack that takes your systems offline for even half a day could cost you tens of thousands in lost productivity alone.

Then there are the recovery costs, which include:

  • Investigating the incident
  • Repairing or rebuilding your systems
  • Retrieving or recreating lost data
  • Upgrading your cyber defences
  • Regulatory fines
  • Legal fees

It all adds up. You may also have to pay a higher cybersecurity insurance premium following an attack, depending on your provider.

Learn how CyberSmart Phish can help your team spot phishing attempts before they cause harm

Reputational damage that erodes customer trust

Falling victim to a phishing attack can seriously harm your reputation. When customers discover that a phishing attack has compromised their personal data, trust evaporates almost instantly.

Among businesses that have experienced a cyberattack, 47% said they struggled to attract new business and 43% said they lost existing customers as a result.

Bad news spreads quickly. Negative reviews appear online, cautionary tales permeate through industry networks, and potential customers choose competitors they perceive as more secure. The impact on your brand persists long after you restore your systems and improve security.

Phishing attacks are particularly damaging to financial and professional services firms. Responsible for highly sensitive information, their clients expect the highest data privacy and security standards. A single breach can completely erode trust and destroy relationships you've built over years.

Regulatory repercussions that cost time and money

Under data privacy regulations like GDPR, you have a legal duty to protect it with “appropriate technical and organisational measures”. If you suffer a phishing attack and regulators determine that you didn’t have reasonable safeguards in place, you could face serious penalties. GDPR fines can reach up to €20 million or 4% of global annual turnover – whichever is higher. 

The compliance impact of phishing is about more than financial penalties. Under GDPR, you have just 72 hours to report certain types of data breaches to regulators. But when you’re trying frantically to understand the full scope of an attack and contain the damage, this can fall through the cracks.

Lastly, regulators may decide to investigate a data breach – particularly if it resulted in the loss of sensitive information, affected a large number of people, or both. Investigations take time and can cause significant disruption.

7 phishing prevention tips to protect your business

1. Train employees to spot red flags

Your employees form your first and most important line of defence against phishing. Host regular cybersecurity awareness training sessions to teach them to spot red flags, like:

  • Urgent demands for action
  • Unexpected payment requests
  • Obvious spelling mistakes
  • Requests for sensitive information

2. Implement multi-factor authentication

Multi-factor authentication (MFA) provides added layers of security to sensitive accounts and documents. 

A skilled and determined hacker can crack even the strongest passwords. Reinforcing your defences with supplementary verification methods (like an authenticator app or one-time SMS code) helps to keep them at bay. Most cloud services – including Microsoft 365 and Google Workspace – offer MFA at no extra cost.

3. Verify requests through separate channels

One of the most effective defences against sophisticated phishing is surprisingly low-tech. If someone requests a payment change, bank transfer, or sensitive information via email, verify the request through a separate channel. For example, by calling a colleague.

This simple step is particularly effective at stopping CEO fraud and spear phishing attempts by neutralising the attacker’s primary weapon – urgency and authority.

4. Enable email security

Most major email providers offer some level of phishing protection as standard. Gmail, Outlook, and other major email services have spam and phishing filters that flag malicious emails before they reach your inbox. 

Ensure you configure these features properly and install patches as soon as they’re available to protect against emerging phishing techniques.

5. Keep systems updated and patched

Outdated software provides easy entry points for attackers. Configure devices and software to update automatically to take the pressure off your team.

This simple step closes many vulnerabilities that phishing attacks attempt to exploit, such as outdated web browsers or unpatched email clients. Regular vulnerability management helps you identify and address these security gaps.

6. Control access and privileges

Not everyone in your organisation needs access to everything. Review who has access to financial accounts, administrative dashboards, customer databases, and other critical systems – updating permissions based on the principle of least privilege

By restricting access rights, you limit the potential damage if someone falls victim to a phishing attack.

7. Create an incident response plan

t’s impossible to eliminate the threat of phishing attacks entirely. Whether it’s a momentary lack of concentration or a sophisticated scam that would fool the most diligent employee, someone will click a phishing link eventually. 

To minimise the damage, create an incident response plan that outlines the steps employees should take if they fall victim to an attack. Make reporting easy and blame-free so employees feel comfortable sharing potential incidents immediately rather than worrying about getting in trouble.

Shield yourself from the impact of phishing

The impact of phishing reaches far beyond your bottom line – reputation, operations, and regulatory compliance are all at risk. The good news? Most attacks exploit simple gaps rather than sophisticated systems. 

Basic steps like employee training, multi-factor authentication, and strong email security can prevent most of these threats. By focusing on these fundamentals, you can dramatically reduce the impact of phishing and keep your business secure.

Want to give your people the skills to recognise phishing scams before they turn into breaches? Check out CyberSmart Learn, our cybersecurity focused learning management system.

Frequently asked questions

  • Email remains the most common communication tool, which makes it a tempting target. Automated phishing kits make it easy to launch large-scale campaigns, while AI tools now allow cybercriminals to create highly convincing, tailored emails at speed.

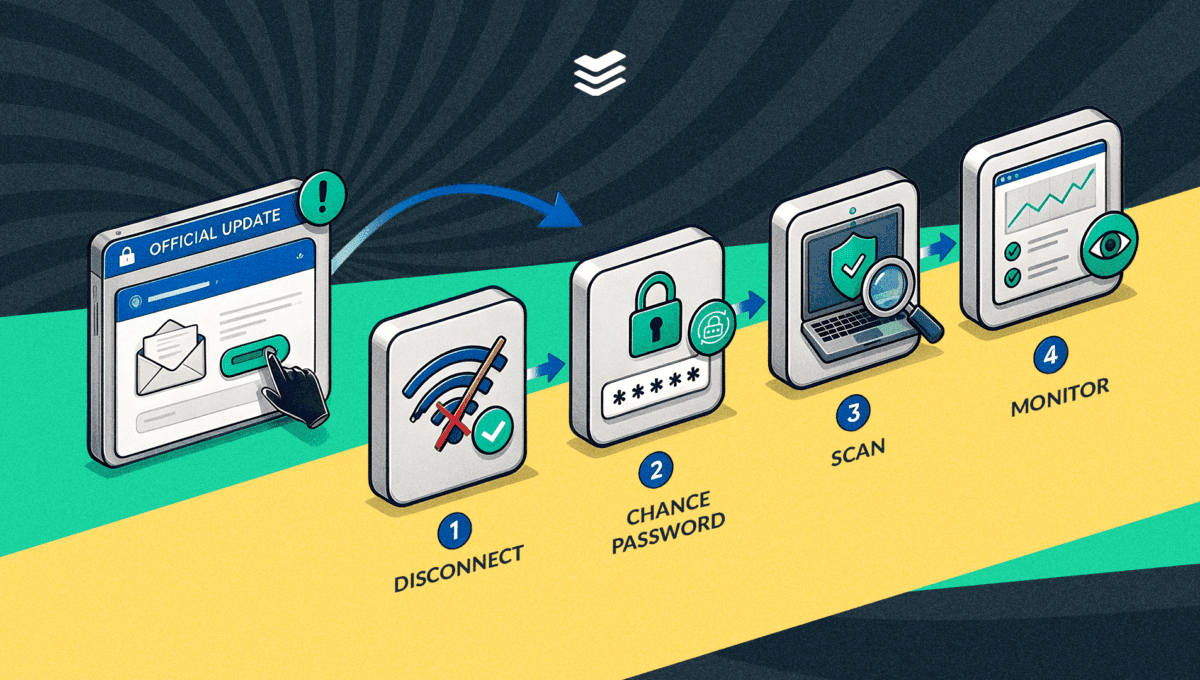
  • Quick action can limit financial and reputational damage associated with phishing attacks. If you or one of your employees falls victim to a phishing attack, you should:

    • Disconnect affected devices from the network
    • Reset compromised accounts with strong passwords and MFA
    • Alert your bank if payments are involved
    • Report the incident to the National Cyber Security Centre (NCSC) or Action Fraud
  • Look out for unusual account activity such as unexpected password resets, invoices with altered bank details, missing emails, or employees reporting suspicious login alerts. Sometimes customers may flag odd emails that appear to come from your domain — a strong indicator of a compromised account.

  • SMEs often have fewer dedicated cybersecurity resources, making them attractive to attackers. They also hold valuable assets: money, client data, supplier relationships, and intellectual property. Hackers see SMEs as low-hanging fruit compared to larger enterprises with stronger defences.

  • Professional services (law, accountancy, consultancy), construction, healthcare, and retail are frequent targets. In other words, industries that handle large payments, sensitive data, and are part of fast-moving supply chains.

What to do if you click on a phishing link

The bad news: you've just clicked on what might be a phishing link.

The good news: you're not alone, and you're not doomed. 

Nearly 1 billion phishing attacks hit inboxes in Q1 2025, and even IT professionals fall for them. The difference between a close call and a costly breach? What you do next.

  1. Document the incident
  2. Disconnect from the network 
  3. Don’t enter any credentials 
  4. Notify your IT team
  5. Scan your device for malware
  6. Change passwords where necessary
  7. Monitor company accounts and systems 

Disconnect from the network

If you suspect your device has been compromised, disconnect it from Wi-Fi or wired networks immediately. This helps prevent malware from spreading across company systems.

Do not enter any credentials

If the phishing site asks for login information or payment details, close the browser immediately. Never enter your company or financial credentials.

Notify your IT team

Report the incident to your internal IT department or cybersecurity team straight away. Include details like:

  • The exact URL (if you can access it safely)
  • How you received the link (email, text, social media)
  • What time you clicked it
  • Any information you might have entered

Under GDPR, you have 72 hours to report certain breaches. The UK's National Cyber Security Centre (NCSC) recommends reporting phishing attempts and suspicious emails to report@phishing.gov.uk.

Learn how CyberSmart Phish can help your team spot phishing attempts before they cause harm

Scan your device for malware

Run a company-approved antivirus or anti-malware scan. Follow the instructions provided by your IT team to ensure no malicious software remains.

Change passwords where necessary

If there’s any chance credentials were exposed, immediately change passwords for affected company accounts. IT may need to enforce a company-wide password reset following password best practices.

Monitor company accounts and systems

Keep an eye on any unusual activity in financial accounts, internal systems, or shared drives. Report anomalies immediately to IT.

Document the incident

Record the time, the link, and the steps you took to address the threat. This helps your security team investigate and prevent future attacks.

Protecting your company’s most vulnerable systems

After clicking a suspicious link at work, certain business systems need immediate attention to prevent widespread damage, such as:

Company email

Check your sent folder immediately. Phishing attacks often use compromised accounts to spread further. One compromised email can infect an entire organisation.

Financial systems

UK businesses lost £1.17 billion to fraud in 2024. If you've accessed any financial platforms recently, alert your finance team. They may need to implement additional security measures or freeze certain transactions.

Shared drives

Malware can spread through shared folders. Your IT team may need to isolate affected areas to prevent infection spreading.

Caught, but not hooked

Clicking a phishing link isn’t the end of the world – it’s what you do next that matters. Acting quickly, reporting to your IT team, and securing your accounts can turn a potential disaster into just a learning moment.

Want to give your people the skills to recognise phishing scams before they turn into breaches? Check out CyberSmart Learn, our cybersecurity focused learning management system.

Frequently asked questions

  • The same principles apply: disconnect from networks, don't enter information, and contact IT. Smishing often targets banking credentials, so pay special attention to financial accounts.

  • On mobile devices and tablets, use Airplane mode for quick disconnection and check app permissions for suspicious additions. Be aware that mobile browsers often hide full URLs, making phishing sites harder to spot.

  • Don't open it. Note the file name and location, then run a full system scan. Your IT team may want to analyse the file in a safe environment.

  • Continue monitoring for at least 30 days. Some attacks lie dormant before activating, and criminals may wait before using stolen credentials.

  • Yes. Transparency helps protect your organisation. Most companies prefer honest reporting over hidden incidents that could escalate.

  • Spam is unwanted email, often selling products. Phishing specifically aims to steal information or install malware.

8 phishing examples for training your employees

Just as anglers use different baits and lures to catch fish, cybercriminals employ various tactics to hook unsuspecting victims. From precision spear phishing scams to whaling attacks that target C-suite executives, hackers have plenty of ways to land their prey.

Understanding these attack methods is crucial for building robust defences. But the best way to prepare your team is to show them what real phishing attempts look like.

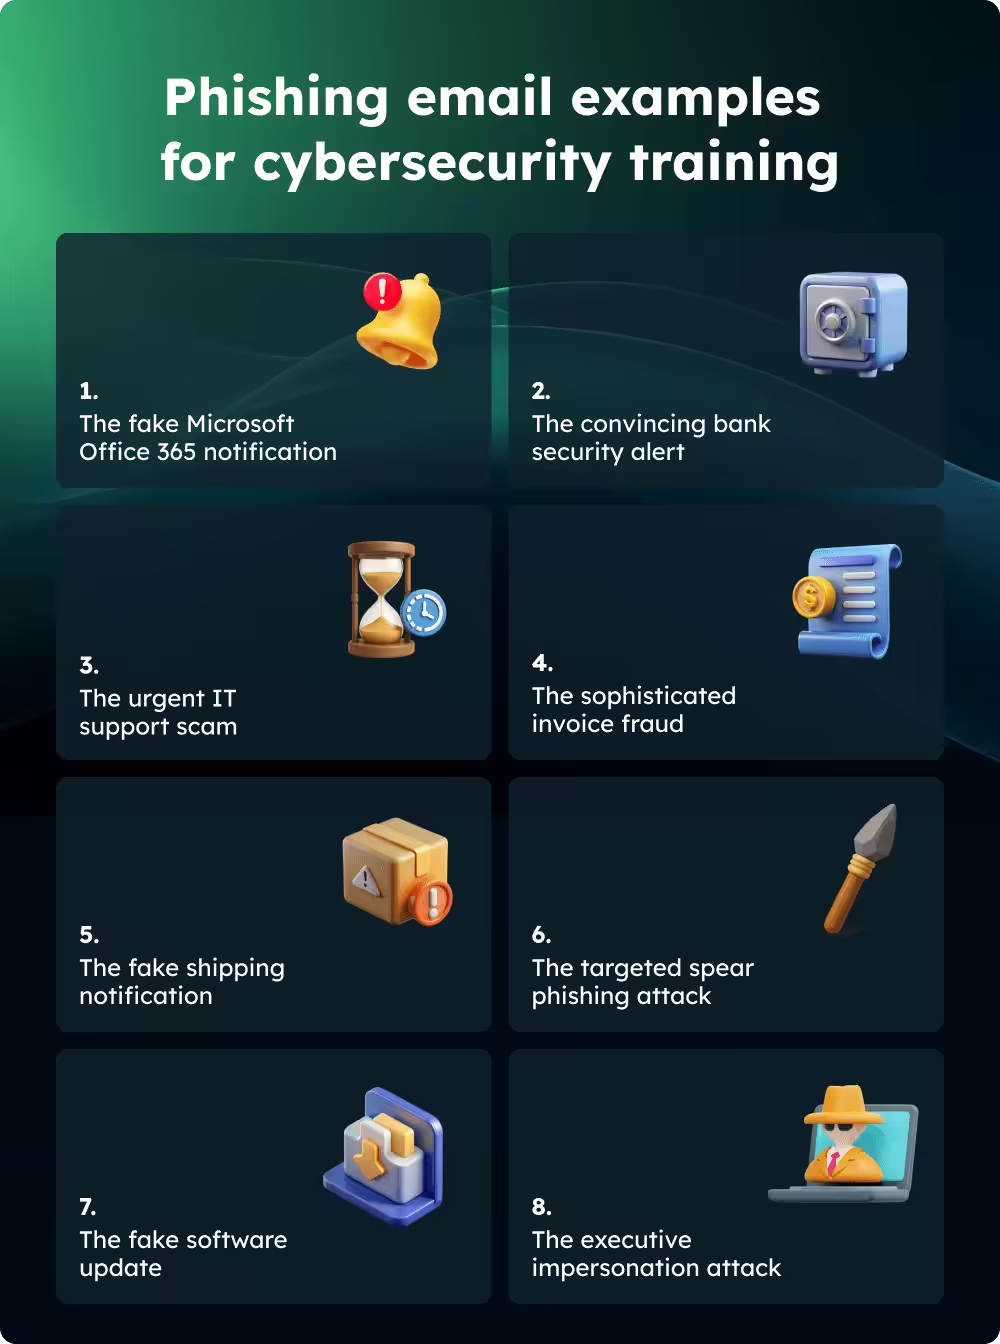
Not sure where to start? Try these eight examples:

  1. The fake Microsoft Office 365 notification

2. The convincing bank security alert

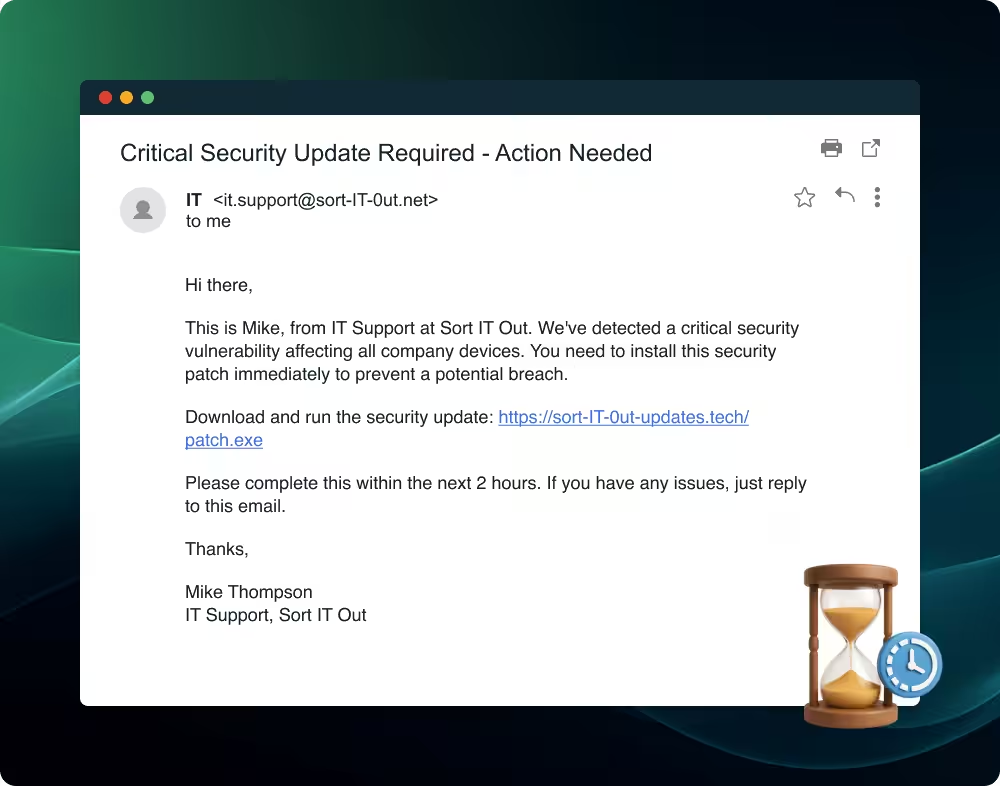
3. The urgent IT support scam

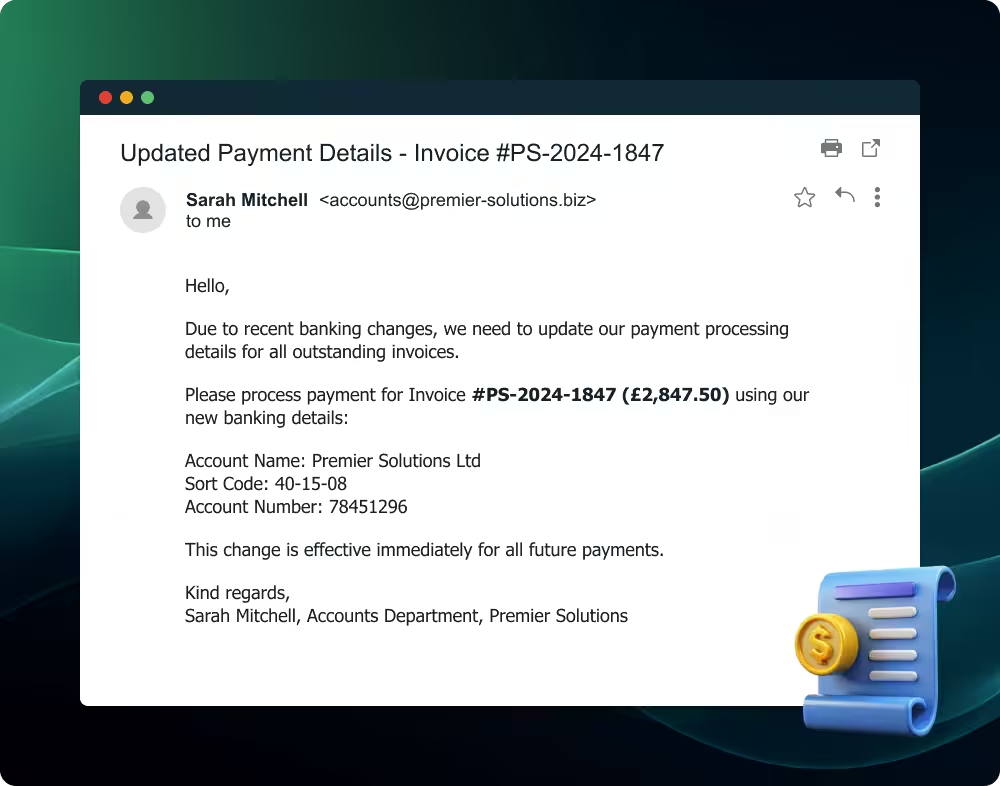
4. The sophisticated invoice fraud

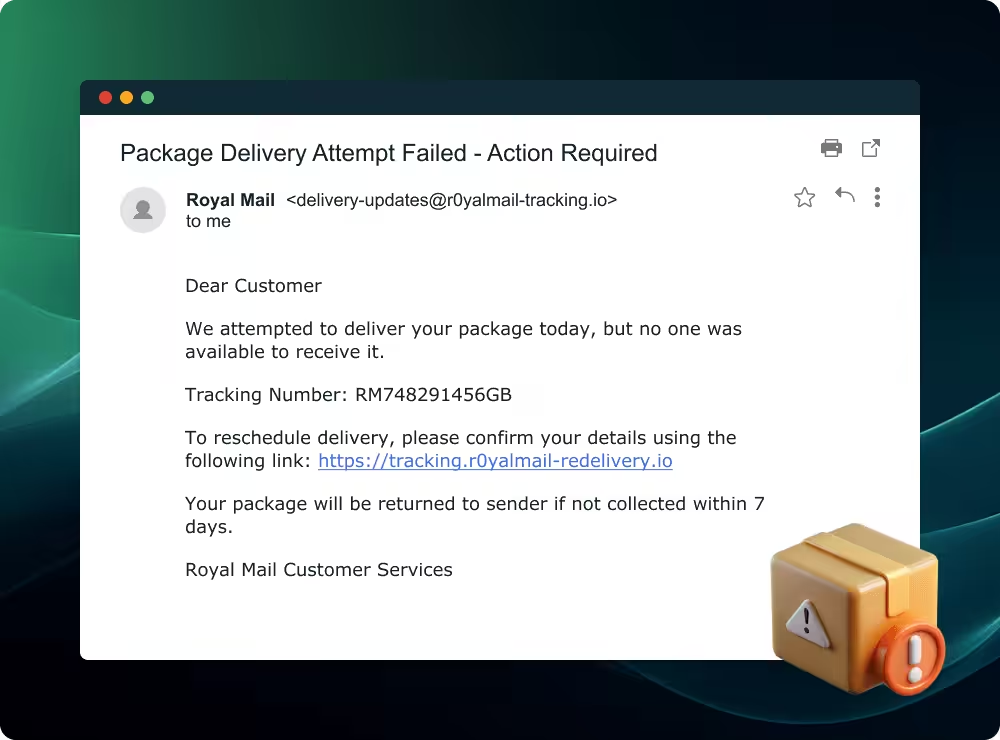
5. The fake shipping notification

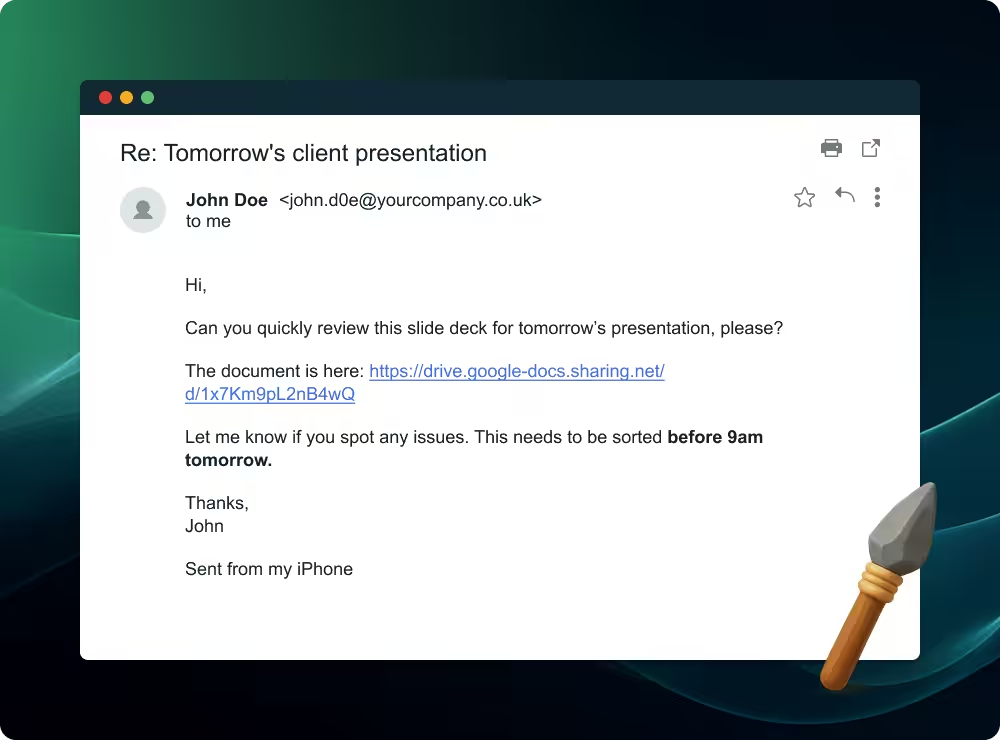
6. The targeted spear phishing attack

7. The fake software update

8. The executive impersonation attack

Why phishing attacks are getting harder to spot

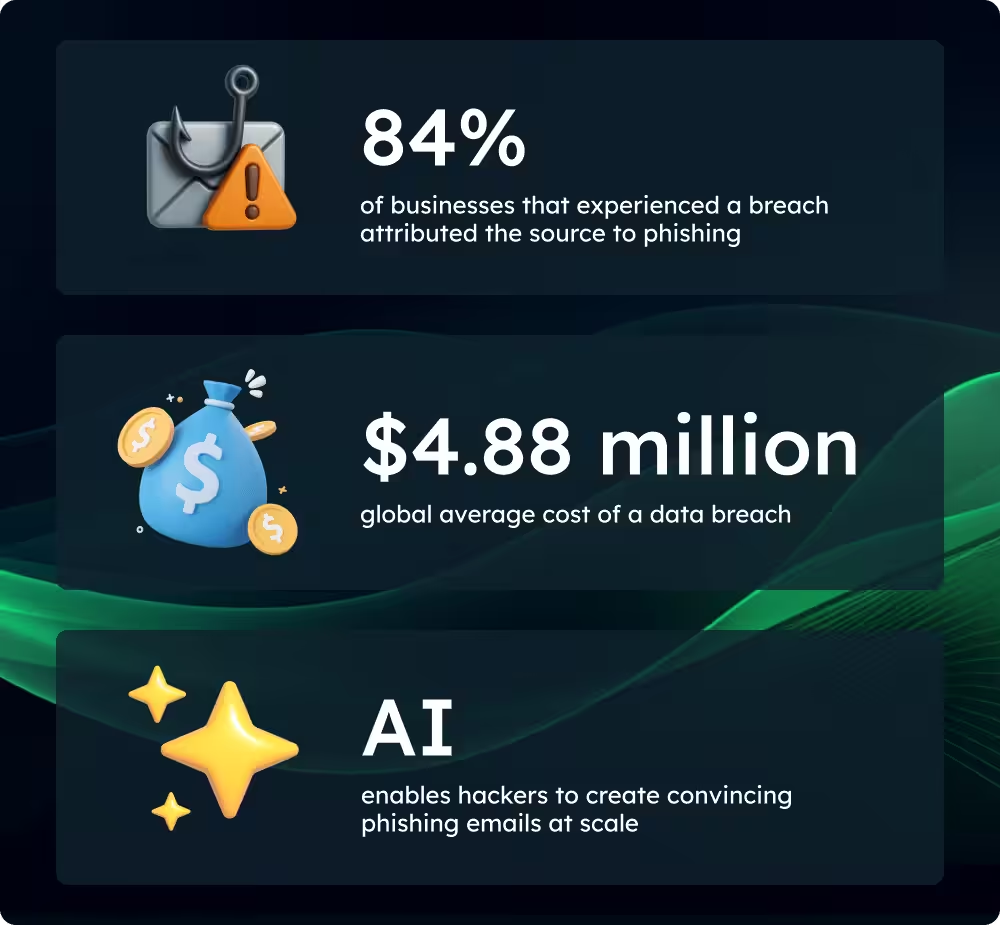
Phishing attacks are becoming more sophisticated and frequent. According to Ipsos’ Cybersecurity Breaches survey 2024, phishing affected 84% of businesses that experienced a breach in 2024.

The financial impact of these attacks is staggering. Researchers estimate the global average cost of a data breach at $4.88 million (approximately £3.9 million) due to:

  • Reparation costs
  • Disruption to business operations
  • Reputational damage
  • Regulatory fines

What makes phishing particularly dangerous today is how attackers use AI to create convincing emails at scale. The most sophisticated can be almost indistinguishable from legitimate communications – unless you know what to look for.

Phishing email examples for training your team

The most effective way to build your team's defences is through practical training that exposes them to real-world scenarios. 

Incorporate the following phishing email examples into your cybersecurity training programmes to teach your team how to spot the signs of phishing attacks.

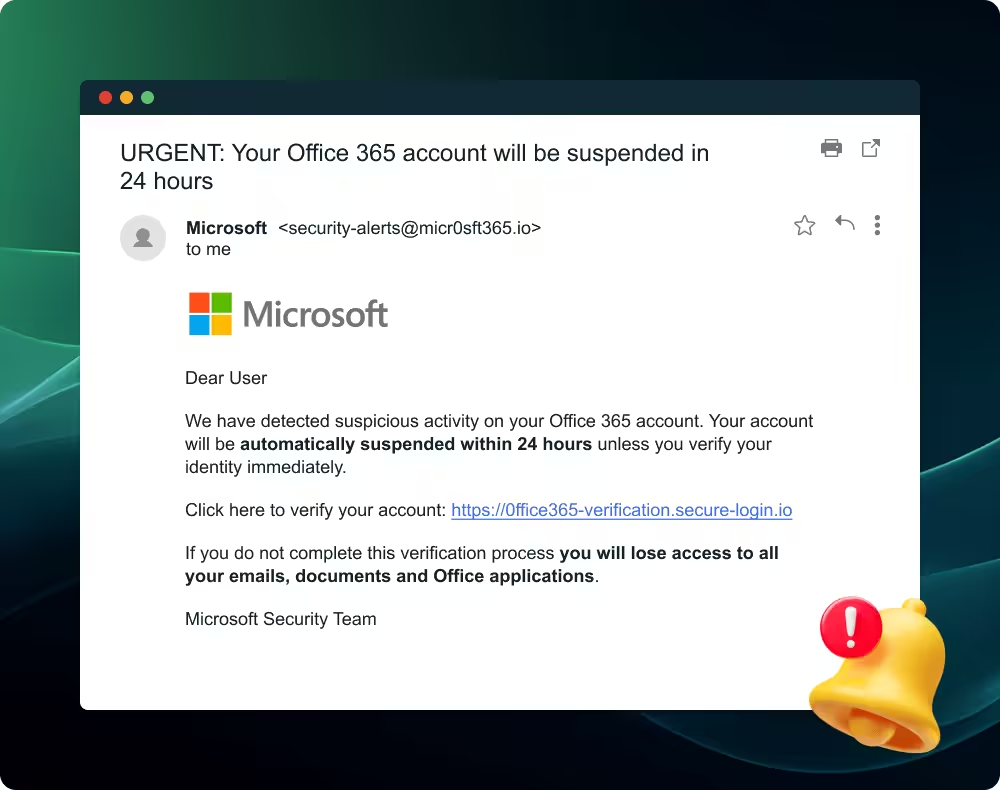
1. The fake Microsoft Office 365 notification

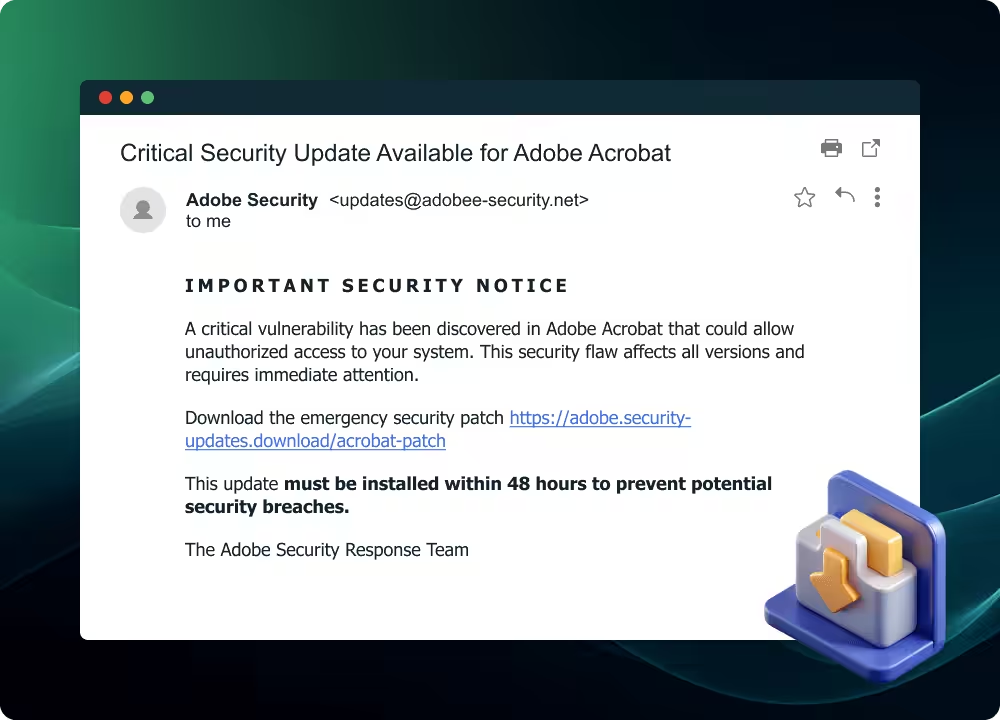
This attack claims your account will be suspended unless you verify your credentials immediately, creating a false sense of urgency. These messages include Microsoft branding and appear to come from a legitimate address.

  • Urgent language, creating false time pressure
  • Suspicious sender addresses with small errors that make them look similar to legitimate domains
  • Links that don't match the claimed destination when you hover over them

Protection tip: Always navigate directly to the service provider's website rather than clicking links in suspicious emails.

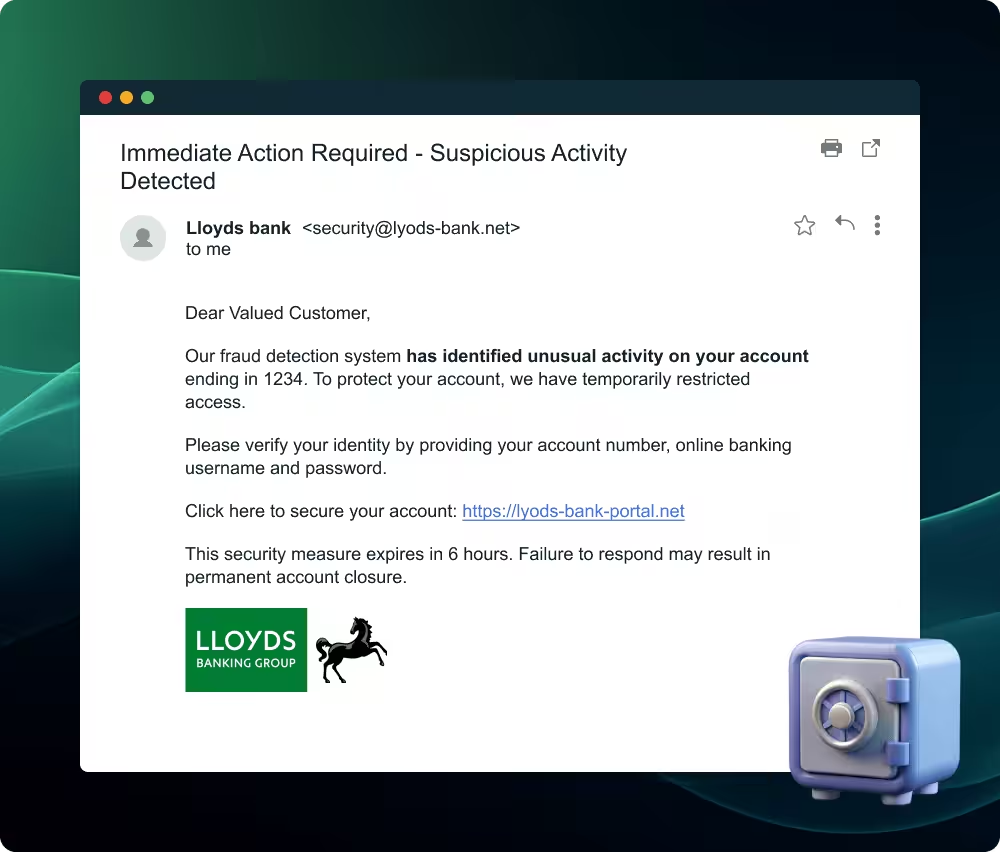
2. The convincing bank security alert

These sophisticated emails mimic legitimate bank communications, using official logos and formatting that closely match genuine correspondence. The messages warn of suspicious account activity and recommend immediate action to secure the account, with the aim of tricking finance team members into handing over sensitive data.

Warning signs:

  • Requests for full login credentials or security codes
  • Slight variations in the bank's web address or email domain
  • Generic account references rather than specific account numbers
  • Poor quality logos or formatting inconsistencies

Protection tip: Banks never ask for complete login details via email. Contact your bank directly using their official phone number if you receive a request that appears dubious.

3. The urgent IT support scam

Similar to the bank security alert, these emails impersonate internal IT departments, claiming urgent security breaches or system failures that require immediate action. They create artificial time pressure, demanding employees bypass normal IT procedures to resolve the supposed issue.

Warning signs:

  • Emails from external addresses claiming to be internal staff
  • Requests to download unknown software or click on suspicious links
  • Pressure to act immediately without following normal IT procedures
  • Messages that don't match your IT team's usual communication style

Protection tip: Verify any urgent IT requests through established internal channels before acting.

4. The sophisticated invoice fraud

In this type of attack, cybercriminals create professional invoices from familiar suppliers but change the payment details to direct funds to fraudulent accounts. The documents maintain authentic branding, formatting, and contact information to avoid suspicion.

Warning signs:

  • Unexpected changes to established payment procedures
  • Requests to update banking details via email
  • Slight variations in company names or email addresses
  • Invoices for services you didn't order or amounts that seem unusual

Protection tip: Always confirm banking detail changes through a separate, verified communication channel before processing payments.

5. The fake shipping notification

Cybercriminals mimic legitimate courier company communications, claiming failed delivery attempts and asking you to reschedule using the supplied link. Attackers often target businesses that receive regular shipments or during peak delivery periods.

Warning signs:

  • Notifications for packages you weren't expecting
  • Links that don't lead to official courier websites
  • Requests for personal information to "confirm delivery"
  • Poor quality email formatting compared to genuine courier communications

Protection tip: Check with the courier directly using their official website or tracking system rather than clicking email links.

6. The targeted spear phishing attack

Spear phishing represents the most personalised form of email attack – with cybercriminals referencing specific projects, recent conversations, or company details – to build credibility. Attackers research their targets extensively, creating emails that appear to come from trusted colleagues, clients, or business partners.

Warning signs:

  • Subtle changes in email addresses or display names
  • Requests that seem out of character for the individual
  • Messages sent at odd times or from unexpected locations
  • Links or attachments you weren't expecting

Protection tip: When in doubt, verify requests through a different communication method, such as a phone call or face-to-face conversation.

7. The fake software update

Fake software updates masquerade as legitimate notifications to trick users. For example, claiming that antivirus programmes, browsers, or business applications require urgent security patches. They include convenient download links that bypass official software update channels.

Warning signs:

  • Update notifications via email rather than through the software itself
  • Generic messaging that doesn't reference your specific software version
  • Download links that don't lead to official software websites
  • Urgent language suggesting immediate security risks

Protection tip: Always update software through official channels or your established IT procedures, never through email links.

8. The executive impersonation attack

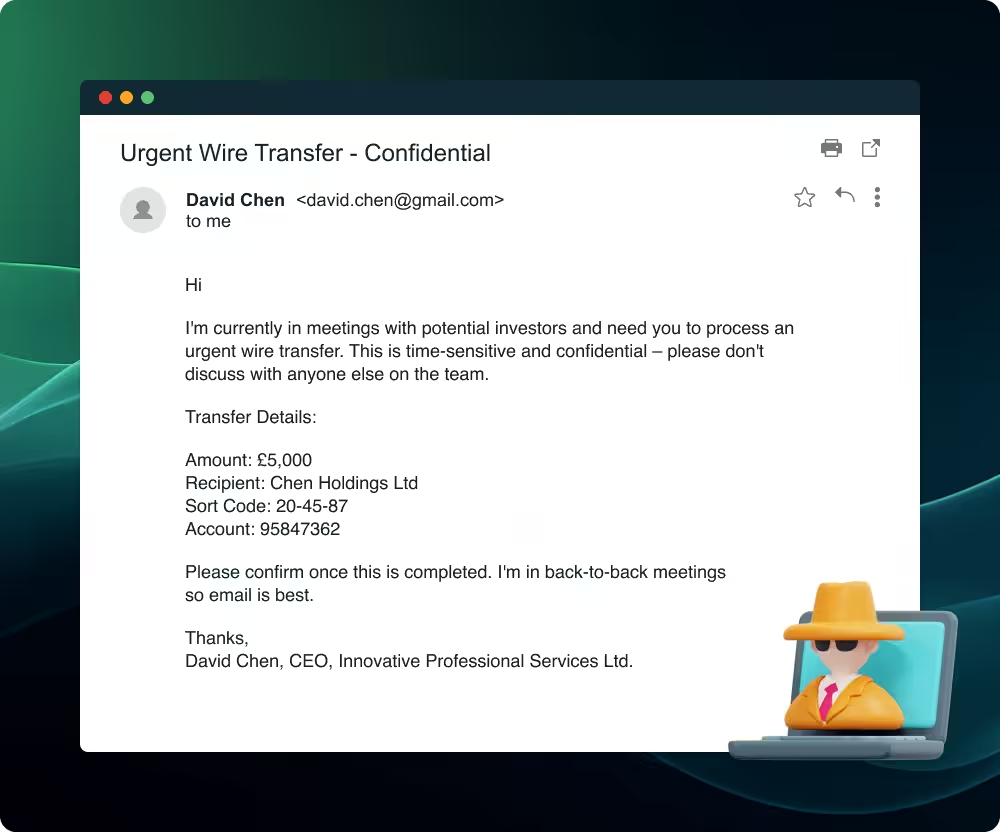
Executive impersonation attacks target employees by mimicking senior leadership, requesting urgent actions such as emergency payments or sharing confidential information. They exploit hierarchical business structures and employees' reluctance to question apparent authority figures, especially under time pressure.

Warning signs:

  • Unusual requests that bypass normal approval processes
  • Pressure to act quickly without following established procedures
  • Email addresses that don't match the executive's usual contact details
  • Tone or language that doesn't match the person's normal communication style

Protection tip: Implement clear verification procedures for high-value requests, especially those involving financial transactions or sensitive data.

Building stronger defences through practical training

The preparation you invest in today could be the difference between a close call and a costly breach.

Whether you’re trying to land the big catch or protect against cyber threats, there’s no substitute for practical experience. By incorporating these phishing mail examples into your training programmes, you’ll help your employees learn how to avoid falling victim to phishing attacks.

Want to go a step further? Consider using a phishing simulator, so you can test their newfound skills in a safe and controlled environment.

Want to give your people the skills to recognise cyber threats before they turn into breaches? Check out CyberSmart Learn, our cybersecurity focused learning management system.

What is NIS2?

If you’re an EU-based business or a UK organisation with clients or partners in Europe, you may need to comply with NIS2. But what is NIS2? How do you know if it applies to your business? And how do you go about complying with it?

According to research, many businesses are ‘unsure’ of the answer to these questions. So, to help your organisation avoid being one of them, here’s everything you need to know.

What is it?

NIS2 is the updated Network and Information Security Directive introduced by the European Union to strengthen cybersecurity across its member states. It builds on the original 2016 NIS Directive by expanding its scope to include more sectors. These sectors include public administration, digital service providers (DSPs), space, and waste management.

NIS2 mandates stricter cybersecurity risk management, supply chain security, incident reporting within 24 hours, and holds company leadership accountable for cybersecurity measures. The directive also enhances cooperation between EU countries and introduces tougher penalties for non-compliance.

What is the goal of NIS2?

Barely a week goes by without some news of an attack or attempt on critical national infrastructure (CNI) and services. Indeed, there are a few things more likely to keep policymakers up at night. For example, think of the chaos caused by the Colonial Pipeline cyber attack in the US or the 2017 WannaCry attack’s impact on the NHS.

NIS2 is the European Union’s attempt to counter potentially devastating CNI attacks. It’s designed to improve resilience against a broad range of cybersecurity threats and develop a unified EU-wide approach to protect critical infrastructure and services.

What does NIS2 include?

NIS2 has a number of key focus areas, each of which contributes to an organisation’s cyber resilience in the face of attack. The areas are: 

  • Incident handling
  • Supply chain risk
  • Policies on risk analysis and information security
  • Business continuity and crisis management
  • Security in systems acquisition, development, and maintenance
  • Policies to assess the effectiveness of measures
  • Basic cyber hygiene practices and training
  • Cryptography and encryption
  • Secure communications
  • Human resources security, asset management, and access control policies
  • Use of multi-factor authentication (MFA)

Is NIS2 mandatory?

For EU member states, yes. NIS2 is an EU directive, which means that member states were required to transpose it into their national laws by no later than the 17th October 2024. However, even non-EU states like the UK are enacting similar legislation. For example, the UK’s Cyber Security and Resilience Bill, currently passing through parliament, is likely to be very similar in content to NIS2.  

But what about businesses?

Well, the directive targets two types of organisation or ‘entities’, to use the legalese. These are ‘Essential Entities’ and ‘Important Entities’, and they span a wide range of sectors. For example, energy, transport, banking, health, digital infrastructure, public administration, and space are all defined as ‘essential’. Meanwhile, manufacturing, food, postal services and digital providers are all defined as ‘important’.

There's also a question of size. NIS2 really only covers medium and large enterprises in the listed sectors. Micro and small enterprises (fewer than 50 staff and more than €10 million turnover) are generally exempt unless they operate in certain high-criticality areas.

What are the consequences of non-compliance with NIS2?

Unlike previous legislation, which was perhaps a little softer on non-compliance, NIS2 comes with pretty stringent penalties.

Financial

NIS2 comes with some real financial clout. Authorities can impose fines for non-compliance of up to €10,000,000 or 2% of global annual turnover for "essential entities," and up to €7,000,000 or 1.4% of global annual turnover for "important entities.”

Administrative sanctions

NIS2 also gives national authorities the power to apply administrative sanctions such as mandatory audits, operational bans, and restrictions on the ability to provide services.

Personal liability for senior management

Perhaps most worryingly for business leaders, senior management may face personal liability for non-compliance. This could lead to disqualification from executive roles, civil lawsuits, and even criminal prosecution if major negligence is involved.

GDPR implications

We’ve yet to see this play out in the real world, but some legal professionals believe that non-compliance with NIS2 could also be considered a breach under GDPR. If this is the case, further penalties and legal consequences could apply. 

All in all, failing to comply with NIS2 is a big risk. EU legislators have learned lessons from previous, poorly adopted regulations and frameworks and, due to the potential seriousness of CNI breaches, have clearly decided the stick is more likely to motivate organisations.
How do you know if your business is in scope for NIS2?

Checking whether you need to comply with NIS2 is a relatively simple process. The following checklist should help you determine whether it applies to your organisation.

1. Identify your sector

Check if your organisation falls under any NIS2-defined essential or important sectors. For example, hospitals and utilities are essential, whereas digital services and certain manufacturers may be important.

2. Check the size thresholds

Confirm if your organisation exceeds the micro and small size exemption. If you have more than 50 employees or turnover greater than €10m, NIS2 likely applies (unless explicitly exempted by sector rules).

3. Review exceptions or special cases

Some organisations are in scope regardless of size, such as certain critical providers. Also, if a more specific sector law applies, it might override NIS2 for your case. For example, financial institutions may fall under the Digital Operational Resilience Act (DORA) instead of NIS2.

4. Check your non-EU business isn’t in scope

It’s also important to note that if your business works with EU organisations, you’ll likely need to comply with NIS2, even if you’re based outside the union. For instance, many UK companies with EU clients, partners, or suppliers fall within its scope.

What does NIS2 mean for MSPs?

Quite a lot. NIS2 specifically refers to managed service providers (MSPs) as one of the entities:

“Providing services related to the installation, management, operation or maintenance of ICT products, networks, infrastructure, applications or any other network and information systems, via assistance or active administration, carried out either on customers’ premises or remotely.”

Again, you’ll need to run through the industry, size and location criteria to determine whether your organisation applies. However, most large EU MSPs are going to find themselves in scope, along with those in the UK that work across borders. If you’re unsure, we recommend reading this excellent summary of applicability.

An opportunity as well as an obligation

However, while many MSPs need to comply with NIS2, it isn’t just an obligation. It’s also an opportunity.

In the UK alone, a fifth of businesses are unsure whether NIS2 applies to them. And, 10% of organisations that are in scope admit to non-compliance. Meanwhile, while compliance has generally been a little better across the EU, many businesses remain confused.

For MSPs who’ve been through their own journey to NIS2 compliance, this is a golden opportunity to offer clients a service. Much the same as they do for Cyber Essentials and other frameworks, clients are going to look to MSPs to help them navigate NIS2 and maintain compliance. After all, who better than MSPs who’ve been through the process and are well-equipped to provide guidance?

How can your organisation comply with NIS2?

If you’re unsure about where to start with NIS2 compliance, remember you’re not alone. 

At CyberSmart, we offer a structured, scalable route to achieving and maintaining NIS2 compliance. We’ll help you identify any gaps through our auditing process, provide a compliance report with actionable recommendations, and help you obtain and maintain NIS2 compliance. 

Check out our NIS2 maturity pathway to find out more.


15 types of phishing attacks and how to protect your business

Phishing attacks are nothing new. But the tactics cybercriminals use? They're evolving faster than ever. Every day, an estimated 3.4 billion phishing emails are sent across the globe, many of them targeting UK businesses. The good news? Once you understand the different types of phishing attacks, you can spot the warning signs and stop them.

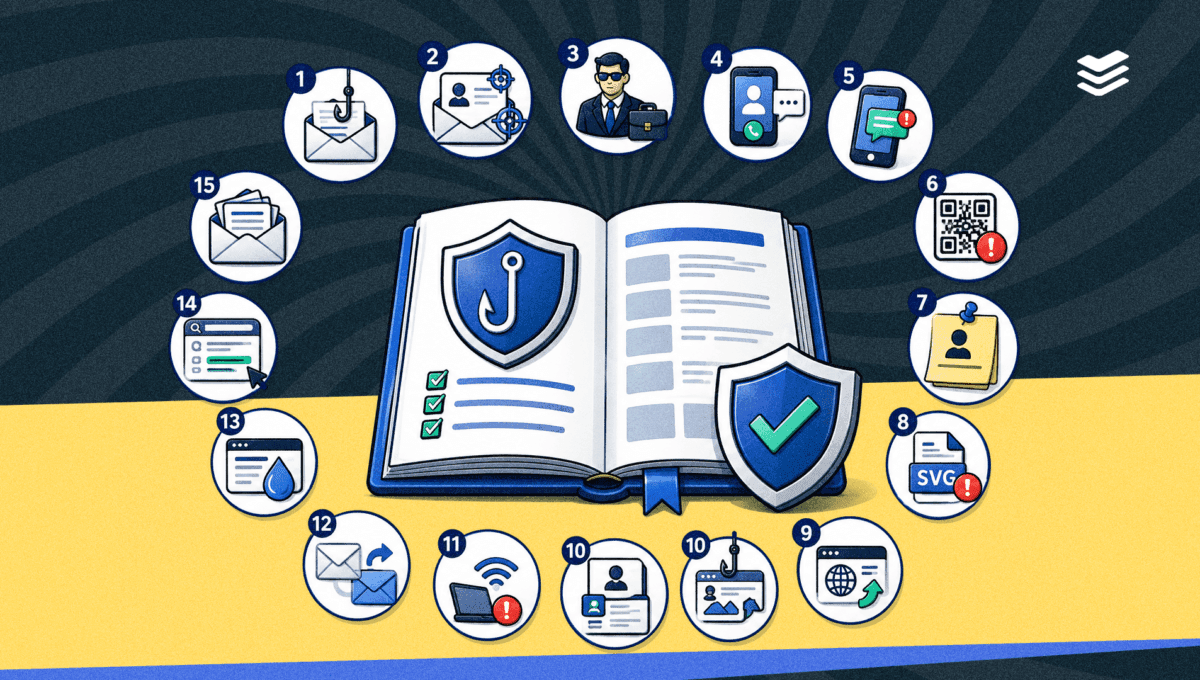
15 of the most popular types of phishing attacks include:

1. Email phishing
2. Spear phishing
3. Whaling
4. Vishing
5. Smishing
6. Quishing
7. “Note to self” phishing
8. SVG phishing
9. Pharming
10. Angle phishing
11. Evil twin phishing
12. Clone phishing
13. Watering hole phishing
14. Search engine phishing
15. Bulk phishing

1. Email phishing

Email is the most common type of phishing attack. Phishing emails often come from addresses that look official but are just slightly off. For example, support@micros0ft.com. While poor grammar was once a giveaway, modern phishing emails are well-written and seemingly credible.

2. Spear phishing

Spear phishing targets specific individuals based on their job title or recent company activity. Attackers research their victims through company websites, LinkedIn, and other social media platforms, using personal insights to make their messages appear legitimate. 

Red flags to watch for:

  • Unusual requests – if the requests come from within your company asking for credentials above their pay grade, message the individual directly using another communication channel for confirmation
  • Slight changes in email addresses or domain

3. Whaling

Also called whale phishing, this tactic zeroes in on executives and high-level decision-makers – the “big fish.” The stakes are higher here, so attackers go to greater lengths, even using AI-generated deepfake video or voice impersonation to deceive their targets. 

In one case, a finance employee was tricked into transferring $25 million after fraudsters used deepfake technology to impersonate the company's CFO and colleagues in a video conference. 

 Common whaling tactics include: 

  • Impersonating executives or board members
  • Creating fake acquisition or legal scenarios
  • Timing attacks when executives are travelling or busy
  • Using insider knowledge gleaned from social media or public statements

To defend against these high-stakes attacks, establish internal checks and approval processes for large transactions, and train executives to spot the hallmarks of phishing.

4. Vishing

Vishing is short for voice phishing and occurs when cybercriminals use phone calls or voice messages to get victims to reveal sensitive information. There was a 442% rise in vishing in 2024, making it clear that this type of phishing is one to look (or should we say listen?)  out for. 

The best defence? 

  • Never give sensitive information over the phone to unsolicited callers
  • Hang up and call back on an official number
  • Be suspicious of urgent requests or threats

5. Smishing

Smishing uses SMS messages to lure victims into clicking on a malicious link. A common smishing pretext is receiving a message from your bank alerting you to suspicious activity.

Other popular smishing campaigns claim that:

  • A package is waiting for collection
  • Your bank account has been compromised
  • You've won a prize or a refund
  • A payment has failed

Early in 2025, U.S. residents were targeted with fake text messages claiming to be from toll road operators like EZPass. The messages warned recipients about unpaid tolls, fines, or potential loss of their driver’s license, urging them to pay online. The scams were driven by an advanced phishing kit sold in China that allows scammers to spoof toll agencies across various states.

6. Quishing

Quishing or QR code phishing is when cybercriminals use QR codes to get victims to download malware or visit fraudulent websites. They often slip these codes into emails, posters, or public spaces.

Because QR codes are hard to inspect before scanning, many victims don’t realise they’re being phished until it’s too late.Only scan QR codes from trusted sources, and always check the URL after scanning before entering any information.

7. “Note to self” phishing

You receive an email from… yourself. But it’s not a friendly reminder. It’s a message from a cybercriminal telling you they’ve hacked your account and have compromising information. They then demand ransom, usually in the form of cryptocurrency. 

That’s what happens in “Note to self” phishing. It’s deeply unsettling, but it’s important to remember that cybercriminals don’t actually have your credentials or any compromising material; they’re just bluffing. 

What to do:

  • Don't panic
  • Don't pay
  • Change your passwords 
  • Mark it as spam and delete it

8. SVG phishing

SVG phishing refers to using scalable vector graphics (SVG) files in phishing attacks. SVGs are image files, but hackers embed them with JavaScript that contains malicious code. 

Since many security systems don’t scan SVGs as thoroughly as PDFs or Office documents, these files often slip through.To protect your business, block or restrict SVG attachments unless necessary, and make sure endpoint security solutions can analyse embedded scripts.

9. Pharming

Sometimes referred to as “phishing without a lure”, pharming is when cybercriminals redirect users to fake, lookalike websites to steal sensitive information. Rather than using social engineering, attackers use technical means like exploiting DNS server vulnerabilities to trick victims. 

Your defence:

  • Keep your devices and browsers updated
  • Use reliable DNS servers
  • Look for HTTPS and valid security certificates
  • Install reputable antivirus software with real-time protection

10. Angler phishing

Angler phishing exploits customer frustration on social media. Scammers monitor complaints directed at companies (especially banks or service providers), then swoop in posing as helpful support reps.

They use fake profiles, unofficial links, and friendly language to get victims to “verify” account info – only to steal it.

Watch out for:

  • Customer service accounts without verification badges
  • Requests to move conversations to private messages
  • Links to non-official websites
  • Requests for passwords or account details

11. Evil twin phishing

Cybercriminals set up fake Wi-Fi access points imitating legitimate ones. Once victims connect, the hackers have access to their internet activity and, by extension, sensitive information, such as login details and personal data. 

Evil twin phishing is common in place spaces like train stations, shopping malls, and airports. 

Here’s how to protect yourself: 

  • Use a VPN if you have to use public Wi-Fi
  • Disable the auto-connect function on your devices

12. Clone phishing

Clone phishing is a difficult-to-spot cyberattack because cybercriminals take a legitimate email that a user has already received and clone it. The only change they make is replacing the original links with malicious ones. 

Precautions you can take: 

  • Hover over links before clicking to verify the URL 
  • If you receive a duplicate or out-of-place email, contact the sender directly to confirm the email's authenticity 
  • Keep antivirus and anti-phishing tools updated so they detect malicious emails and attachments.

13. Watering hole phishing

Watering hole phishing occurs when hackers compromise a website that’s frequented by a specific group of people. For example, employees of a company, government officials, and members of a particular industry. 

Once the site is infected with malware, anyone who visits it may unknowingly download malware, giving attackers access to sensitive systems or data.

Tips for safe browsing: 

  • Keep all software and browsers up to date to close known security vulnerabilities.
  • Use reputable antivirus and anti-malware tools to detect and block threats.

14. Search engine phishing

Also known as SEO poisoning, search engine phishing is when cybercriminals create malicious websites and use SEO techniques to make the sites appear high in search results for popular or trending keywords. Since most users tend to click on the top few results, this increases the chances that users will visit these harmful sites.

When you click on one of these poisoned links, you might be: 

  • Tricked into entering personal information like login credentials, credit card details, or other sensitive data.
  • Infected with malware or ransomware if the site automatically downloads malicious software.
  • Redirected to other phishing or scam sites that continue the attack chain.

15. Bulk phishing

Bulk phishing is when attackers send a large number of generic phishing emails to many people at once. They’re usually the easiest to spot as they use simple, non-personalised messages to trick recipients into clicking malicious links or giving away personal info. Attackers rely on volume, hoping some victims will fall for the scam.

Key features of bulk phishing:

  • Mass distribution: attackers send thousands of identical or very similar phishing emails.
  • Generic content: the messages usually contain general, non-personalised language like “Your account has been compromised” or “Click here to verify your information.”
  • Goal: to trick recipients into clicking malicious links, downloading malware, or submitting login or financial info on fake websites.

Knowledge is your best defence

These 15 types of phishing attacks show just how diverse and dangerous the threat landscape has become. Phishing isn't going away, but with a diligent approach to cybersecurity and the right tools, your business won’t be an easy catch.

Want to give your people the skills to recognise cyber threats before they turn into breaches? Check out CyberSmart Learn, our cybersecurity focused learning management system.

What is vishing in cybersecurity, and how can you protect your business?

We’ve all heard of phishing, but what is vishing in cybersecurity? It’s short for voice phishing and is a type of social engineering attack where cybercriminals use phone calls, voicemails and voice messages to trick people into divulging sensitive information. 

It might sound like the sort of thing only the elderly would fall for, but with the rise of AI, it’s an increasing threat and one that you can’t afford to ignore.

Understanding vishing in cybersecurity

Vishing weaponises something we instinctively trust – human conversation. While most of us have learned to spot suspicious emails – the typos, the urgent demands, the dubious sender addresses – phone calls bypass these defences entirely. A confident voice claiming to represent your bank, IT department, or tax authority taps directly into our tendency to trust spoken communication.

This psychological advantage helps explain why vishing attacks rose by 442% in the second half of 2024.

How AI’s transforming vishing

Although vishing is a type of phone scam, it’s far more sophisticated than someone phoning to say you’ve won a prize in a competition you never entered, but have to pay taxes and registration fees to claim it. 

Today, cybercriminals are automating vishing campaigns with AI-powered tools and techniques, such as:

  • Text-to-speech engines, which convert written text into realistic human speech
  • Voice cloning and deepfake audio, which replicate a person’s voice 
  • Automatic speech recognition (ASR), which allows AI to understand what the victim is saying in real time

As AI tools become more accessible, the barrier to launching convincing voice scams is dropping, making vishing more dangerous and difficult to detect.

How vishing works in practice

Here's an example of the sequence of events in a typical vishing attack:

  • You receive a call that appears to be from your bank
  • The caller creates urgency, for example, by claiming there has been suspicious activity on your account
  • They ask you to verify your identity by providing account details or passwords
  • Once they have your information, they use it to access your accounts or sell it on the dark web

Common vishing techniques

Help desk social engineering

Attackers pose as legitimate help desk or IT staff. They call employees to trick them into: 

  • Sharing login credentials
  • Disabling multi-factor authentication 
  • Installing remote access tools

Wardialing

Cybercriminals use automated tools to systematically call hundreds or even thousands of numbers based on predictable telephone number structures within specific area codes. They play a pre-recorded message to trick victims into calling back or revealing sensitive information.

Caller ID spoofing

Attackers use technical or third-party tools to falsify the displayed caller ID, showing names such as “Bank of England,” “IRS,” “Police,” or even personal contacts.

Dumpster diving

Also known as trash tracing, this technique can be digital or physical and involves combing through discarded documents to glean information, like names, account numbers, balances and more. Having this information makes vishing attempts appear a lot more credible.

VoIP

Scammers use Voice over Internet Protocol (VoIP), which allows them to make calls over the internet instead of traditional phone lines. This helps them conceal their locations and identities.

3 signs of vishing

Unfortunately, you can't examine a voice call like you would a suspicious email. Instead, listen for these warning signs:

1. Unexpected urgency

If the caller’s pushing you to act immediately, hang up. Real organisations give you time.

2. Asking for information they should have

Banks don't need your PIN. IT doesn't need your password. If they're fishing for details, it's a scam.

3. Threats and pressure

Saying things like "Your account will be closed" or "You'll face legal action". Scammers use fear to cloud your judgment.

How to protect your business from vishing

Building strong defences against vishing, or other mobile phishing attempts, doesn't require a massive budget or technical expertise. Start with these practical steps:

Train your team regularly

Make vishing awareness part of your regular cybersecurity training. Run simulations where employees practice handling suspicious calls. Focus on anyone who handles sensitive data.

Implement verification procedures

Create clear protocols for verifying caller identities. If someone claims to be from a supplier or partner, hang up and call them back on a known number.

Use technology

While email filters can't stop voice calls, you can use call-blocking services and apps that identify potential spam calls. Consider implementing multi-factor authentication that doesn't rely on SMS, as scammers often try to intercept text messages.

Don't let scammers have the last word

Now that you understand what vishing in cybersecurity is, you can take simple, proactive steps to keep your business and team protected.

Want to give your people the skills to recognise cyber threats before they turn into breaches? Check out CyberSmart Learn, our cybersecurity focused learning management system.

What is clone phishing? The email threat you’ve probably seen before

When it comes to cybersecurity threats, phishing remains the most persistent and dangerous. One particularly deceptive variant is clone phishing. This occurs when cybercriminals copy or clone a legitimate email and subtly alter it with malicious links or attachments, making it difficult to detect.

How does clone phishing work?

Clone phishing exploits familiarity and trust. Attackers first obtain a legitimate email, often through prior compromise or email interception, and then create a near-identical replica. They carefully replace real links or attachments with malicious ones while keeping the email's tone and formatting intact. The email is then sent to the original recipients or others in the same organisation, using a spoofed or compromised account.

Because the content appears routine and expected, victims are likely to interact without suspicion, enabling the attacker to steal credentials or install malware. Attacks can use clone phishing to bypass multi-factor authentication (MFA) by tricking users into entering their credentials and one-time MFA codes on a fake site.

Transform your team into your strongest security asset with CyberSmart Learn, our cybersecurity awareness training tool designed for businesses and MSPs. 

Clone phishing vs spear phishing: what’s the difference?

Spear phishing involves crafting entirely new, personalised messages tailored to a specific individual. These emails often reference job titles, recent activities, or shared contacts to appear credible.

Clone phishing, on the other hand, is based on existing communications. The attacker takes a legitimate email you've seen before and duplicates it.
Some of the most common clone phishing techniques are:

Domain spoofing and lookalike domains

Attackers create fake email addresses or domains that appear legitimate at first glance. 

Cybercriminals sometimes use a trick called homograph attacks to fool people into visiting fake websites. This involves using characters from different alphabets that look exactly like regular English letters, but are completely different. 

For example:

  • The website "amazоn.com" might look normal at first glance.
  • But in this case, the letter 'о' isn’t the regular English (Latin) "o". It’s a Cyrillic 'о', which looks the same but is a different character entirely.

This subtle change is invisible to users but can redirect them to malicious websites controlled by attackers, where personal data may be stolen or malware installed.

Advanced URL obfuscation

To hide malicious destinations, attackers may use URL shorteners or compromised websites that redirect to harmful pages. This type of obfuscation makes it difficult, even for savvy users, to tell where a link goes before they click.

Mobile-optimised cloning

Many professionals check emails on mobile devices, where full URLs are hidden. Cybercriminals exploit this by crafting emails that display perfectly on small screens, increasing the chances that users will tap links or download files without verifying their authenticity.

How to spot a clone phishing attempt

Despite their convincing appearance, cloned phishing emails show subtle warning signs. Here’s how to spot them:

  • Inspect the sender’s email address: instead of accounts@legitimatecompany.com, it might be accounts@legitirnatecompany.com. Always hover over the sender’s name to reveal the true address.
  • Watch for unexpected urgency: if a routine invoice suddenly demands "immediate action to avoid suspension," it’s a red flag.
  • Double-check any new instructions: new login links or payment details? Confirm with the sender through another channel before taking action.
  • Trust your instincts: if something feels off, even slightly, it’s worth a second look.

Did you know? Microsoft, DocuSign, and internal Human Resources departments are the most impersonated entities in phishing attempts.

How to defend against clone phishing

Protecting against clone phishing requires a combination of user awareness and technical safeguards:

  • Enable email authentication protocols like SPF, DKIM, and DMARC to prevent domain spoofing.
  • Use anti-phishing filters and email threat detection tools that scan for suspicious links and attachments.
  • Train employees to verify any unexpected emails, even those that appear routine or familiar.

Stay one step ahead of clone phishing

Clone phishing is stealthy, convincing, and increasingly common. Its ability to exploit trust and familiarity makes it especially effective, often evading both technical safeguards and human intuition.

By learning to recognise the subtle differences in emails, staying cautious with unexpected requests, and using secure communication channels for verification, you can reduce the risk of falling victim to clone phishing.

Want to give your people the skills to recognise cyber threats before they turn into breaches? Check out CyberSmart Learn, our cybersecurity focused learning management system.

How to avoid fake CAPTCHA scams

CAPTCHAs are an everyday internet security feature, so much so, that most of us rarely consider them anything more than a bit of an annoyance. But what if the puzzle you solved led to malware attack? Here’s everything you need to know about a new and sophisticated threat: fake CAPTCHA scams.

What is a CAPTCHA?

A CAPTCHA, or “Completely Automated Public Turing Test to Tell Computers and Humans Apart”, to give it its full name, is a security measure. As it says on the tin, its purpose is to differentiate between human users and bots.

CAPTCHAs present a challenge that’s easy for humans but difficult for computers to solve, such as clicking on pictures of motorbikes or buses until there aren’t any left. Or, if the website is a little more old school, entering a sequence of letters or numbers displayed on the screen. This helps protect websites from spam and other bot-driven attacks.

You’ll have almost certainly come across some form of CAPTCHA at some point; they’ve become one of the most regularly deployed security measures around. Unfortunately, cybercriminals have also figured out how to weaponise them to launch malware or phishing scams.

How do fake CAPTCHA scams work?

Fake CAPTCHA scams use familiar internet behaviour, such as solving a challenge, to trick users into executing commands that download and install malicious software. These scams are usually hosted on spoof websites, but not always. Some have managed to compromise legitimate websites.

One example is “ClickFix” which presents victims with a fake version of Cloudflare’s Turnstile CAPTCHA. What makes this so clever is that cybercriminals have copied everything from the visual layout to the unique identifier system Cloudflare uses to tag every request moving through its systems.

When users land on what they think is a CAPTCHA page, they’re promoted to tick the usual box to verify that they’re human. So far so normal, but what happens next is the crux of the scam. The victim follows a set of instructions that includes keying a seemingly random sequence in.

However, what appears random, is actually a cleverly concealed PowerShell command, copied onto the user’s clipboard. Once executed, this command goes and retrieves and runs malware on the user’s device and any systems connected to it. 
The worst part about this threat? It can evade most standard defences. Tools like anti-virus software or anti-malware are usually designed to block suspicious downloads or activity. As a result, they’re unlikely to pick up a CAPTCHA scam because the user has been tricked into launching the malware themselves.

How can your business protect itself from fake CAPTCHA scams?

Given the sophistication of CAPTCHA scams, it might seem as though there’s little you can do to protect your business. But fear not, with the right combination of technical defences, employee training and continuous monitoring, it’s easily possible.

1. Set up advanced threat detection

First up, there’s a few things on the technical side it’s worth doing:

  • Use browser isolation to prevent staff from interacting with fake CAPTCHA scams or any other untrustworthy scripts
  • Enable bot dection and rate limiting on login portals to reduce the risk of credential stuffing or brute-force attacks
  • Always use multi-factor authentication to block unauthorised access even if employee credentials are compromised

2. Train employees to recognise the risks

It’s a well worn statistic but around 95% of all breaches stem from some form of human error. The same is true when it comes to fake CAPTCHAs, even if the error is being tricked rather than careless. And, as with most other threats, the best way to counter this is through cybersecurity awareness training, this includes:

  • Regular training to help your people recognise suspicious CAPTCHA behavior, such as requests to download software, run scripts, or enter sensitive information
  • Use simulation based training, including fake CAPTCHA scenarios to build employee confidence in spotting scams
  • Teach employees to carefully inspect URLs before interacting with CAPTCHA pages and to develop a “pause and verify” habit when something feels off
  • Encourage reporting of suspicious CAPTCHA pages for early detection
  • Put in place rules for CAPTCHA challenges. Your staff should only ever interact with them if they’re confident it’s hosted on a trusted website, verify URLs through SSL certificates, and never run scripts prompted by CAPTCHA pages

3. Continuous monitoring

As well as taking proactive steps to upskill your staff, it’s also advisable to use continuous monitoring and improvement to assess your defences. 

  • Use dark web monitoring services to detect if any employee or customer credentials have been compromised and exposed online
  • Continuously monitor company systems for unusual or suspicious behaviour
  • Conduct exercises simulating CAPTCHA phishing attacks to evaluate weaknesses and improve your defences

4. Secure your business’s domains

Finally, it’s often overlooked by businesses, but one of the best ways to avoid phishing scams like fake CAPTCHAs is to monitor your domains and act quickly to lock anything out of the ordinary down.

  • Protect your email domains with DMARC, DKIM, and SPF policies to prevent spoofing that can lead to spear-phishing attacks using fake CAPTCHA pages.
  • Monitor for typosquatting domains that mimic your legitimate URLs and take action to shut them down.
  • Ensure legitimate login portals use CAPTCHA implementations with challenge-response verification rather than simple click-based CAPTCHA

Want to know more about protecting your business from malware? Check out our free guide to the best malware protection for businesses.